
Aystat Detect Hidden
| 开发者 | stonemanhero |
|---|---|
| 更新时间 | 2026年11月15日 23:27 |
| 捐献地址: | 去捐款 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
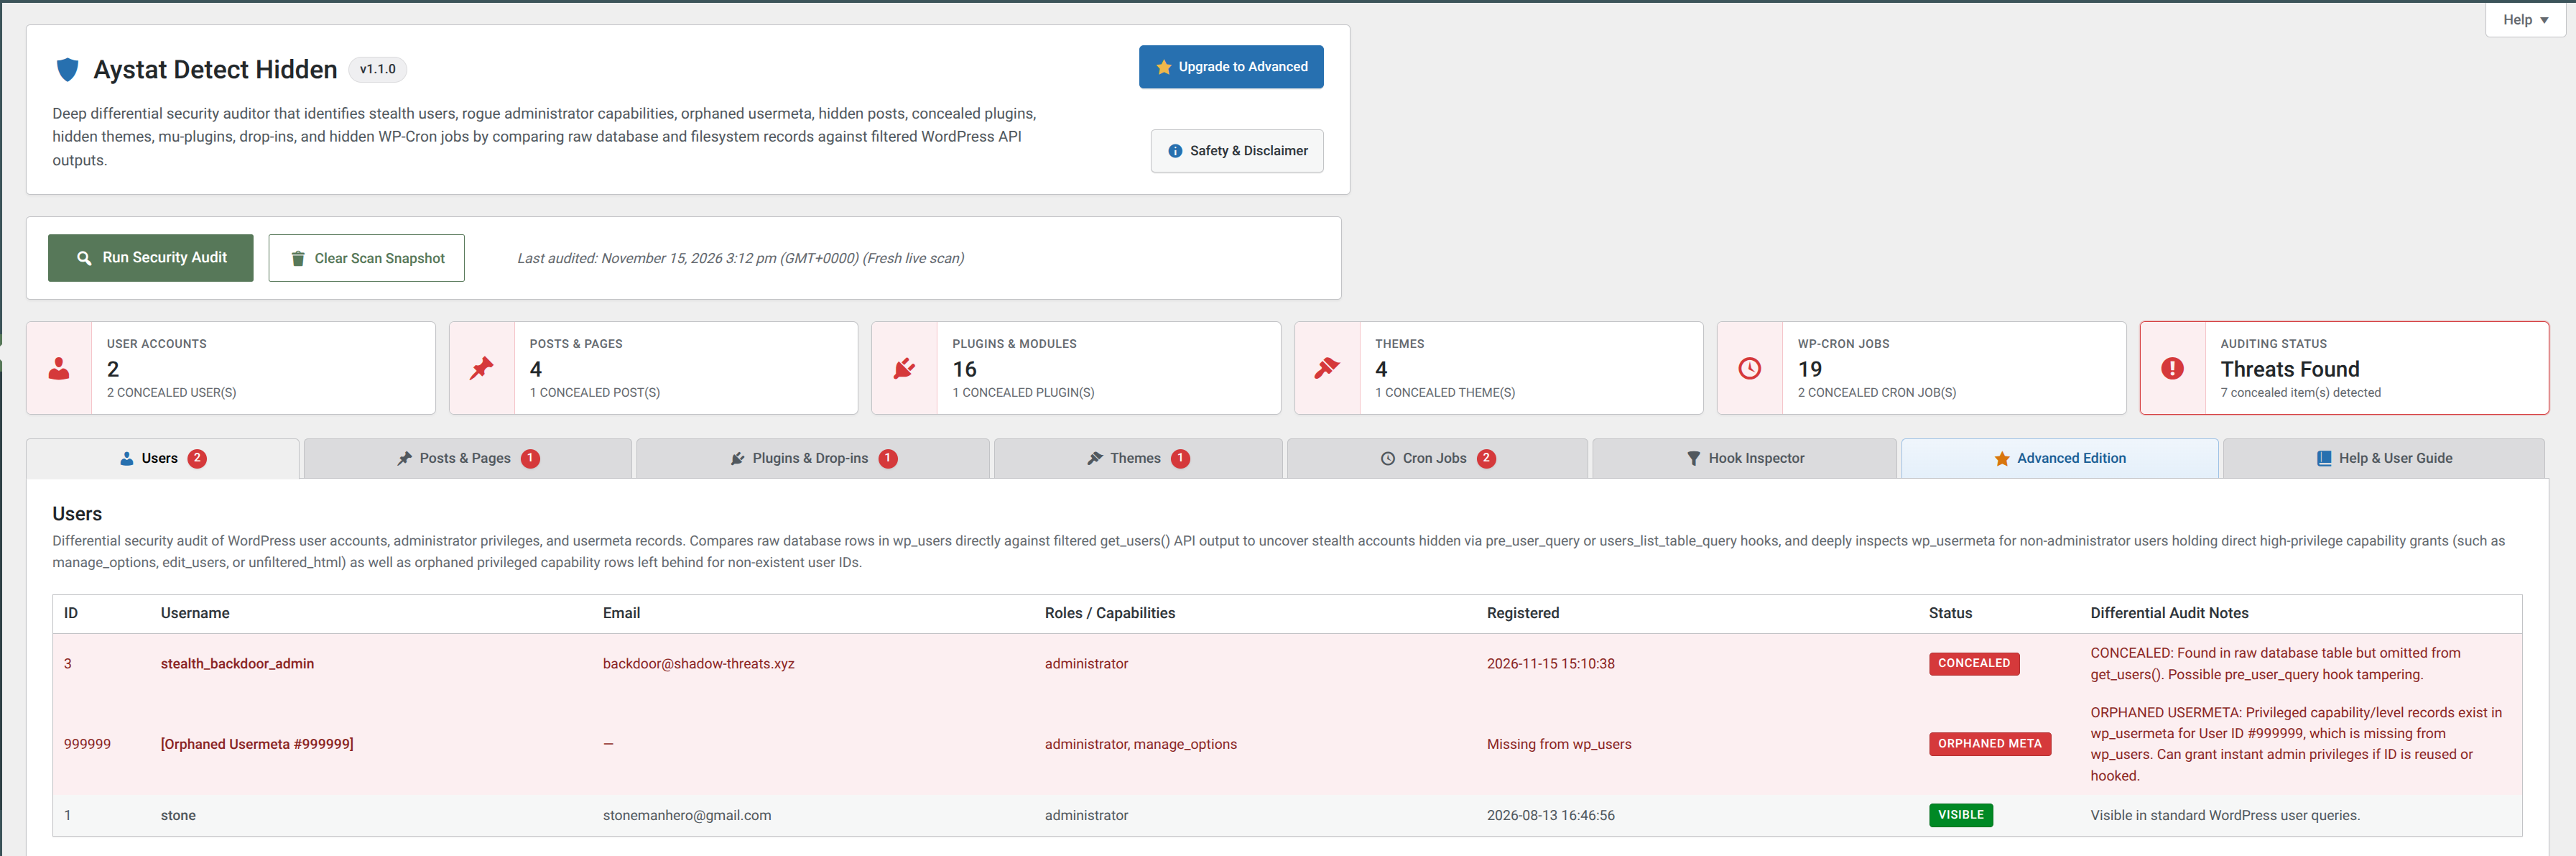
- Hidden Users, Rogue Capabilities & Orphaned Usermeta
Malware adds a rogue administrator account to the
wp_usersdatabase table, then registers a hook onpre_user_queryto filter its own ID out of all standard WordPress queries. Attackers also inject direct high-privilege capability grants (manage_options,edit_users,install_plugins,unfiltered_html) onto low-privilege accounts (such as asubscriberorcustomer), or leave orphanedwp_capabilitiesrows inwp_usermetafor deleted user IDs ready for instant privilege re-hydration. - Concealed Posts & Doorway Pages
Attackers insert SEO spam, phishing forms, or doorway pages into
wp_posts, then manipulatepre_get_postsorposts_whereso the posts never appear in the WordPress Admin post list. - Concealed Plugins
Rogue plugins or backdoors hook into the
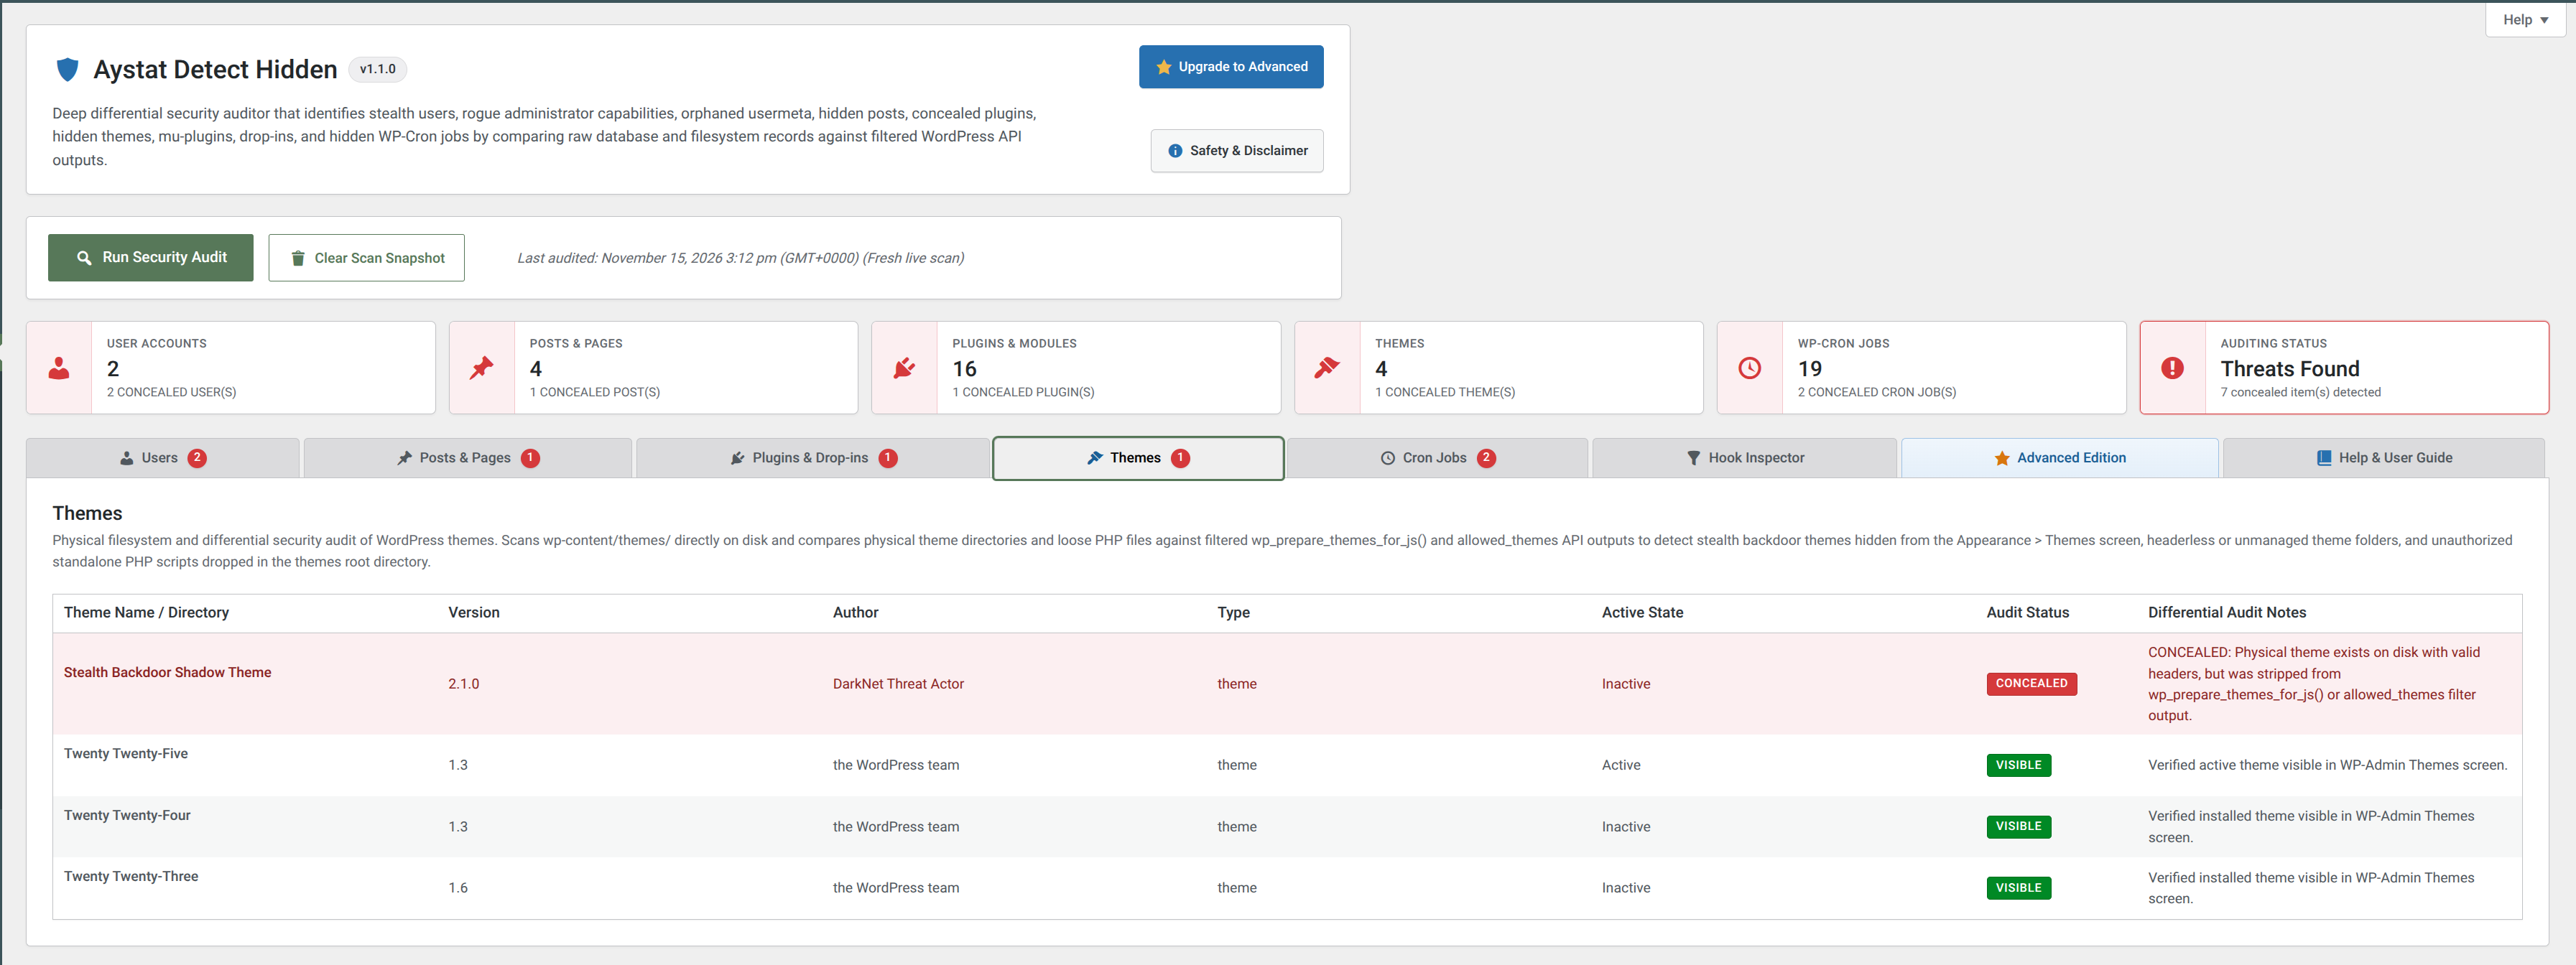
all_pluginsfilter to hide themselves from the/wp-admin/plugins.phpinterface while continuing to execute on every HTTP request. - Concealed & Unmanaged Themes
Attackers plant backdoor themes or rogue PHP shells inside
wp-content/themes/and filterwp_prepare_themes_for_jsorallowed_themesto hide them from Appearance > Themes.
- User & Privilege Differential Audit
Fetches visible users via standard
get_users()queries and compares them against raw database rows queried directly from{$wpdb->users}and{$wpdb->usermeta}. Flags concealed user accounts, non-administrator accounts holding direct high-privilege capability grants (ROGUE CAPS), and orphaned privilegedwp_usermetarecords (ORPHANED META) missing fromwp_users. - Post & Page Differential Audit
Executes
WP_Querywith active filters and compares returned IDs against raw database records from{$wpdb->posts}. Any post or page omitted from the API query is flagged. - Plugin & Component Audit
Physically inspects the plugins directory via
DirectoryIterator(supporting subdirectories, single-file plugins, and unmanaged standalone PHP scripts) and compares physical files against filteredall_pluginshook output. - MU-Plugin & Core Drop-in Inspection
Enumerates all active Must-Use plugins and core architectural drop-ins in the content directory, highlighting high-privilege drop-ins (
db.php,object-cache.php) with elevated security advisories. - Themes Differential Audit
Physically scans
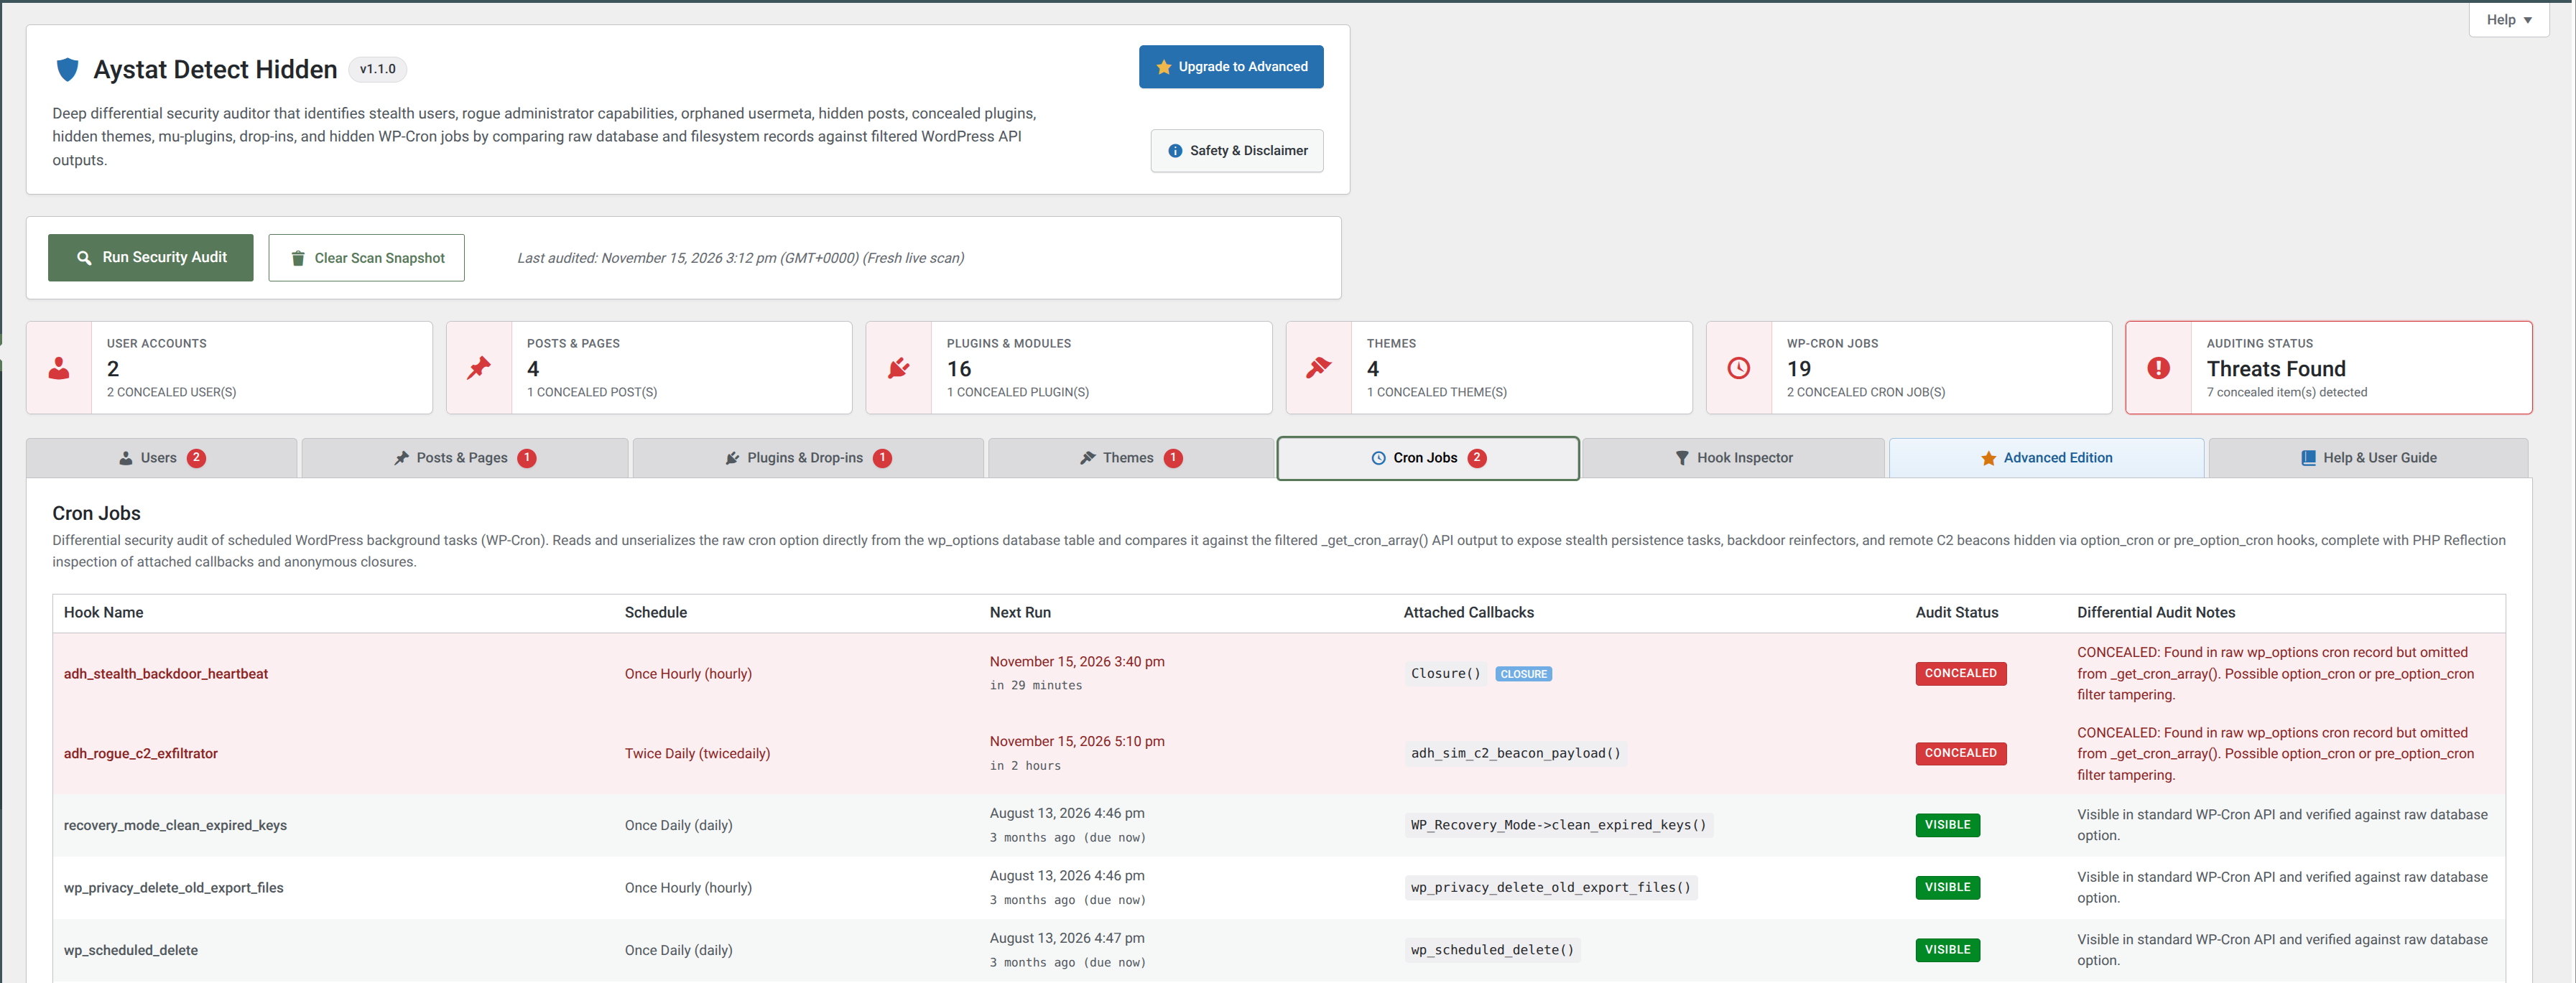
get_theme_root()(wp-content/themes/) viaDirectoryIteratorand compares on-disk theme directories and standalone.phpfiles againstwp_prepare_themes_for_js()andallowed_themesfilter outputs. - WP-Cron Jobs Differential Audit
Compares filtered
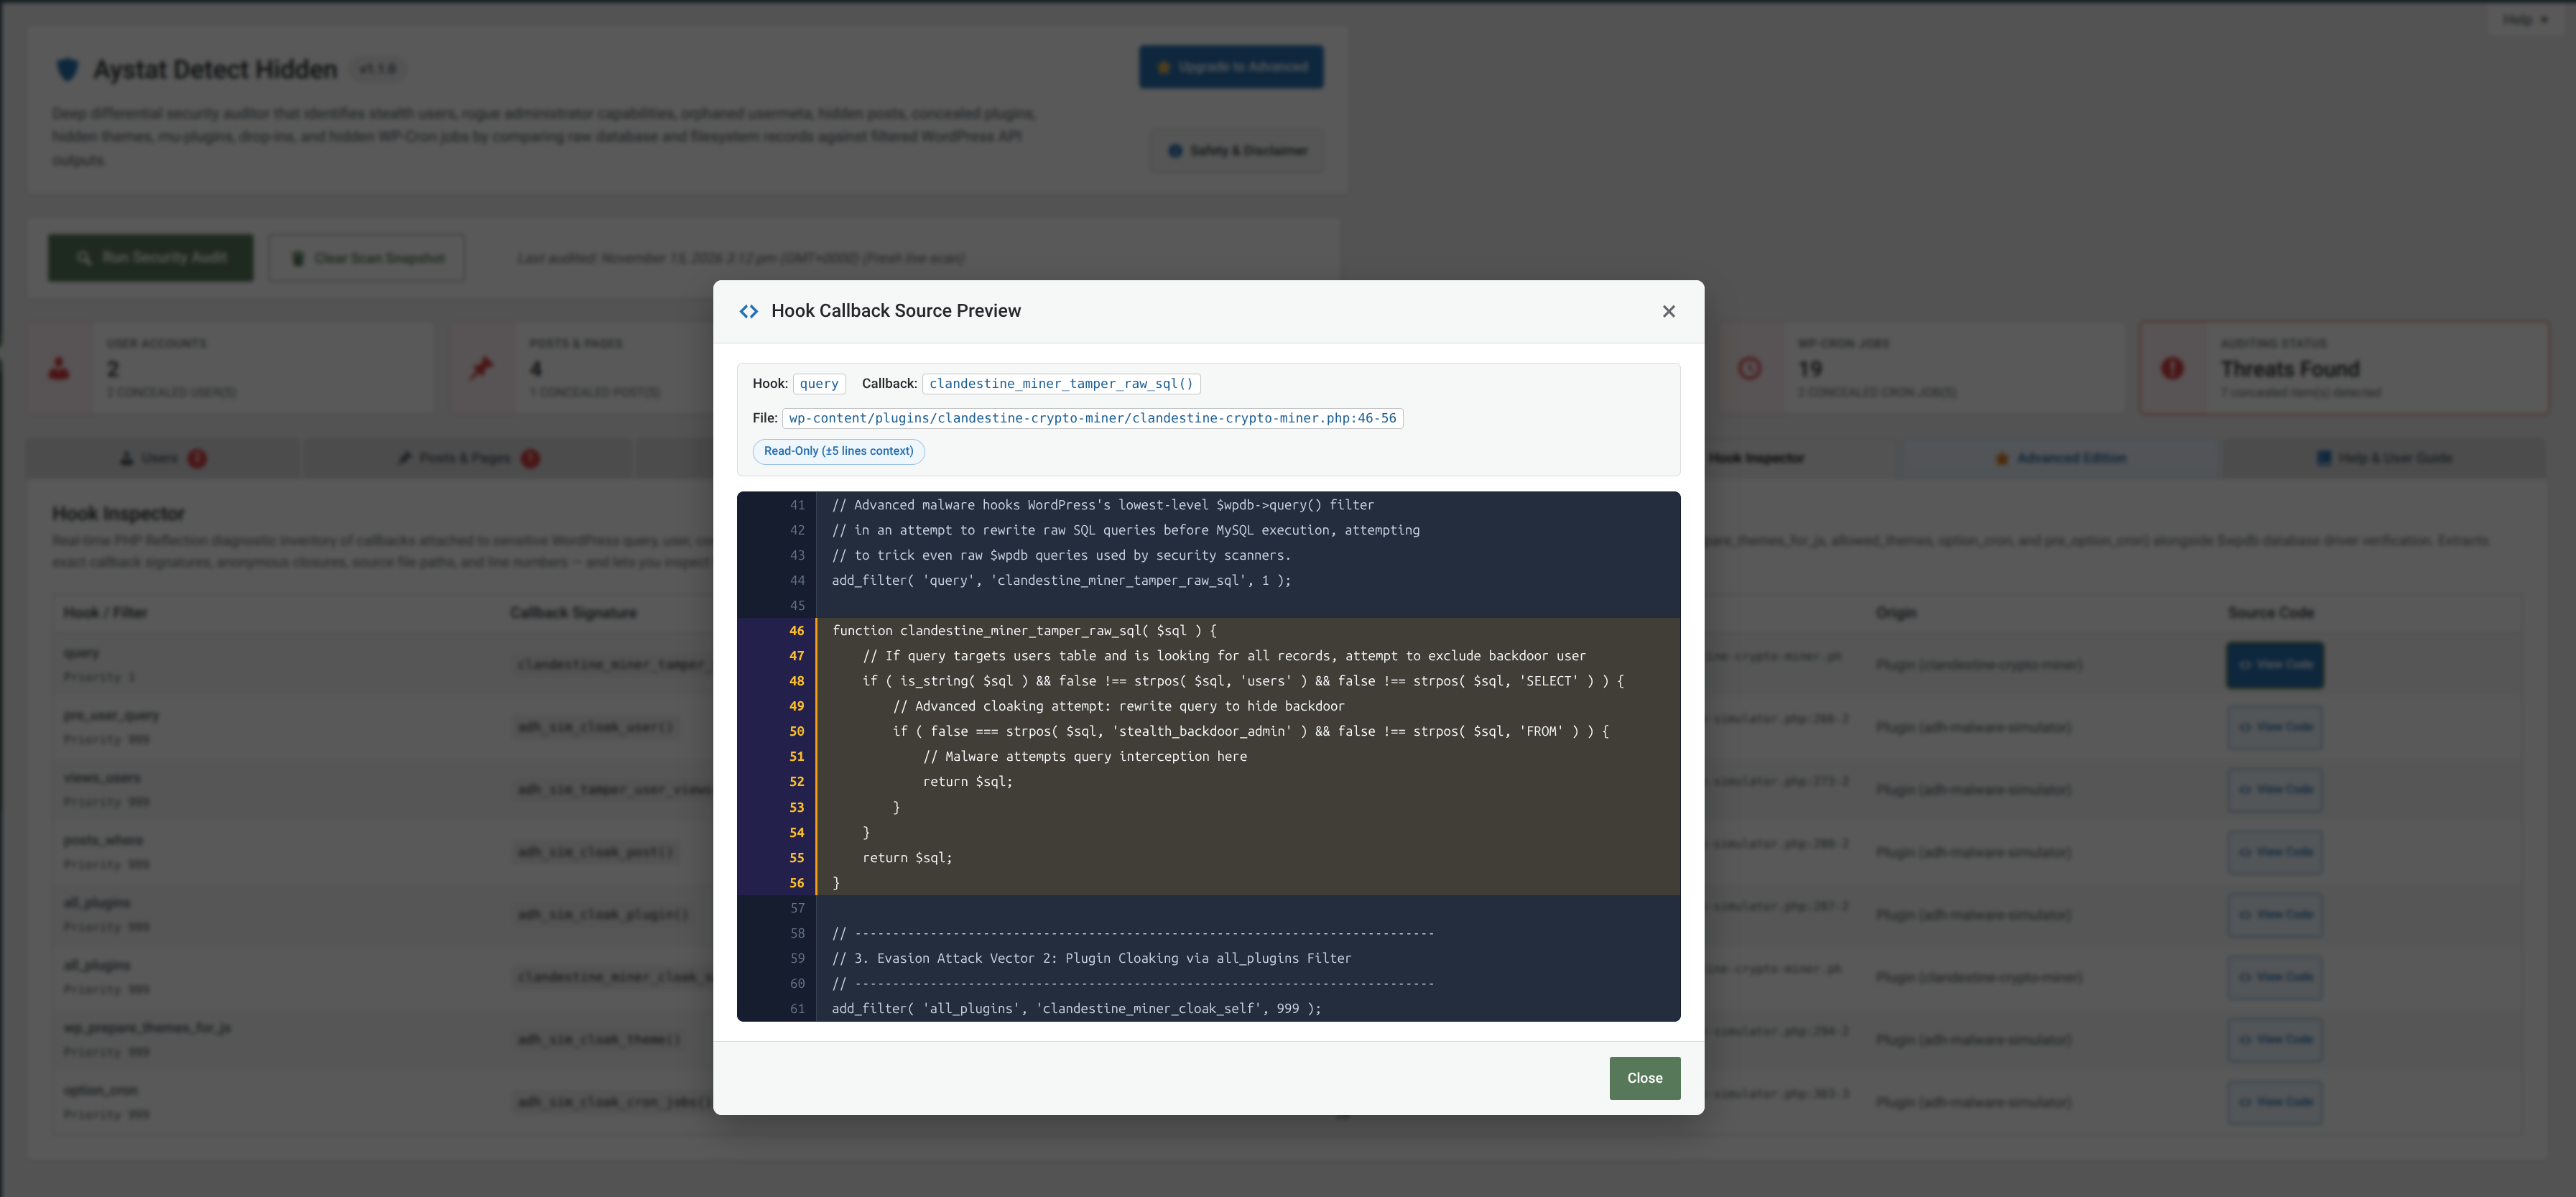
_get_cron_array()schedules against the raw serializedcronoption row in{$wpdb->options}to uncover stealth persistence tasks cloaked viaoption_cronorpre_option_cronfilters, inspecting attached callbacks via PHP Reflection. - Enhanced Hook & Query Inspector with Inline Code Preview
Leverages PHP Reflection to analyze callbacks on sensitive filters (
query,pre_user_query,get_user_metadata,all_plugins,wp_prepare_themes_for_js,allowed_themes,posts_where,option_cron,pre_option_cron), revealing exact file paths, declaration line numbers, anonymous closures, and a 1-click View Code read-only modal with ±5 lines of surrounding context.
- 1-Click Safe Remediation Instantly delete rogue users, purge orphaned privileged usermeta, trash spam posts, delete concealed themes (with active-theme safety guards), unschedule concealed WP-Cron persistence tasks, and delete unauthorized backdoor plugin files with strict path traversal safeguards.
- PDF / JSON Exportable Security Audit Reports Generate client-ready PDF/Print Security Audit Certificates and machine-readable JSON audit snapshots to prove to clients that their database and hooks were audited for stealth malware.
- WP-CLI Automation (
wp aystat audit --format=json) Run differential security audits across agency multi-site fleets, SSH scripts, and CI/CD pipelines from the command line. - False-Positive Whitelisting Ignore approved exceptions (custom tools, custom capabilities, themes, or intentional drop-ins) with a single click, keeping your audit reports clean.
- Autonomous 24/7 Background Scans Scheduled WP-Cron runner with configurable scan frequencies (Hourly, 2h, 3h, 6h, 12h, Daily, Weekly).
- Smart State-Diff Email Alerts Zero email fatigue — alerts dispatched only when new threats appear or threat status changes.
- Priority Security Support Direct developer assistance and priority updates.
安装:
- Upload the
aystat-detect-hiddenfolder to the/wp-content/plugins/directory, or install directly through the WordPress plugin installer. - Activate the plugin through the 'Plugins' screen in WordPress.
- Navigate to Tools > Detect Hidden in your WordPress admin menu.
- Click Run Security Audit to execute a full differential analysis.
屏幕截图:
常见问题:
Does this plugin affect frontend site speed?
No. Audits execute only when an administrator triggers a scan in the admin dashboard. Zero queries or hooks are added to front-end visitor traffic.
What makes this scanner different from other security plugins?
Standard security plugins ask WordPress APIs for lists of users, plugins, and themes. If stealth malware has hooked pre_user_query, all_plugins, or wp_prepare_themes_for_js, standard plugins are blinded by the same hooks. Aystat Detect Hidden queries the database tables and filesystem directly to uncover hidden discrepancies.
What is the difference between Free and Advanced?
The Free version on WordPress.org provides 100% complete differential auditing across users, privilege grants, orphaned usermeta, posts, plugins, drop-ins, themes, WP-Cron jobs, and hook inspection (including inline source code preview). The separate Advanced edition adds 1-click automated threat deletion (users, orphaned usermeta, posts, plugin files, themes, cron jobs), false-positive whitelisting, exportable PDF & JSON client security audit reports, WP-CLI automation (wp aystat audit --format=json), and 24/7 background WP-Cron scans with smart email alerts.
更新日志:
- Added Hidden & Unmanaged Themes Differential Scanner (
Themesmetric card and tab), comparing physicalwp-content/themes/directories and loose.phpfiles againstwp_prepare_themes_for_js()andallowed_themesoutputs. - Upgraded Users Scanner to detect Rogue Administrator Capabilities (
ROGUE CAPS, direct high-privilege capability grants on non-administrator accounts) and Orphaned Privileged Usermeta (ORPHANED METAinwp_usermetawith no matchingwp_usersrecord). - Added Hidden WP-Cron Jobs Differential Scanner (
cronoption differential) in a dedicated Cron Jobs tab, comparing_get_cron_array()against raw{$wpdb->options}records and inspecting attached callbacks via PHP Reflection. - Added Inline Source Code Preview Modal ("View Code") to the Hook Inspector, allowing administrators to inspect the exact PHP callback lines (with ±5 lines of surrounding context) in read-only mode.
- Added
wp_prepare_themes_for_js,allowed_themes,get_user_metadata,pre_option_cron, andoption_cronmonitoring to the Hook & Query Interception Inspector. - Moved Hook & Query Interception Inspector to a dedicated dashboard tab located between Cron Jobs and Advanced Edition.
- Hook and query driver inspections are now strictly informational diagnostics and no longer count toward active threats or auditing status.
- Redesigned 6-card metric dashboard with full-height icon strips, dynamic threat icon highlighting, WordPress site timezone timestamp formatting, and threat-only circular tab count badges.
- Updated User Guide, contextual Help tabs, and documentation.
- Added Enhanced Hook & Query Interception Inspector using PHP Reflection: extracts exact file paths, line numbers, closure detection, and provenance classification.
- Added actionable Threats Found card navigation with automatic tab switching and smooth scrolling to flagged items.
- Added False-Positive Whitelist (Ignore/Unignore) feature to approve legitimate exceptions.
- Added Clear Scan Snapshot action to reset cached scan states safely.
- Updated file and directory path resolution to use core WordPress path functions.
- Removed all locked/premium-gated code to ensure 100% free, unrestricted functionality in the WordPress.org edition.
- Added defense-in-depth low-level SQL query filter isolation to defeat in-memory query rewrites.
- Added critical alert detection for active hooks on the WordPress
queryfilter. - Added unmanaged standalone PHP script and headerless plugin directory detection.
- Added elevated security warning badge and advisories for
db.phpandobject-cache.phpdrop-ins. - Added runtime database driver class integrity checks.
- Added perceptible live scanning states and execution time reporting.
- Added persistent audit state on page reload.
- Scalability optimizations for databases with 30,000+ users and high post counts.
- Enhanced button flex layout and Dashicons alignment to prevent line-wrapping.
- Initial public release with differential user, post, and plugin auditing.