
Beardo Multisite Activation Console
| 开发者 | beardotools |
|---|---|
| 更新时间 | 2026年9月28日 20:12 |
| 捐献地址: | 去捐款 |
| PHP版本: | 8.0 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
- Agencies and hosts managing client sites on one network
- Universities, franchises, and publishers with dozens or hundreds of subsites
- Anyone who has ever bulk-activated a plugin and immediately regretted it
- Learn more: beardo.tools/multisite-activation-console
- Get help: help.beardo.tools
安装:
- Upload the plugin folder to
/wp-content/plugins/ - Network Activate it from Network Admin → Plugins
- Open Network Admin → Plugins → Activation Console
屏幕截图:
常见问题:
Does this work on a regular (single-site) WordPress install?
No. The console is built for multisite networks and must be network activated. On a single-site install it does nothing.
Can it break my network by turning off something critical?
It's designed specifically so it can't. Changes run one at a time with a health check first, so a problem on one site stays on that site. And a protected list stops it from ever deactivating itself or anything that would lock a super admin out. Developers can add to that list with the beardo_mac_protected_plugins filter.
Who can use the console?
Only super admins (users with the manage_network_plugins capability). Regular site admins won't see it.
What does the audit log record?
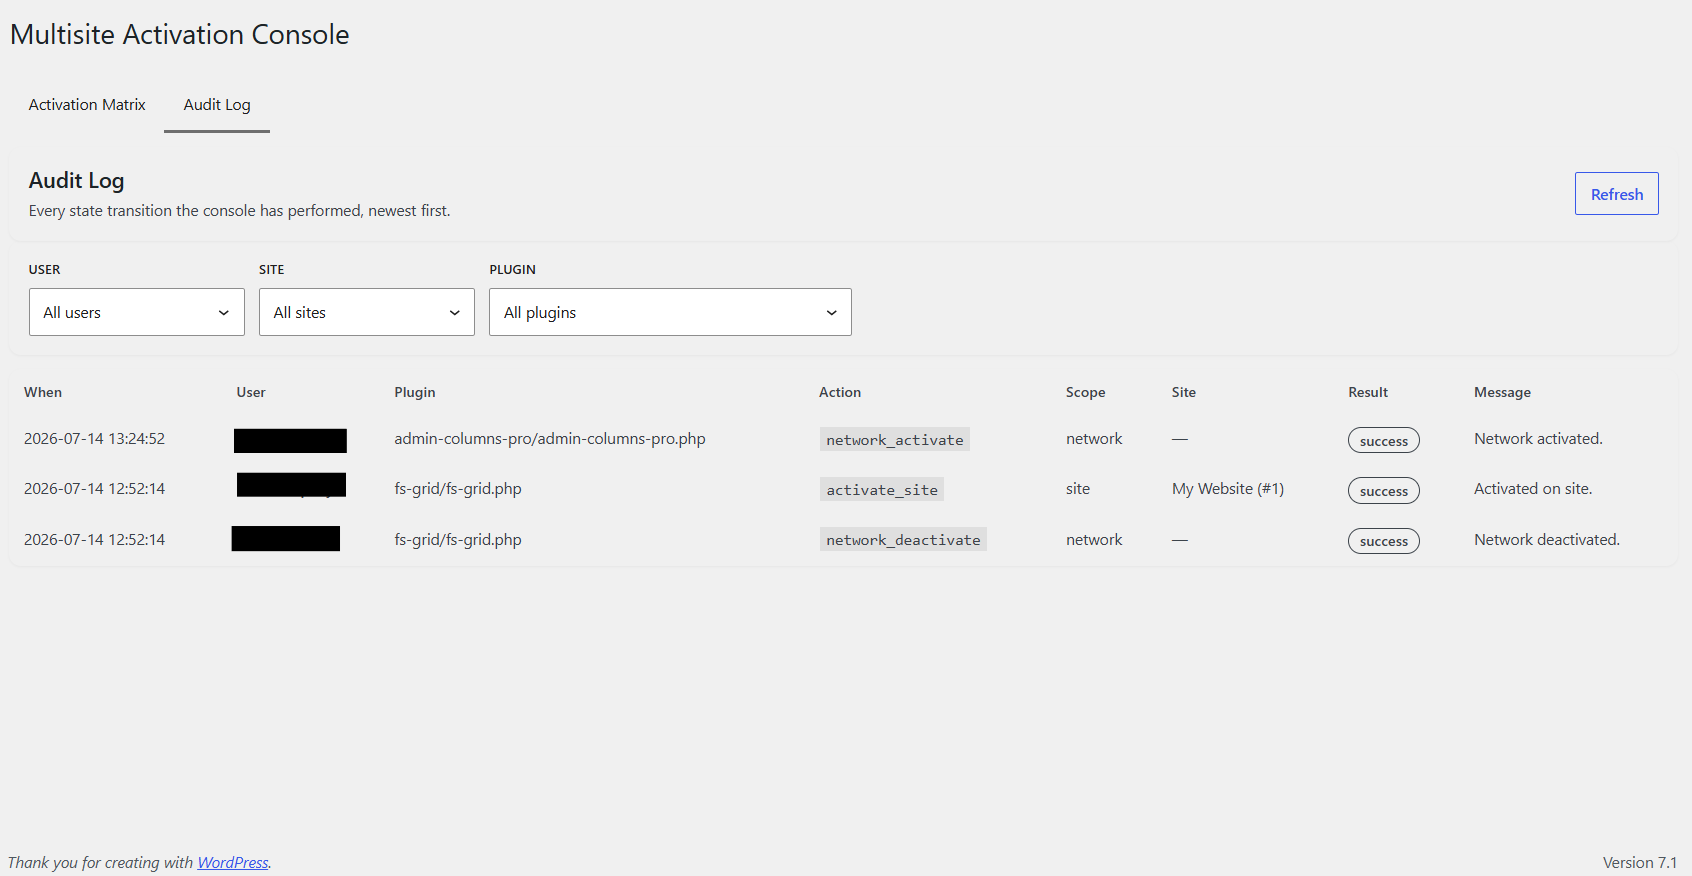
Who made the change, which plugin, what they did, which site it applied to, whether it succeeded, and when. You can filter the log by person, site, or plugin.
Does it send any data anywhere?
No. There are no external calls, no analytics, and no tracking of any kind.
What happens if I uninstall it?
The audit log table is removed. Nothing else on your network is touched — your plugins stay exactly as they were.
更新日志:
- Security hardening: stale-entry cleanup is refused unless the plugin is still network active, so it can never switch a plugin off on a site without running its deactivation hook.
- Security hardening: per-site activation is refused for network-only plugins, matching WordPress core.
- Security hardening: stricter validation of console REST requests.
- New: Export the audit log as CSV or Excel (.xlsx) from the Audit tab. Choose between the currently filtered entries and the full log. Exports include every matching entry, not just the rows on screen (up to 10,000 rows per file).
- CSV exports are protected against spreadsheet formula injection.
- Excel export requires PHP's zip extension; a clear message is shown if it is missing.
- Tested up to WordPress 7.1.
- Initial public release.
- Activation matrix — every plugin's state (network active, per-site active, or off) across all subsites in a single DataViews grid
- Safe transitions — one state change per request, so a fatal error on one subsite never takes down the whole batch
- Dry-run validation — backend health checks run before any change is executed
- Stale dual-state cleanup — detects and strips redundant per-site entries for network-active plugins without deactivating anything
- Dead-reference cleanup — removes activation entries for plugins no longer present on disk
- Audit log — every state transition recorded network-wide with acting user, target site, action, and result, filterable by user, site, and plugin
- Guardrails — a filterable protected list (
beardo_mac_protected_plugins) prevents the console from deactivating itself or locking out a super admin - Admin theme compatibility — console colors flow through a plugin-scoped CSS token layer, and the focus ring follows the user's admin color scheme
- Full RTL support This release follows an internal beta series; 1.0.0 is the first version published to WordPress.org.