Checkout Origin Guard
| 开发者 | potar |
|---|---|
| 更新时间 | 2026年10月8日 04:59 |
| 捐献地址: | 去捐款 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 6.9 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
- Bot Block (traffic level)\ Detects and throttles abusive requests before they become orders:
- Analyzes user agents, referrers, and known bot signatures
- Counts final checkout submissions in fixed one-minute windows for classic AJAX and Checkout Blocks
- Supports monitor, soft, and hard blocking modes
- Built-in allowlist for search engines, uptime monitors, and core WordPress services
- Company Shield (checkout level)\ Validates business identity and email quality at checkout:
- Flags suspicious or synthetic business names
- Detects repeated syllables, odd vowel ratios, and gibberish patterns
- Identifies disposable email domains and role-based accounts (admin, info, sales, etc.)
- Can run in:
- Monitor; log and annotate orders
- Soft; create the order and automatically place it on hold or pending
- Hard; block checkout with a user-facing error message
- Payment AVS signals (post-payment; optional)\ For gateways that expose AVS results in order meta, Checkout Origin Guard can treat “AVS: U; unavailable / not checked” as a risk signal:
- Does not change how your gateway authorizes or captures payments
- Can be configured to:
- Ignore the signal
- Add an order note only
- Add an order note and bump a risk-score meta field
- Put the order on hold for manual review
- Uses flexible pattern matching; can scan specific gateway meta keys or fall back to scanning all order meta for common “AVS: U” messages such as the PayPal string
- Off by default; you opt in and choose the behavior
- 🛡️ Bot Block; Detects and blocks automated bots by analyzing user agents, referrers, and checkout behavior patterns.
- ⚡ Checkout Attempt Limits; Scores more than ten final order submissions from one IP within a fixed minute, without counting cart refreshes, coupon changes, or payment callbacks.
- 🧠 Company Shield; Reviews configured deny fragments, disposable email domains, and corroborating company-name patterns at checkout.
- 🌎 Allowlist Controls; Preserve access for search engines, uptime monitors, and essential WordPress and WooCommerce services.
- 🔒 Hard / Soft / Monitor Modes; Choose between logging only, soft blocking, or full hard blocking.
- 🧾 AVS “U” Risk Signals (optional); Treat “Address not checked / unavailable” as a post-payment risk signal; add notes, increase risk score, or hold the order.
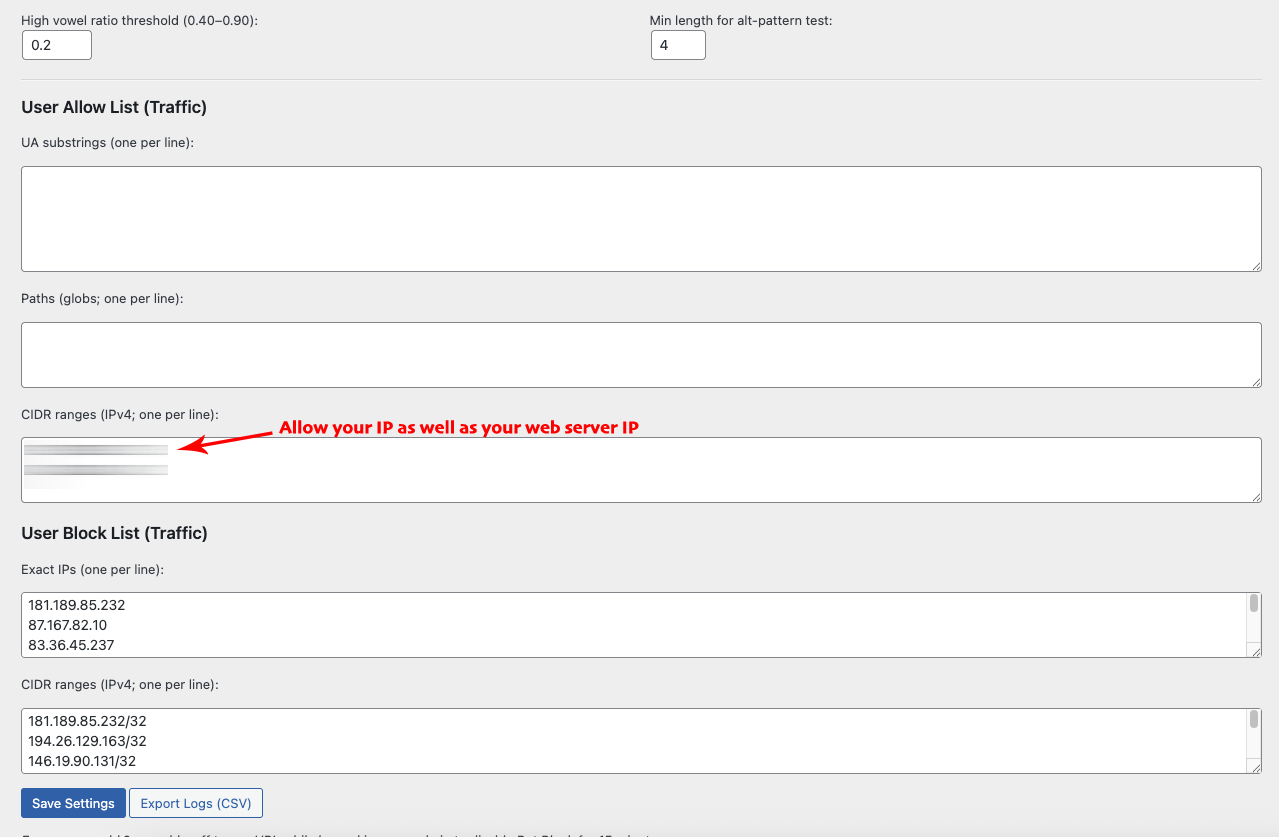
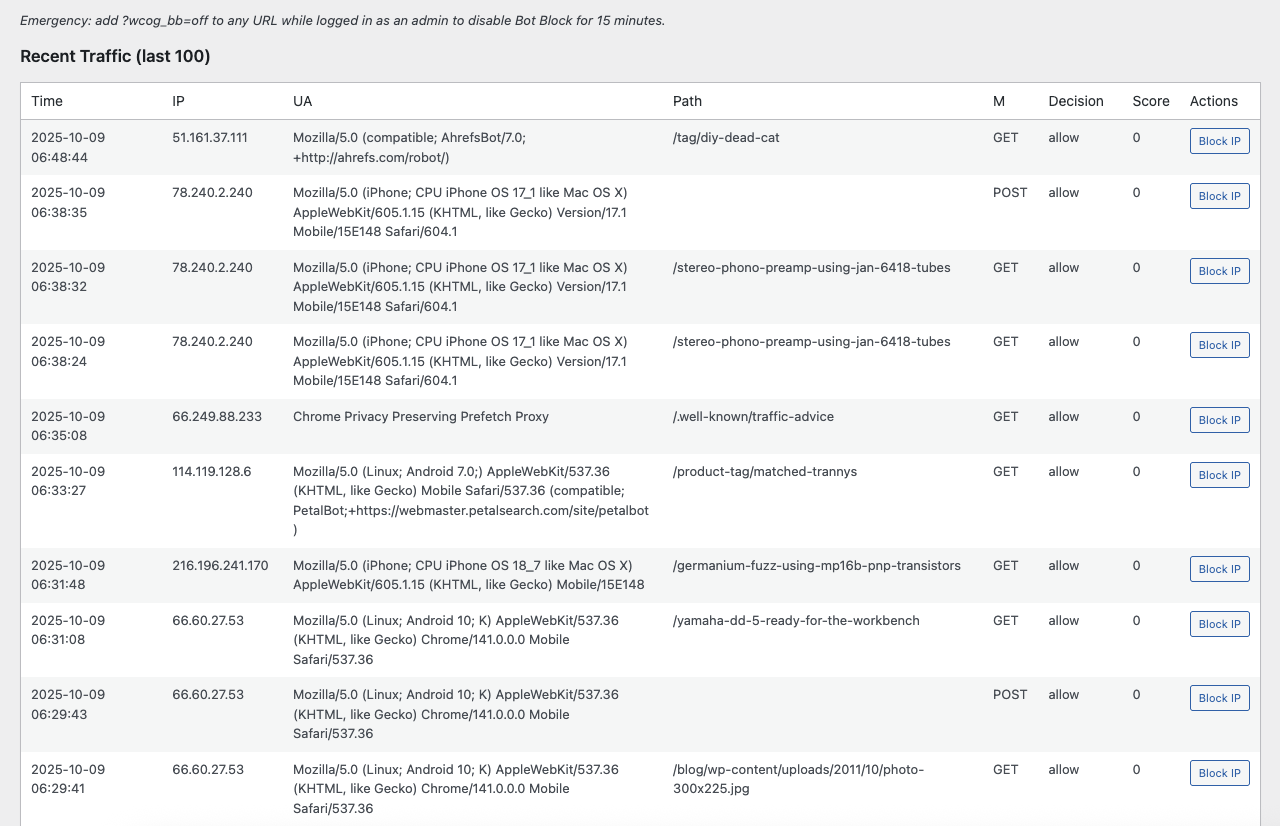
- 🗂️ Log Viewer; See activity including timestamps, IPs, user agents, paths, and detection outcomes.
- 🧩 One-Page Dashboard; Configure settings, review logs, and manage allow/deny lists from a single screen.
- 🚫 Manual Block / Unblock; Instantly remove or restore access for specific IPs with one click.
- 💾 CSV Export; Download checkout-origin activity logs for security review or record keeping.
- Card testing and BIN probing
- Fake business registrations and spam accounts
- Automated scripts hammering your checkout endpoints
- Reduce chargeback and fraud risk
- Keep your order list clean and reviewable
- Shorten the time spent cleaning up junk orders and bogus signups
- Prevent card testing or order spam
- Review orders with suspicious company names and email addresses
- Detect rapid repeat checkout attempts from the same IP
- Block suspicious POST requests that hit checkout endpoints
- Add an extra layer of review for orders where the gateway reports “AVS unavailable / not checked”
- Maintain cleaner order history and logs for real customers
安装:
- Upload the plugin folder to
/wp-content/plugins/checkout-origin-guard/ - Activate the plugin through the Plugins menu in WordPress.
- Go to WooCommerce → Checkout Origin Guard in the admin sidebar (or Tools → Checkout Origin Guard if WooCommerce is not present).
- Configure your preferred mode:
- Monitor; log only, no blocking (recommended starting point)
- Soft Block; log and slow or defer traffic
- Hard Block; log and deny abusive access entirely
- Review logs, then fine-tune detection thresholds and allowlists before enabling Soft or Hard modes in production.
- Optional; enable AVS “U” handling under Payment AVS Signals, starting with “Add order note only” before switching to “Hold for review” on higher-risk stores.
屏幕截图:
常见问题:
Does this plugin affect SEO bots or uptime monitors?
Google, Bing, and Apple search crawlers are allowed after cached reverse and forward DNS verification. Configured AI and uptime User-Agent allowances apply to GET and HEAD traffic. Known exploit probes are checked before allowances. Other crawler identities remain subject to scoring.
Will it block my own IP?
Your logged-in administrator sessions are never blocked by Bot Block. If you manually block your own address, you can unblock it from the plugin dashboard with one click.
Does it replace a firewall or security plugin?
No. Checkout Origin Guard complements existing firewall or security plugins. It focuses specifically on WooCommerce checkout behavior and identity quality, rather than broad HTTP filtering.
Does this change how my gateway processes payments?
No. Checkout Origin Guard does not interfere with your payment gateway’s authorization or capture logic. The optional AVS “U” feature runs after the gateway has responded and only:
- Adds order notes
- Adjusts a risk-score meta field
- Optionally changes the WooCommerce order status to “on-hold” for manual review
What is AVS “U” and why should I care?
AVS (Address Verification Service) compares billing address details against card-issuer records. The code “U” usually means:
- Address not checked, or
- Service unavailable, or
- Acquirer had no response
I do not know my gateway meta keys. Can I still use AVS detection?
Yes. The AVS settings include an optional Gateway Meta Keys list. If you know the exact meta keys your gateway uses to store AVS results, you can enter them for more precise scanning. If you leave the field blank, Checkout Origin Guard will scan all order meta values for common AVS U patterns, including PayPal-style messages such as:
AVS: U: Unavailable / Address not checked, or acquirer had no response. Service not available.
Can I export my logs?
Yes. All log data can be exported to CSV from the plugin dashboard for review, forensics, or integration with external tools.
Where is log data stored?
Logs are stored in a dedicated database table inside your existing WordPress database. They contain timestamps, IP addresses, user agents, paths, HTTP methods, and a decision flag. No external services are used; all data remains on your server. You can clear or truncate this table using your preferred database tools if you want to reset history.
更新日志:
- Added final-checkout attempt limits for classic AJAX and Checkout Blocks with fixed one-minute windows.
- Added verified search crawler handling and exploit detection before allowlisting.
- Removed hard rejections based solely on missing origin data or lowercase names; preserved email checks when company names are allowed.
- Added trusted proxy controls, richer traffic logs and CSV exports, privacy information, and scheduled log retention.
- Preserved admin bypass, payment callback handling, AVS options, and user-profile IP controls.
- Prevented Bot Block from interrupting WooCommerce checkout and payment AJAX transport requests that can surface as generic payment-source errors.
- Hardened admin input handling for allowlists, blocklists, disposable-domain patterns, and emergency bypass activation.
- Reduced repeated runtime work by caching normalized settings and precompiled path allow rules during each request.
- Expanded settings-page guidance so advanced Company Shield thresholds are easier for non-technical store owners to tune safely.
- Added two high-signal checker heuristics: all-lowercase billing first+last name; and unknown checkout origin (no referrer and no UTM).
- When triggered, these flags can bump the order risk score meta for faster review and safer automation.
- Added optional AVS “U” handling as a post-payment risk signal; can add notes, bump a risk-score meta field, or hold orders for review.
- Refined Company Shield heuristics and help text for business and email validation.
- Minor performance and logging improvements in the checkout validation flow.
- Confirmed compatibility with WordPress 6.9.
- Updated code to align with upcoming WordPress coding and security guidelines.
- Improved IP hard block stability and unblock handling.
- Added real-time log refresh option.
- Enhanced Company Shield heuristics for email and business name detection.
- Unified all settings on one page with persistent values.
- Performance improvements and code cleanup.
- Added CSV export for logs.
- Added referrer and nonce validation checks.
- Expanded allowlist for common search engine bots.
- Fixed settings persistence and default value population.
- Added Populate Defaults button.
- UI refinements and improved table layout.
- Merged “Bad User Patterns” module into core.
- Added company/email heuristics and rate-limit detection.
- New single-page admin interface.