
DevaGroup DevaGuard – Site Security Monitor
| 开发者 | kasroka |
|---|---|
| 更新时间 | 2026年10月30日 17:45 |
| PHP版本: | 7.2 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
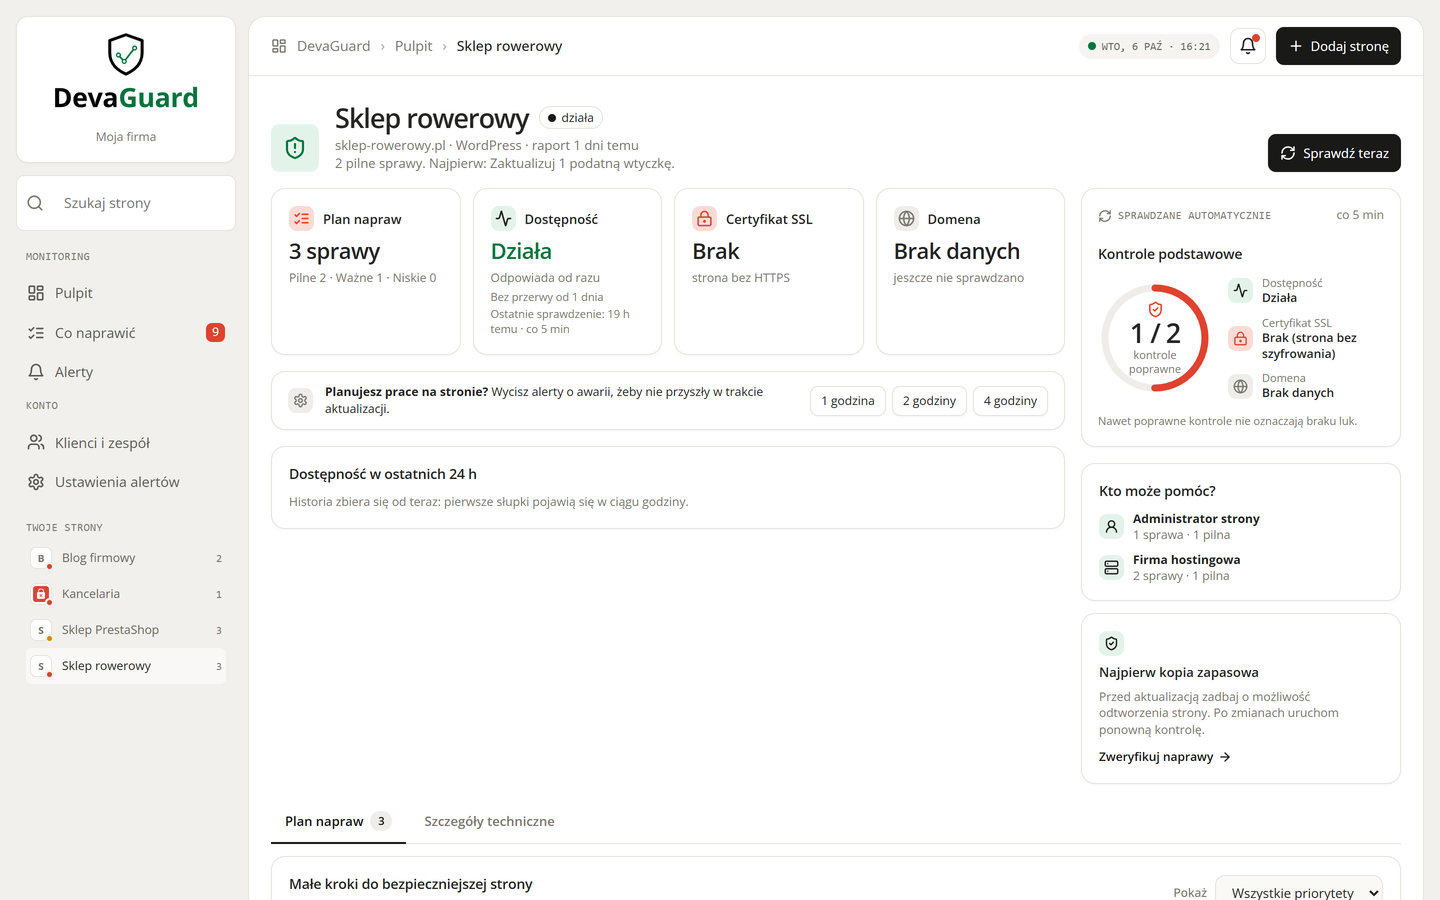
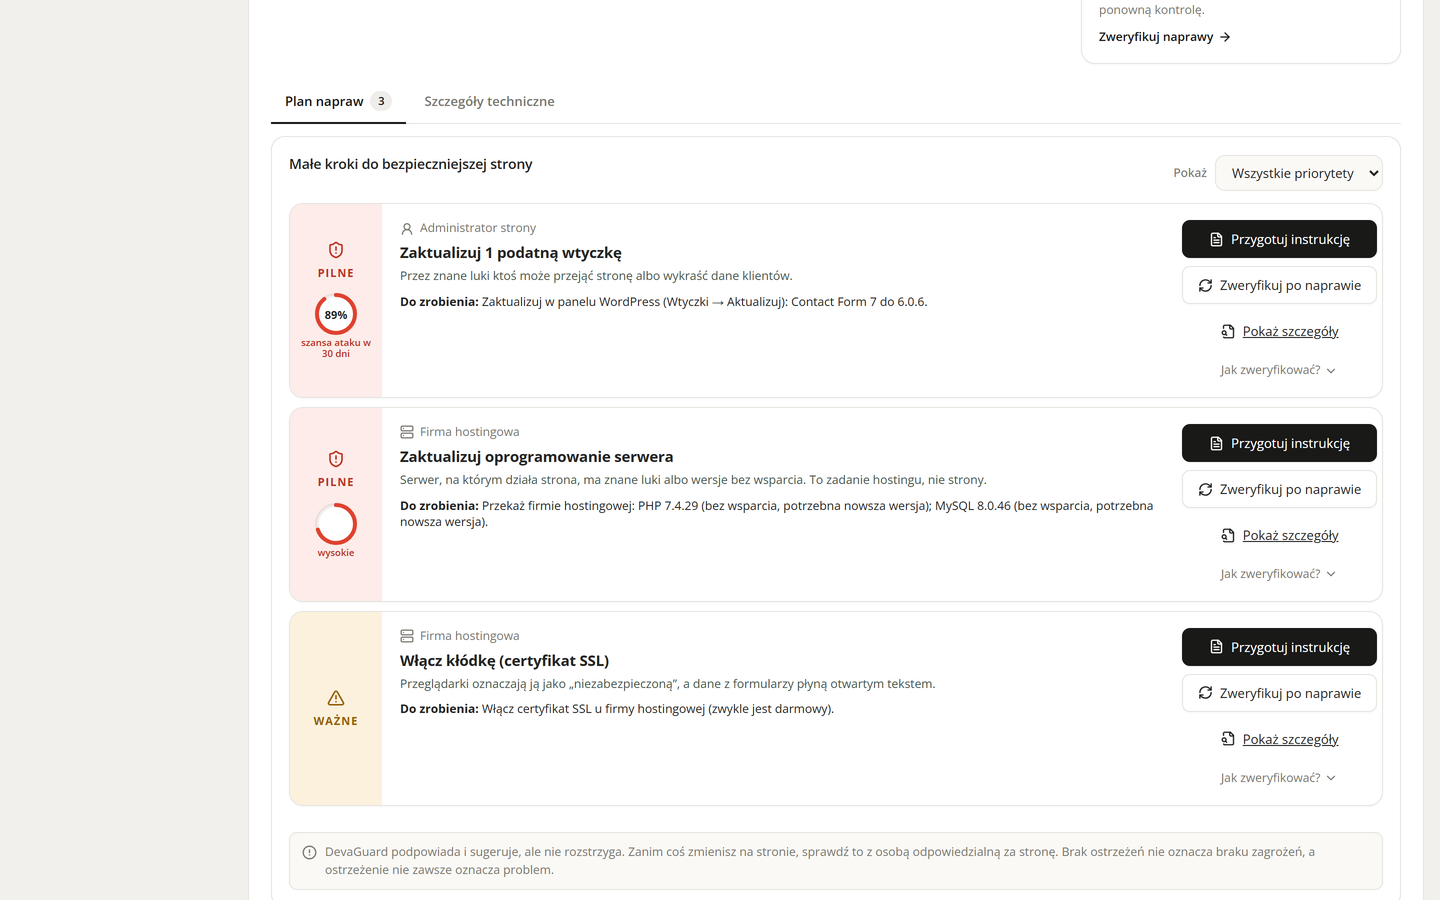
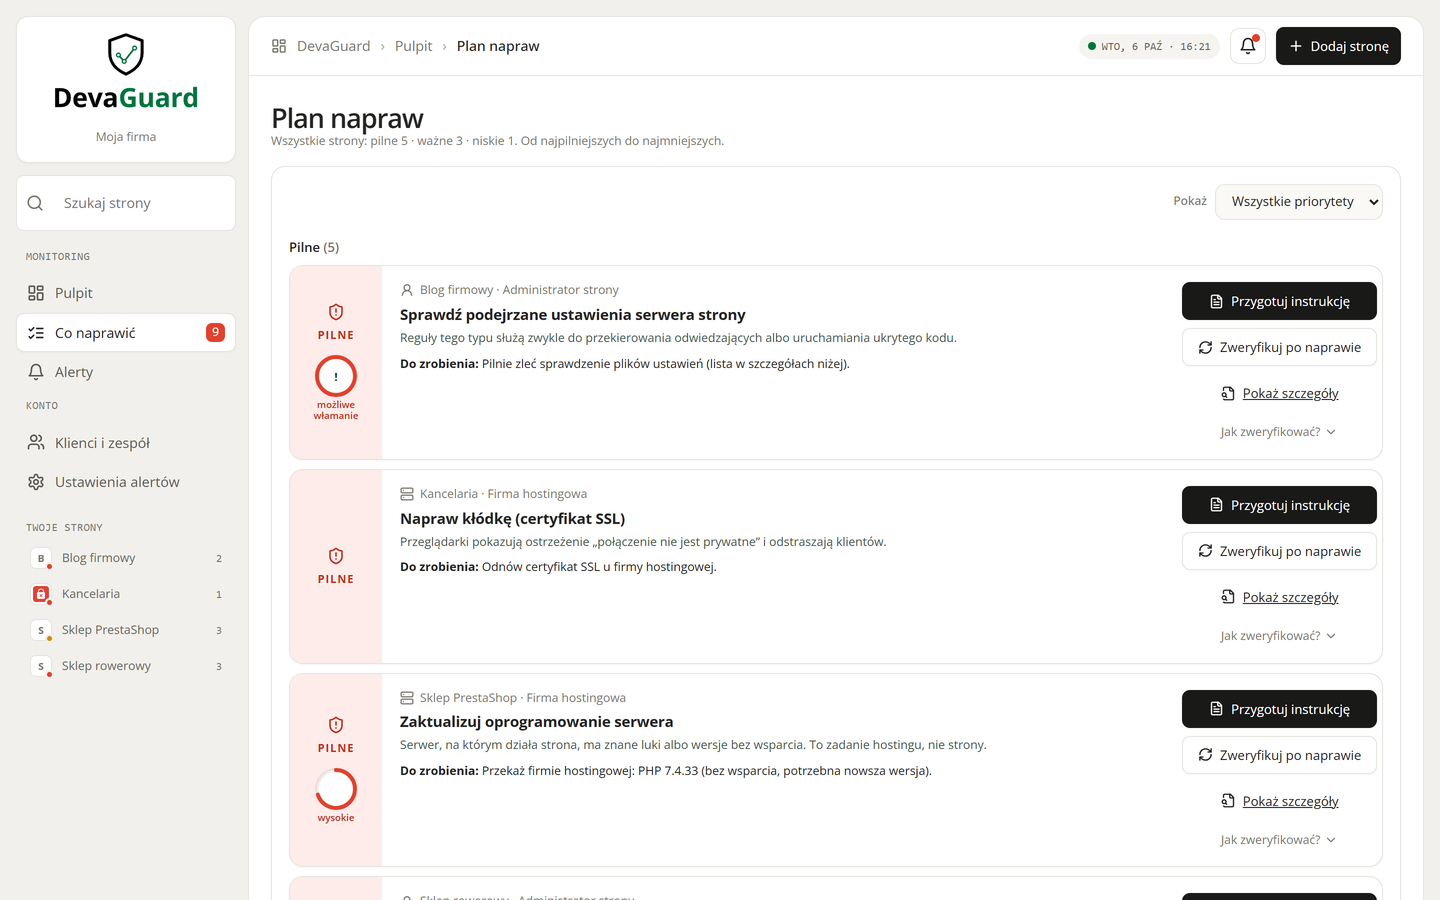
DevaGuard is a website security monitoring service run by DEVAGROUP sp. z o.o., Kraków, Poland. This plugin connects your site to a DevaGuard dashboard. Once a day, and right after every update, it collects information about your site and sends it to the DevaGuard server you configure. The dashboard turns it into a plain-language repair plan: what is urgent, why it matters and who should fix it.
The plugin is read-only. It never changes your content, settings or files, never installs anything and does not expose any endpoint on your site.
What the plugin reports:
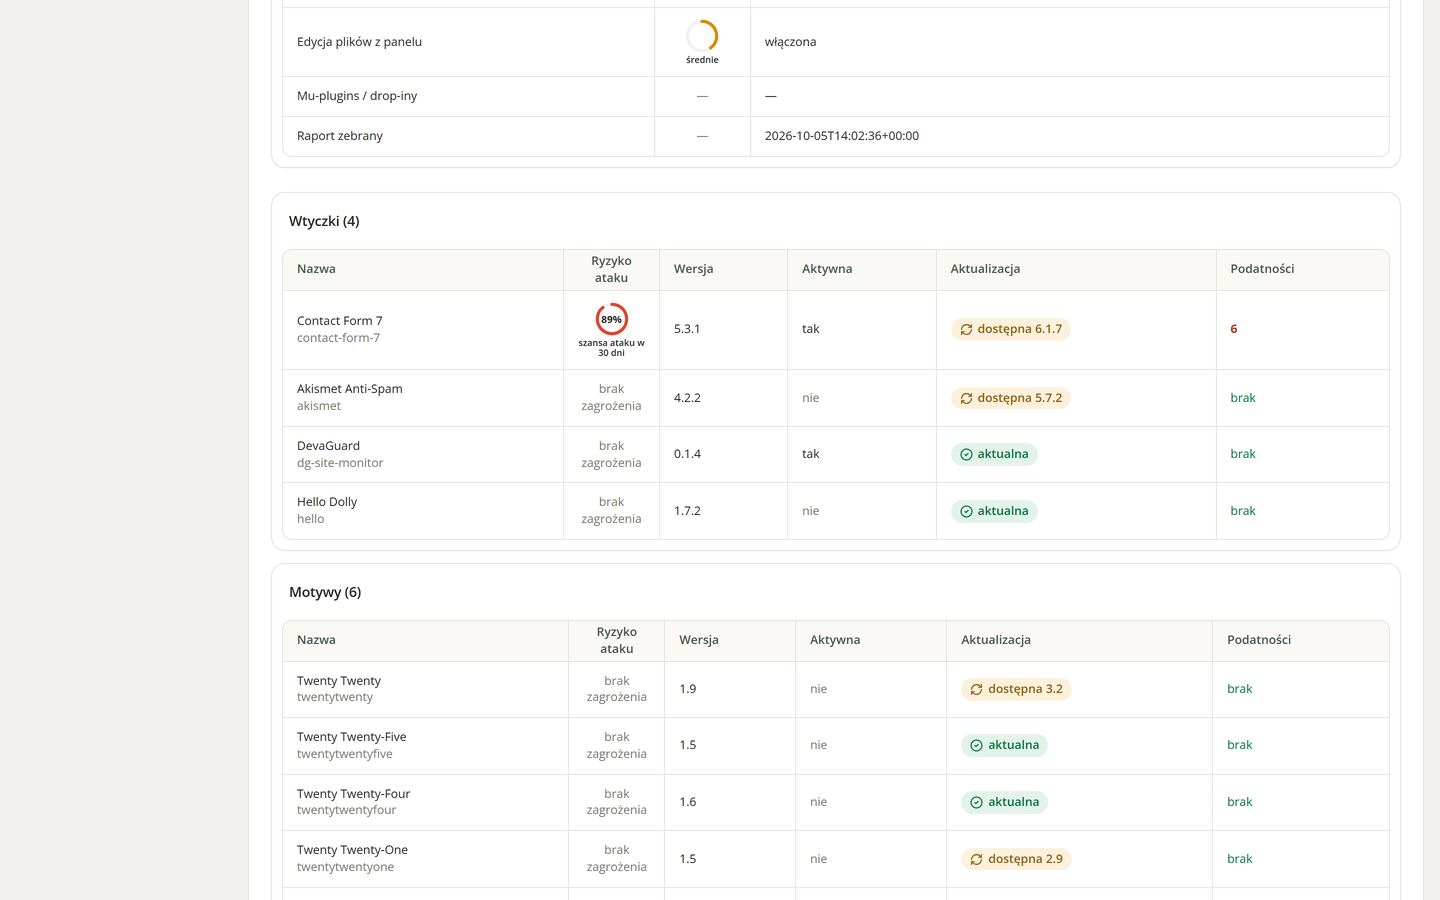
- WordPress, PHP, database and web server versions, plugins and themes with available updates.
- File integrity: core and WordPress.org plugin files compared with official checksums, PHP files in uploads, unknown PHP files in wp-content, files changed in the last 7 days.
- Suspicious rules in .htaccess, .user.ini and wp-config.php (only findings and a file hash are sent, never the file contents).
- Injected scripts in posts, options and post meta (only the location and type of finding are sent, never the content).
- Administrator events: new administrator, e-mail or password change, login from a new network, failed login bursts. Logins and IP addresses stay on your site; only hashes and counts are sent.
- Last backup date (UpdraftPlus and common backup plugins).
安装:
- Install and activate the plugin.
- In your DevaGuard dashboard add the site and copy the server address and the site key.
- Go to Tools → DevaGuard, paste both, click Save, then "Send data now".
屏幕截图:
常见问题:
Does it slow down my site?
No. The plugin does nothing on visitor requests. The daily report runs in WP-Cron.
Does it fix problems?
No. It only reports. Fixes are made by the site administrator or the hosting company, following the instructions in the dashboard.
Can I see what is sent?
Yes. Tools → DevaGuard shows everything the plugin collects, with a copy button.
How do I remove it?
Deactivate and delete the plugin. Uninstalling removes all its options and scheduled events.
更新日志:
0.1.18
- Detects a phpMyAdmin login page that the hosting provider serves under the site address (/phpmyadmin/, /pma/), even when it is not a folder of the site. Placeholder pages such as "phpMyAdmin moved" are ignored.
- After an automatic WordPress update the report is sent with the new version. Before, the report sent right after the update still carried the old version, so the updated core files were reported as modified.
- The site checks from inside whether account logins (/?author=1, REST users list), XML-RPC, the WordPress version and readme.html are visible to visitors, so the DevaGuard server no longer sends these requests from outside. Hosting firewalls (ModSecurity) treated them as a scan and blocked the DevaGuard server.
- Plugin renamed to "DevaGroup DevaGuard – Site Security Monitor" (directory review). The DevaGuard service and dashboard keep their name.
- Sites behind Cloudflare: the login log records the visitor's real address (taken from the Cloudflare header only when the connection really comes from Cloudflare), so ordinary logins are no longer reported as "from a new network".
- Administrator logins through XML-RPC and application passwords are logged too (once per hour per account and network).
- Each login records how many failed attempts came from the same address in the hour before; plugin and theme installations are logged with the account that made them.
- The "site is alive" signal is sent every 5 minutes and includes the site's own home page status and SSL certificate expiry date, so the dashboard can see the site from inside when the hosting firewall blocks the DevaGuard server.
- The report is sent right after plugins, themes or WordPress are updated, without waiting for WP-Cron.
- "Verify after fixing" in the DevaGuard dashboard now requests a fresh report on the next heartbeat.
- PHP libraries that plugins install in uploads (Composer packages, e.g. PDF generators for invoices) are reported separately and no longer raise a break-in alert; each file is still checked for typical web shell code.
- First release in the WordPress.org directory.