
Forge12 Security – Firewall, Malware Scanner, 2FA & Login Security
| 开发者 | forge12 |
|---|---|
| 更新时间 | 2026年10月27日 21:17 |
| PHP版本: | 8.1 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
- Repair with one click — put the original back over a modified WordPress, plugin or theme file, one at a time or all at once, and restore files from quarantine
- Firewall before WordPress — requests are checked before WordPress and every other plugin load
- Same-day signatures — malware signatures and firewall rules the day they are published; the free plugin receives the same rule set 30 days later
- Country blocking and IP ranges — allow or block by country, and by IPv4/IPv6 range
- Tamper-proof audit trail, Slack and Telegram alerts, daily digest
- Remote monitoring, WP-CLI and multisite network management for looking after many sites
- Database snapshots with restore, Google Safe Browsing, and automatic repair and quarantine instead of a report
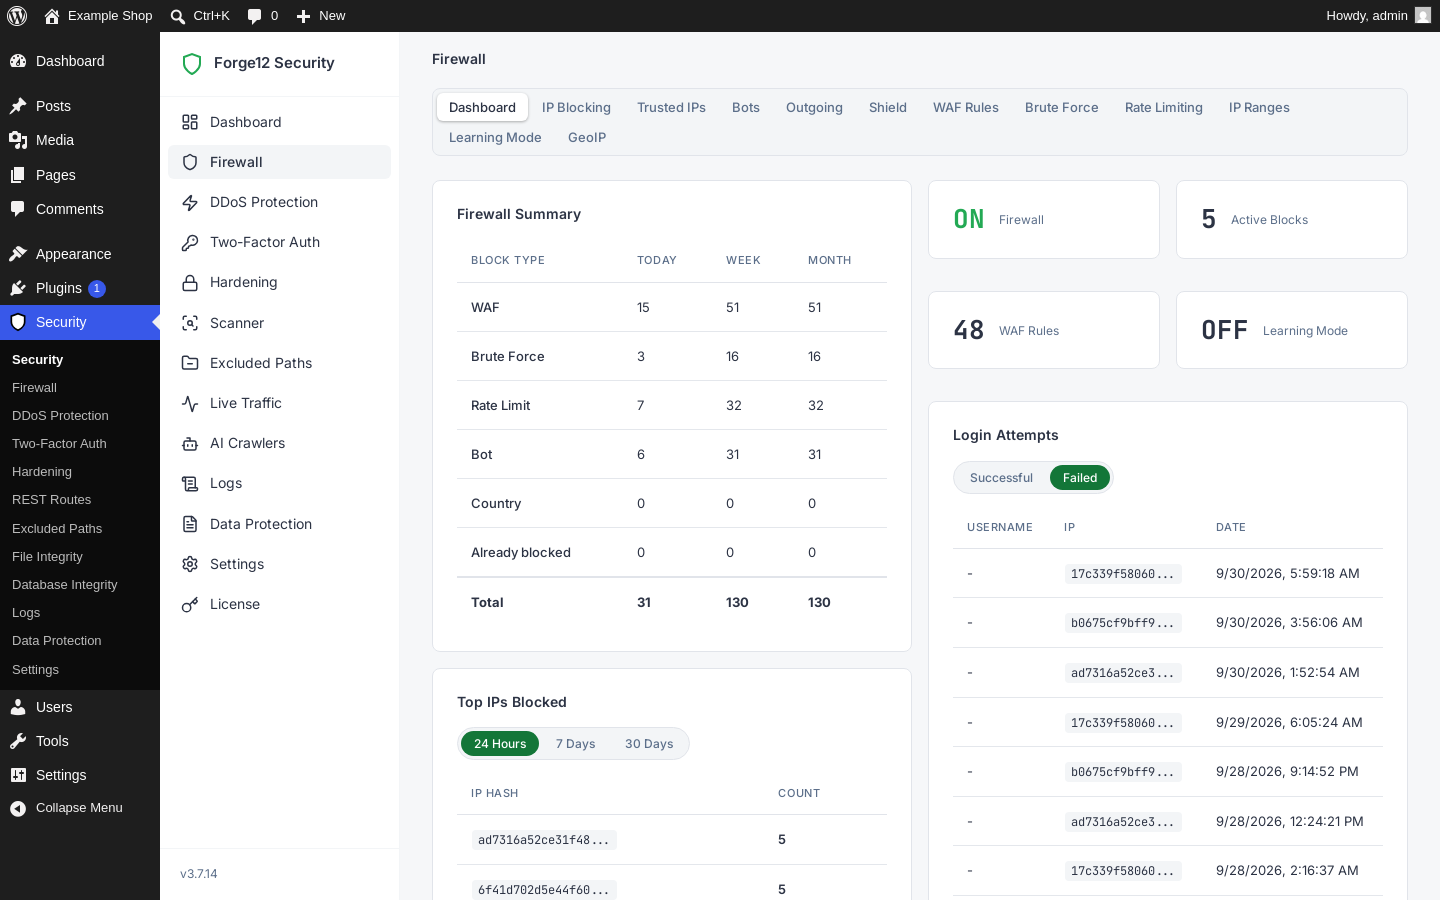
- Web application firewall. Scores each request against a signature set and refuses it when a category threshold is reached. A learning mode records what matches without blocking, so the exceptions your own site needs can be created from what actually happened.
- Outbound traffic monitoring. Watches where this installation sends data and to whom, learns which hosts are normal, and reports the new ones. Stolen data has to leave the server somehow; this is where that shows.
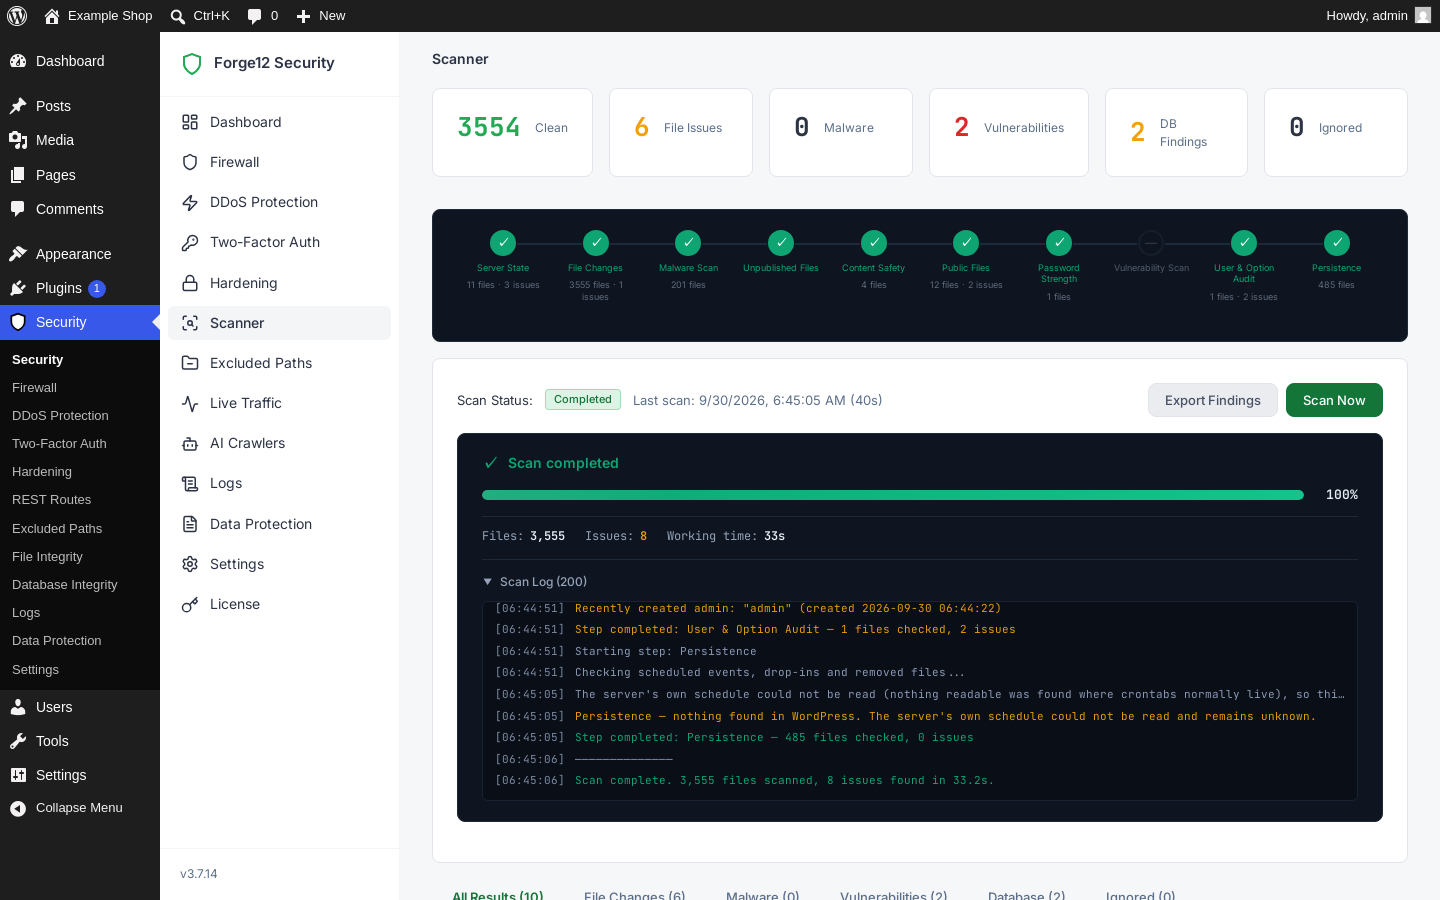
- Reinfection, not just infection. A file that was removed and came back is proof of persistence. The scanner looks for what put it back — a scheduled event, a must-use plugin, a drop-in — instead of deleting it again.
- Behaviour rules. Judges a file by the sequence of things its code does (create a user, hand it the administrator role, mark it to be found again), not by how it is written. Obfuscation is free to change; the steps are not.
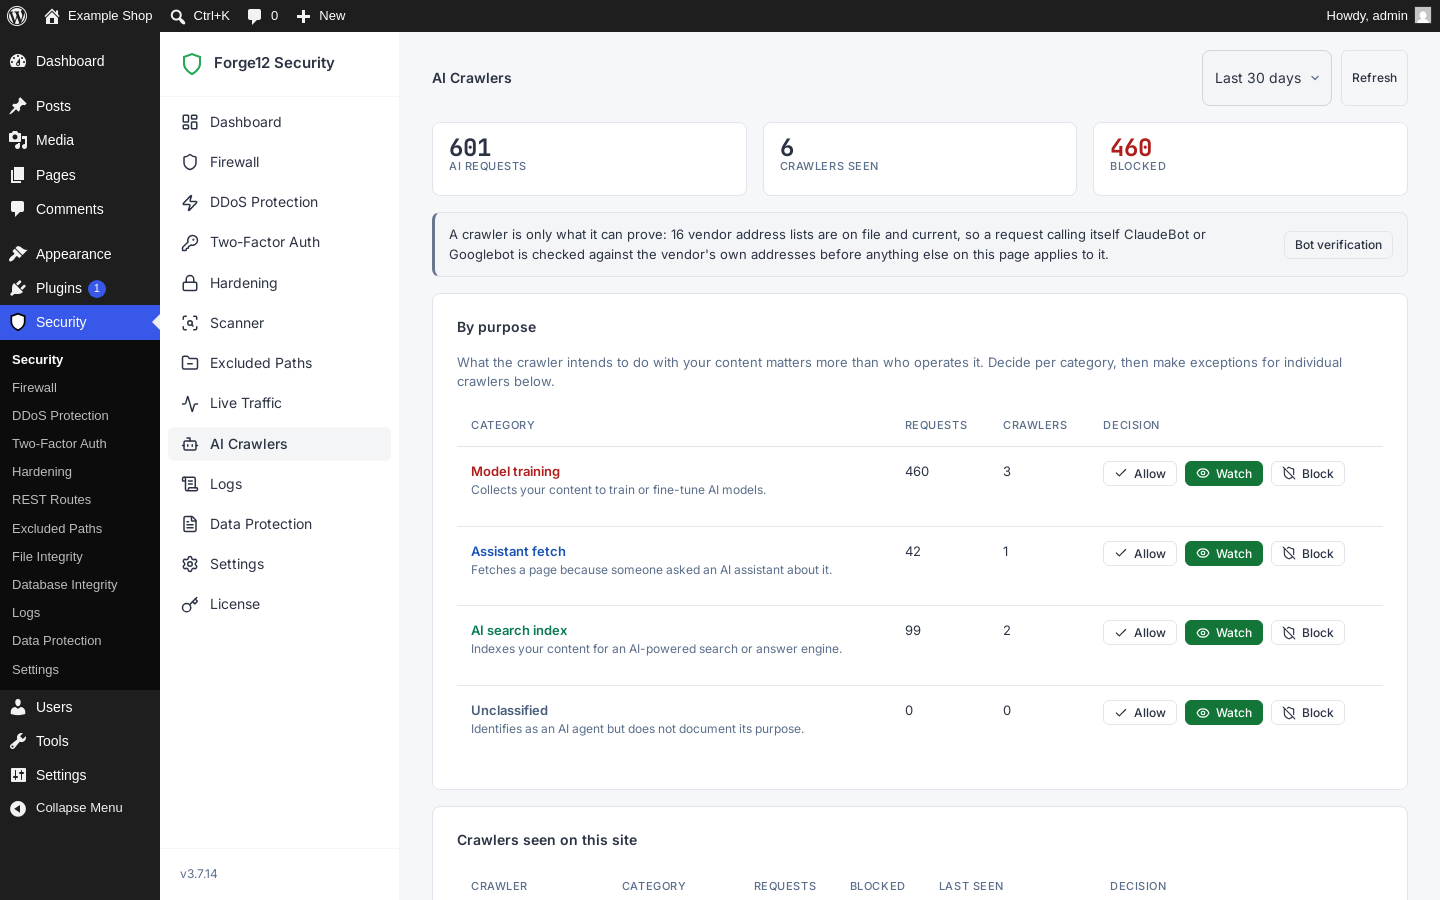
- AI crawler detection with proof. Anyone can put "ClaudeBot" in a header. Crawlers are checked against the address ranges their operators publish, so a claim that cannot be verified is treated as unverified rather than as fact. Each crawler, or each category of crawler, can be allowed, watched or refused.
- Login protection and two-factor authentication. Rate limiting, lockouts, TOTP with locally generated QR codes, and an optional custom login address.
- WordPress 6.2 or higher
- PHP 8.1 or higher
- MySQL 5.7 / MariaDB 10.3 or higher
安装:
- Upload the
forge12-securityfolder to the/wp-content/plugins/directory - Activate the plugin through the 'Plugins' menu in WordPress
- Navigate to the Forge12 Security menu in the admin sidebar
- Review the Dashboard and enable/disable modules as needed
- Configure individual module settings through the respective pages
- Check the Dashboard - Review your security score and enable recommended modules
- Run a File Scan - Go to File Integrity and create a baseline
- Review Hardening - Enable hardening options that suit your site
- Set Up Notifications - Configure your notification email in Settings
- Enable 2FA - Activate two-factor authentication for admin accounts
屏幕截图:
其他记录:
- Regex-based request filtering with customizable rules
- IP blocking with automatic expiration
- Bot detection with reverse DNS verification for Googlebot, Bingbot, Yandex, Baidu, DuckDuckBot
- Request validation (method, URL length, null byte detection)
- Predefined rule sets for common attack patterns (SQL injection, XSS, path traversal)
- WAF Learning Mode that records what the firewall would have blocked
- Automatic whitelist rule generation from learning mode results
- Watches where this installation sends data, and to whom
- Learns a baseline of the hosts your site normally talks to, then reports the ones that are new
- Refuses an outbound call before the connection is opened, so exfiltration and callbacks to a command server are stopped rather than logged after the fact
- The step every worthwhile attack has to take in the end — stolen data has to leave the server somehow
- Holds a known-vulnerable plugin shut until its update arrives
- The unauthenticated endpoints of a plugin with a published, unpatched vulnerability stop answering — the plugin’s own code is never touched
- Closes the window between disclosure and update: the weighted median from publication to mass exploitation is five hours, and 46 % of vulnerabilities are still unpatched on the day they are published
- Recognises crawlers operated by AI companies: OpenAI, Anthropic, Google, Perplexity, Meta, Apple, Amazon, Common Crawl, ByteDance and more
- Sorts them by what they do with your content: model training, assistant fetches on behalf of a user, AI search indexing
- Records which crawler requested what, and how often
- Allow, watch or block each crawler or whole category
- Matching robots.txt directives generated from your decisions
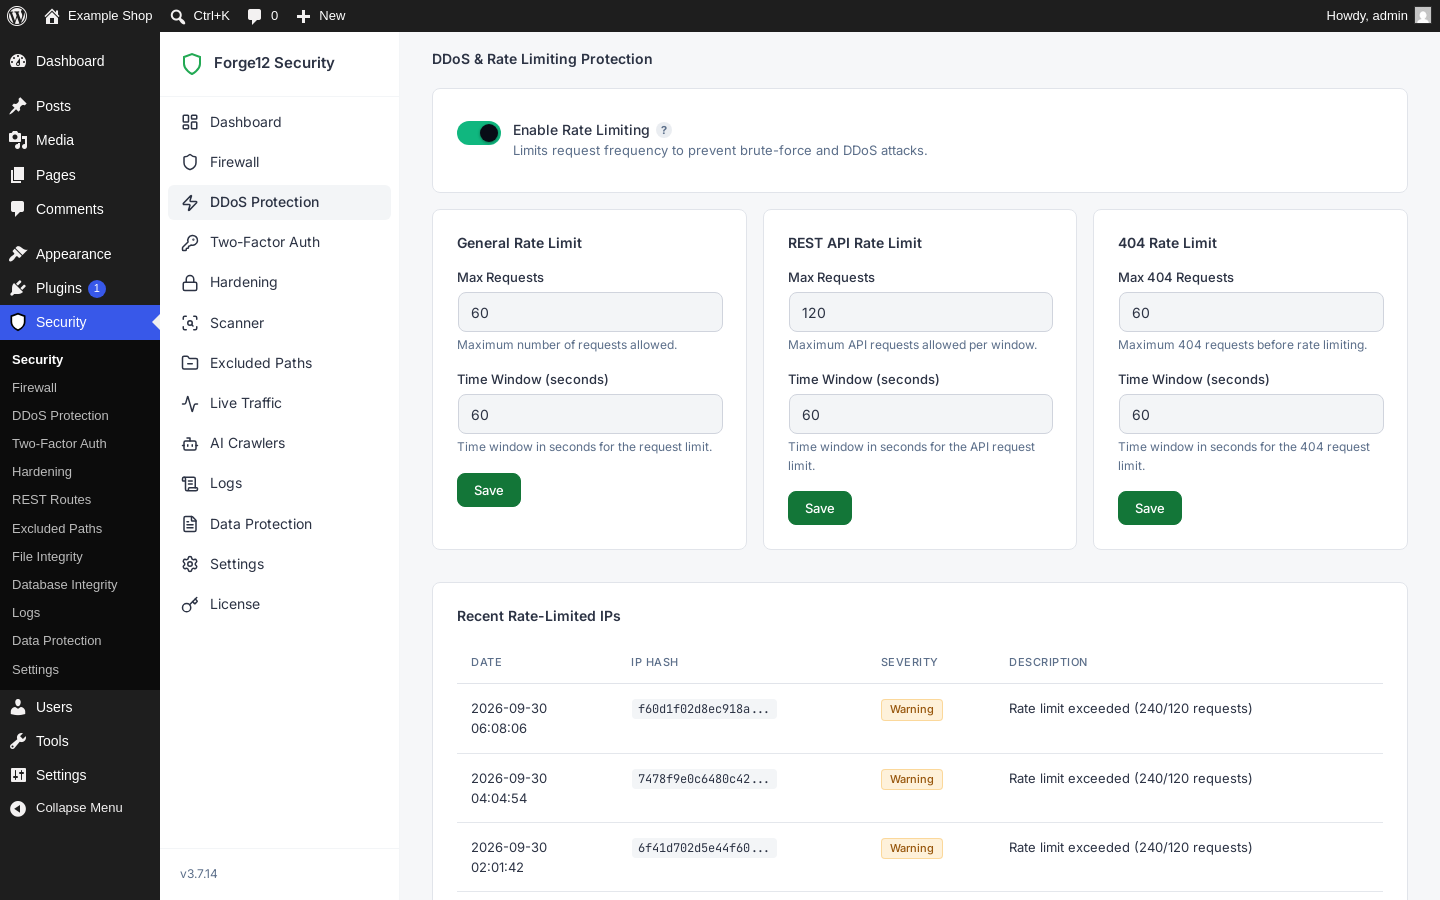
- Configurable request rate limits per IP
- Separate rate limits for REST API endpoints
- 404 rate limiting to detect and block vulnerability scanners
- Automatic IP blocking on limit exceeded
- IP whitelist for trusted addresses
- Brute force prevention with automatic lockout (5 attempts / 15 min)
- Two-factor authentication (TOTP) with QR code setup
- Recovery codes for 2FA
- Login honeypot for bot detection
- Custom login URL to hide wp-login.php
- SilentShield bot check on the login, registration and password reset forms — Forge12's own service, served from Germany, no Google script in your visitors' browsers
- Login activity logging (success, failure, lockout)
- Configurable strong password policy (minimum length, uppercase, numbers, special characters)
- Breached password detection via Have I Been Pwned API (k-Anonymity)
- 2FA enforcement per role, with a grace period for gradual rollout
- SHA-256 checksum baseline of all WordPress core, plugin, and theme files
- Automatic scheduled scans with configurable intervals
- Repository verification against WordPress.org originals
- Automatic scheduled malware and integrity scans
- Quarantine and delete suspicious files
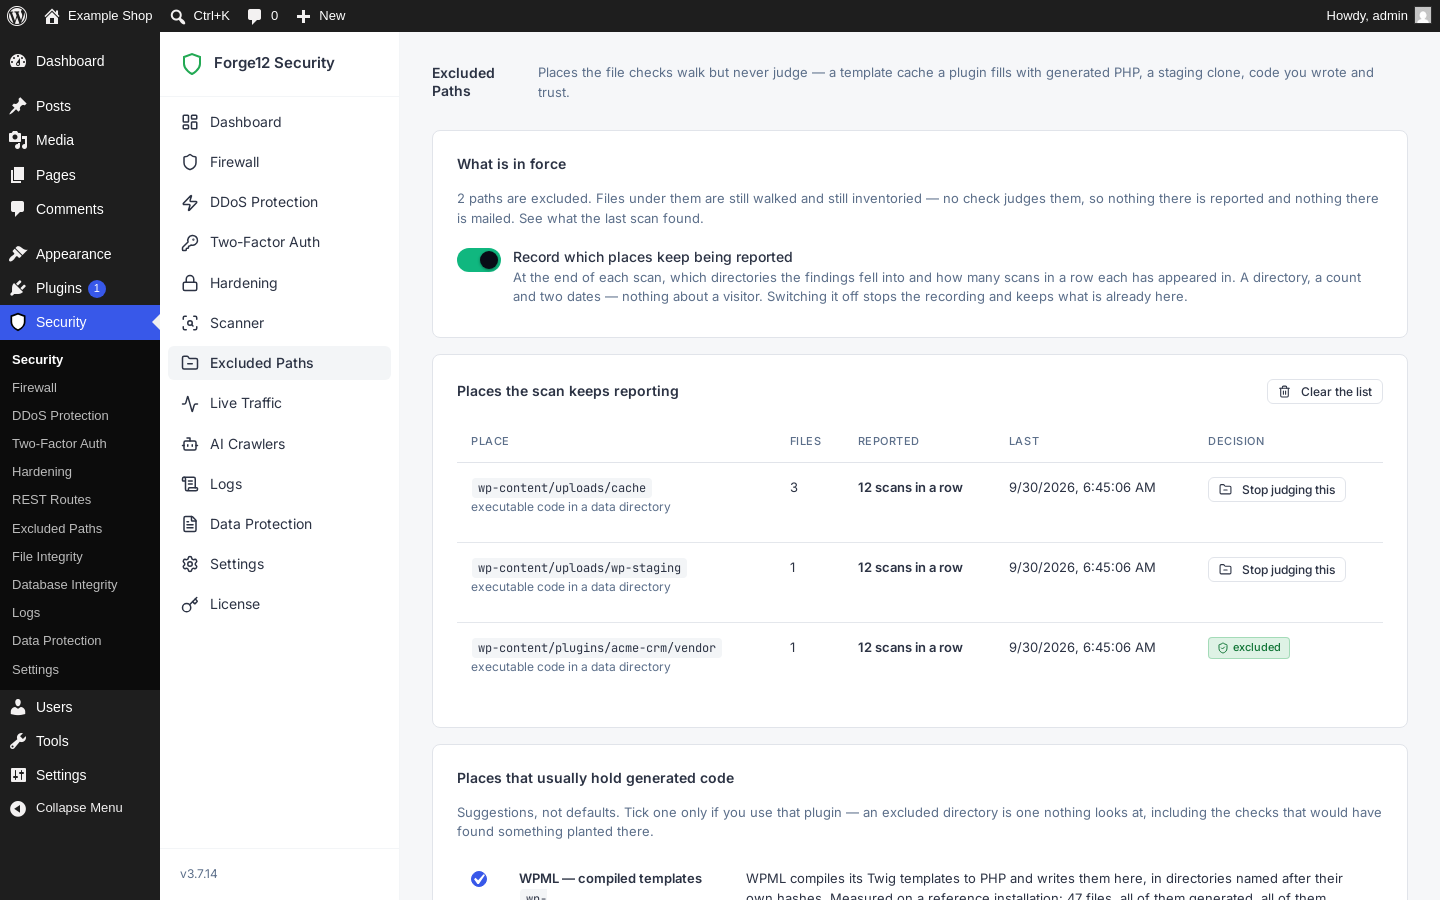
- Excluded paths: a page for the directories no file check should judge — a template cache a plugin fills with generated PHP, a staging clone, code you trust. It records which places your scans keep reporting and how many scans in a row, so excluding one is a button rather than a path typed from memory; entries can be switched off instead of deleted, and known candidates are offered as ticks, never applied on their own
- Pattern-based malware detection with 283 built-in signatures
- Detects eval/base64 backdoors, shell uploads, code obfuscation, and remote includes
- Heuristic detection via entropy and structure analysis, beyond signature matching
- Three sensitivity levels: critical signatures only, critical and high, or everything including heuristics
- Files that still match the checksum their author published on WordPress.org are never flagged
- Mark a reviewed file as allowed — pinned to its content, so a later change brings it back into scope
- File Guard: an unexpected PHP file is reported the moment it is executed, not on the next scheduled scan. On its own this covers files that load WordPress, which is most of them, because a shell usually wants the database.
- Suspicious file flagging with threat identification
- Extensible signature database (JSON format)
- Persistence check: finds what puts a removed file back — a scheduled event, a must-use plugin, a drop-in — starting with the evidence that actually proves reinfection, a file that was taken away and is back
- Attack surface: records which REST routes and AJAX actions are reachable without logging in and which of those change something, and reports the door that newly appeared
- Update guard: verifies an installed update against the per-file checksum manifest WordPress.org publishes, so a package that is not what the author shipped is caught on arrival
- Known hashes: covers premium plugins, bespoke themes and this plugin itself, where wordpress.org publishes no original to compare against
- File inventory instead of modification times: a dropped file cannot make itself old with touch, and a plugin update no longer resets what counts as new
- Behaviour rules: judges a file by the sequence of things its code does — create a user, hand it the administrator role, mark it to be found again — not by how it is written
- Every finding says in plain words what it means and what to do about it, instead of naming the rule that fired
- Monitors wp_options, wp_posts, wp_postmeta, wp_users, wp_usermeta
- Detects unauthorized modifications, injected scripts and phishing URLs in posts, comments and options
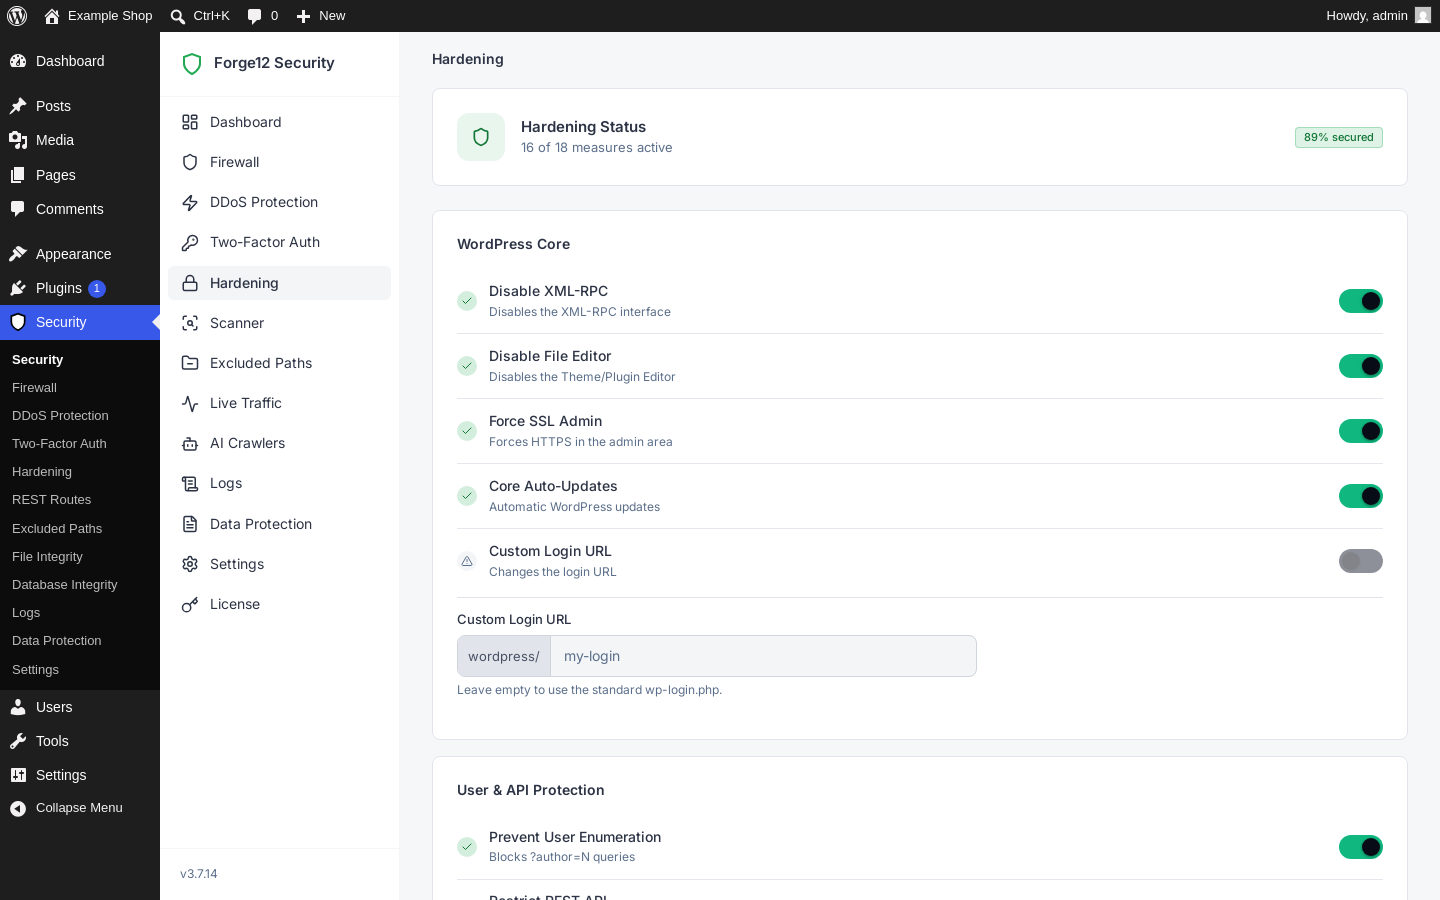
- Disable XML-RPC and pingbacks
- Disable file editor
- Force SSL for admin area
- Block PHP execution in uploads directory
- Prevent user enumeration
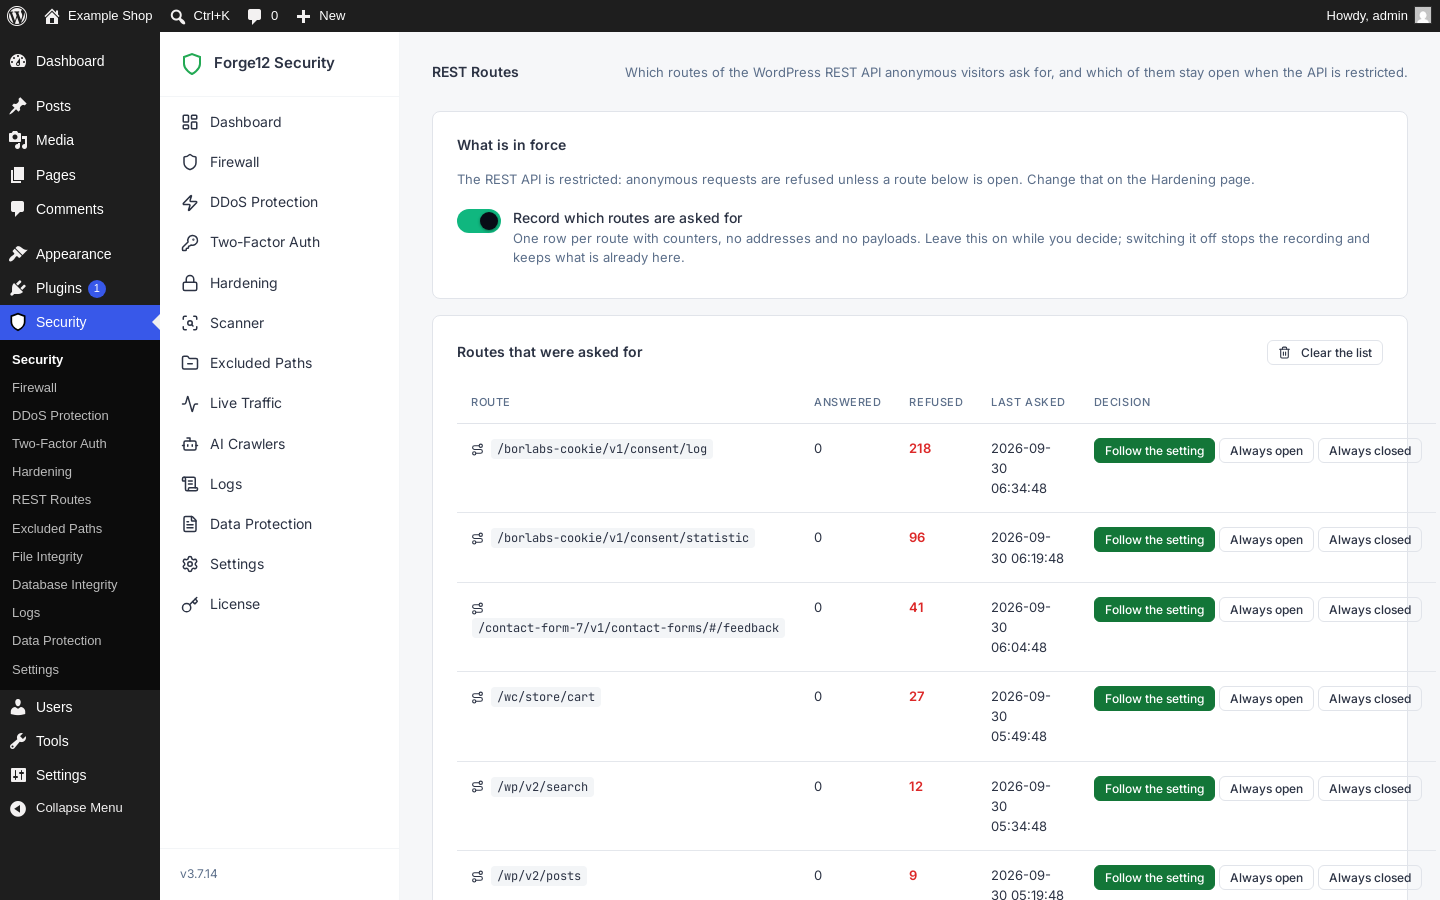
- Restrict REST API to authenticated users
- Disable application passwords
- Remove WordPress version info
- Configurable Content-Security-Policy header
- Full suite of security headers (HSTS, X-Frame-Options, X-Content-Type-Options, etc.)
- Limit post revisions
- Shorter session lifetimes
- Limit concurrent sessions per user
- Auto-update WordPress core
- Comment spam honeypot protection
- Strong password enforcement with configurable rules
- SilentShield bot protection for login, registration and password reset forms
- Alerts for critical and high severity events
- Findings collected and sent as one message, grouped and counted, instead of one email per finding
- Anything critical sent immediately, with whatever else has collected
- Unsubscribe link in every message, for people who no longer have an account on the site
- Weekly summary of what was blocked, attempted and found — sent whether or not anything went wrong
- Optional notifications for IP blocks
- Scan summary emails when changes are detected
- Configurable notification email address
- A test button to check delivery
- Slack and Telegram alerts and a daily digest are part of Forge12 Security Pro
- Watch requests as they arrive, with response code, request type and bot classification
- Block an IP straight from a traffic entry
- Records security-relevant requests (errors, blocks, login attempts) and keeps 24 hours
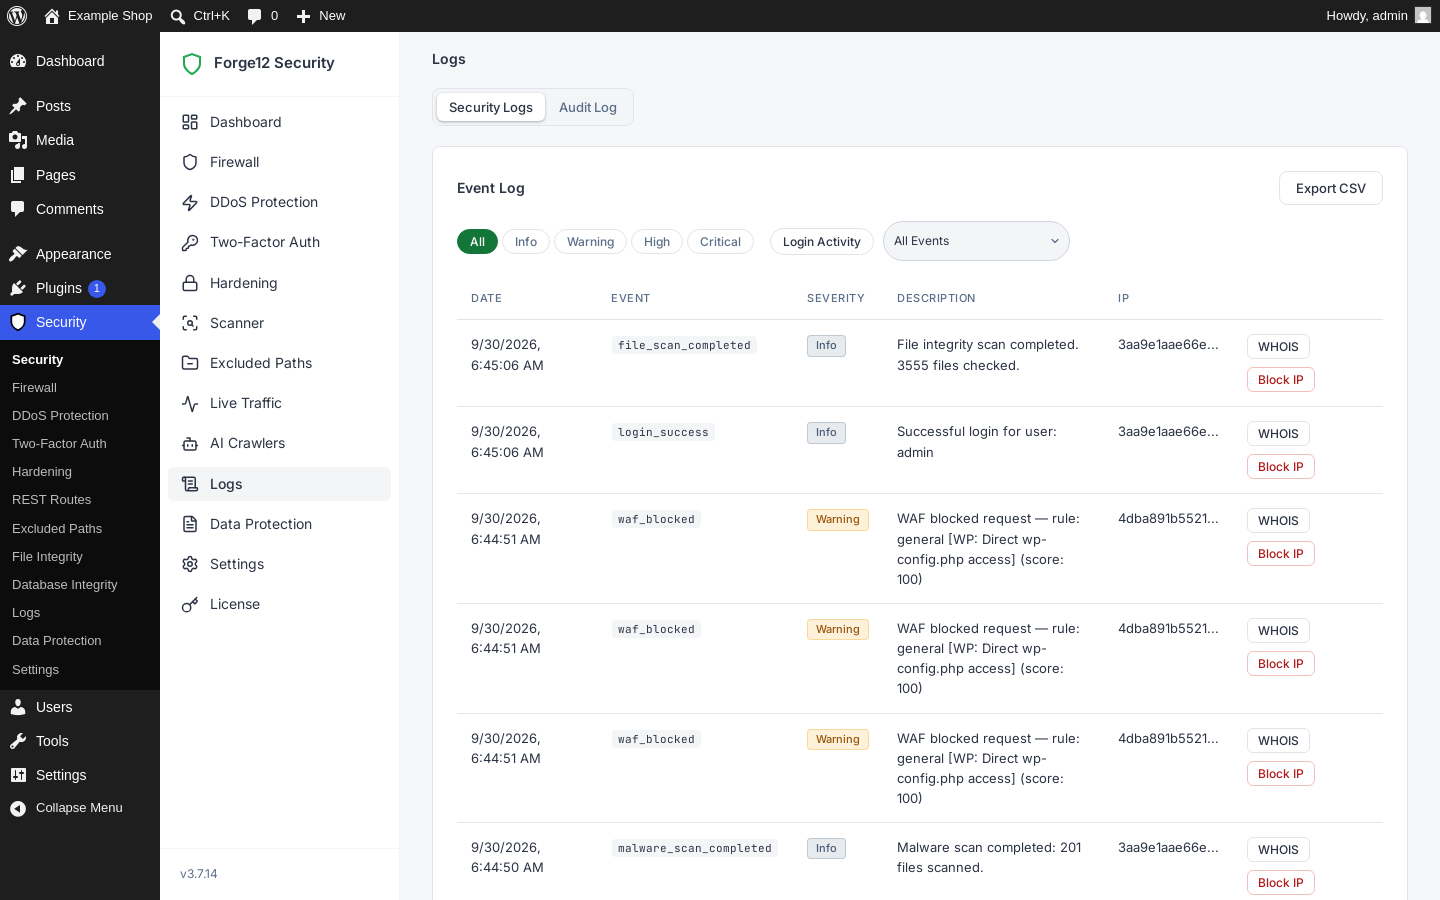
- Comprehensive event logging for all security actions
- Filterable by event type and severity
- Quick-filter for login activity
- CSV export
- Block IPs directly from log entries
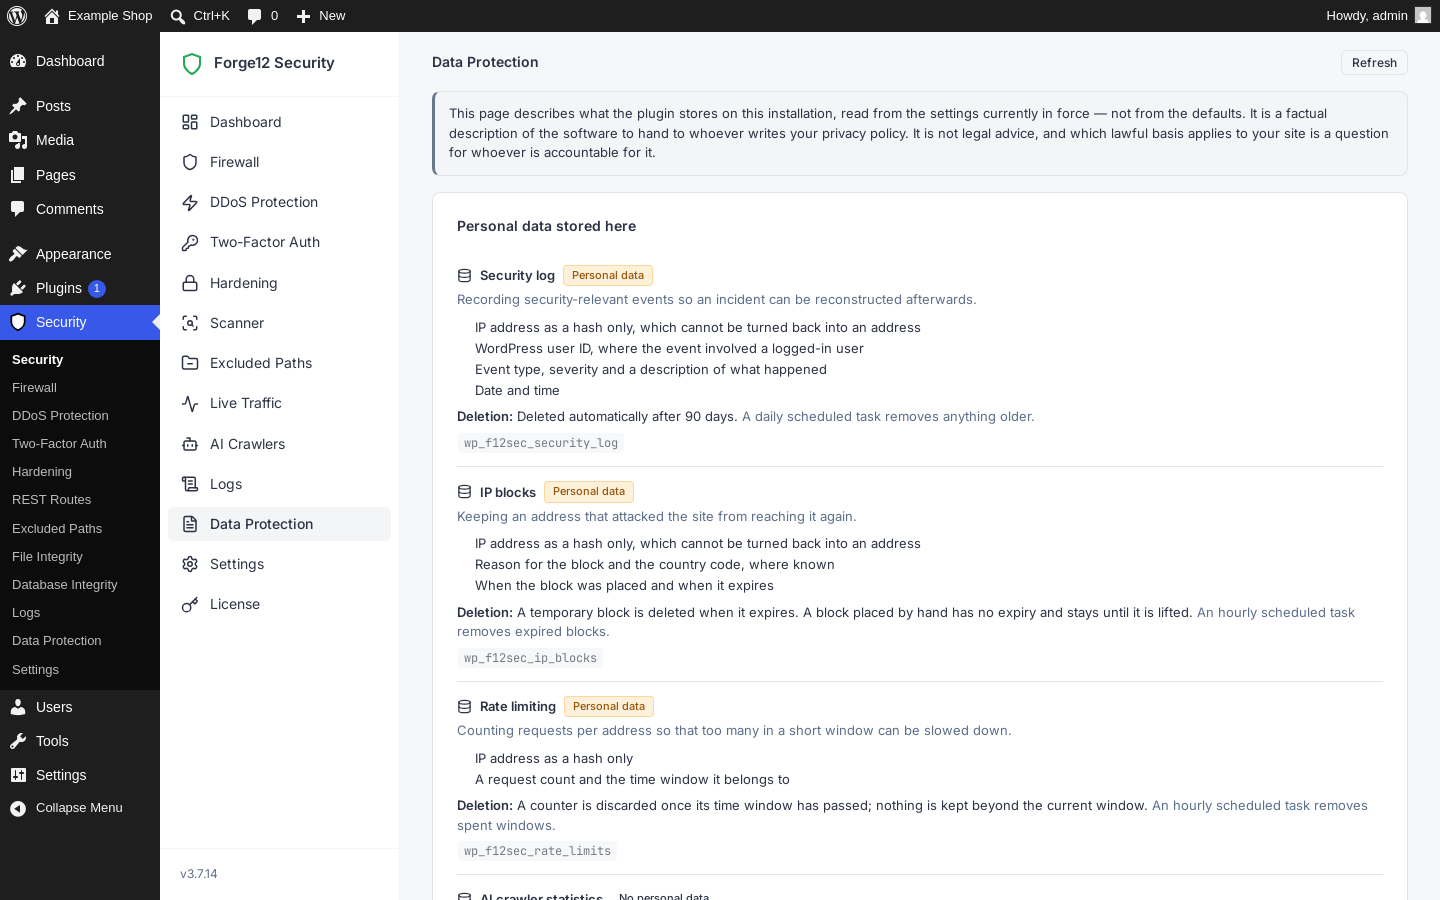
- Configurable log retention (default: 90 days)
- IP anonymization via HMAC-SHA256 (no plain IPs stored)
- Optional AES-256-CBC encrypted IP storage
- WordPress privacy exporter integration
- WordPress privacy eraser integration
- Import/export settings as JSON
- Security score with detailed breakdown
- Modern React-based admin interface
常见问题:
What is the difference between Forge12 Security and Forge12 Security Pro?
Everything described on this page is free and stays free, without a trial period or a limit. Forge12 Security Pro is an add-on for sites that want problems fixed rather than reported: one-click repair of modified files and restore from quarantine, a firewall stage that runs before WordPress, same-day malware signatures and firewall rules, country blocking, a tamper-proof audit trail, Slack and Telegram alerts, and remote monitoring for many sites.
Do I need this plugin to use Forge12 Security Pro?
Yes. Pro extends this plugin and needs it installed and active. Removing Pro leaves this plugin and all of its settings as they were.
Does this plugin work with caching plugins?
Yes. Forge12 Security operates at the PHP level and is compatible with all major caching plugins. Rate limiting and firewall checks happen before page caching kicks in.
Will the custom login URL break my site?
No. If you forget the custom login URL, you can deactivate the plugin via FTP/file manager and the standard wp-login.php will work again. Password-protected post forms (action=postpass) continue to work normally.
Does this plugin store IP addresses?
By default, IP addresses are hashed using HMAC-SHA256 and never stored in plain text. Optionally, you can enable AES-256-CBC encrypted storage if you need to identify specific IPs. These options help minimize stored personal data; they do not guarantee GDPR compliance.
Can I use this with other security plugins?
While possible, we recommend using only one comprehensive security plugin to avoid conflicts. If you need specific features from another plugin, you can disable overlapping modules in Forge12 Security.
What happens when the malware scanner finds something?
Suspicious files are flagged with the detected signature name. You can review the file, move it to encrypted quarantine, or permanently delete it after a separate confirmation. Modified WordPress, plugin and theme files are compared with their published version; to replace one, reinstall or update it from the dashboard. Confirmed false positives can be ignored or excluded.
How does the honeypot work?
The honeypot adds an invisible form field to login and comment forms. Real users never see or fill it. Bots that automatically fill all form fields trigger the honeypot and are blocked. The field name rotates every 6 hours to prevent bot adaptation.
How does the SilentShield bot check work?
A small client is loaded on your login, registration and password reset forms. It watches how the form is filled in and leaves a token on it; on submission the plugin asks the SilentShield API what that token was worth, and you set the threshold below which a submission is refused. It replaced the Google reCAPTCHA integration in 3.3.44, because that one loaded Google’s script into the browser of everybody who opened your login page, handing Google their address and setting Google’s cookies for a form only your own staff ever use. SilentShield is Forge12’s own service and answers from a German host with no CDN in front of it, so the transfer is one you can put in a contract. What has not changed: it is still a third-party script in the visitor’s browser, and the visitor’s address still reaches somebody else. Like the check it replaced it fails open by default — an outage at the API must never be the reason nobody can log in — and a filter is there for sites that would rather be locked out than let a bot through.
Does the breached password check send my passwords to an external service?
No. The HIBP check uses k-Anonymity: only the first 5 characters of the SHA-1 hash of the password are sent to the API. The full password never leaves your server. Results are cached for 24 hours.
Where do I require two-factor authentication for a role?
Under Two-Factor Auth, above the user list. Switch on the roles that must carry a second factor, set the grace period beside them, and save. The roles offered are the ones your site actually has, including any a plugin adds.
What is the 2FA grace period?
It is how long somebody may go on working before the requirement takes effect: 0 to 90 days, counted from that account's first sign-in after you switch the requirement on. Nobody is ever locked out by it. The sign-in itself succeeds either way; once the period is up, the account is taken to the setup screen and stays there until a second factor is in place, and during the period it sees a notice with the days remaining. A grace period of zero days means the setup screen appears at the next sign-in.
How does 404 rate limiting work?
404 rate limiting monitors how many "Page Not Found" errors a single IP generates within a time window. Vulnerability scanners typically probe hundreds of known paths rapidly, generating many 404s. When the threshold is exceeded, the IP is automatically blocked.
How does bot detection work?
Bot detection identifies fake search engine crawlers. When a visitor claims to be Googlebot (via User-Agent), the plugin performs a reverse DNS lookup to verify that the IP actually belongs to Google. If the reverse DNS check fails, the bot is flagged as fake and optionally blocked. Results are cached for 24 hours.
What is WAF Learning Mode?
Learning Mode records normal request patterns (URLs, methods, parameter names) over a configurable period (default: 7 days). After the learning period, you can generate whitelist rules from the observed traffic. These whitelist rules ensure that known-good requests bypass WAF checks, reducing false positives.
Why can this plugin not repair files or run the firewall before WordPress?
Both write into places the WordPress plugin directory does not allow this plugin to write to: code into files, and files into the WordPress, plugin and theme folders or the site's root folder. Those features are part of Forge12 Security Pro, which is not distributed through the directory. This plugin still finds, explains and compares every modified file, and quarantines or deletes suspicious ones.
Can I export my settings to another site?
Yes. Go to Settings > Import / Export. You can export all settings as a JSON file and import them on another WordPress installation.
更新日志:
- A .htaccess in wp-admin, wp-includes or the installation root was reported as an executable file that WordPress never published, at critical severity, by its name alone. That is right for a planted one, and wrong for the access rules a hardening plugin writes on purpose. A file now counts as access control only when every line is an access directive (require, order, deny, allow, satisfy, authentication, error documents, options that switch features off). Anything else, such as a handler, a type, a PHP value, a prepend, a rewrite, a redirect or a header, keeps the critical verdict. The file is still listed.
- The same goes for a php.ini or .user.ini that only sets limits, error handling and OPcache. One that can load code (a prepend or append file, an extension, a module given by path, switched-off function limits) stays critical.
- Six malware signatures asked only for a word "somewhere near" another one and reported well-known libraries: Symfony Process, the PEAR copy in UpdraftPlus and Matomo, Matomo's system summary. They now ask for what they are named after: a shell started by proc_open, a sort callback that is assert or system, dl() with a module or request data, a decoded string run by a bitwise xor, an admin_init callback that creates an administrator, a variable called with request data. The attacks stay detected.
- Imunify's rule store (wp-content/imunify-security) is not read as code, like Wordfence's.
- A plugin that a remote tool updates changed all its files in the eyes of the check against the recorded state, and it was reported again at every scan. When the version of a plugin has changed since the scan before, its changed files are now recorded again and the update is written to the log. A file that changes while the version stays the same is still reported.
- The Changelog section of readme.txt was longer than the 5000 characters the plugin directory shows. Older entries are in changelog.txt.
- WordPress.org sometimes publishes two valid hashes for one file, when its published revision changed within a release. The check read only one of them, or the list as if it were a single value, so an unchanged file was reported as modified while "View differences" showed nothing. A file is now clean when it matches any published hash, for plugins, themes, the check after an update and the test whether a file is the published original. A file that matches none is still reported.
- The signature file and the changelog named well-known web shells and the calls a backdoor is made of in plain text, so a host's scanner that matches on text reported both as malware. The signature file now writes one character of each such word as an escape, and the changelog describes such code in words. The scanner reads exactly the same signatures as before.
- Importing signatures keeps the file in that form.
- The service was on the allowlist because refusing it would stop a feature, and so it never appeared anywhere. It is now counted in the list of destinations (first and last use, in how many hours it was used, which plugin or file made the call), still without any judgement: no log line, no decision, and the call always goes through, whatever the rules for other destinations are.
- A counted destination does not count towards the baseline and does not restart its quiet time.
- Only the service and the hosts below its name are counted. A lookalike such as evil-silentshield.io is still an unfamiliar destination.