Loggedin - Session Manager: Limit Concurrent Logins & Auto Logout
| 开发者 |
joelcj91
duckdev foxelabs |
|---|---|
| 更新时间 | 2026年11月9日 04:25 |
| 捐献地址: | 去捐款 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
WP_Session_Tokens API. It needs no cron jobs, no background polling and no external services, and it works with any theme and host.
Loggedin at a glance
- What it does: limits concurrent logins per account, logs out idle users, and manages every signed-in device.
- Price: free. Optional add-ons add per-role limits, per-user limits, a live sessions view and real-time logout.
- Default: one device per account. A new login signs out the others.
- Where the settings are: Users → Loggedin in the WordPress admin.
- Requirements: WordPress 6.5 or later, PHP 7.4 or later.
- Privacy: no external calls, no tracking, no data sent anywhere.
- Made by: Foxe Labs. Active since 2016.
- Set how many devices an account can be signed in on at once, from 1 upwards.
- Choose what happens when someone goes over the limit:
- Logout Oldest signs out the oldest device and lets the new login in.
- Logout All signs out every other device, so the new login is the only one.
- Block New refuses the new login and shows a message on the login screen.
- Leave administrators out of the limit, so nobody is locked out of their own site.
- Covers social login, magic-link and popup login plugins too, under Logout Oldest and Logout All.
- Sign out sessions nobody has used for a set number of minutes.
- Show a countdown warning before the logout happens.
- Give each role its own idle timeout.
- The check runs on the server, so a forgotten open tab doesn't keep a session alive.
- Set how long a login lasts, with and without "Remember Me".
- End every session of any user from the Sessions page, the Users screen or WP-CLI.
- Log out all users on the site at once, instantly, even with thousands of accounts. Your own session stays signed in.
- See each user's session count and last login on the Users screen, with a sortable Last login column.
- Sign users out everywhere one at a time or with a bulk action.
- Sign users out of their other devices when their password changes or is reset.
- A user blocked by the limit can email themselves a link that signs out their other devices. It is offered only after the right password, and the link expires after 15 minutes.
- Write your own blocked-login message, with links.
- Tell users why they were signed out ("your account signed in on another device"), or send them to a page you choose.
- "Your sessions" on the profile screen lists each device a user is signed in on, where and when, with a Sign out button for each.
- WP-CLI commands:
wp loggedin sessions list,wp loggedin sessions destroy,wp loggedin sessions destroy-allandwp loggedin settings. - A REST API under
loggedin/v1. - Documented actions and filters for every decision: change the limit per user or role, exempt service accounts, log forced logouts, or add your own login rule. See the developer docs.
- Membership sites on MemberPress, Paid Memberships Pro, Restrict Content Pro, s2Member or WooCommerce Memberships, to stop one paid account being shared by a group.
- Online courses and LMS sites on LearnDash, LifterLMS, Tutor LMS or Sensei, so each seat is used by the person who paid for it.
- Subscription stores on WooCommerce Subscriptions or Easy Digital Downloads, to keep subscriber accounts personal.
- Intranets and client portals that need one device at a time per staff or client account.
- Communities on BuddyPress or BuddyBoss, to cut down on shared and duplicate accounts.
- Sites with security or compliance rules (healthcare, finance, education) that require a session limit and an idle timeout.
- Active Sessions: see who is logged in right now, every device for each user, and sign out one session or all of them.
- Limit Per Role: give each WordPress role its own concurrent login limit.
- Limit Per User: set a different limit for one user from their profile.
- Real-time Logout: when a session ends, the user's other open tabs go to the login screen straight away.
- Getting started
- Login limits
- Lockout and recovery
- Auto logout
- Force logout
- Users screen and profile sessions
- Compatibility with social, magic-link and popup logins
- WP-CLI commands
- Add-ons
- Developer docs: hooks, filters and REST API
安装:
- In the WordPress admin, go to Plugins → Add New Plugin, search for "Loggedin" and click Install Now.
- Click Activate.
- Go to Users → Loggedin to set the login limit and choose what happens when it's reached.
屏幕截图:


常见问题:
How do I limit concurrent logins in WordPress?
Install and activate Loggedin, go to Users → Loggedin → Login limits, set the maximum number of active logins and choose a login logic: Logout Oldest, Logout All or Block New. Save. The limit applies from each user's next login.
How do I prevent account sharing on my membership site?
Set the limit to 1. With Logout All or Logout Oldest, a second person logging in signs the first one out, so sharing one account becomes annoying fast. With Block New, the second login is refused until the first device signs out. Loggedin works with MemberPress, Paid Memberships Pro, WooCommerce, LearnDash and other plugins that log users in through WordPress.
How do I automatically log out inactive users?
Go to Users → Loggedin → Auto logout, turn on idle logout and set the timeout in minutes. Users see a countdown before they are signed out, and each role can have its own timeout. It's free and built in since version 3.4.0.
How do I force logout a user in WordPress?
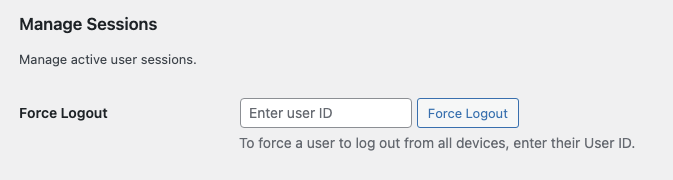
Go to Users → Loggedin → Sessions, enter the user's ID, email or username under Force Logout and click the button. Every session of that user ends immediately. You can also use Sign out everywhere on the user's row on the Users screen, or run wp loggedin sessions destroy <user>.
How do I log out all users at once?
Click Logout All Users on Users → Loggedin → Sessions, or run wp loggedin sessions destroy-all. It finishes instantly at any number of users because it sets one site-wide cut-off time instead of looping through accounts. Your own session stays signed in.
How can I see who is logged in to my WordPress site?
The Users screen shows each user's number of active sessions and their last login. Each user sees their own devices under Your sessions on their profile. For a live list of everyone signed in right now, with every device, add the Active Sessions add-on.
Can I set different limits for administrators and subscribers?
Yes, with the Limit Per Role add-on. Each role gets its own limit, for example 5 for administrators and 1 for subscribers. A user with several roles gets the highest. To leave administrators out of the limit altogether, turn on Don't limit administrators in the free plugin.
Can I set a different limit for one user?
Yes, with the Limit Per User add-on, which adds a limit field to the user's profile.
A user is locked out by Block New. What can they do?
If self-unlock is on, the error shows a link after the right password. The user gets an email with a link that signs out all their devices, and can then log in. An administrator can also force logout the user from the Sessions page.
Why was I signed out with "your account signed in on another device"?
Someone logged in to your account on another device, and the site allows only a set number of devices at once, so this one was signed out. If it wasn't you, change your password.
Will installing Loggedin or changing the limit log out current users?
No. Loggedin acts only when someone logs in. Existing sessions stay until they expire, the user logs out or a later login replaces them. Turning on auto logout gives every session the full timeout from the moment you save.
Does Loggedin work with WooCommerce, MemberPress, LearnDash and BuddyPress?
Yes. Any plugin that logs users in through WordPress is covered with no extra setup. Social login, magic-link and popup login plugins are covered under Logout Oldest and Logout All; Block New can refuse them only when the plugin checks first, as Nextend Social Login does. Tested with WooCommerce, Ultimate Member, Nextend Social Login, Magic Login, Two Factor, Limit Login Attempts Reloaded, WPS Hide Login and User Switching. See compatibility.
Is Loggedin the same as a "limit login attempts" plugin?
No. Limit login attempts plugins block repeated wrong passwords to stop brute-force attacks. Loggedin limits how many devices a valid account can be signed in on at the same time. They do different jobs and work well together.
Does Loggedin work with Redis or other session storage?
Yes for Logout All, Block New, force logout and log out all users, which go through the standard WP_Session_Tokens API. Logout Oldest and the per-device lists need WordPress's default session storage in user meta.
Does Loggedin slow down my site?
No. Loggedin does its main work when someone logs in or out, and on its own admin screens. On other pages it only reads its settings and, with auto logout on, the signed-in user's last activity. There's no cron, no polling and no remote request. With auto logout on, a small script tracks activity in the browser and checks in with the server at most once a minute while the page is in use.
Is Loggedin GDPR compliant?
Loggedin calls no external services and sends no data anywhere. It uses the session records WordPress already keeps, which hold the IP address and browser of each login, and stores each user's last login time and, with auto logout on, when each session was last active. The profile screen shows only part of the IP address. Mention WordPress sessions in your privacy policy as you would without the plugin.
How long does a WordPress login last?
By default, 14 days with "Remember Me" checked and 2 days without. Change both under Users → Loggedin → Auto logout → Session length, or with the auth_cookie_expiration filter.
Can I change the message shown when a login is blocked?
Yes, under Users → Loggedin → Lockout & recovery. Developers can also use the loggedin_error_message filter:
php
add_filter( 'loggedin_error_message', function ( $message ) {
return 'Your account is already signed in on another device.';
} );
Does Loggedin support WP-CLI?
Yes. wp loggedin sessions lists, counts and ends a user's sessions, and wp loggedin settings reads and changes settings. Commands that end sessions ask for confirmation unless you pass --yes. Run wp help loggedin or see the WP-CLI docs.
更新日志:
- Fix: The login screen no longer shows a critical error when another plugin's login message filter returns nothing.
- Fix: A device signed out by a newer login no longer gets a critical error on its next page on WordPress 6.5, or on sites that set
COOKIE_DOMAINto false. - Fix: Admin screens that another plugin prints outside wp-admin no longer show a critical error.
- Fix: Loggedin no longer causes a critical error when another plugin or an add-on returns nothing from one of its filters, or passes something other than a user to the login check.
- New: Settings screen rebuilt with a sidebar of pages — Login limits, Lockout & recovery, Auto logout, Sessions, Add-ons and Help — and Save in the page header.
- New: Self-unlock — a user blocked by Block New can email themselves a link that signs out their other devices. Only offered after the right password; links are single-use and expire after 15 minutes.
- New: "Don't limit administrators" setting.
- New: Set the blocked-login message on the Lockout & recovery page.
- New: A device signed out by a newer login is told why on the login screen, or sent to a page you choose.
- New: Auto logout is now free and built in — idle logout with a countdown, timeouts per role and session length.
- New: A password change or reset can sign the user out of their other devices. On for new sites. A password an LDAP or SSO plugin copies in as the user signs in doesn't count.
- New: Sessions and Last login columns, and a "Sign out everywhere" action, on the Users screen.
- New: "Your sessions" on the profile screen.
- New: Logout Oldest and Logout All now also apply to logins that skip the login form (social login, magic links, popup logins).
- New: Switching to a user with User Switching isn't treated as their login, so it signs out none of their devices.
- New: Add-ons can add pages, cards and fields from PHP with the
loggedin_settings_schemafilter. - New:
loggedin_sessions_displacingaction before Logout All or Logout Oldest ends sessions, andloggedin_uninstalledafter the plugin is deleted. - New:
loggedin_settings_propertiesfilter, so an add-on's own key in Loggedin's settings is saved, andloggedin_session_deviceto name the devices in a user's session list. - New: A notice lists add-ons that need an update for the new settings screen.
- Improve: Block New checks the password first. A wrong password gets WordPress's usual error, not the limit message.
- Improve: Add-ons built for the old screen keep working, and links from before 3.4.0 still open the right page.
- Improve:
wp loggedin settings setaccepts true/false, yes/no, on/off or 1/0 for on/off settings. - Improve: Keyboard, screen reader and contrast fixes on the settings screen, the auto logout warning and the profile's sign-out buttons. The current page and focused fields stay visible in Windows high contrast mode.
- Improve: Login modes added by other plugins through
loggedin_logicscan be saved. - Improve:
loggedin_destroy_all_sessionsnow fires for every way a user is signed out everywhere, including the Users screen, a password change and the unlock email. - Improve:
POST /loggedin/v1/settingsaccepts every setting, not only the limit and the login mode. - Improve: Fewer database queries on each page: settings that are often unset are stored so they load with the rest, and pages that don't sign anyone in no longer load the translations to check a setting.
- Fix: Checking a password without signing in, such as WooCommerce's "current password" field, an application password, or the first step of two-factor login, no longer signs the user out of their other devices under Logout All or Logout Oldest. With a two-factor plugin, devices are signed out only once the code is entered.
- Fix: The Block New message, and its unlock link, now show through Ultimate Member's login form and Limit Login Attempts Reloaded, which replaced them with an "incorrect password" error.
- Fix: The old force-logout link now also checks that the user can manage options.
- Fix: Logout Oldest skips sessions that already expired, and ends as many as needed when the limit was lowered.
- Fix:
wp loggedin sessions listno longer shows leftover sessions on a site that stores sessions elsewhere, such as Redis. - Fix: Deleting the plugin now also removes the review notice's settings, and on multisite removes Loggedin's settings from every site.
- Changed: Requires WordPress 6.5.
- Changed: Renamed to "Loggedin - Session Manager: Limit Concurrent Logins & Auto Logout", now that auto logout is built in.
- Changed: Force Logout moved to Manage › Sessions, and Support is now Help.
- Changed:
loggedin_session_invalidatedpasses the hashed session token instead of the raw one. - Changed:
loggedin_error_messagealso passes the user, andloggedin_initpasses thePlugininstance. - Changed: Sites updating from an earlier version keep self-unlock, the administrator exemption and sign-out on password change off until turned on.
- Fix: Some valid add-on license keys were rejected as invalid. Keys containing a
%followed by two characters from 0–9 or a–f, in either case (for example%bB) were shortened before being sent to the licensing server. Affected add-ons could not be activated and so stopped receiving updates.
- New: Logout All Users — sign out every user on the site in one click from the Force Logout panel, with a confirmation dialog. Instant at any user count, and the admin who triggers it stays logged in.
- New:
wp loggedin sessions destroy-all— the same site-wide logout from WP-CLI. - New: REST endpoint
POST /loggedin/v1/sessions/destroy-allbacking the admin button. - New:
loggedin_logout_all_usersaction fired when a site-wide logout is triggered, andloggedin_session_invalidatedaction fired for each stale session as it is rejected. - Improve: The site-wide logout goes through the standard
WP_Session_TokensAPI, so it works with any session storage backend.
- Improve: Faster settings reads — the plugin's settings are now built once per request instead of on every read, cutting repeat work on each login and admin page load.
- Improve: Loggedin is now published under the Foxe Labs brand. Nothing about how the plugin works has changed.
- Improve: Updated every link in the plugin to the new foxelabs.com product pages and docs.foxelabs.com documentation.
- Improve: Removed the leftover Loggedin section on Settings → General. It only pointed at the real settings page and has been redundant since 2.0 — settings live under Users → Loggedin.
- Improve: Dropped the manual translation loading call — WordPress has loaded translations for wordpress.org plugins by itself since 4.6, so the call was redundant.
- Compat: Tested with WordPress 7.1.
- New: WP-CLI support — manage Loggedin from the command line with
wp loggedin sessions(list, count, destroy) andwp loggedin settings(list, get, set). Runwp help loggedinfor the full reference. - New:
wp loggedin sessions destroy <user> --token=<hash>signs a user out of a single device instead of all of them. - New:
loggedin_cli_initaction so add-ons can register their own subcommands under thewp loggedinnamespace. - New:
loggedin_destroy_sessionaction fired when an individual session is destroyed. - Improve: Renamed to "Loggedin - Session Manager, Limit Concurrent Logins & Force Logout" to reflect the plugin's broader scope. Nothing about the concurrent-login limiting has changed — same settings, same behaviour, same plugin.
- Improve: The CLI refuses to write a setting the sanitizer would reject, so a typo can no longer silently reset your login logic to the default.
- Improve: CLI commands are only loaded on WP-CLI requests — a normal page load doesn't pay for them.
- New: Review-request notice restored, powered by the
duckdev/wp-review-noticelibrary and scoped to the Loggedin settings screen with a 7-day delay. - Improve: Legacy review-notice state migrated to the new storage keys so users who already dismissed the prompt stay dismissed.
- Improve: Admin notices now render inside the plugin's centered page column instead of above the header.
- Fix: Left-hand gap between the plugin header and the admin sidebar caused by WordPress's default
#wpcontentpadding.
- New:
loggedin.admin.tabsJS filter — addons can register their own React component as a tab in the Loggedin admin nav, with optionalbefore/afterpositioning hints. Powers the new Active Sessions addon. - New: Cross-sell banner on the Force Logout panel routed through
loggedin.settings.force_logout.cross_sellso addons can hide or replace it once installed. - Improve: Addon card layout reworked — primary CTA pinned to the left of the footer, "More details" link on the right, title-cased license button labels.
- Fix: The v2 → v3 settings migration never ran on existing installs, leaving legacy option keys in place after the upgrade.
- New: Modern React-powered admin under Users → Loggedin with two tabs — Settings (concurrent-login limit + login logic + Force Logout panel) and Add-ons (catalogue + license management).
- New: REST API at
/loggedin/v1/for settings, session management and add-on licensing. - New: Unified
loggedin_settingsoption registered withshow_in_rest, readable and writable by the React admin and by external integrations through the standard core-data flow. - New: Force Logout panel now accepts a user ID, email or username — the resolver detects the input shape automatically.
- New: Add-ons module powered by Freemius — official add-ons (Real-time Logout, Limit Per User, Limit Per Role) self-register via the new
loggedin_register_addonfilter and appear in the Add-ons tab. - New: JavaScript extension slot — add-ons can append their own React
PanelBodyto the Settings tab via theloggedin.settings.panelsfilter. - New: Documented PHP hook surface —
loggedin_init,loggedin_settings_defaults,loggedin_admin_script_vars,loggedin_addons_catalog,loggedin_destroy_oldest_sessionand more. - Improve: Reorganised plugin structure (PSR-4 namespaces under
DuckDev\Loggedin\) and aligned with WordPress Coding Standards. - Improve: Comprehensive sanitisation pass across every input and option write path.
- Improve: PHP 7.4 is now the minimum supported version. For the full release history, see the changelog.