
Proofwright
| 开发者 | sirahama |
|---|---|
| 更新时间 | 2026年8月6日 20:55 |
| PHP版本: | 8.1 及以上 |
| WordPress版本: | 7.0 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
/.well-known/security.txt + Vulnerability Disclosure Policy publisher.
Tamper-evident evidence log. An append-only, cryptographically verifiable log of the material actions taken on your site.
Not legal advice. A "not legal advice" disclaimer appears on every generated document and report.
Related plugin
This plugin is complete and fully functional on its own. Some further capabilities — continuous vulnerability monitoring, the SRP incident workflow, the supplier-conformity register, exportable evidence packs, a cross-site fleet console and team review — are provided by a separate plugin, Proofwright Pro, available from proofwright.eu. They are not part of, and not required by, the plugin in this directory.
屏幕截图:
常见问题:
Does this make my site CRA-compliant?
No. Proofwright provides the workflow and the provable evidence; compliance is your legal responsibility. The "not legal advice" disclaimer appears on every generated document and report.
What does this plugin include?
Everything it needs to be useful on its own: component inventory, the SPDX 2.3 / CycloneDX 1.5 SBOM, immutable hash-chained snapshots with diff, the posture score and on-site readiness engine, the scope wizard, the CRA document generator, the compliance calendar, the cross-framework crosswalk, the security.txt / VDP publisher, and the tamper-evident evidence log — all fully functional, with no restrictions. Continuous vulnerability monitoring, the SRP incident workflow, the supplier register, exportable evidence packs and a cross-site fleet console are provided by a separate plugin, Proofwright Pro (see "Related plugin").
Does the plugin send my data anywhere?
No. This plugin runs entirely on your server — the readiness engine and SBOM make no external calls, and there is no licence check or phone-home of any kind.
更新日志:
- Fixed the software inventory listing build tools (npm dev dependencies) as if they were part of your site. Re-scan after updating.
- Fixed a fatal error when exporting CRA documents. Now translated into all 23 EU languages plus Arabic.
- Now available in 14 European languages. Bundled translations are loaded correctly.
- Added the full GPL-2.0 licence text to the package; removed an unused generated file.
- The posture-score breakdown, the SBOM change-since-last-snapshot view, and the attestation-renewal check now run on every install with no restrictions. Served pages load their stylesheet via the WordPress style API.
- Minor packaging fix.
- Housekeeping: removed unused image files from the package.
- Pages the plugin serves now link a packaged stylesheet instead of embedding CSS; documents you download keep their styles inline so the saved file works on its own.
- The plugin is fully functional with no restrictions of any kind: all feature gating removed, no licence checks, and the plugin no longer defines global WordPress constants. Further capabilities are provided by a separate plugin.
- Packaging refresh for the plugin directory; no functional changes since 0.23.2.
- Every feature in the plugin is fully functional, with no restrictions of any kind.
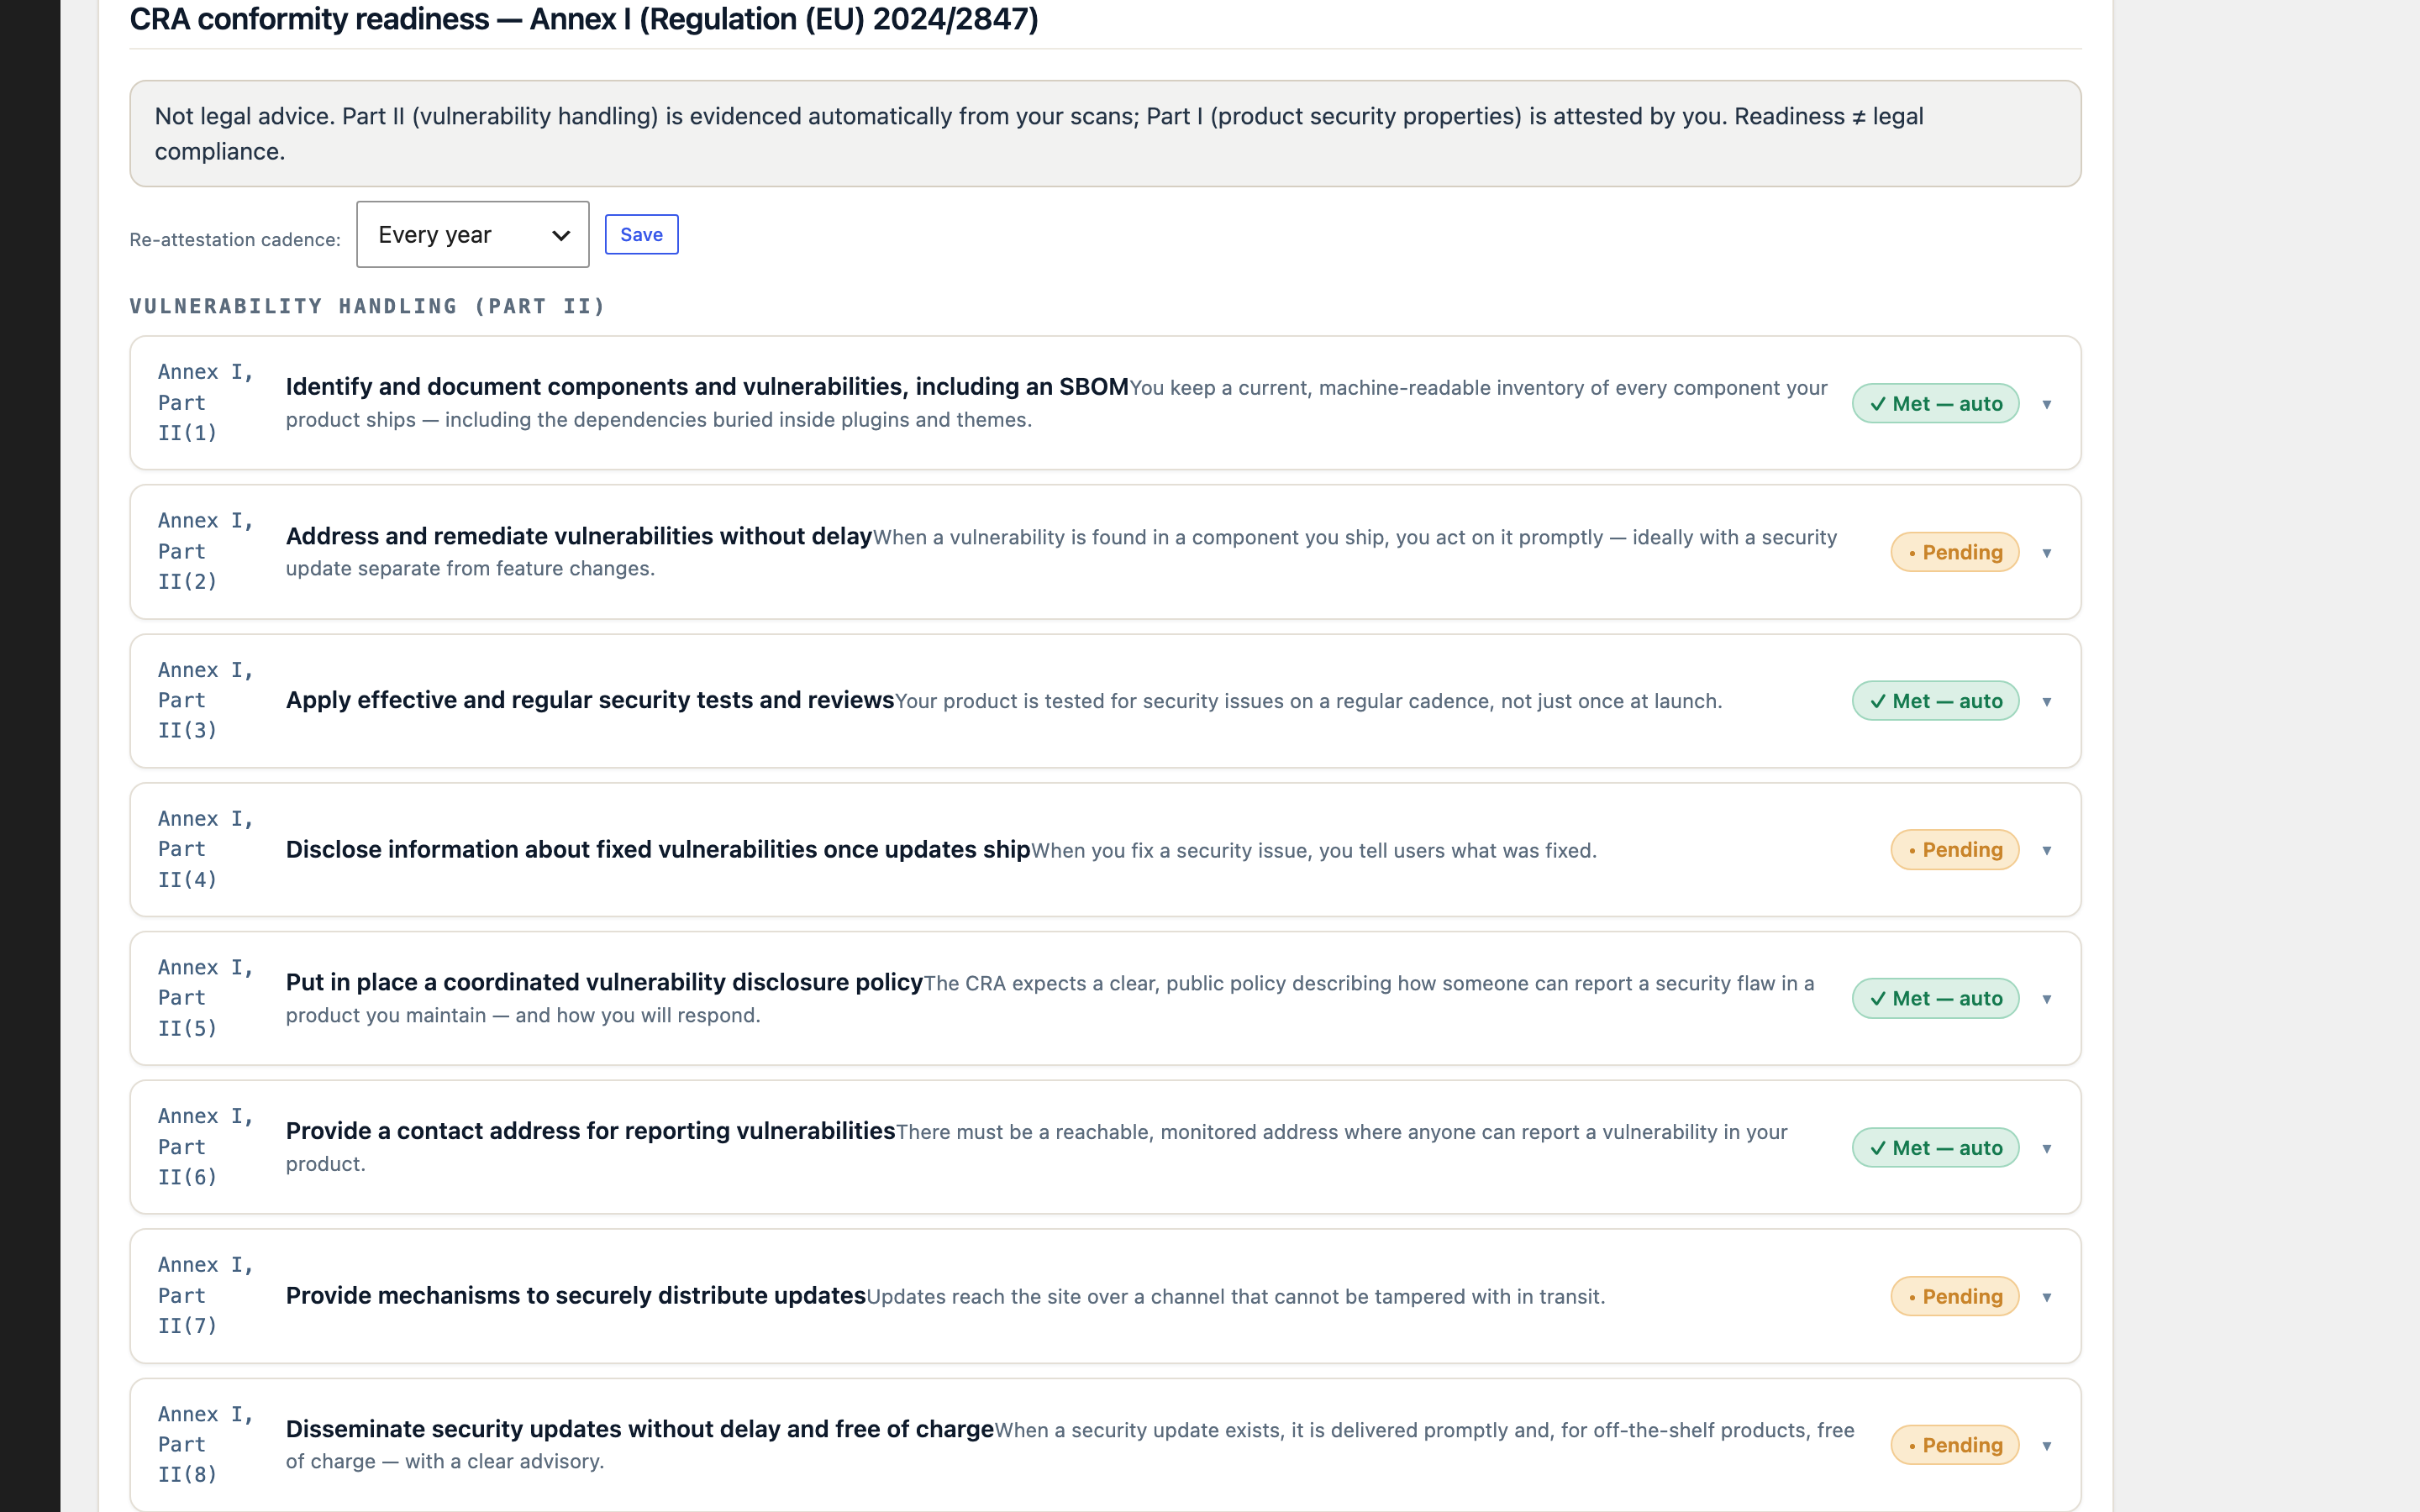
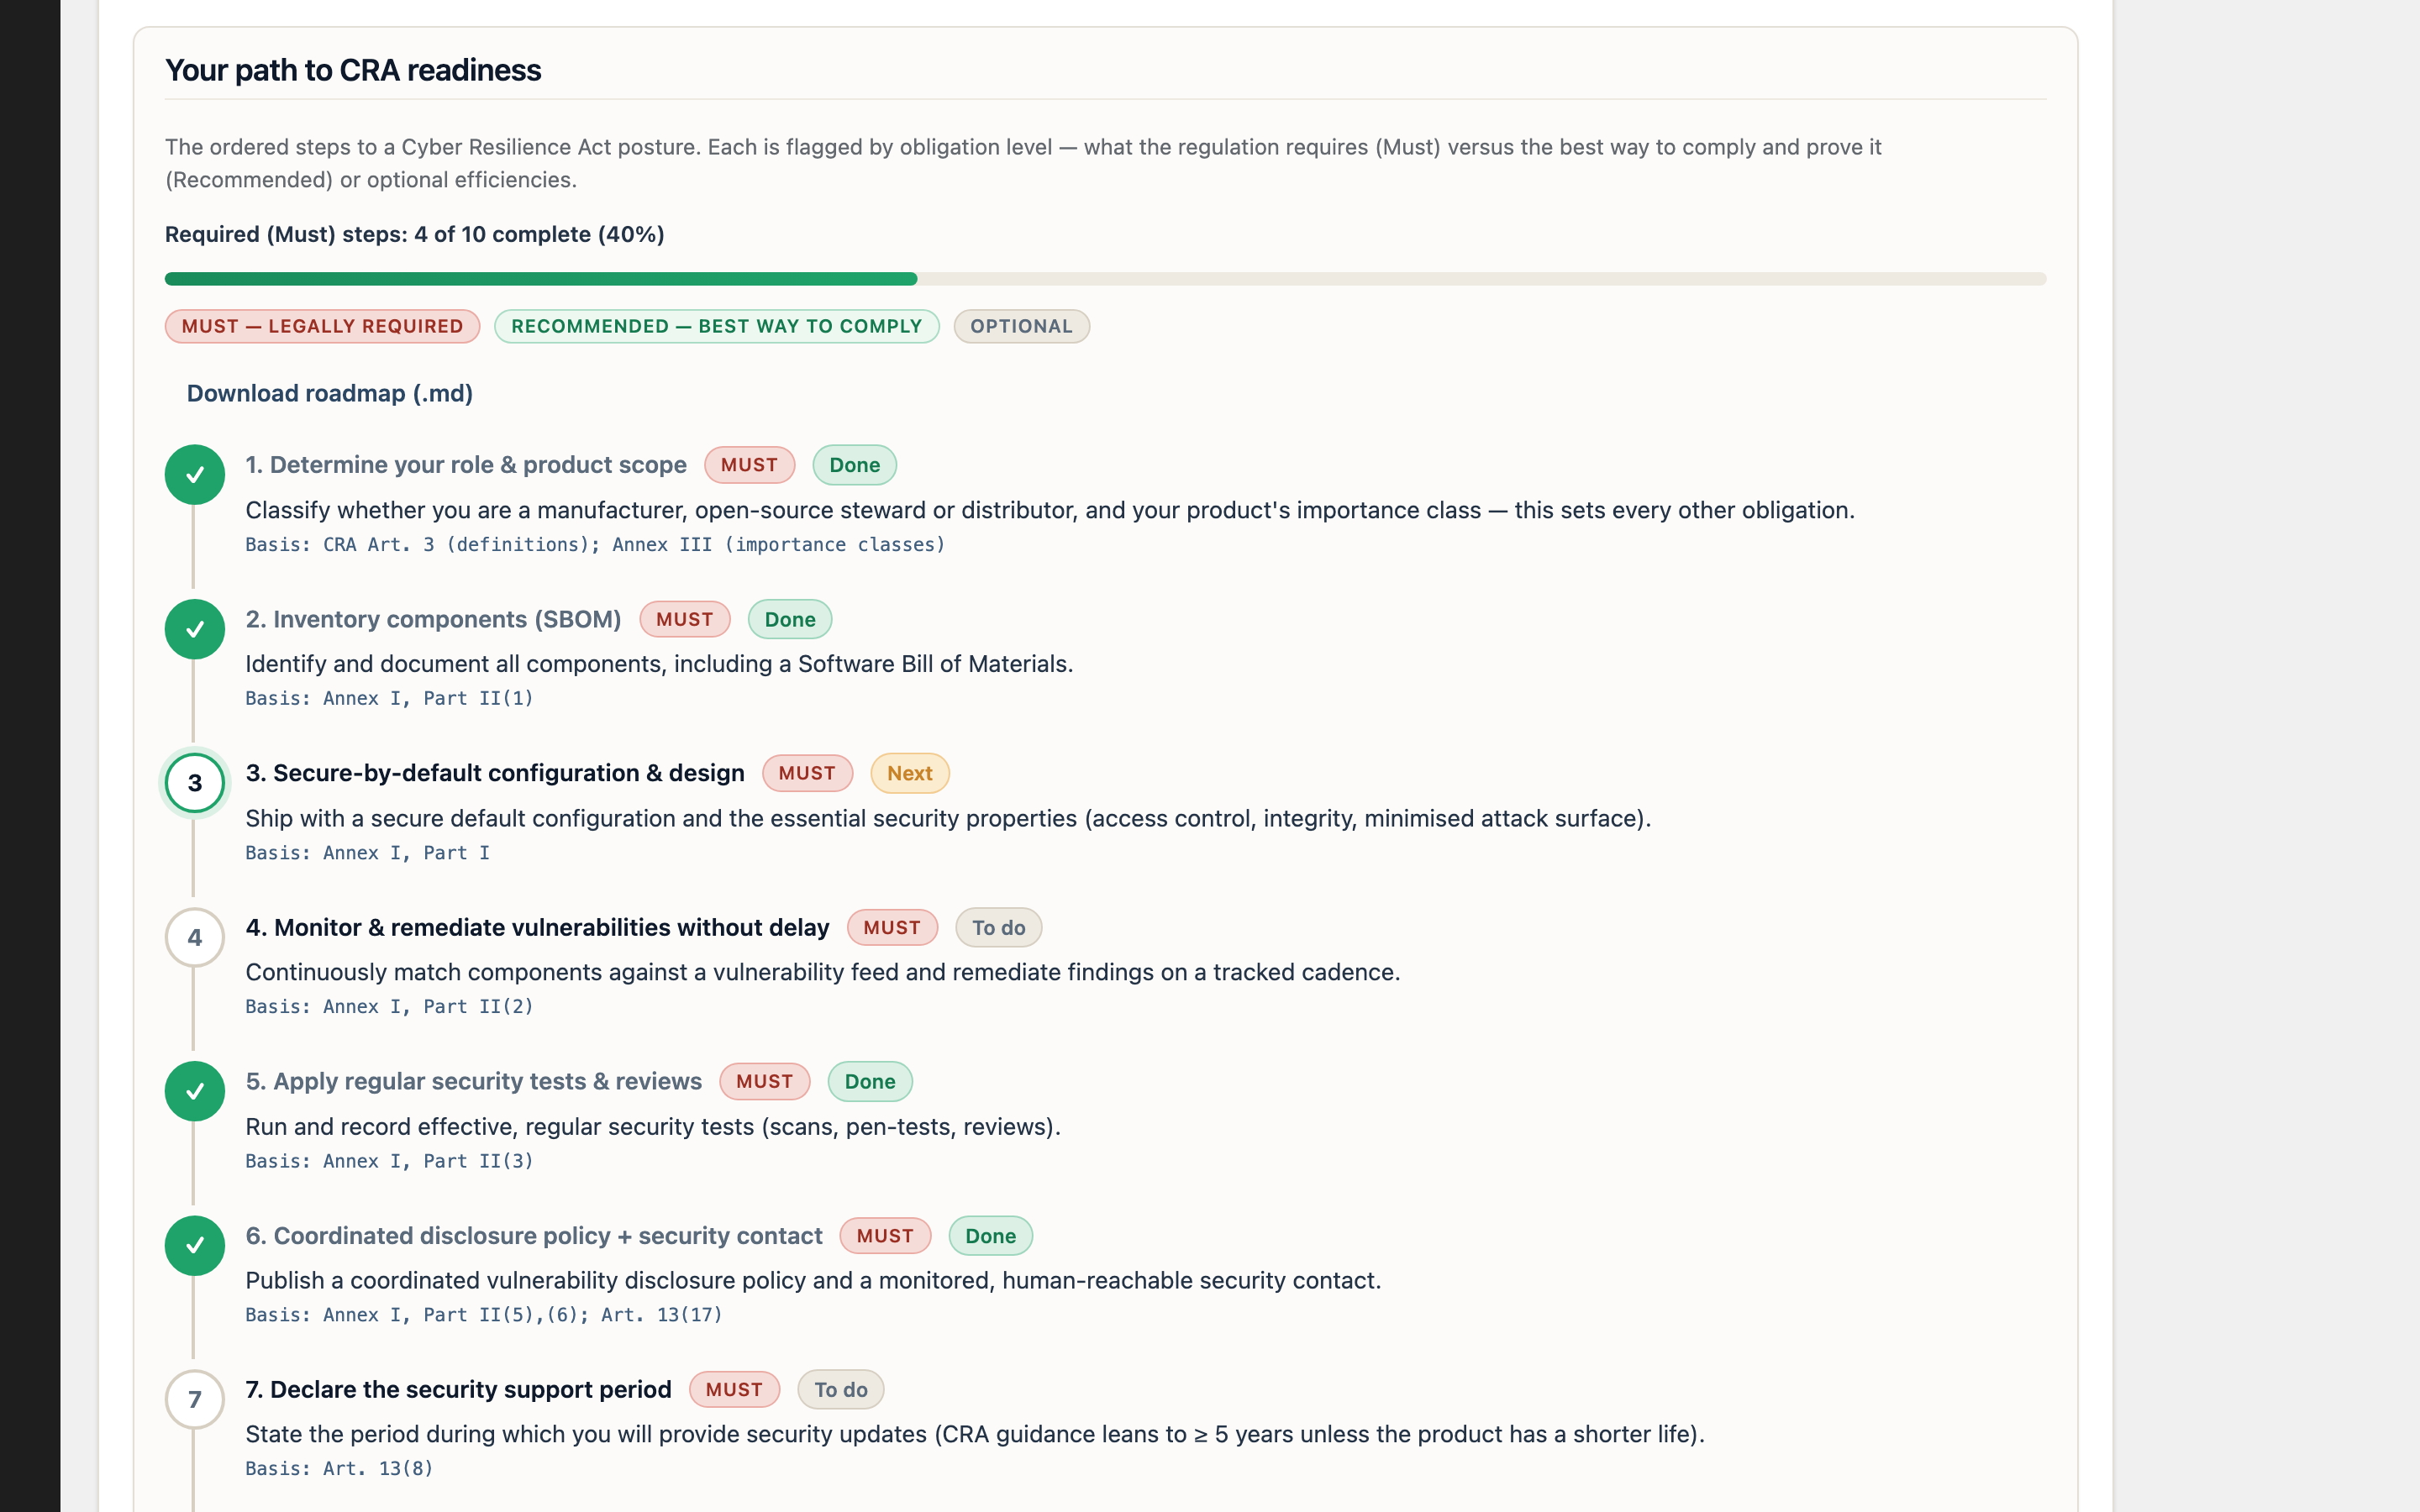
- CRA readiness roadmap, a compliance calendar with iCal export, a cross-framework control crosswalk (ISO/IEC 27001, SOC 2, NIS2), and the on-site readiness engine mapped to CRA Annex I.
- Annex II "Information and Instructions to the User" document generator; front-end (npm/yarn) dependency scanning folded into the SBOM.
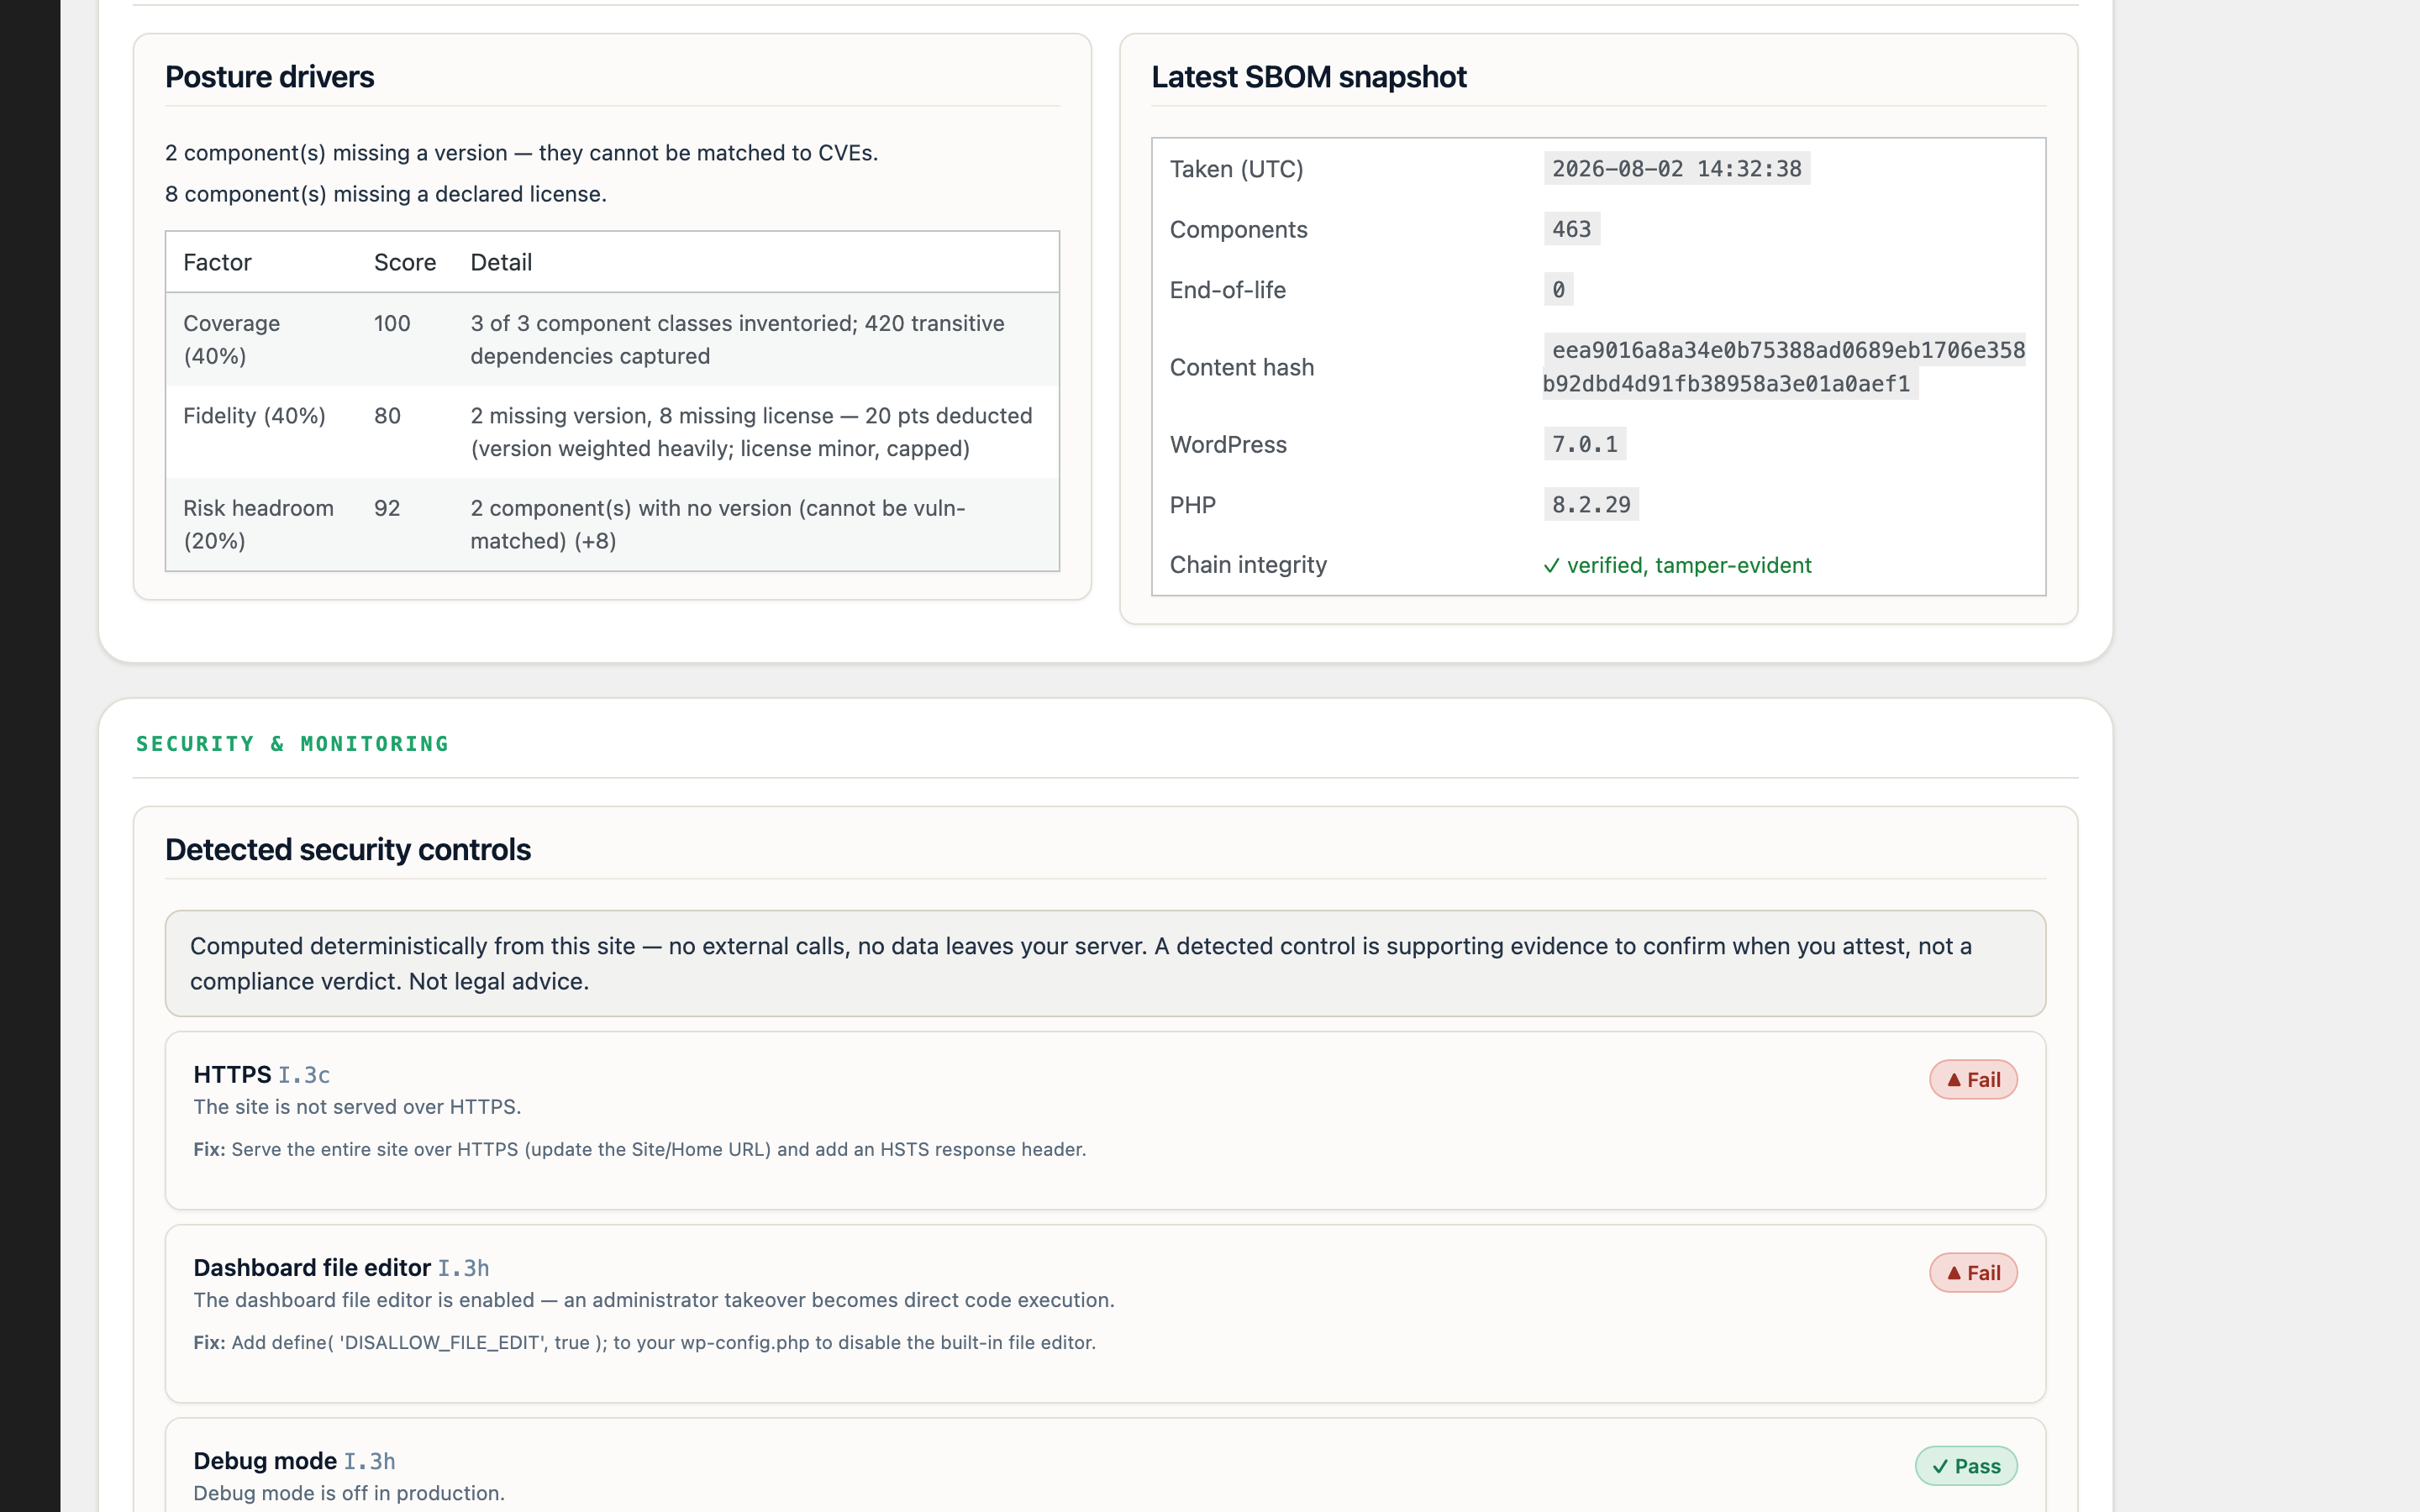
- Readiness engine: deterministic, on-site security-posture detection mapped to CRA Annex I (no external calls). Detected controls are shown as evidence; gaps are shown with copy-paste remediation guidance.
- Inventory + SBOM (SPDX 2.3 / CycloneDX 1.5) with PURLs and direct/transitive depth; immutable, hash-chained SBOM snapshots with diff-over-time and EOL flagging; deterministic posture score; scope wizard; CRA document generator; tamper-evident evidence log. Pre-flight secret + PII scan on every export.
- Initial release: SBOM spine + compliance posture score.