
Rogue Admin Detector
| 开发者 | UsmanR |
|---|---|
| 更新时间 | 2026年11月19日 19:12 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
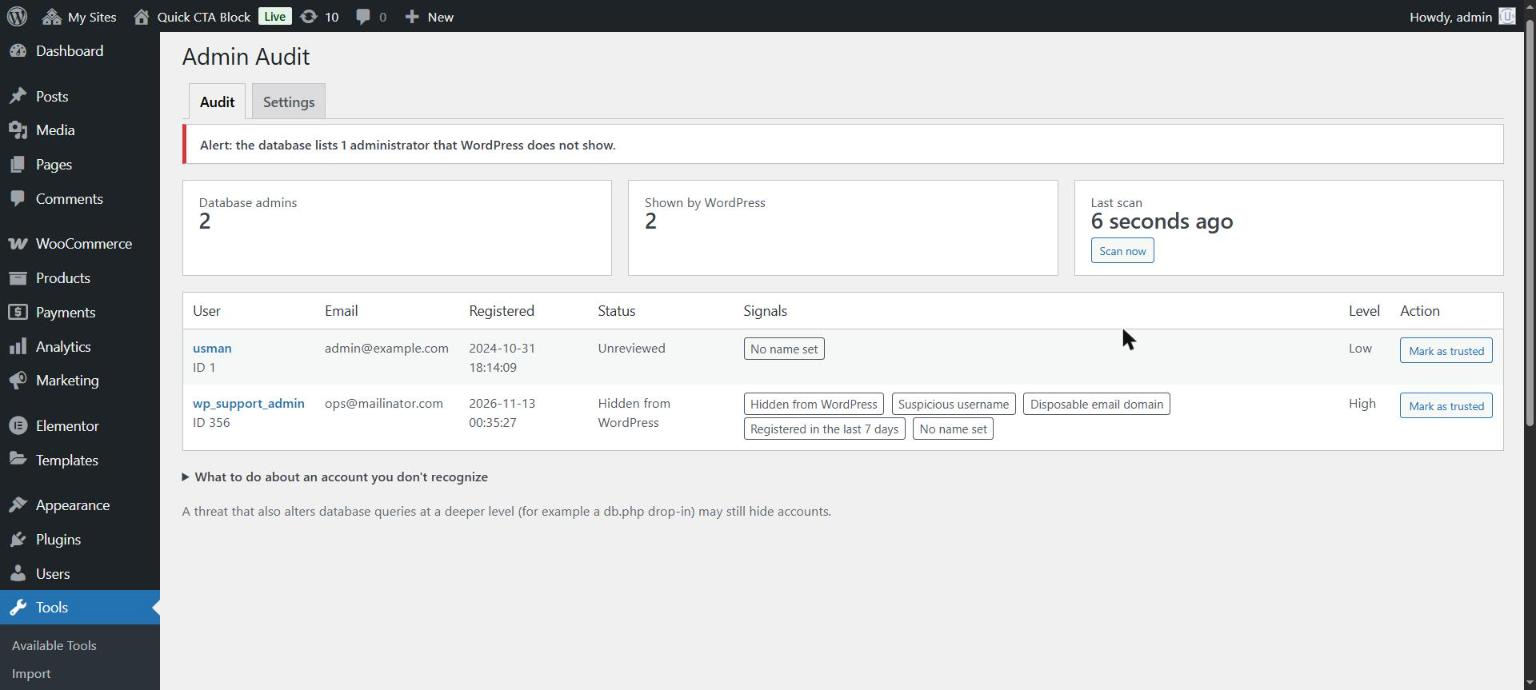
- Lists accounts that have administrator rights in the database (up to 500 accounts, ordered by user ID).
- Compares that with the Users screen and the WordPress user counts, and flags any account WordPress does not show ("Hidden from WordPress").
- Lets you mark your own admins as trusted so unreviewed ones stand out.
- Shows plain-language warning signals such as a suspicious username, a disposable email domain, or a brand-new account.
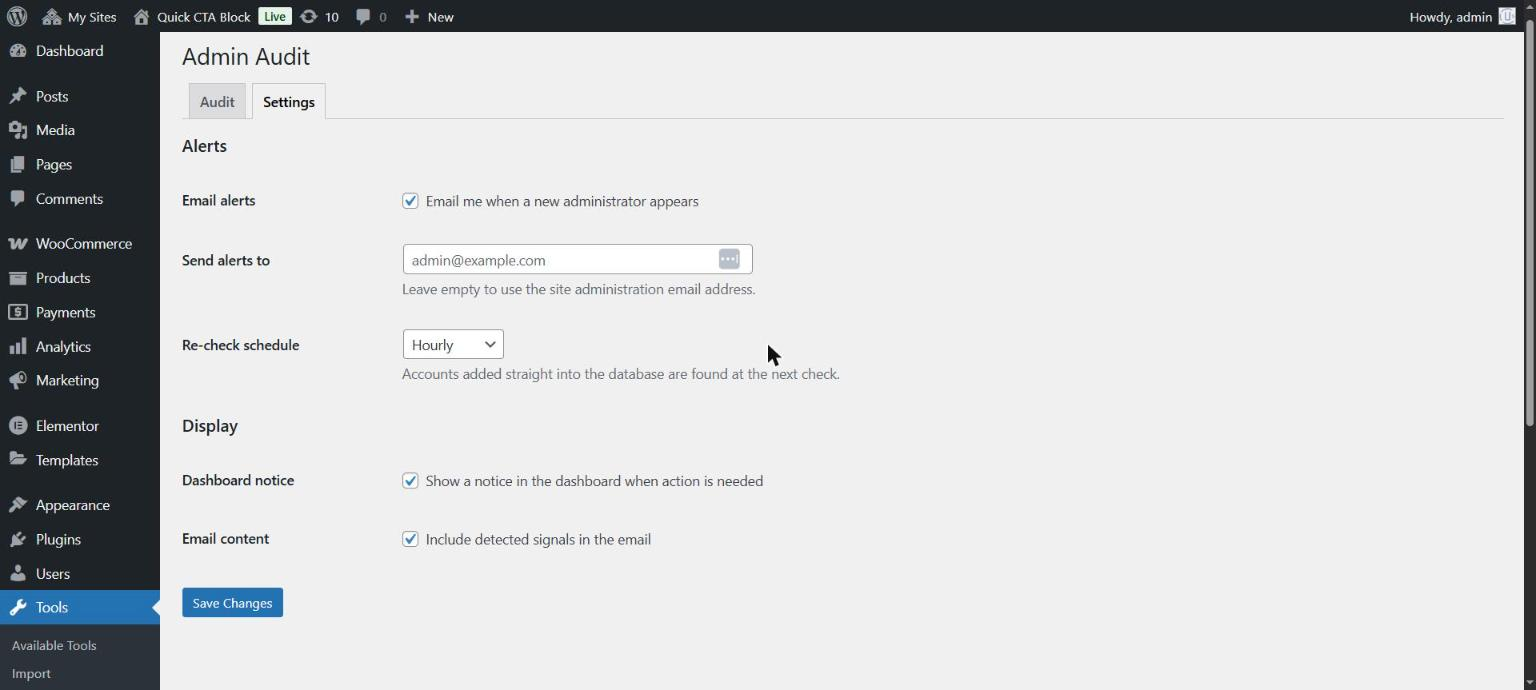
- Emails you when a new administrator appears, and re-checks on a schedule so accounts added straight into the database are caught too.
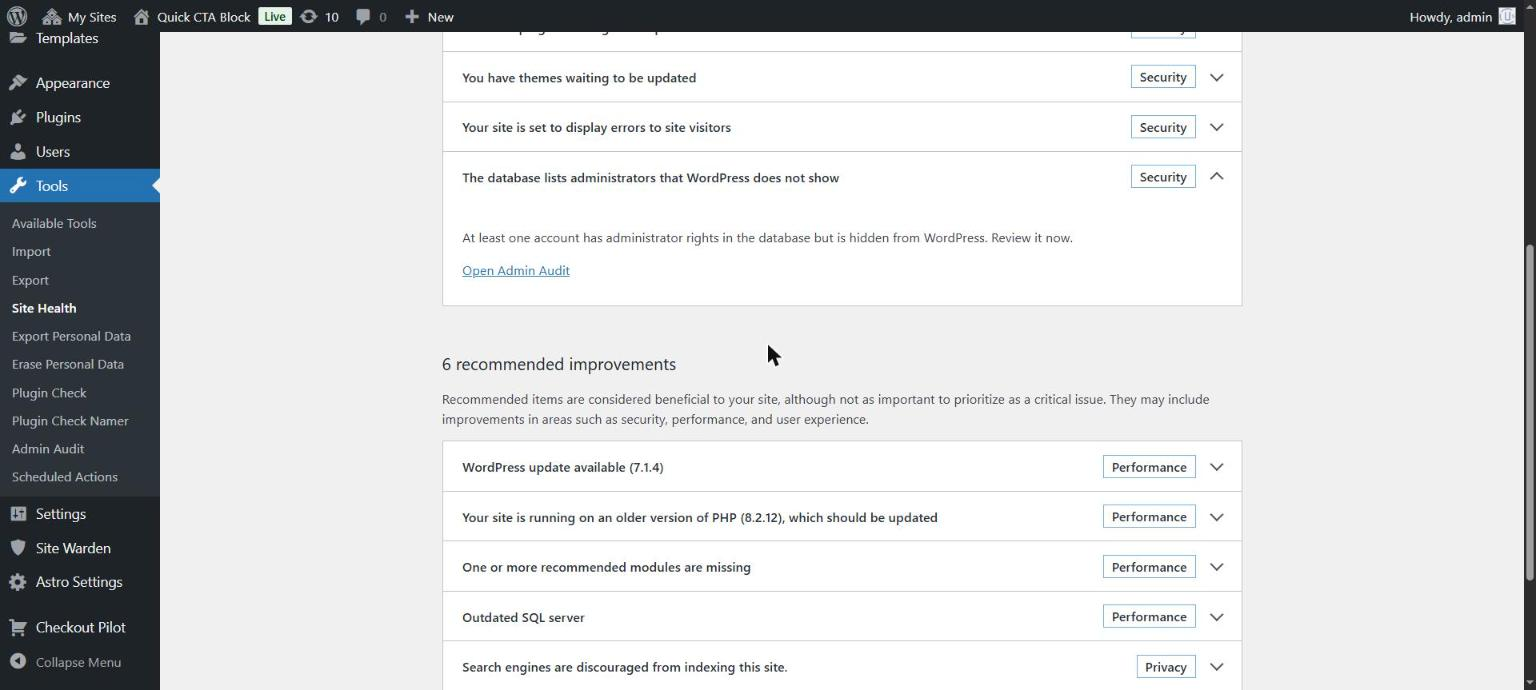
- Adds a Site Health test and a WP-CLI command that does not change any users:
wp rogue-admin scan.
安装:
- Upload the plugin folder to
/wp-content/plugins/, or install it from the Plugins screen. - Activate it.
- Open Tools > Admin Audit and review your administrators.
- Optional: set the alert email on the Settings tab.
屏幕截图:
常见问题:
Does it delete suspicious users?
No. Version 1.0 only reports. Open the user in the normal Users screen, or follow the steps on the Audit page.
Does it send data anywhere?
No. Everything stays on your site. The only message sent is the alert email you enable.
Why was I not alerted at once when an account was added in phpMyAdmin?
Direct database inserts do not trigger WordPress events. The scheduled check finds them at its next run (hourly by default), or click Scan now.
Does it work on multisite?
Yes, when activated on an individual site. Network-wide reporting is not included.
The page says everything agrees. Is my site clean?
It means the database and WordPress agree about administrators. It is not a malware scan.
Which accounts are detected?
Detection looks for the administrator role (and flags a suspicious user_level). Accounts granted individual capabilities without the role are not detected in v1.0.
Is there a limit on how many administrators it checks?
Yes. The audit lists up to 500 administrator accounts, ordered by user ID. Sites with more than 500 administrators are marked as capped and the newest accounts may not be listed.
更新日志:
- Initial release.