
ScanForge File & Theme Security
| 开发者 | adnanlimdi |
|---|---|
| 更新时间 | 2026年10月31日 22:47 |
| 捐献地址: | 去捐款 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
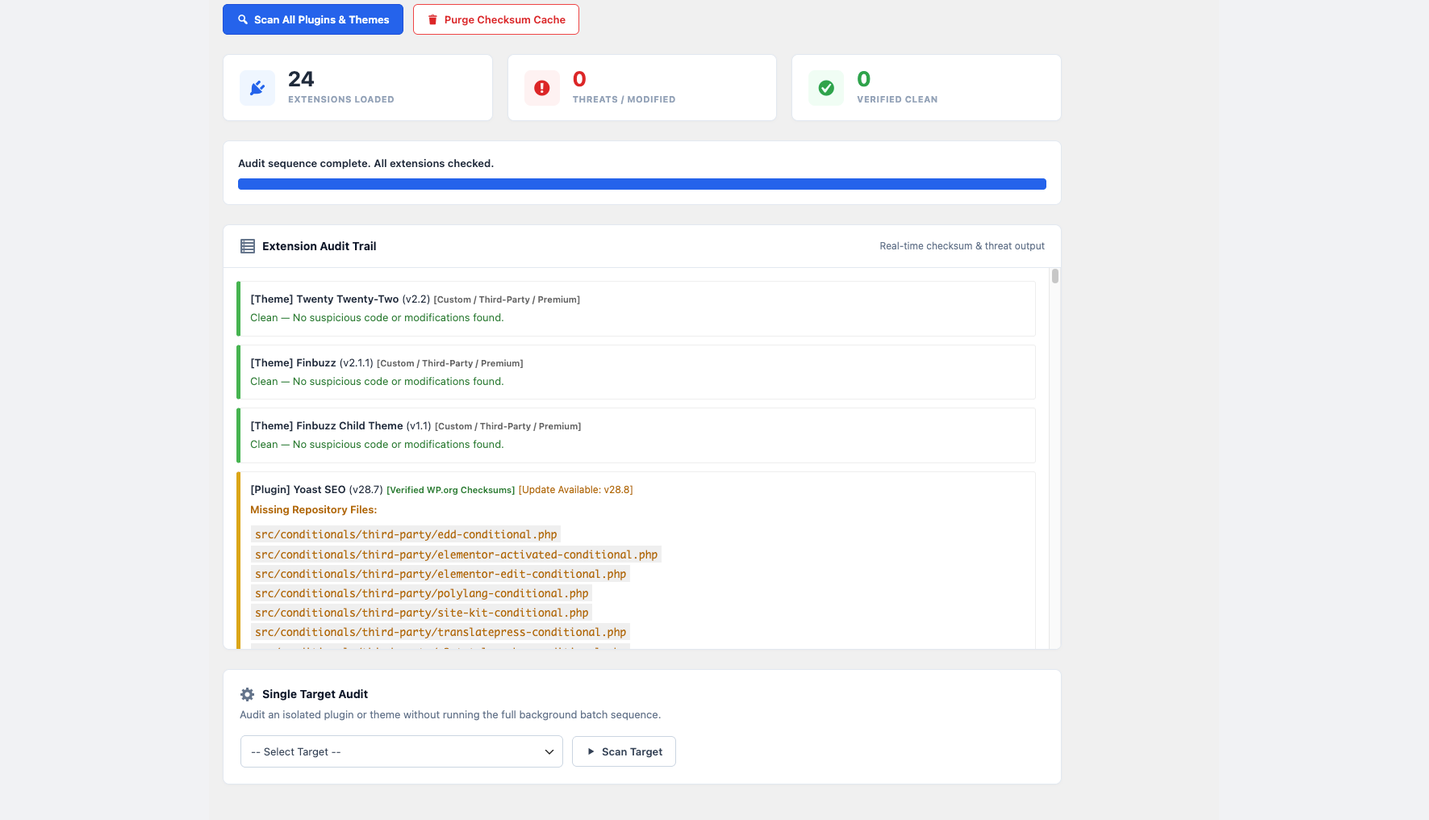
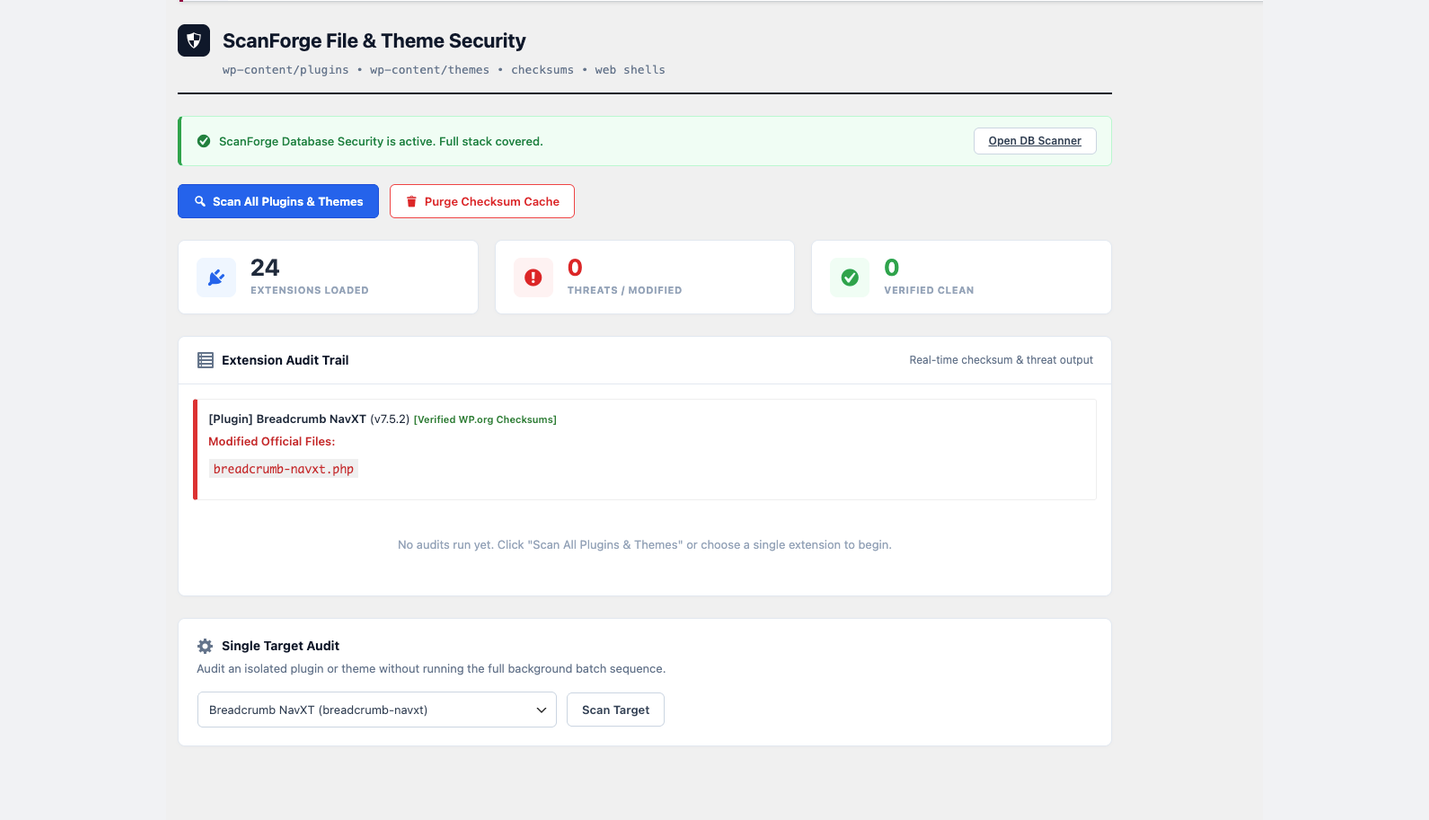
- Official WordPress.org Checksum Verification: Instantly identifies modified repository files, unauthorized rogue additions, or missing script components by comparing local hashes directly with official release manifests.
- Web Shell & PHP Backdoor Detection: Heuristically matches file contents against known malicious signatures, including WSO, b374k, FilesMan, c99, and r57 web shells.
- Injected File Manager Discovery: Detects unauthorized dropped file management utilities (such as Tiny File Manager variants) via distinctive functional signatures (
FM_ROOTPATH,FM_SESSION_KEY). - High-Risk Code Pattern Flags: Uncovers dangerous execution wrappers such as nested
eval(base64_decode()), dynamic assertion backdoors, and shell execution handling raw superglobal inputs ($_POST,$_GET,$_COOKIE). - Intelligent Vendor Whitelisting: Automatically ignores standard dependency trees (
vendor/,node_modules/,tests/) to eliminate false alarms and maximize scanning speed. - On-Demand & Lightweight: Runs sequential, memory-safe audits only when you click "Scan", leaving zero background cron overhead on your server.
- Full-Stack Security Integration: Seamlessly pairs with ScanForge Database Security to audit SQL tables (
wp_posts,wp_options) alongside your filesystem scripts.
安装:
- Upload the
scanforge-file-securitydirectory to your/wp-content/plugins/directory, or upload the ZIP file directly via Plugins > Add New > Upload Plugin. - Activate the plugin through the Plugins screen in WordPress.
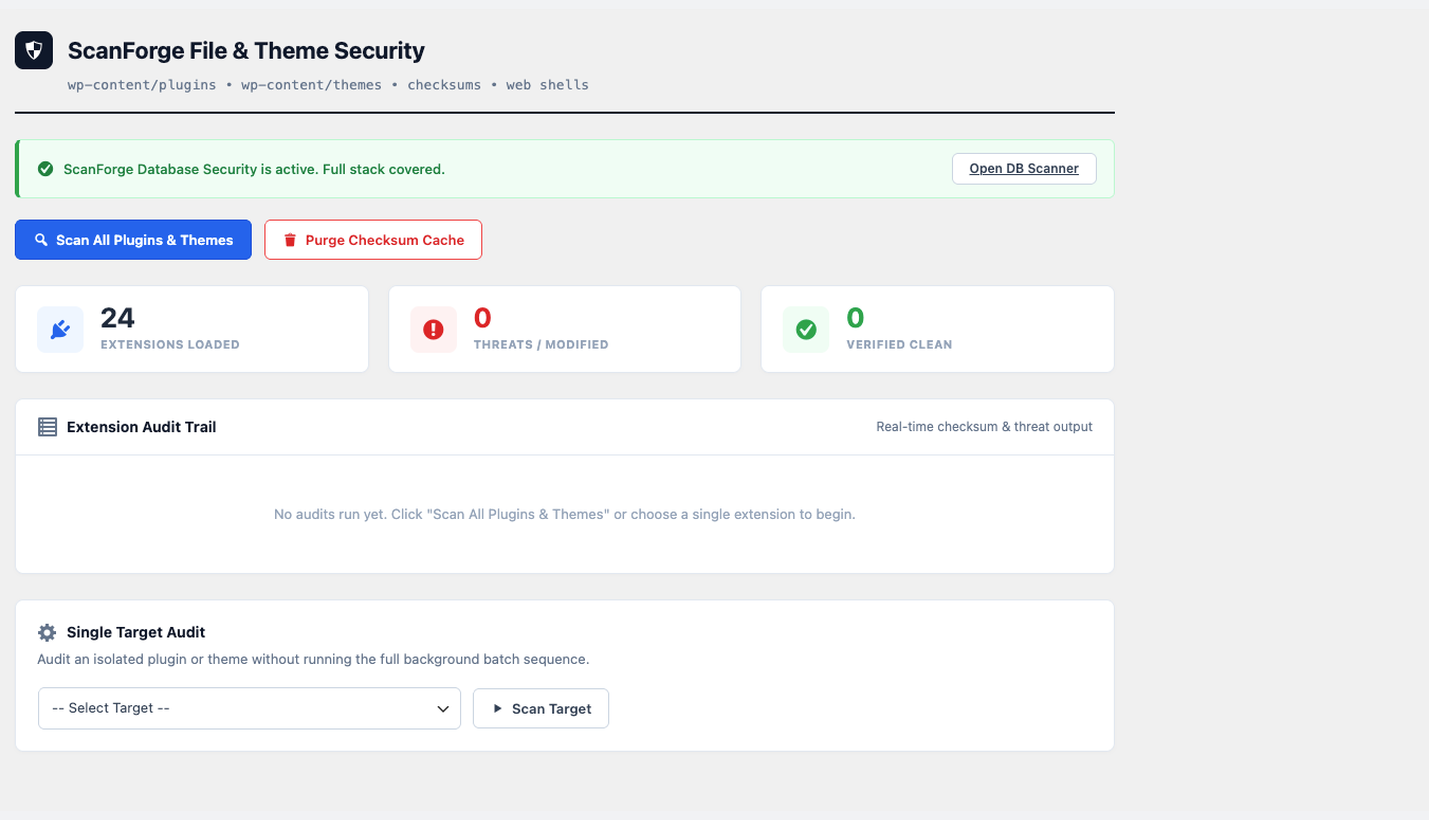
- Navigate to Tools > ScanForge Files to run a comprehensive audit, or click ScanForge File Audit on any individual row in Plugins > Installed Plugins.
屏幕截图:
常见问题:
How do I check if my WordPress plugin files have been hacked or modified?
Navigate to Tools > ScanForge Files and select Scan All Plugins & Themes. ScanForge connects to the WordPress.org Checksum API to compare your local plugin files against official release files. Any altered core files, missing scripts, or rogue injected PHP files will be highlighted in the audit log.
Can ScanForge audit single-file plugins?
Yes. Standalone root plugins (such as hello.php) are audited alongside multi-folder extensions for web shells, malicious eval strings, and unauthorized modifications.
Does this plugin run background processes or slow down page loads?
No. ScanForge contains zero background cron workers, continuous tracking scripts, or frontend overhead. Audits run strictly on demand when an administrator triggers them.
How does ScanForge handle third-party vendor directories?
To prevent false positives on legitimate composer libraries (like AWS SDKs or Symfony components), ScanForge ignores common library folders (vendor/, node_modules/, tests/) during static heuristic checks while still validating repository integrity.
How does ScanForge differ from all-in-one security suites?
Most comprehensive security plugins focus primarily on incoming network firewalls (WAF) and brute-force protection. ScanForge functions as a focused static file auditor and integrity validator designed to inspect actual PHP files and catch malicious code that slipped past firewalls.
How do I clean malicious database injections?
ScanForge File & Theme Security inspects filesystem scripts. To scan and remove malicious redirect scripts, spam links, and obfuscated payloads stored inside your MySQL database tables (wp_posts, wp_options, wp_comments), pair this tool with ScanForge Database Security.
更新日志:
- Fixed theme classification bug where official directory and default core themes defaulted to "Custom / Third-Party".
- Added automatic detection for bundled default themes (Twenty Twenty-Five, Twenty Twenty-Four, etc.) and WordPress.org theme directory listings.
- Refactored badge labeling in the admin audit trail to show "Official WP Theme".
- Updated UI cards and live statistic counters to maintain aesthetic consistency with ScanForge Database Security.
- Initial release.
- Added single and batch audit orchestration for plugins and themes.
- Integrated official WordPress.org Checksum API integrity checks with transient caching.
- Added automatic checksum cache flushing on plugin upgrades and manual cache purge utility.
- Integrated JSON-driven threat signatures for web shells and Tiny File Manager detection.
- Fully compliant with WordPress Coding Standards (WPCS).