SyncNet Patch Radar
| 开发者 | syncnetolivergiesbert |
|---|---|
| 更新时间 | 2026年11月2日 22:38 |
| PHP版本: | 8.0 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
SyncNet Patch Radar collects security alerts automatically and shows only what really matters: critical vulnerabilities in widely used products such as Windows, Exchange, NetScaler, FortiGate, Cisco, VMware, Java, Chrome or PHP.
An alert is shown when it
- is rated critical by the German Federal Office for Information Security (BSI / CERT-Bund), or
- is listed by the US agency CISA as actively exploited (Known Exploited Vulnerabilities), or
- is rated CVSS 9.0 or higher (adjustable), exploitable over the network without authentication, and was reported by the vendor itself (NVD),
- Clean list with search ("Am I affected?") and vendor filters
- Several critical vulnerabilities in the same product are combined into one card ("Google Chrome: 12 critical vulnerabilities") – one update usually fixes them all
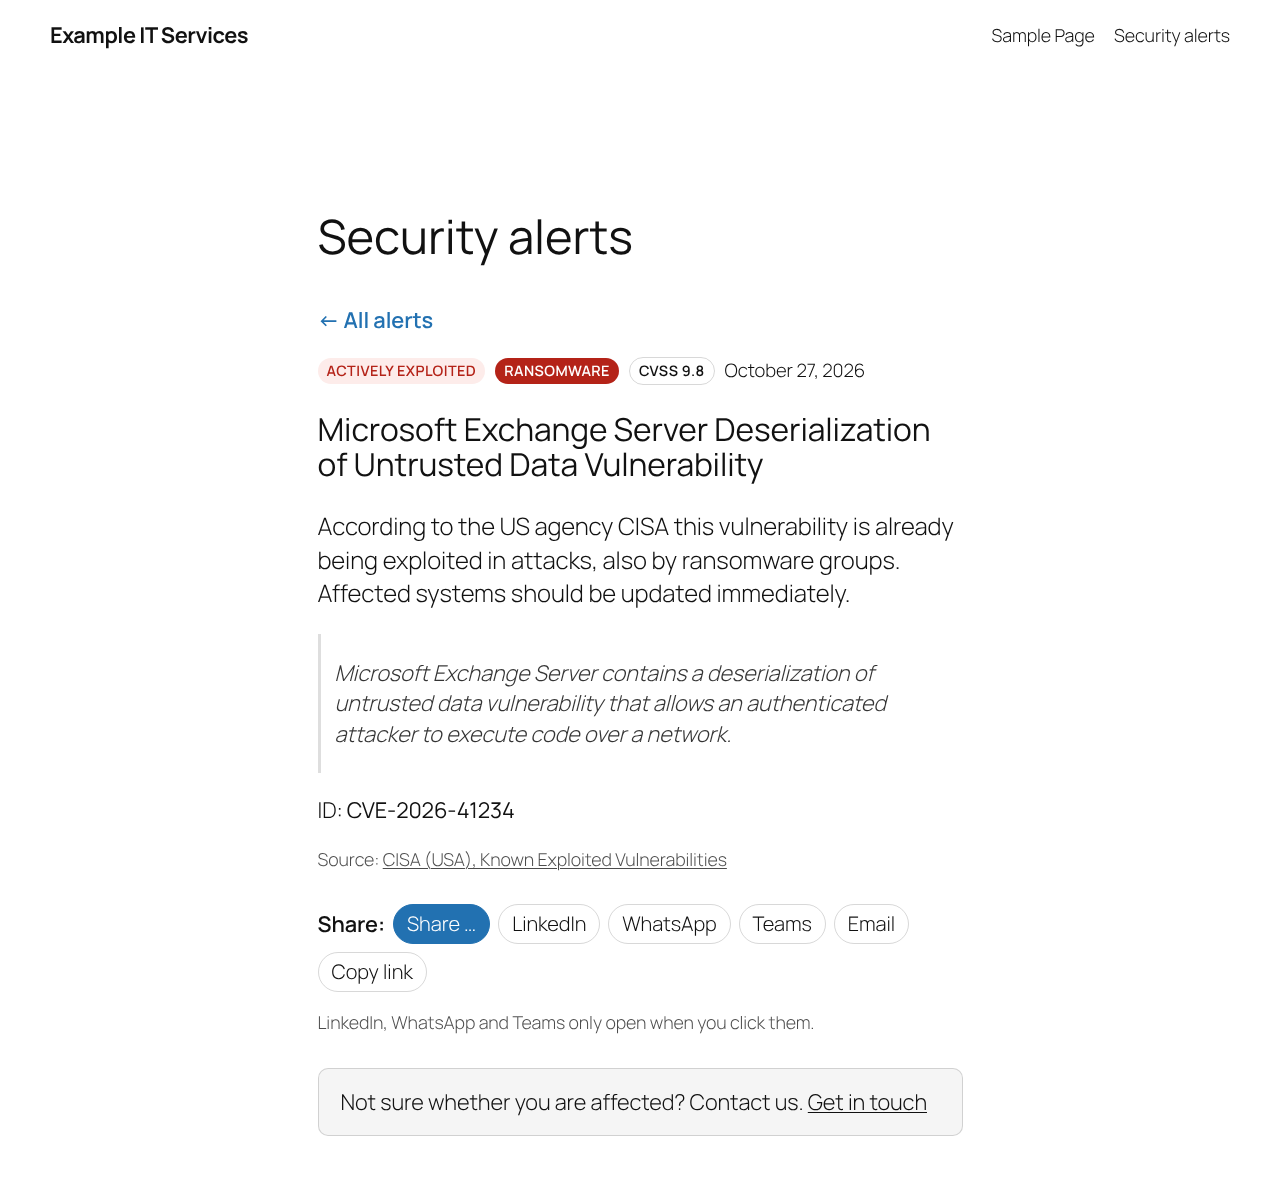
- Every alert and product group has its own page to share (LinkedIn, WhatsApp, Teams, email, copy link, native share on phones) – shared links always point to your site
- RSS feed for all alerts and one feed per vendor
- You choose where the subscription box and the share buttons appear: above, below or both
- Source and link to the original record on every card
- Optional small red dot on your menu item for the alerts page while a fresh, actively exploited vulnerability is listed (off by default)
- Optional one-line "latest critical alert" for your front page and a compact box for any page
- Optional call to action ("Not sure whether you are affected? Contact us")
- Check tool in the settings: enter a CVE ID and see which condition is met
- No tracking, no cookies, no external scripts or fonts – visitors never connect to third parties
- Nothing is fetched until you switch fetching on in the settings
- Translation ready
[syncnet_patch_radar]– the list (a draft page with it is created on activation)[syncnet_patch_radar_latest]– one discreet line with the newest alert[syncnet_patch_radar_box count="3"]– compact cards with a link to the list
安装:
- Install and activate the plugin. A draft page "Security alerts" with the shortcode
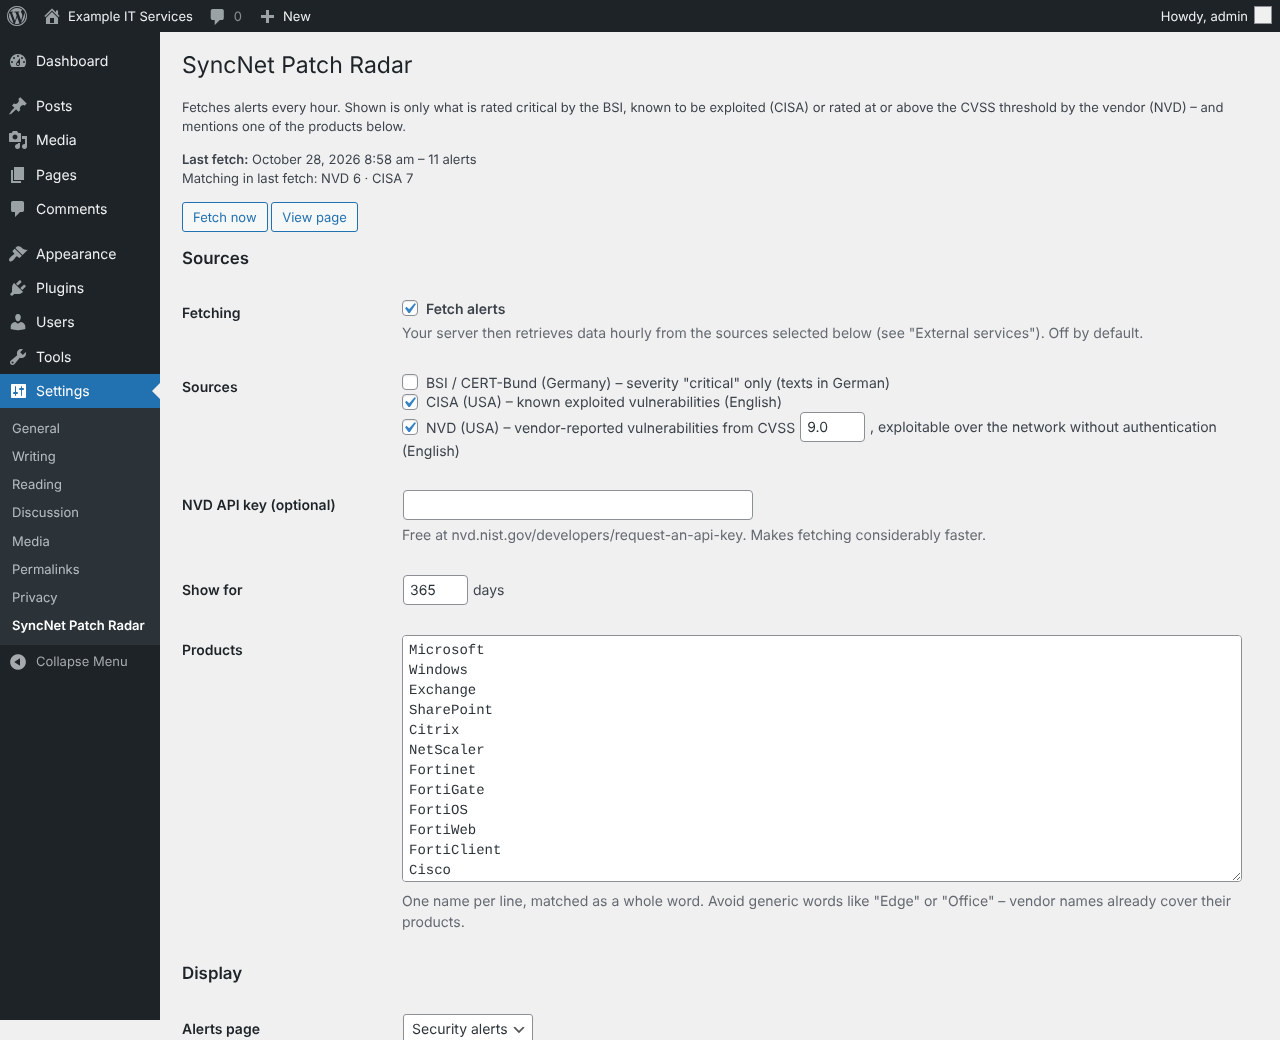
[syncnet_patch_radar]is created. Nothing is fetched yet and the plugin never adds menu items itself. - Go to Settings → SyncNet Patch Radar, choose sources, CVSS threshold and product list, tick Fetch alerts and save. The first fetch starts.
- Rename and publish the page when you are ready.
- Optional but recommended: request a free NVD API key and enter it – fetching becomes much faster.
- Recommended: set up a real cron job calling
https://your-site.example/wp-cron.php?doing_wp_cronevery hour, so fetching runs reliably even with page caching.
屏幕截图:
常见问题:
Why is the list empty after activation?
Nothing is fetched until you switch fetching on: go to Settings → SyncNet Patch Radar, tick "Fetch alerts" and save.
Why are some vulnerabilities missing?
Only critical ones in products from your list are shown – this is intentional. Use the check tool in the settings to see why a specific CVE is not listed.
Why are some texts in English or German?
BSI advisories are published in German, CISA and NVD descriptions in English. The plugin's own texts follow your site language.
Does the plugin slow down my site?
No. Data is fetched in the background and stored; pages only read the stored list. Search and filters run in the visitor's browser.
Can I show a credit for the author?
Yes, there is an option in the settings. It is off by default.
更新日志:
1.4.1
- Fix: on servers with a short PHP time limit the first fetch could be cut off, so no alerts appeared. The fetch now respects the time limit and continues on the next run.
- New settings: show the RSS subscription box above and/or below the list (or not at all), and the share buttons above and/or below a single alert.
- First public release.