
UX3 Security
| 开发者 | ux3security |
|---|---|
| 更新时间 | 2026年9月30日 06:13 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPL-2.0-or-later |
| 版权网址: | 版权信息 |
详情介绍:
- Web Application Firewall — blocks SQLi, XSS, and other common attack patterns
- Bot protection — detects and blocks bad bots, fake search-engine crawlers, anonymous bot traffic
- Spam protection — honeypot + content-based detection for forms
- Word filter — block requests matching custom keyword lists
- Geo-blocking — block traffic from specific countries
- Rate limiting — prevents brute-force and scraping
- Smart filter — one-click allow-list for false positives
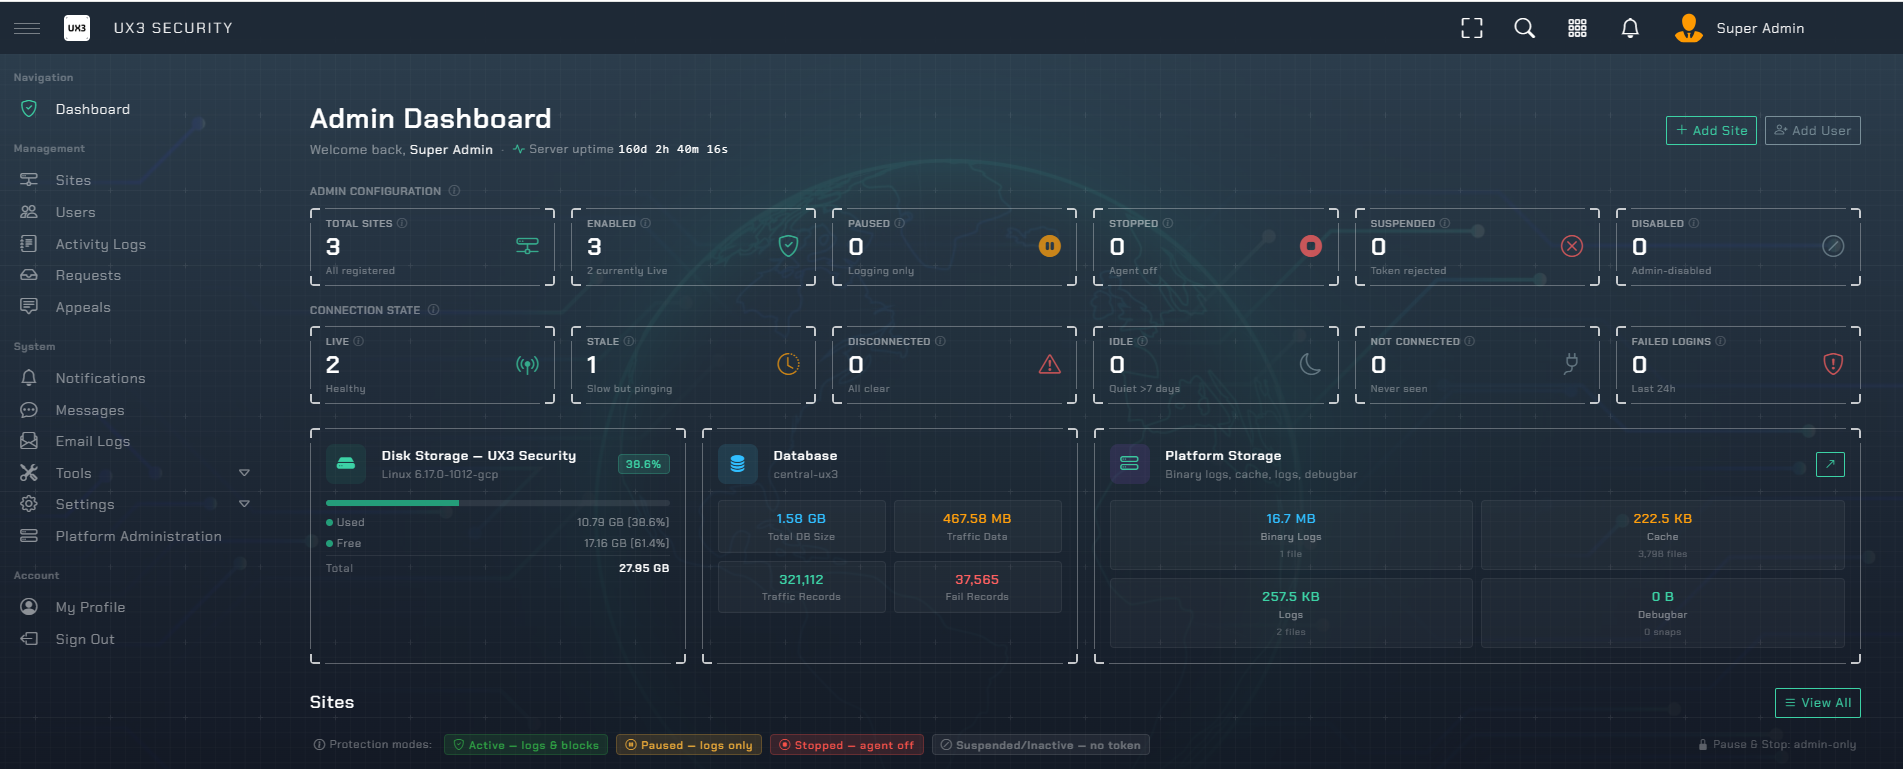
- Centralized dashboard — all your sites in one place at central.ux3security.com
- Real-time alerts — email notifications for attacks, disconnections, disk warnings, etc.
- Sign up at central.ux3security.com and add your site
- Copy the API URL and token from your dashboard
- Install this plugin and paste them into Settings → UX3 Security
- Enable protection — done. Manage rules from the dashboard.
安装:
- Upload the plugin files to
/wp-content/plugins/ux3-security/, or install via the Plugins screen in WordPress - Activate the plugin through the 'Plugins' screen
- Visit Settings → UX3 Security
- Review the Data Processing Consent section — this explains exactly what data the plugin sends to the UX3 Security API and to ip-api.com. Tick the consent checkbox only if you agree.
- Paste your API URL and API Token (from your UX3 Security dashboard)
- Tick "Enable UX3 Security protection" and Save
auto_prepend_file in your php.ini — see the Settings page for the exact directive.屏幕截图:
常见问题:
Do I need an account on central.ux3security.com?
Yes. The plugin is the agent — it works in conjunction with the central dashboard where you create accounts, add sites, and configure rules.
What happens if my site can't reach the API?
The agent caches firewall rules locally for 5 minutes. If the API is unreachable, it continues using the cached rules — your site stays protected even during brief network blips. After cache expiry, the agent skips silently rather than break your site.
Will this plugin slow down my site?
The agent is highly optimized — typical overhead is 1-3ms per request. Rules are cached on disk so most requests don't even need a database lookup.
Can I temporarily disable protection?
Yes — uncheck "Enable UX3 Security protection" on the settings page. No need to deactivate the plugin.
How do I withdraw consent?
Uncheck the consent checkbox on Settings → UX3 Security and save. The agent stops making outbound requests immediately.
How does the plugin display warning pages when a request is blocked?
Blocked visitors see a warning page served in an iframe from central.ux3security.com. The plugin does not cache warning-page HTML in your WordPress database or filesystem — the styled page is served live from Central each time.
Where are my settings stored?
In the WordPress options table — same place as other plugin settings. They're cleaned up automatically if you delete (not just deactivate) the plugin.
更新日志:
- Initial release
- WordPress wrapper for the UX3 Security agent (v1.1.0)
- Settings page for API URL / token / enable toggle
- Auto-detect existing auto_prepend_file config and recommend if not set
- Reports install_method = 'wp_plugin' to the dashboard