
Volixta Support – Helpdesk, Customer Support Ticket System & Customer Portal
| 开发者 | volixta |
|---|---|
| 更新时间 | 2026年11月9日 11:23 |
| PHP版本: | 8.1 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
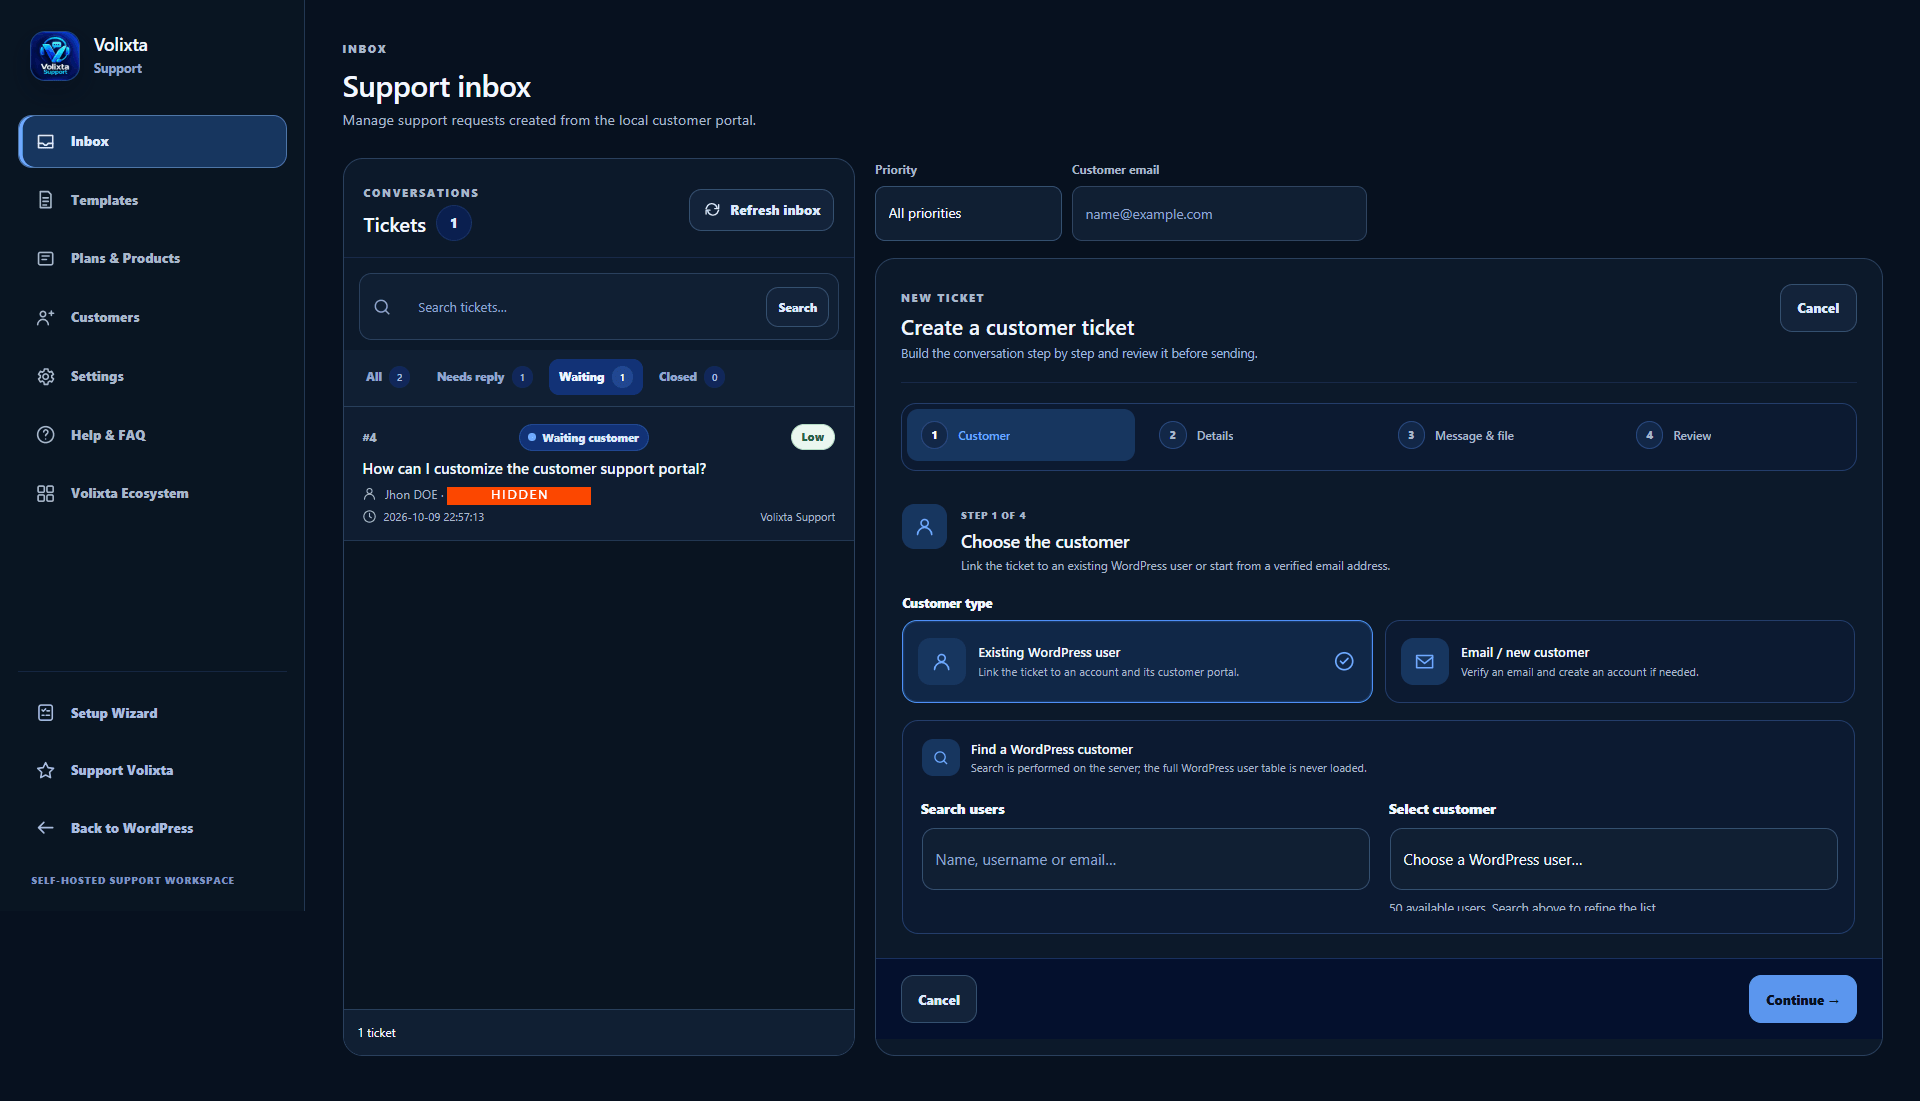
- Create tickets for WordPress users, manually saved contacts or email-only customers.
- Search and filter tickets by status, priority, customer email and keywords.
- Set Low, Medium or Urgent priority; review conversations and customer history.
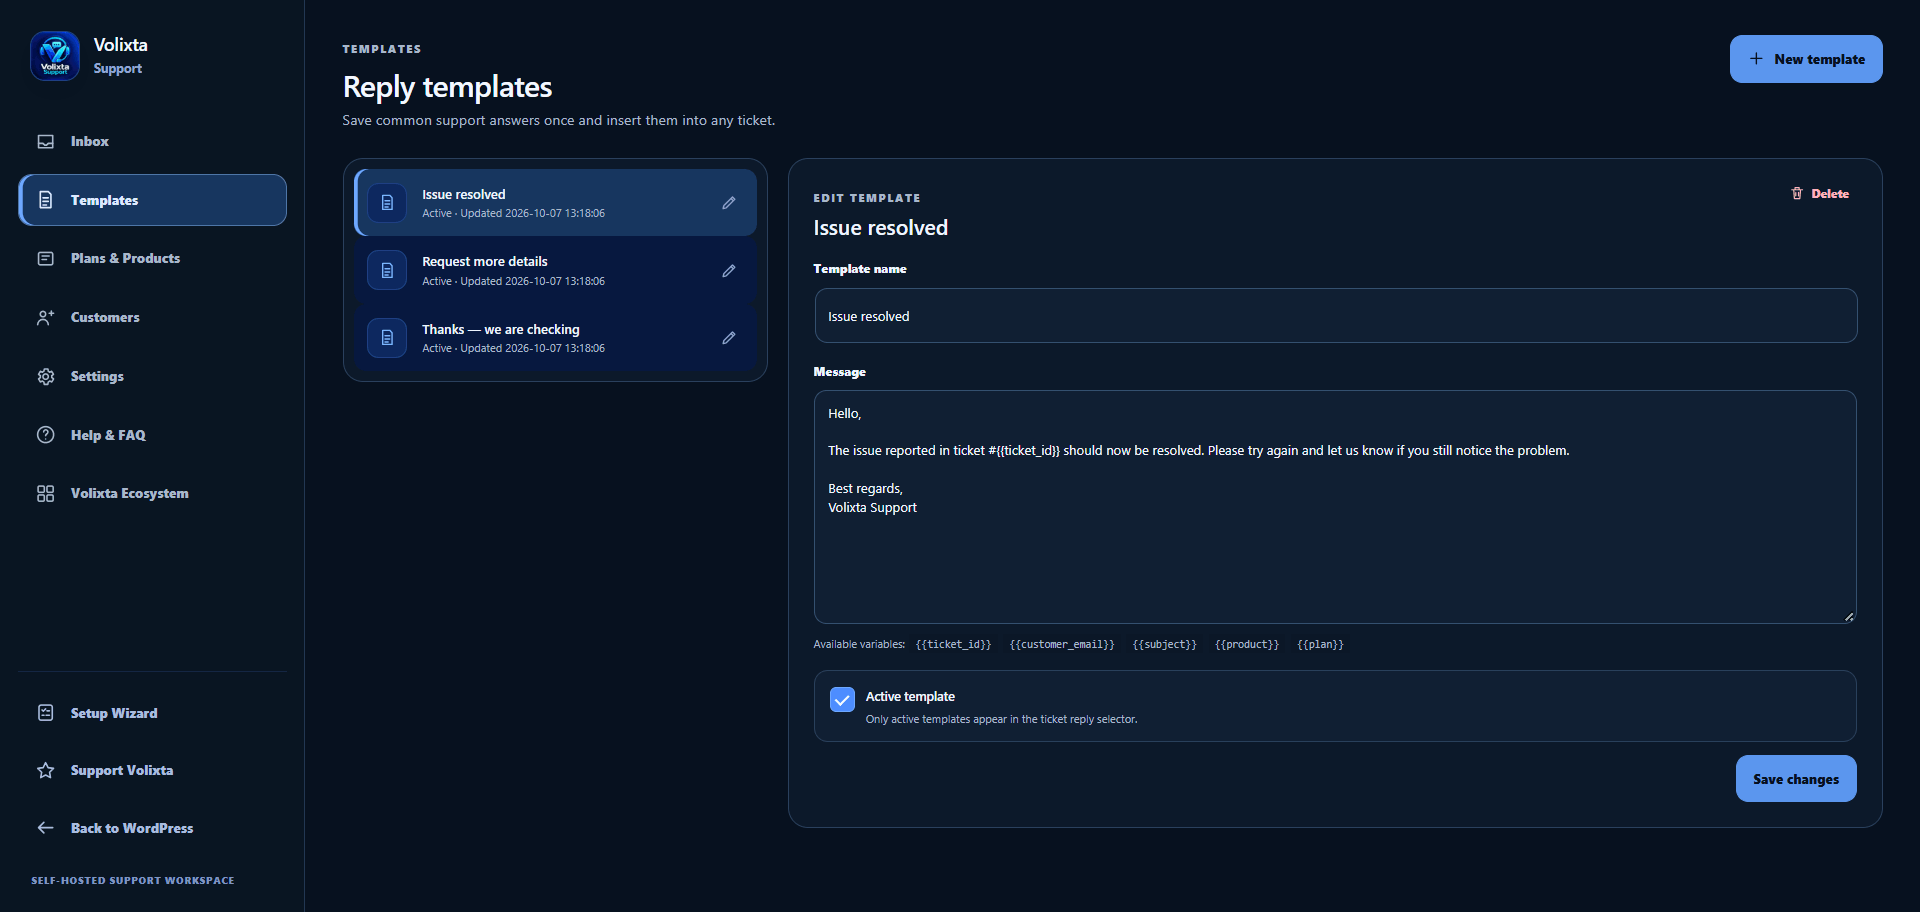
- Reply to customers, use reusable message templates, edit your own administrator replies and close tickets.
- Associate tickets with support products and manage supported file attachments.
- Work from a responsive interface on desktop, tablet and mobile.
[volixta_support_portal]
Signed-in customers can create tickets, read conversations, reply, review their ticket history and check assigned plans, ticket allowances, expiration dates and renewals. Eligible plans can be purchased through WooCommerce when enabled. The portal verifies ticket ownership using WordPress authentication.
Optional account registration sends a secure password-setting email and requires acceptance of the published privacy policy. Customers can claim eligible earlier guest tickets after verifying their email and latest guest ticket number.
Guest tickets and spam protection
Enable guest tickets separately and place this shortcode on a published page:
[volixta_support_guest_ticket]
Visitors can submit tickets for active support products with no support-plan association. They receive an expiring private email link that provides access only to the individual ticket and its replies, not to an account or full ticket history. Email addresses already associated with WordPress accounts must use the sign-in flow.
Configure up to three optional consent checkboxes, a honeypot, minimum submission time, rate limits and optional Cloudflare Turnstile. Consent responses are available to authorized administrators.
External service disclosure: When enabled, Turnstile loads https://challenges.cloudflare.com/turnstile/v0/api.js and sends challenge tokens to https://challenges.cloudflare.com/turnstile/v0/siteverify. Cloudflare may process IP addresses, browser/device information and challenge data. A Cloudflare account and site/secret keys are required. See the Cloudflare Privacy Policy and Terms.
Support products, plans and quotas
- Create local support products independently of WooCommerce products.
- Allow unrestricted support for eligible products not associated with a plan.
- Create limited or unlimited ticket allowances, with optional expiration.
- Set daily, weekly, monthly, yearly or custom quota renewals, or disable automatic resets.
- Cover multiple products under one plan with a shared ticket allowance.
- Assign plans manually or automatically by WordPress user role.
- Track assignments, purchase records, eligibility and access status.
uploads/volixta_support_files. Apache/LiteSpeed access is blocked by an installed .htaccess rule; Nginx requires the additional access-denial rule shown in plugin settings. Do not serve these files directly.
Newer attachments use a stable encryption key. A migration tool handles older files encrypted using WordPress salts. Back up the stable key, migrate older files and verify downloads before changing salts. SMTP passwords must be re-entered after salt rotation; existing guest links may also become invalid. With private retention disabled, administrators may still send supported email attachments without permanently storing them.
Guided setup
An eight-step wizard covers Design, Email, Products, Plan, Customer, Portal, Files and Ready. Configure appearance, email delivery, support products, plans, customer access, optional guest tickets and registration, public-form protection, and private attachment permissions. Advanced settings remain available after setup.
Customer Satisfaction (CSAT)
Enable optional 1–5 star ratings and comments for closed tickets. Signed-in customers and guests with valid private links can submit one review per ticket. View feedback in a dedicated administrator popup, track satisfaction statistics and optionally send review invitations by email. Configure CSAT in the Setup Wizard or Settings > Portal & access.
安装:
- Install the plugin using Plugins > Add New > Upload Plugin, or upload the
volixta-supportfolder to/wp-content/plugins/. - Activate Volixta Support and follow the setup wizard. Choose the administrator and customer portal designs, configure email delivery and add your support products.
- Create an optional support plan, or leave eligible products unrestricted. Add customer assignments when needed.
- Review the private Support Center page, or place
[volixta_support_portal]on a suitable published page. Add the page to your site's menu. - To accept tickets without accounts, enable guest tickets in Settings > Portal & access. Create a guest page or select a published page and use
[volixta_support_guest_ticket]. - To enable account registration, publish and select your privacy policy in Settings > Privacy, then enable registration in the plugin's portal settings.
- Configure optional consent checkboxes, spam controls and Cloudflare Turnstile if you need them.
- In the wizard Files step or Settings > Portal & access > Private file storage, configure encrypted retention, separate upload permissions for signed-in customers and guests, and the permitted extensions.
- Add or review support plans in Plans & Products. Configure manual or role-based assignment, and WooCommerce linking if you sell plans.
- Test email delivery, ticket creation and replies, and authorized uploads and downloads. Confirm that the private portal and guest page display correctly in your chosen palette.
wp-config.php (including security salts), private encrypted attachments and any configured stable file key. Update the existing plugin in place; do not uninstall first. After upgrading, review the new upload permissions and allowed formats. Migrate older attachments when needed and verify their downloads before changing WordPress salts.屏幕截图:




常见问题:
Can visitors submit a ticket without creating an account?
Yes. Enable guest tickets and publish a page containing [volixta_support_guest_ticket]. Visitors receive a private, expiring link for their individual conversation. They cannot browse other tickets. Addresses already registered on the site are directed to sign in.
Why are no products displayed in the guest ticket form?
The guest form only lists active products that have never been linked to a support plan. Check the product's status and plan associations. A product attached to an inactive plan is still restricted.
Can visitors create an account and recover their earlier tickets?
Yes, if registration is enabled and the site has a published privacy policy. New accounts are created as Subscribers and receive an email to set their password. Customers can claim eligible earlier guest tickets after verifying their email address and providing their latest guest ticket number.
Can I customize the consent checkboxes?
You can configure up to three checkboxes independently, including their text, optional linked text and URL, and whether each response is required. The recorded answers are visible to authorized administrators.
What protects public forms against automated submissions?
Optional protections include a honeypot, minimum form-completion time, request rate limits and Cloudflare Turnstile. Turnstile must be configured with your own Cloudflare keys and requires the external service described above. Reliable email delivery is important for guest access links and registration emails.
Do customers need a WordPress account to be added to Customers?
No. You can maintain manual contacts and use them when creating tickets without registering them as site users. Linking an existing account or creating a new Subscriber account is optional. Removing a manual contact does not delete its tickets or a linked account.
Where can I view a customer's earlier tickets?
Open a ticket in Inbox and choose History in the ticket header to view other requests, including closed conversations. Choose Files to review the ticket’s saved incoming and outgoing attachments. Signed-in customers also have their own ticket history in the private Support Center. Guests can open only the specific tickets for which they have valid private links.
Do I need WooCommerce to use Volixta Support?
No. The inbox, private portal, guest tickets, local products, support plans, quotas and notifications work without WooCommerce. The integration is optional and is used to sell support-plan access through qualifying orders.
Can I provide unrestricted support or unlimited plans?
Yes. Products without a plan association can accept unrestricted requests, and support plans can have unlimited ticket allowances. You can also limit tickets and set renewal or expiration rules. Products already linked to a plan remain protected when the plan is inactive.
Can a support plan cover more than one product?
Yes. A plan may cover multiple local support products. If the plan has a limited quota, tickets for those products count against its shared allowance.
Can I assign plans without selling them?
Yes. Assign plans to individual WordPress users or use role-based assignment rules. WooCommerce is only necessary if you want qualifying orders to grant or extend entitlements.
What happens when a WooCommerce order is cancelled or refunded?
Volixta Support revokes the entitlement contributed by the affected order without removing unrelated purchases or assignments. Existing WooCommerce orders are not deleted by the plugin.
Can I customize the helpdesk and portal separately?
Yes. Standard, Immersive and Focus can be chosen separately for the administrator workspace and customer portal. The selected portal palette also styles registration and guest ticket forms.
Can I use my hosting email account to send notifications?
Yes. Configure SMTP host, port, encryption, authentication and sender details in the plugin settings, then send a test email. By default, the transport applies only to Volixta Support messages. Site-wide SMTP routing is optional.
Can I attach files without permanently storing them?
Yes. When private retention is disabled, administrators may still include supported files in outgoing ticket emails. When retention is enabled, files are encrypted and available through authorized downloads.
How are private attachments protected?
Stored attachments use AES-256-GCM encryption and access-controlled downloads. The plugin blocks direct HTTP access with a .htaccess rule on Apache/LiteSpeed. On Nginx, administrators must add the server rule shown in settings.
What is the safest way to update Volixta Support?
Back up your WordPress database, private encrypted attachment directory, and wp-config.php (including the original security salts). Keep an exact, secure backup of VOLIXTA_SUPPORT_FILES_KEY if configured. Try the update on staging first, then update or replace the existing plugin in place using the WordPress update flow. Never uninstall the old version to perform an upgrade; uninstall is destructive.
Do I need to run the Setup Wizard again after updating?
No. An in-place update retains the existing setup. Review Settings > Portal & access, file storage, the permitted extensions and customer/guest upload permissions. Then test the ticket list, support plans, customer portal, replies, email delivery, uploads and protected downloads.
How should I check older attachments and encryption keys after upgrading?
Keep the original WordPress security salts until any older salt-derived attachments have been migrated in Settings > Portal & access > Private file storage. Run the migration in batches of up to 15 records, resolve failures and verify representative older downloads. A batch ceiling of 15 does not mean 15 files are stored. Never lose or unexpectedly replace the stable encryption key: it may be in the database or explicitly provided through the 64-character hexadecimal VOLIXTA_SUPPORT_FILES_KEY constant in wp-config.php. Rotating WordPress salts can also affect encrypted SMTP credentials and previously issued guest links.
How can I safely roll back a failed update?
Avoid uninstalling. Restore the plugin code together with a matching database, private attachments and the correct keys from one known-good backup. Restoring only a previous ZIP may leave database changes behind. Test the restore on staging before applying it to production.
Can I update directly from version 1.0.1?
Yes. Version 1.2.0 retains the upgrade path introduced in 1.1.0 and is designed to upgrade the existing installation while retaining its original nine support tables, tickets, products, plans and settings, and adding a table for manual contacts. Do not uninstall the older version first. Back up your data and run the old-attachment migration after updating. Test the upgrade on a staging site before production.
Why should I preserve WordPress salts when updating?
Older encrypted attachments may rely on keys derived from the salts in wp-config.php. Keep those values unchanged until you have migrated older files in Settings > Portal & access > Private file storage, using Scan / migrate up to 15 attachments as needed (each batch examines up to 15 attachment records), and verified that downloads succeed. New retained files use a separate stable encryption key that must also be preserved.
What happens to my data if I deactivate or uninstall the plugin?
Deactivation keeps the data. A successful uninstall permanently removes the plugin's dedicated tables, tickets, messages, support plans, settings and stored private attachments. It does not delete WordPress accounts or WooCommerce orders. Manually selected or customized pages remain; plugin-created default pages are removed only when they can be safely identified. If private-file cleanup fails, the plugin preserves database records and encryption keys to avoid irreversible loss; some already-removed files may still be missing. Back up important data first.
更新日志:
- Improved responsive ticket action buttons with a balanced three-column layout when Volixta Task Manager Lite is not installed, while preserving a compact layout when the integration is available.
- Improved the support ticket interface with a cleaner, more organized header and better alignment of ticket information and actions.
- Enhanced responsive layouts across desktop, tablet, and mobile screens, making better use of available space.
- Optimized the positioning of ticket status, priority, customer details, and action buttons for improved readability and usability.
- Improved compatibility with Volixta Task Manager Lite integration, ensuring linked-task actions fit naturally alongside Files, History, and Feedback controls.
- Updated the plugin name to "Volixta Support – Helpdesk, Customer Support Ticket System & Customer Portal" for improved clarity.
- Added optional Customer Satisfaction (CSAT) ratings and comments for closed support tickets.
- Added a dedicated Feedback popup alongside Files and History in the administrator ticket workspace.
- Added customer feedback settings, satisfaction statistics and optional email invitations.
- Integrated feedback controls into the Setup Wizard and existing email notification system.
- Improved rating forms with five golden stars and responsive styling across all design palettes.
- Updated the plugin name to "Volixta Support – Helpdesk, Tickets & Customer Portal" for improved clarity.
- Optimized the WordPress.org readme with a more concise description, relevant keywords and improved documentation structure.
- Added: Volixta Task Manager Lite to the Volixta Ecosystem page, with automatic plugin status detection, installation, activation and dashboard navigation.
- Improved: Unified the admin interface layout across Standard, Immersive and Focus themes.
- Improved: Standard theme now uses the same sidebar navigation and workspace structure with a light color palette.
- Improved: Responsive navigation across different screen sizes.
- Fixed: Inconsistent layout between admin appearance modes.
- Fixed: Corrected the plugin version tag.
- Added: Optional integration with Volixta Task Manager Lite to convert customer support tickets into linked project tasks.
- Added: Ability to create tasks directly from support tickets, automatically carrying over ticket subjects and priorities.
- Improved: Navigation between support tickets and their related tasks, with detection of existing linked tasks to prevent duplicates.
- Updated: Plugin documentation with Volixta Task Manager Lite integration details and installation link.
- Added secure encrypted file attachments for customer and guest ticket creation and replies, as well as administrator ticket replies.
- Added separate upload permissions for logged-in customers and guests, with configurable allowed file extensions and server-side MIME validation.
- Added dedicated Files popups in the administration and Customer Portal to view and download sent and received attachments, with file-type icons and responsive layouts.
- Added administrator-only attachment deletion with confirmation, nonce verification, capability checks and secure file removal.
- Moved ticket attachments and customer history into separate dialogs to keep conversations clean and organized.
- Added attachment management to customer profiles, including sent, received and older files.
- Improved attachment input styling, popup controls and Elementor compatibility across Standard, Immersive and Focus design palettes.
- Added a dedicated file storage and permissions step to the Setup Wizard, synchronized with Portal & access settings.
- Improved legacy attachment migration with clearer progress reporting, accurate file counts and automatic return to the relevant settings section.
- Strengthened file encryption, download permissions, ticket ownership validation, nonce verification and guest upload restrictions.
- Improved database schema verification, encrypted file handling and protection against unsafe storage paths.
- Strengthened uninstall safeguards to preserve encryption keys and database records when private file cleanup fails.
- Added an Updates & backups section to Help & FAQ, covering safe upgrades, data backups, encryption keys, migration and recovery.
- Improved WordPress coding standards compliance, including filesystem operations, database queries, translation comments and upgrade notices.
- Updated the plugin version, readme stable tag, NOTICE and internal database revision to 1.2.0.
- Preserved compatibility with existing tickets, customers, support plans, settings and encrypted attachments.
- Upgrades must be performed in place without uninstalling the previous version. Back up the database, private attachments and encryption keys before updating.
- Added optional guest ticket submission with a separate public form, private expiring ticket links and guest replies.
- Introduced optional account registration with privacy-policy consent and secure email verification for claiming older guest tickets.
- Added configurable guest consent checkboxes, Turnstile integration, honeypot protection, completion-time checks and request rate limits.
- Added three Customers views and a manual contact directory, with optional Subscriber account creation and account linking.
- Expanded administrator ticket creation to use existing site accounts, saved contacts or email-only customers.
- Added paginated Customer History in Inbox, including closed tickets, and guest consent answers in ticket details.
- Expanded the setup wizard to seven steps with portal, registration and guest page creation or selection.
- Added stable encryption for newly retained attachments and a tool to migrate files encrypted by older versions.
- Improved registration, guest forms, responsive layouts and Standard, Immersive and Focus styling.
- Strengthened permissions, private link handling, file downloads, migration and uninstall safeguards.
- Refined interface prefixes, translations, SQL handling and WordPress plugin compatibility checks.
- Preserved existing tickets, plans and database structures during upgrades from 1.0.1; added a dedicated table for manual contacts.
- Redesigned ticket notification emails using responsive HTML layouts.
- Matched email colors to the selected Standard, Immersive or Focus palette.
- Added support for the WordPress site logo or favicon in notifications.
- Refined email branding and templates for new tickets, confirmations, support replies, customer replies and SMTP tests.
- Improved the ticket creation review step, field alignment and full-width summaries.
- Minor interface improvements and fixes.
- Initial public release.