高级自定义字段(ACF)
| 开发者 |
elliotcondon
bradt deliciousbrains wpengine mattshaw lgladdy antpb mindctrl modernnerd rfmeier andrewbotz dalewilliams polevaultweb johnstonphilip wordpressdotorg |
|---|---|
| 更新时间 | 2026年11月20日 03:57 |
| PHP版本: | 7.4 及以上 |
| WordPress版本: | 7.1.5 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
标签
下载
6.6.2
3.1.8
3.1.9
3.2.0
3.2.2
3.2.3
3.2.5
3.2.7
3.2.8
3.3.1
3.3.2
3.3.3
3.3.5
3.3.6
3.3.8
3.3.9
3.4.0
3.4.1
3.4.3
3.5.2
3.5.7
3.5.8
4.0.0
4.0.1
4.0.2
4.0.3
4.1.2
4.1.4
4.1.5
4.1.6
4.1.8
4.2.2
4.3.0
4.3.1
4.3.2
4.3.4
4.3.5
4.3.6
4.4.2
4.4.4
4.4.5
4.4.6
4.4.8
4.4.9
5.6.10
5.6.2
5.6.5
5.6.7
5.6.8
5.6.9
5.7.0
5.7.1
5.7.10
3.1.7
6.3.11
6.6.0
6.8.7
6.8.9
4.1.3
4.3.3
4.4.1
4.4.11
4.4.12
5.6.3
5.7.12
5.7.13
5.7.2
5.7.3
5.7.4
5.7.6
5.7.7
5.7.8
5.7.9
5.8.10
5.8.11
5.8.2
5.8.3
5.8.4
5.8.7
5.9.0
5.9.1
5.9.3
5.9.4
5.9.5
5.9.6
4.3.8
5.9.7
6.3.10.2
6.3.9
4.4.0
5.12.4
6.2.9
2.0.4
5.12.6
2.0.5
2.1.1
3.1.5
3.5.3
3.5.6
5.10.1
5.11
5.6.4
5.9.9
6.0.5
6.3.0
5.9.2
1.1.1
6.8.1
6.8.2
5.10.2
5.11.4
5.12.3
5.6.6
6.0.1
6.0.2
6.0.6
1.1.4
2.0.3
5.8.1
5.8.5
6.0.4
6.0.7
6.1.2
6.1.6
6.2.0
5.12.5
5.8.12
5.8.13
6.1.0
6.2.1
6.2.2
6.2.4
6.2.6
3.0.1
3.4.2
5.8.6
6.1.1
6.1.8
6.2.7
2.0.0
4.4.3
5.9.8
6.1.3
6.2.8
5.10
6.0.3
3.3.7
4.2.1
4.3.7
4.3.9
5.12.1
6.3.3
6.3.1
6.3.4
3.0.3
3.1.0
3.1.6
5.12
6.1.5
6.3.2
6.3.6.2
6.3.6.3
3.1.3
5.12.2
5.8.14
5.8.8
6.3.5
6.4.0.1
6.4.1
6.4.2
6.4.3
3.0.7
3.2.9
1.1.0
2.1.4
3.0.2
3.0.4
3.1.4
3.5.1
6.1.4
6.2.5
6.3.6
6.5.0
6.5.1
1.0.2
1.0.3
3.3.0
5.8.9
6.8.8
4.1.0
6.2.3
6.3.6.1
6.6.1
6.7.0
6.7.1
3.2.4
3.2.6
3.3.4
6.1.7
6.7.2
1.0.0
2.0.2
3.0.6
3.1.1
3.1.2
3.5.4
4.4.7
5.11.1
5.11.2
6.4.0
6.8.0
2.1.3
3.5.0
3.5.5
5.7.5
6.3.12
6.8.3
6.8.4
6.8.5
1.1.2
2.0.1
6.8.6
1.0.5
1.1.3
3.0.0
4.1.1
4.2.0
4.4.10
5.11.3
5.8.0
6.0.0
6.2.6.1
6.8.10
6.8.11
6.8.12
详情介绍:
高级自定义字段(ACF®)通过为您提供所有使用数据的工具来将 WordPress 站点转变为一个成熟的内容管理系统。
使用 ACF 插件完全控制您的 WordPress 编辑屏幕、自定义字段数据等。
https://www.youtube.com/watch?v=9C6_roqghZQ&rel=0
Add fields on demand.
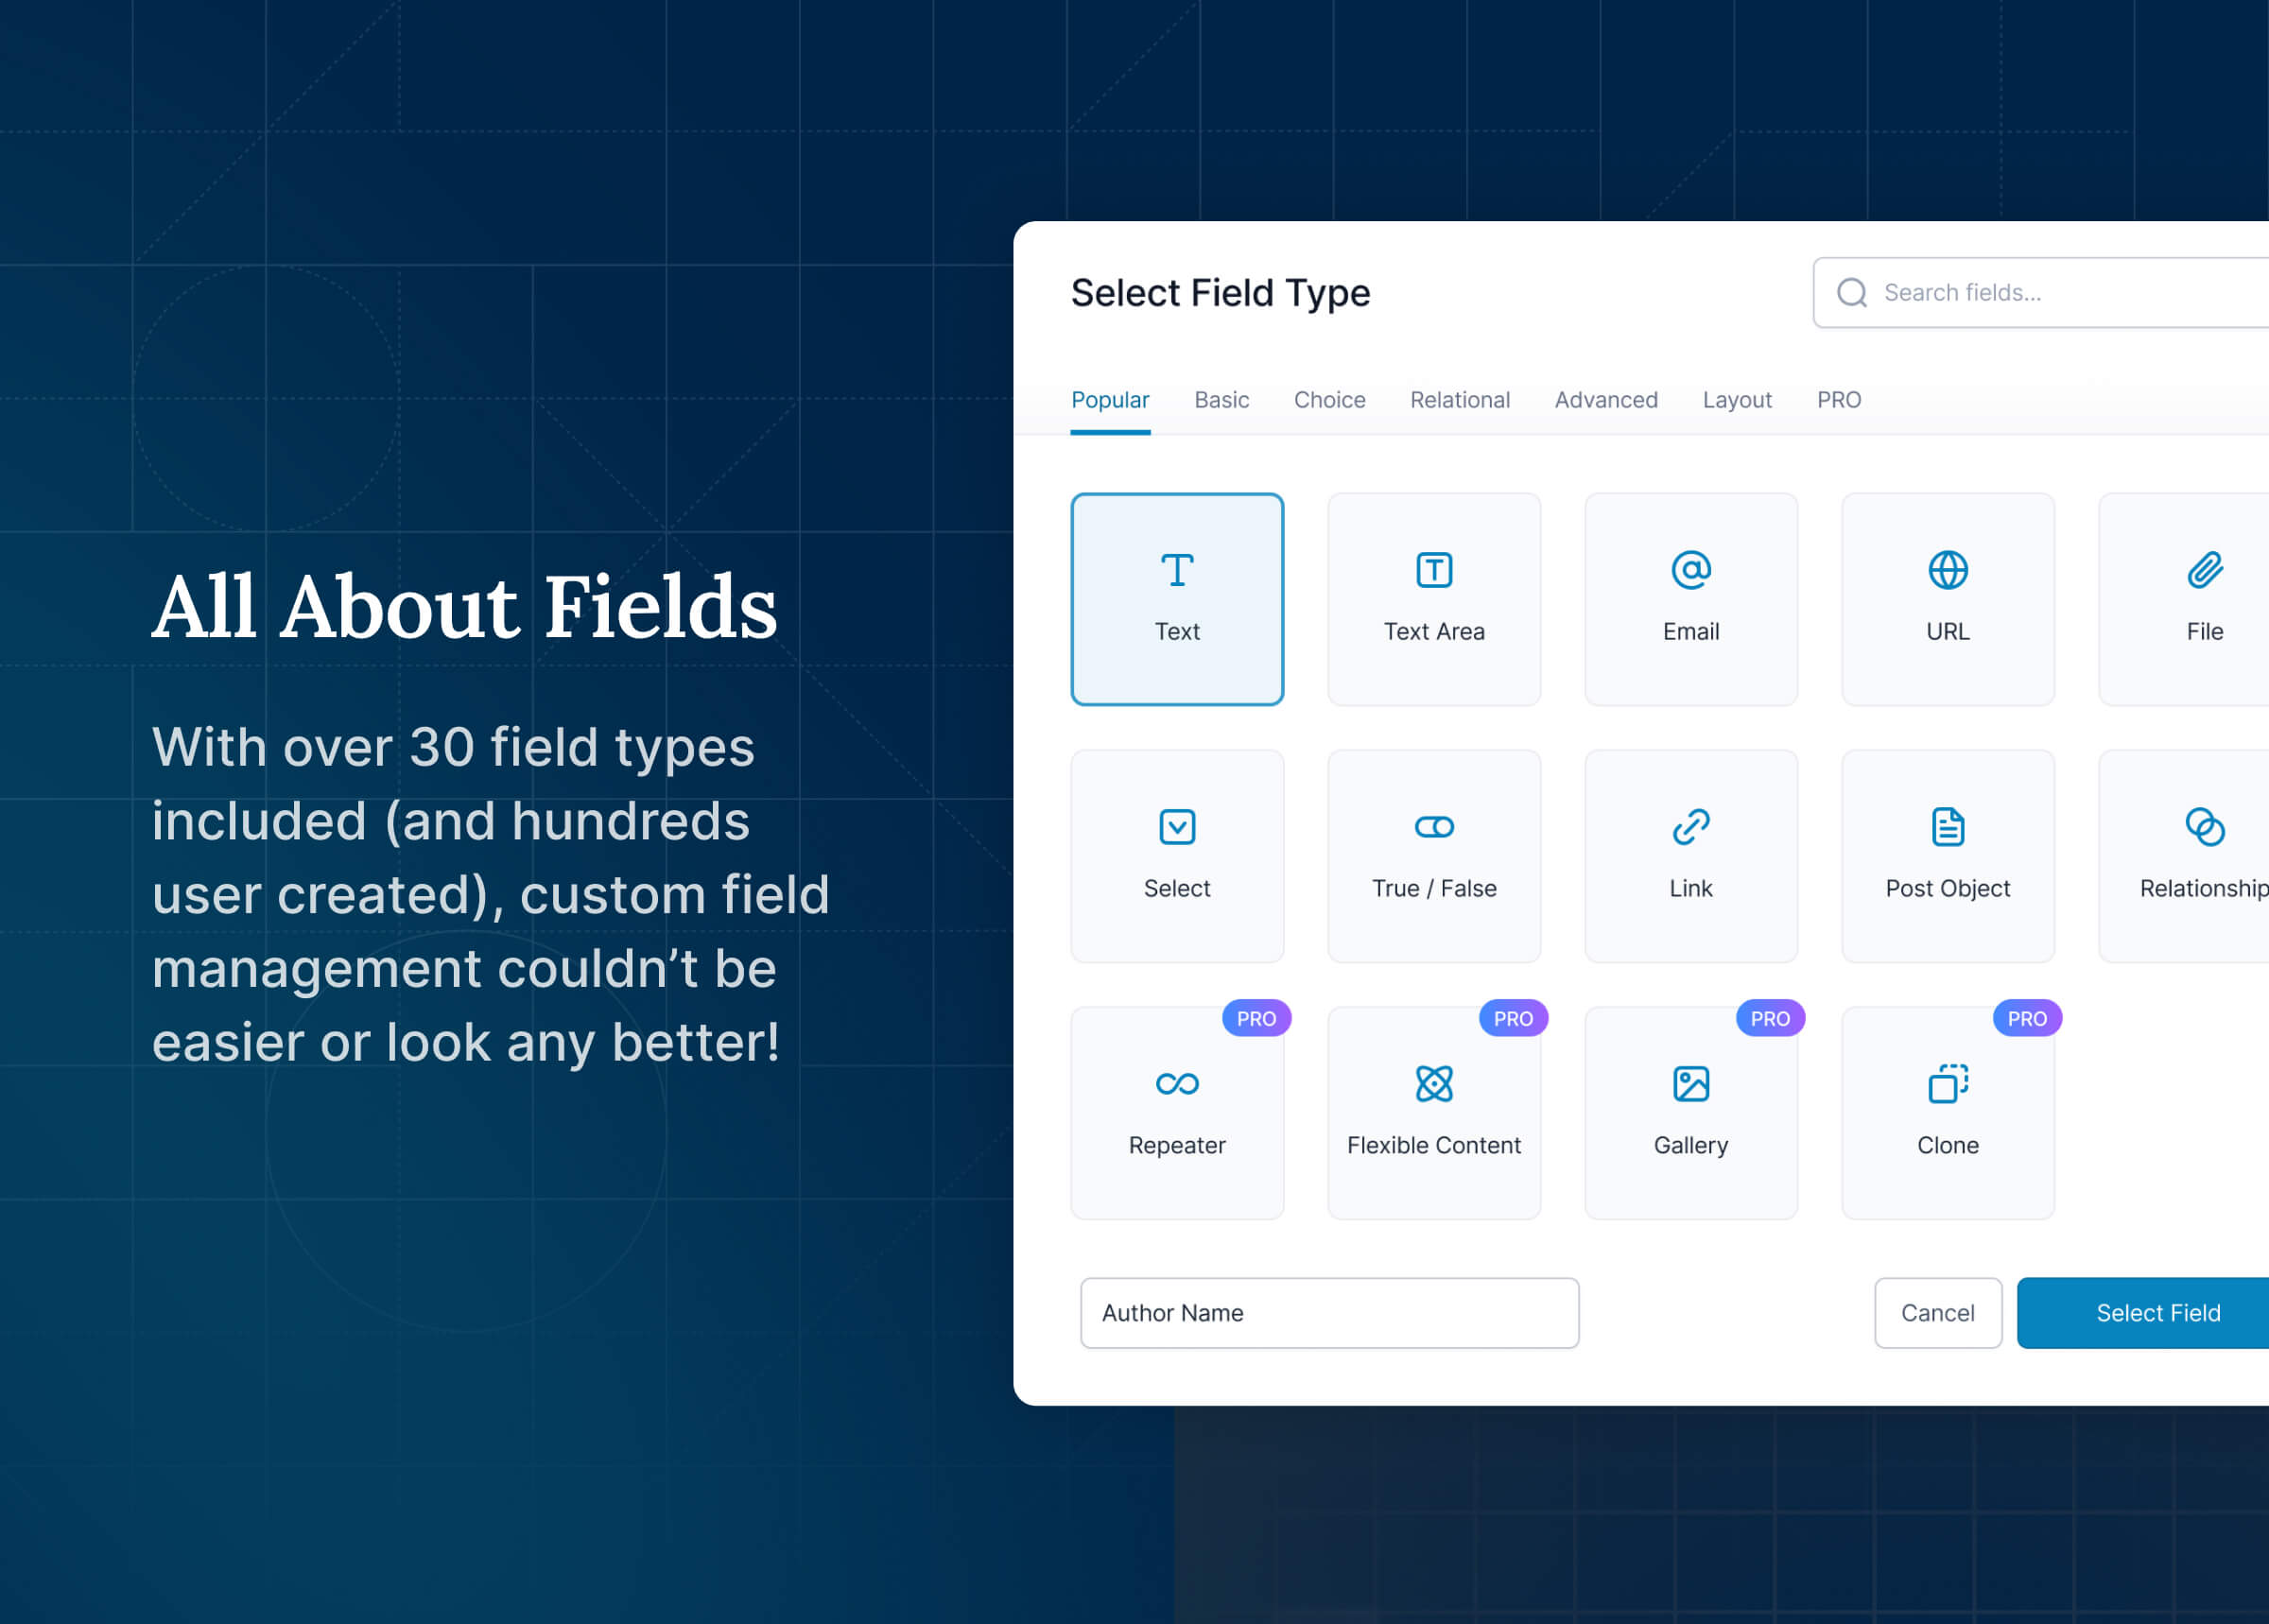
The ACF field builder allows you to quickly and easily add fields to WP edit screens with only the click of a few buttons! Whether it's something simple like adding an “author” field to a book review post, or something more complex like the structured data needs of an ecommerce site or marketplace, ACF makes adding fields to your content model easy.
Add them anywhere.
Fields can be added all over WordPress including posts, pages, users, taxonomy terms, media, comments and even custom options pages! It couldn't be simpler to bring structure to the WordPress content creation experience.
Show them everywhere.
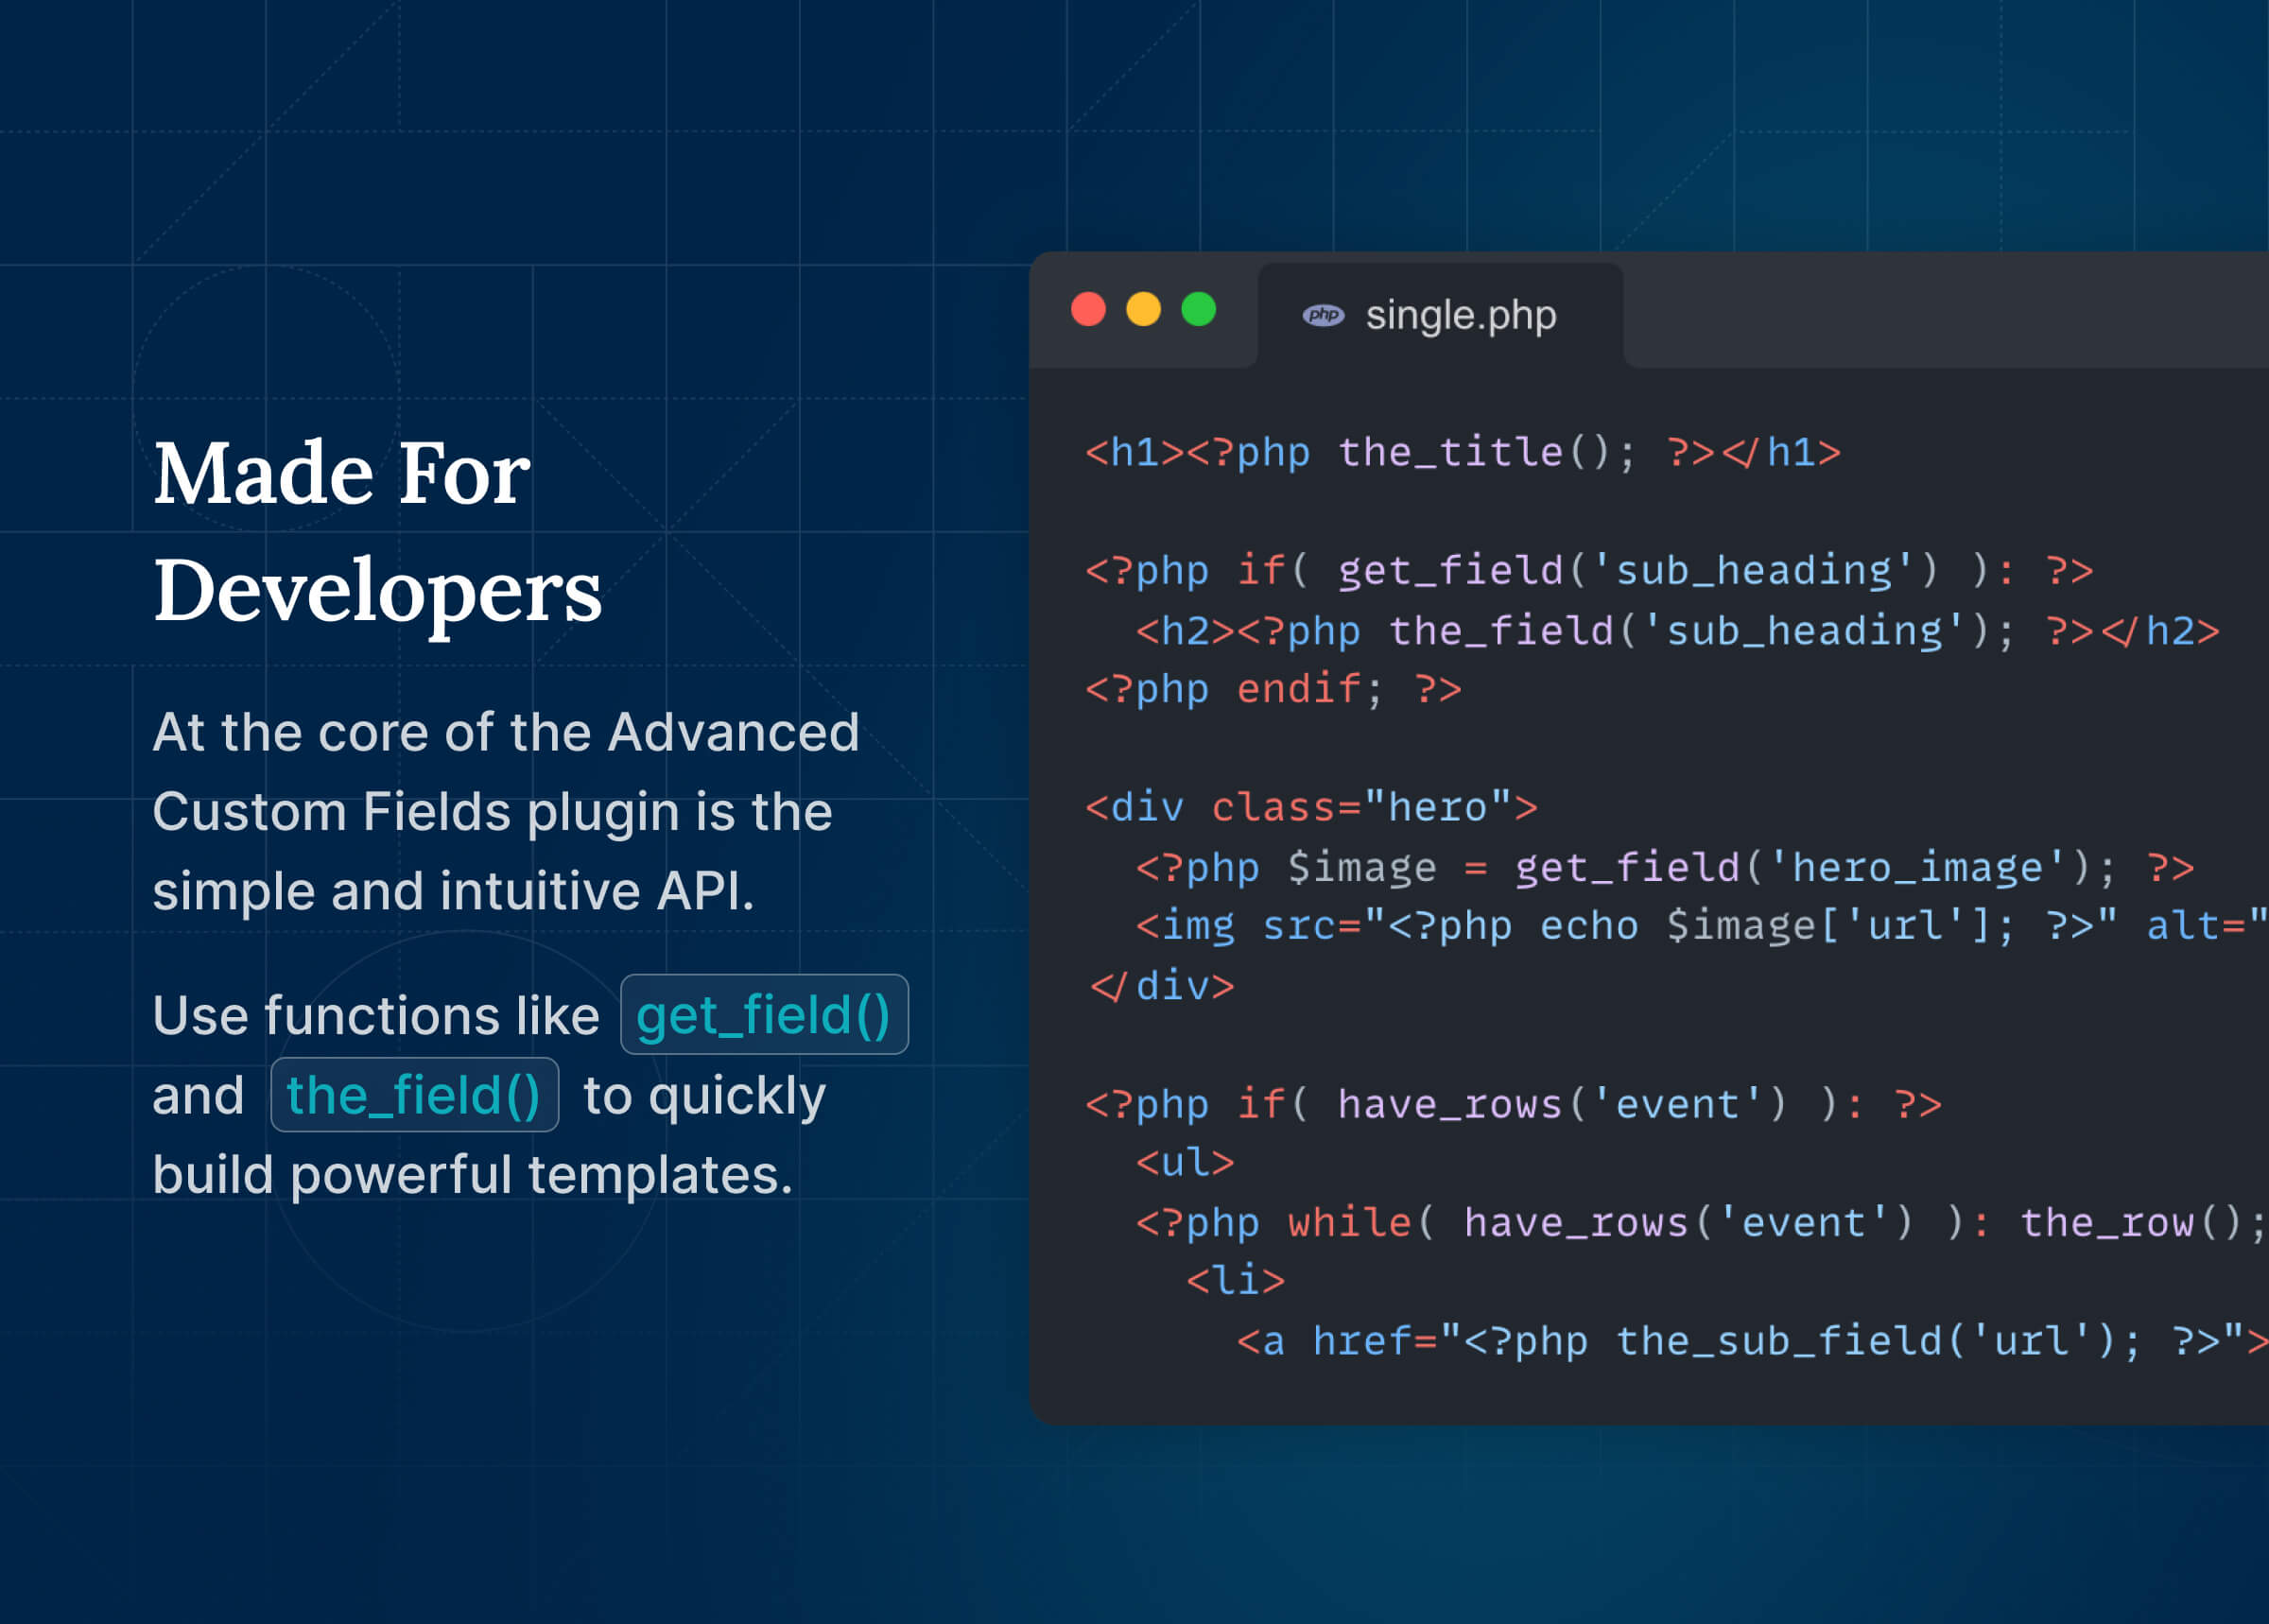
Load and display your custom field values in any theme template file with our hassle-free, developer friendly functions! Whether you need to display a single value or generate content based on a more complex query, the out-of-the-box functions of ACF make templating a dream for developers of all levels of experience.
Any Content, Fast.
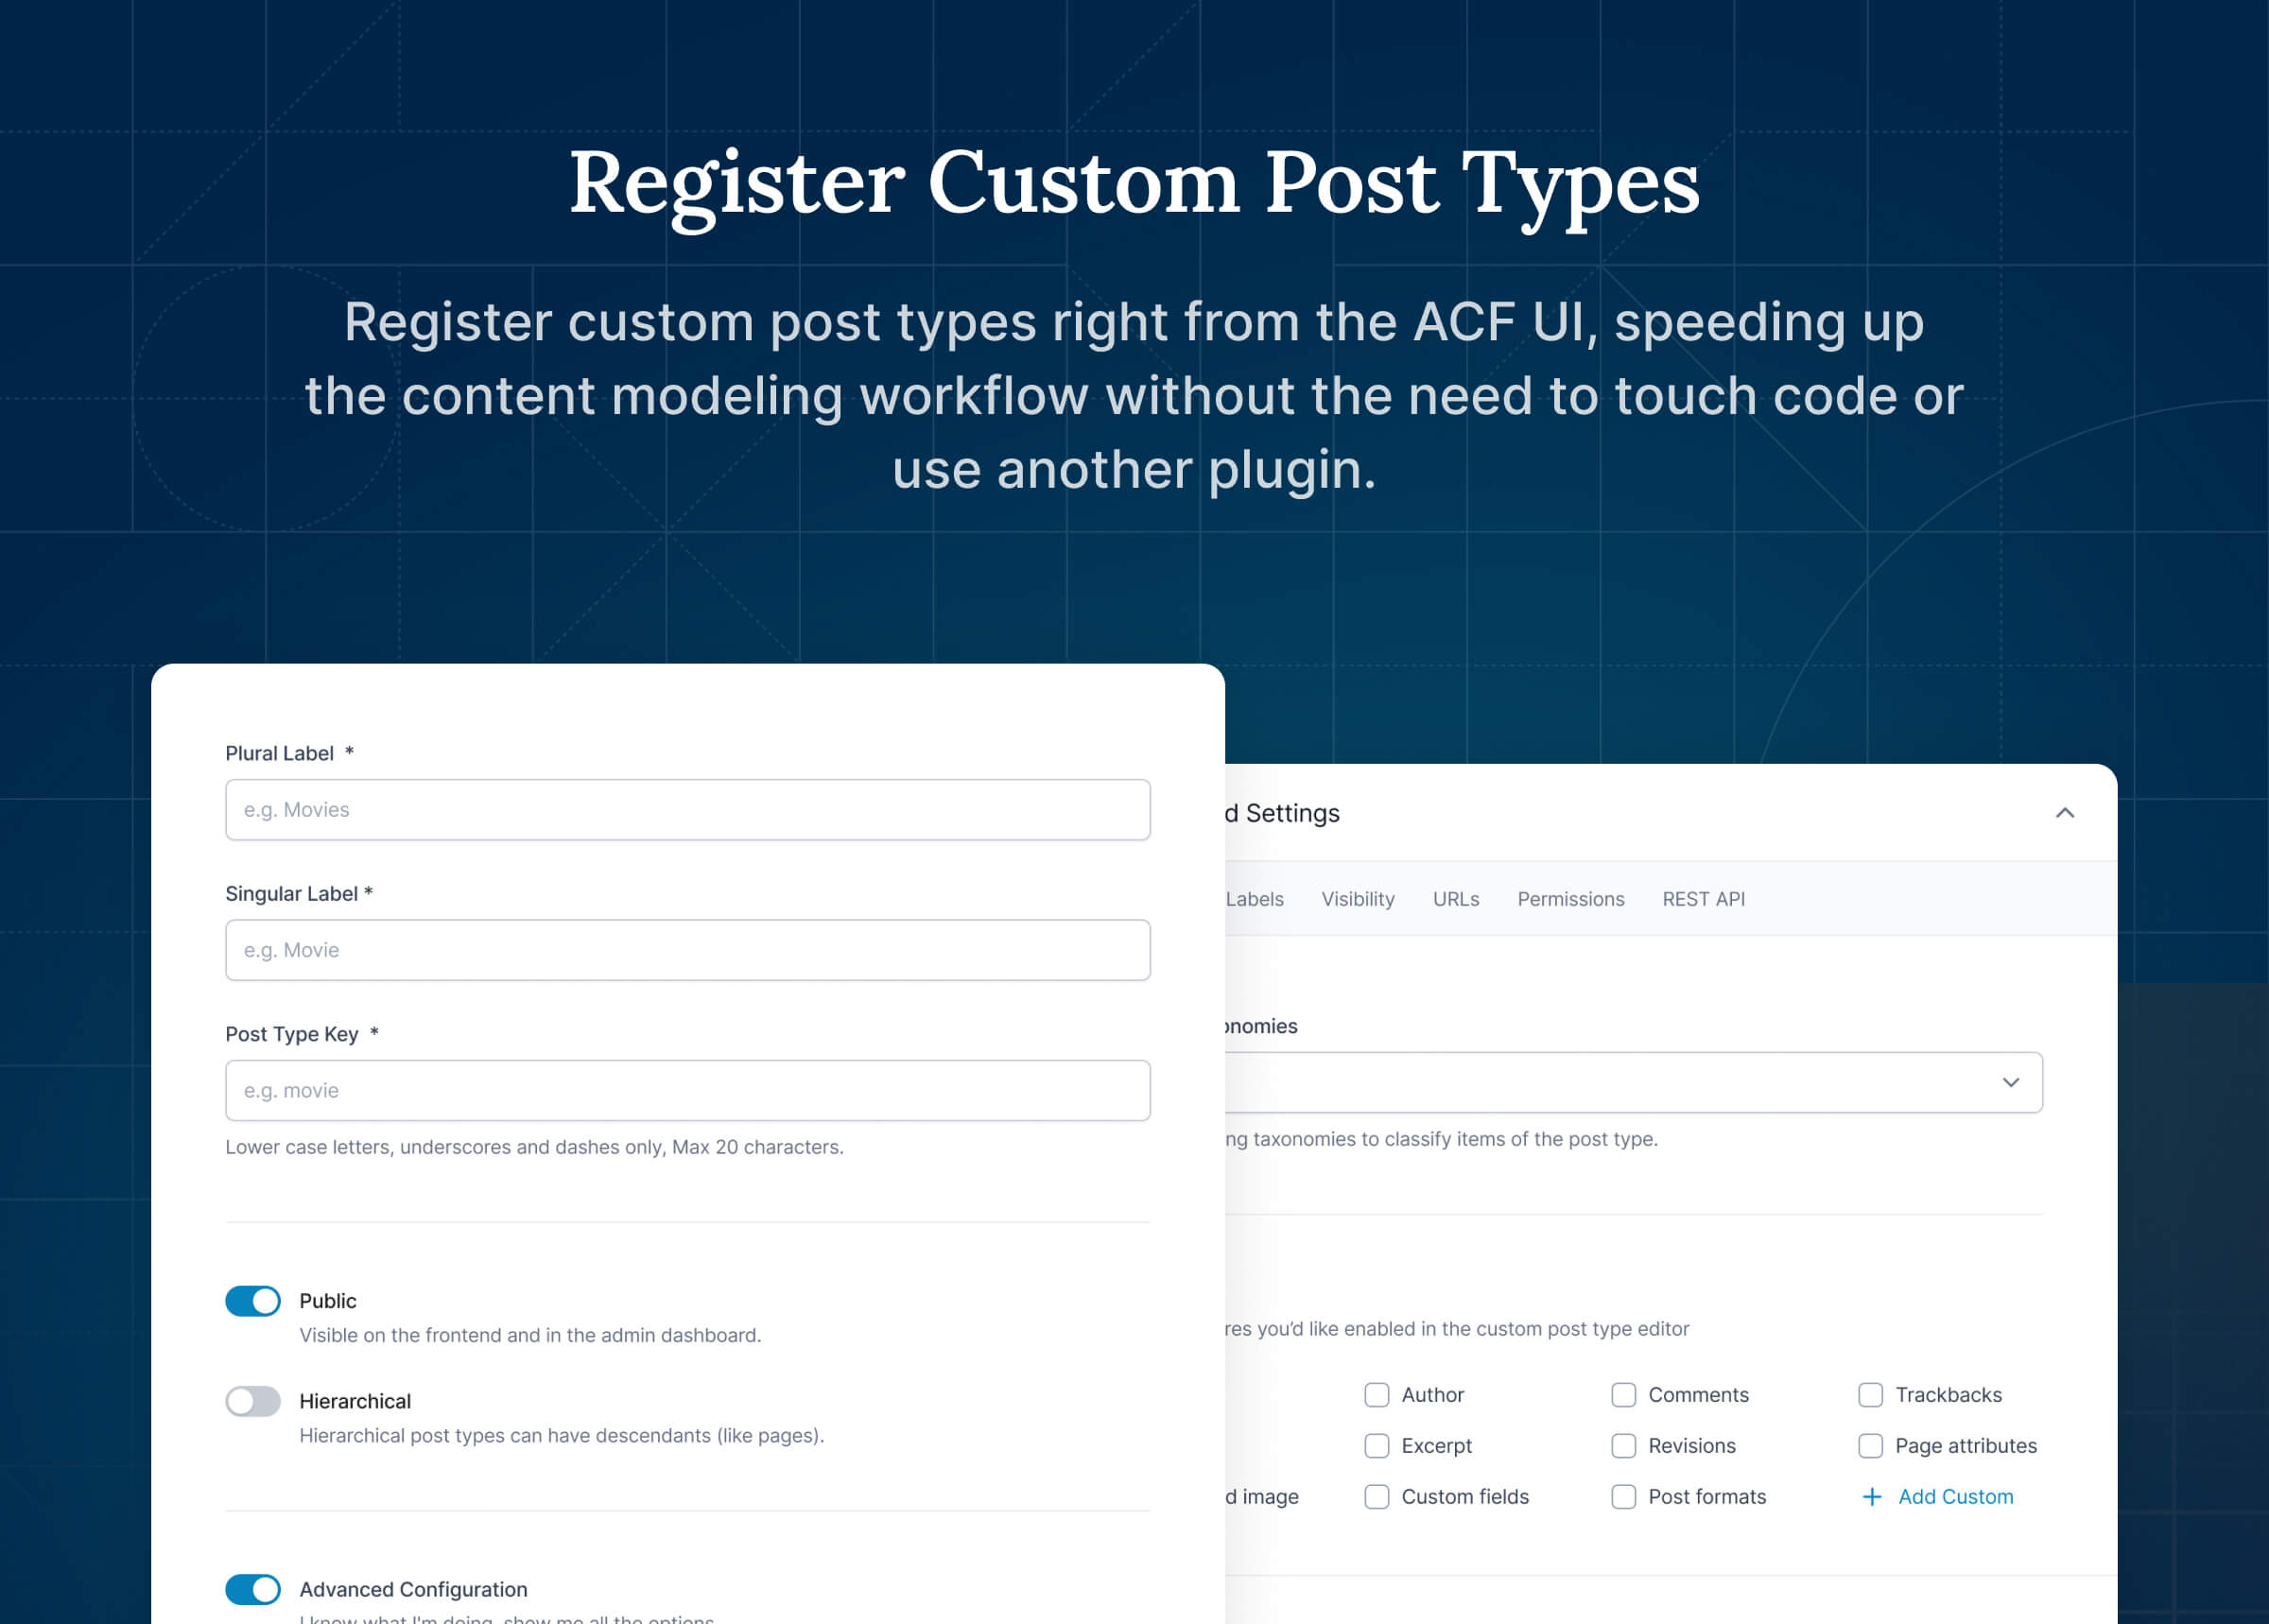
Turning WordPress into a true content management system is not just about custom fields. Creating new custom post types and taxonomies is an essential part of building custom WordPress sites. Registering post types and taxonomies is now possible right in the ACF UI, speeding up the content modeling workflow without the need to touch code or use another plugin.
Simply beautiful and intentionally accessible.
For content creators and those tasked with data entry, the field user experience is as intuitive as they could desire while fitting neatly into the native WordPress experience. Accessibility standards are regularly reviewed and applied, ensuring ACF is able to empower as close to anyone as possible.
Documentation and developer guides.
Over 10 plus years of vibrant community contribution alongside an ongoing commitment to clear documentation means that you'll be able to find the guidance you need to build what you want.
功能
- Simple & Intuitive
- 功能强大
- 30 多种字段类型
- 完整的在线说明文档
- 数百万用户
- The Repeater Field allows you to create a set of sub fields which can be repeated again, and again, and again.
- ACF Blocks, a powerful PHP-based framework for developing custom block types for the WordPress Block Editor (aka Gutenberg).
- Define, create, and manage content with the Flexible Content Field, which provides for multiple layout and sub field options.
- Use the Options Page feature to add custom admin pages to edit ACF fields.
- Build fully customisable image galleries with the Gallery Field.
- Unlock a more efficient workflow for managing field settings by reusing existing fields and field groups on demand with the Clone Field.
安装:
从 WordPress 网站管理后台进行安装
- Visit Plugins > Add New
- Search for "Advanced Custom Fields" or “ACF”
- Install and Activate Advanced Custom Fields from your Plugins page
- Click on the new menu item "ACF" and create your first custom field group, or register a custom post type or taxonomy.
- Read the documentation to get started
屏幕截图:
常见问题:
插件开发者能为用户提供的技术支持有哪些?
Support Forums. Our ACF Community Forums provide a great resource for searching and finding previously answered and asked support questions. You may create a new thread on these forums, however, it is not guaranteed that you will receive an answer from our support team. This is more of an area for ACF developers to talk to one another, post ideas, plugins and provide basic help. View the Support Forum
Looking for non-minified files?
Our plugin's non-minified JS and CSS files are available on GitHub.
Does ACF collect any data?
ACF includes an optional email signup to receive plugin updates and news. No data is collected unless you choose to subscribe. Your email is stored in accordance with WP Engine's Privacy Policy.
更新日志:
6.8.12
Release Date 19th November 2026
- Security -
scripttags in ACF Block preview HTML, including ones that load an external file, no longer run in the block editor unless the block opts in withallowDangerousPreviewScriptsinblock.json(orallow_dangerous_preview_scriptsinacf_register_block_type()), or the site opts in with the newacf/blocks/allow_dangerous_preview_scriptsfilter - Security - The
[acf]shortcode no longer shows fields from draft or private posts referenced by a prefixed ID such aspost_123when used inside an ACF Block, or outside the loop such as in a widget on a 404 or search page - Security - Icon Picker fields set to return an icon string no longer reveal the URLs of private Media Library images in the REST API
- New - ACF now has a new Settings page with a Features tab for turning ACF features on and off without code. In ACF PRO, the License and Updates screens are now tabs on this page. Settings defined in code are shown as "Managed via code" and can't be changed in the UI
- New - Developers can add their own tabs, sections and fields to the Settings page with the new
acf/settings_page/tabs,acf/settings_page/general/sectionsandacf/settings_page/general/{$section}/fieldsfilters. The Features tab can be hidden with the newacf/settings/show_settingsfilter - New - ACF Abilities are now enabled by default for all field groups, post types and taxonomies on WordPress 6.9 and later. They can be turned off for each object, or for the whole site from the Settings page. The
enable_acf_aisetting has been renamed toenable_abilities, and existingallow_ai_accessvalues are not carried over - Enhancement - The "Edit Block" button text on ACF Blocks V3 that turn off the preview with "renderPreview": false can now be changed with acf.placeholderButtonText in block.json or the new
acf/blocks/default_placeholder_button_textfilter - New - ACF Blocks registered with
acf_register_block_type()can now set the InnerBlocksdefault_blockanddirect_insertoptions - Enhancement - ACF Abilities now publish valid JSON Schema, so MCP clients such as ChatGPT can discover and use them. Schemas now describe conditional logic, Repeater and Group sub fields, and Flexible Content layouts
- Enhancement - Breaking change: generated post type and taxonomy ability names now include the object type, so they no longer collide. For example,
acf/create-bookis nowacf/create-book-postandacf/booksis nowacf/list-book-posts. Agent prompts and MCP configurations that use the old names need updating - Enhancement - The
acf/field-groupsAbility now includes the list of fields within each field group - Enhancement - The Date Picker field's bundled jQuery UI stylesheet has been updated to version 1.14.2
- Enhancement - New
acf/blocks/auto_inline_editing/field_return_type_supports_auto_inline_editingfilter allows customizing which fields support auto inline editing in ACF Blocks - Enhancement - Child options pages now appear in their parent's menu in Menu Position order, whether they were registered in the UI or in PHP. A parent page that redirects to its first child now opens the child with the lowest Menu Position
- Enhancement - Google Map fields now find the city for more addresses, such as those that only have a neighborhood or sublocality
- Fix - ACF Blocks no longer crash in the block editor when WordPress or Gutenberg loads React 19
- Fix - ACF Blocks V3 now save default field values when a block is inserted and left unedited
- Fix - Auto inline editing in ACF Blocks now works with field values that contain
&, and saves inline edits as plain text instead of HTML-encoded text - Fix - Auto inline editing in ACF Blocks no longer replaces empty array or object field values with a placeholder string
- Fix - Passing a post object to
wp_insert_post()no longer causes a fatal error, a regression in 6.8.11 - Fix - Saving relational fields no longer causes a fatal error when another plugin stores an array in meta whose name starts with
_, a regression in 6.8.11 - Fix - Reading a field before the main query is set up no longer triggers an
is_preview()notice, a regression in 6.8.10 - Fix - Viewing a draft, pending or scheduled post without a preview link no longer loads field values from its latest revision, and front-end forms on those views no longer save into the revision, a regression in 6.8.10
- Fix - Image fields no longer fail validation with "File must be a valid image." on hosts that use stream-wrapped file systems
- Fix - Image and Gallery fields now respect the
acf/is_image_fieldfilter when validating values - Fix - Disabled Flexible Content layouts no longer appear in post previews
- Fix - Number and Range field validation messages now show decimal minimum and maximum values correctly
- Fix - The ACF media modal no longer stops showing new uploads after a search returns no results
- Fix - Field group metaboxes that appear without a page reload can now be collapsed and expanded
- Fix - True/False fields using the stylized UI now show the switch correctly in right-to-left languages
- Fix - Field group settings no longer show an incorrect top border on small screens
- Fix - The Icon Picker field no longer attempts to load an attachment preview when the selected icon is not from the Media Library
- Fix - Options pages no longer trigger a "Using null as an array offset" deprecation notice on PHP 8.5
- Fix - Field groups and other ACF internal post types no longer trigger PHP warnings when an
acf/load_{$post_type}filter returns an invalid value - Fix - The license status no longer shows as Active after a license is deactivated
- Security - Custom values submitted to Checkbox, Radio, and Select fields with "Save Custom Values" enabled can no longer corrupt the field's settings or add HTML attributes to the field's wrapper. The new
acf/fields/allow_append_choicesfilter can be used to restrict who can add new choices to a field. Thanks to Jakub Herman via WPScan for the responsible disclosure - Security - ACF now sanitizes field, field group, post type, taxonomy, and options page settings saved by users without the
unfiltered_htmlcapability. For those users, a field's wrapper settings are limited to width, class, and id. Event handler (on*) attributes in a field's wrapper setting are no longer output for any field, including fields registered in PHP or local JSON - Security - Field values of password-protected posts are no longer shown by the
[acf]shortcode, block bindings, JSON-LD output, or the REST API until the password is entered. REST responses also no longer expand a referenced password-protected post into a full post object - Security - The
[acf]shortcode and ACF block bindings now output only user IDs for User fields, rather than personal data such as names and email addresses. The previous output can be restored with the newacf/bindings/allow_user_datafilter - Security - Files uploaded through the basic uploader by users without the
upload_filescapability no longer generate PDF preview images or save embedded audio and video cover art. This can be changed with the newacf/upload/generate_previewsfilter - Security - ACF now discards submitted field values unless the field was rendered for the content being saved or its field group's location rules match it.
Inputs outside these rules, such as fields added with JavaScript, can be allowed with the
acf/form/{context}/allowed_field_keysandacf/options_page/allowed_field_keysfilters. Registration forms no longer save fields from field groups set to "User Form is Add / Edit". Thanks to vuxvinh via WPScan for the responsible disclosure - Security - WordPress's Custom Fields meta box, its AJAX handler, and XML-RPC can no longer change meta that belongs to ACF fields
- Security - Basic uploader nonces are now tied to the content being edited
- Security - The AJAX request that loads field groups while editing a post no longer returns field groups assigned to other content
- Security - The Relationship, Post Object, and Page Link fields no longer reveal the titles or statuses of posts the current user cannot read, and no longer save newly selected posts the user cannot read. Existing selections the user cannot read are shown as "(Restricted item)" and are kept when the user saves. Thanks to vuxvinh via WPScan for the responsible disclosure
- Security - Relationship, Post Object, and Page Link values rendered in ACF Blocks now leave out posts the author of the post cannot read, such as another user's unpublished drafts. This can be disabled with the new acf/fields/relational/hide_unreadable_posts filter
- Security - Bidirectional fields now only add references to posts the current user can edit, terms they can assign, and users they can edit or set as a post's author. Saves made with update_field(), WP-CLI, or cron are not checked, and the new acf/bidirectional/can_update_target and acf/is_trusted_save_context filters can adjust this. Thanks to vuxvinh via WPScan for the responsible disclosure
- Fix - The [acf] shortcode and ACF block bindings no longer cause a fatal error on PHP 8 when a field returns objects, such as a Relationship field set to return post objects. These values, and arrays containing nested values such as an Image field set to return an array, now output nothing, except for User fields, which output user IDs
- Fix - Field settings containing
&,<, or certain HTML entities no longer cause the field to revert to its default settings after saving - Fix - Saving a custom choice no longer removes backslashes from the field's other settings
- Security - ACF now validates that uploaded PDF files begin with the standard
%PDF-header before further processing, rejecting files that do not match the expected format - Security - The Relationship, Post Object, Image, Gallery, and File fields now enforce WordPress read permissions on referenced posts and attachments when returned in REST API responses
- Security - ACF now verifies both preview context and the caller's edit capability before substituting revision data when field values are retrieved for a post
- Security - The
_acf_formtoken used by frontend forms now expires and is bound to its issuing render, andacf_encrypt()/acf_decrypt()gain an optional$contextargument for domain separation between token uses - Security - ACF now consistently runs field validation on frontend form submissions containing field data, ensuring required-field checks and custom
acf/validate_valuefilters cannot be circumvented - Security - ACF's REST API schema no longer discloses per-object field-group configuration in OPTIONS requests to callers who lack read permission on the target object
- Security - The User field AJAX endpoint now validates that the request nonce was created for a User field
- View Release Post
- Enhancement - ACF Blocks registered via
acf_register_block_type()orblock.jsonwithout an explicit version now default to v3 on WordPress 7.1 or later. Blocks that specify a version continue to use the version they declare, and the default can be customized via theacf/blocks/default_block_versionfilter - Enhancement - ACF Blocks v3 now supports a
renderPreviewoption inblock.json. Setting"renderPreview": falseshows a placeholder with the block's icon, title, and an "Edit Block" button in the editor instead of rendering the block's template as a live preview. The block continues to render normally on the front-end, and legacy v2 blocks combining"mode": "edit"with"supports": { "mode": false }are automatically migrated when upgraded to v3 - Fix - Inline editable fields in ACF Blocks V3 no longer require a second click before they can be edited
- Fix - Radio buttons now appear correctly in ACF admin screens
- Fix - Image and Gallery fields no longer reject SVG uploads when the Safe SVG plugin is active
- Fix - Image and Gallery fields no longer reject SVG files
- Security - ACF Image and Gallery fields now enforce server-side validation to accept only image files
- Security - The
pathattribute of registered ACF Blocks is now protected from being overridden by client-supplied block data - Security - ACF's
acf_encrypt()andacf_decrypt()helpers now authenticate encrypted values with an HMAC and no longer fall back to base64 encoding when OpenSSL is unavailable - Security - ACF's comment, user, and options page form save handlers now only save values for fields whose field groups are assigned to the current save context
- Security - The Post Object, Page Link, and Relationship field AJAX search queries now enforce WordPress read permissions, preventing unauthenticated visitors from seeing non-public post statuses or post types
- Security - The User field now returns only user IDs in REST API responses to requesters without the
list_userscapability, preventing unauthenticated visitors from seeing user email addresses
- Fix - Google Maps field values are no longer double-encoded when saved in an ACF block
- Fix - Inserting a Link field value in the Classic Editor no longer triggers validation for other required fields before the post is saved
- Fix - Auto Inline Editing blocks no longer return truthy placeholder strings for empty field values fetched from a different post inside the block render template
- Fix - ACF Blocks (V2 and V3) no longer crash when rendering an oEmbed field whose title begins with
[or{ - Fix - Field group location rules without a location value no longer cause PHP warnings on page load
- Fix - The appearance of the URL, Number, and Select fields has been improved on WordPress 7.0+
- Fix - ACF fields now save on WooCommerce orders when using HPOS in compatibility mode
- Security - ACF PRO's save handler for WooCommerce order fields now verifies security nonces and only attaches on the order edit screen, preventing unauthenticated field value updates for stores utilizing HPOS
- Security - The Flexible Content "Rename Layout" modal no longer allows for the execution of a potential stored XSS vulnerability
- Security - A default limit of 1000 has been applied to user-contributed choices for Checkbox, Radio, and Select fields to improve security, with a new
acf/fields/max_appended_choicesfilter available for customization - Security - Special characters within LIKE patterns are now fully escaped in
wp_optionsqueries via$wpdb->esc_like()
- Security - ACF AJAX field handlers now validate that the request nonce was created for the expected field type
- Enhancement - ACF PRO now satisfies plugin dependencies declared against
advanced-custom-fields, so plugins requiring ACF can activate when only ACF PRO is installed - Enhancement -
acf_inline_toolbar_editing_attrs()now accepts areturn_arrayargument that returns the attributes as an escaped array suitable for use withwp_get_attachment_image() - Fix -
acf_form()with'post_id' => 'new_post'and afieldslist of field names no longer fatal errors whenacf_form_head()runs before WordPress's main query is built - Fix - Multiple
acf_form()calls wrapped inside a single outer<form>tag with one submit button no longer silently drop field values,post_title, orpost_contentfrom the non-last forms - Fix - Duplicating a V3 block with identical attributes no longer displays corrupted preview content in the duplicate
- Fix - Switching between tabs containing WYSIWYG fields no longer leaves the admin menu pinned against a shorter page, which could lock page scroll
- Security - The oEmbed field's AJAX preview no longer performs URL discovery for users without the
edit_postscapability.
- Security - ACF frontend forms (
acf_form()) now respect thepost_titleandpost_contentform configuration options when processing submissions, ensuring those values are only saved when the form is configured to accept them. Thanks to Sarawut Poolkhet (MisterHelloz) for the responsible disclosure. - Security - ACF frontend forms (
acf_form()) now only save values for fields assigned to the form via thefieldsorfield_groupsparameters, or via the form's location rules
- Security - ACF now correctly checks user permissions before running database upgrades on a specific site in a multisite network
- New - A
wp.datastore (acf/fields) is now available in ACF PRO for reading and writing ACF field values from JavaScript, which can be enabled via a newacf/settings/enable_datastorefilter (requires WordPress 6.7 or later). - New - ACF PRO block bindings now support live preview and editing in the block editor, when both the datastore and the
enable_block_bindingssetting are enabled. - New - ACF PRO can now save metabox field values via Gutenberg's native REST flow with full revision and autosave support when using the datastore.
- New - ACF PRO Blocks can now define their field group inline via an
acf.fieldsarray inblock.json, or via afieldsargument inacf_register_block_type(), with field keys auto-generated and scoped to the block - Fix - Repeater and Flexible Content row helpers no longer trigger a PHP 8.x
TypeErrorwhenrow_index_offsetor the active loop index is non-numeric - Fix - V3 Blocks with
hideFieldsInSidebarenabled no longer show fields in the sidebar after the inline toolbar popover is closed - Fix - Scrollbars no longer appear under the tabs in field groups containing many tabs
- Fix - The
acf/delete-{taxonomy}ability no longer returns a 501 error when called without an explicitforceargument, as terms cannot be trashed - Fix - The
prepare_field_for_ability_importfilter is now correctly removed after each Abilities field group import, preventing subsequent imports in the same request from having values corrupted
- Fix - V3 blocks with WYSIWYG fields no longer enqueue TinyMCE editor assets on the frontend
- Fix - V3 blocks with identical attributes and different InnerBlocks content no longer return cached output from the first block on the frontend
- View Release Post
- New - ACF now integrates with the WordPress Abilities API, allowing external consumers (AI tools) to manage field groups, post types, and taxonomies when explicitly enabled via the
enable_acf_aifeature flag - New - ACF can now generate JSON-LD structured data fields when explicitly enabled via the
enable_schemafeature flag - New - ACF now includes WP-CLI support with new
wp acf jsoncommands for importing, exporting, syncing, and checking the status of ACF JSON files - New - ACF custom post Types now support the WordPress 6.9+ "Notes" editor feature via a new "Notes" checkbox in the Supports settings
- Enhancement - The Blocks V3 "Open in Expanded Editor" button text can now be customized via a new
acf.expandedEditorButtonTextblock.json property - Enhancement - A new
acf/blocks/default_expanded_editor_button_textPHP filter allows customizing the default "Open in Expanded Editor" button text for all V3 blocks - Enhancement - The Blocks V3 edit and "Open in Expanded Editor" buttons can now be hidden via a new
acf.expandedEditorButtonsblock.json property - Enhancement - A new
blocks/expanded_editor_overlay_classJS filter allows customizing the CSS class on the Expanded Editor modal overlay - Enhancement - ACF Blocks V3 now preloads the block form HTML alongside the preview, eliminating an extra AJAX call on mount
- Enhancement - ACF inline script tags now use
wp_print_inline_script_tag()for Content Security Policy (CSP) compliance and nonce support - Enhancement - The Expanded Editor buttons are now hidden for V3 blocks that have no fields assigned
- Fix - Flexible Content fields now properly clean up nested postmeta when a parent layout containing nested Flexible Content fields is deleted
- Fix - The Expanded Editor "Done" button now stays disabled until the AJAX save completes, preventing data loss
- Fix - Pressing Escape while the Expanded Editor is saving will no longer close the modal, preventing data loss
- Fix - InnerBlocks content containing backslashes or dollar signs now renders correctly
- Fix - Auto Inline Editing now only applies to ACF Blocks V3, resolving incorrect hover/focus borders appearing on V2 blocks
- Fix - Validation errors in the V3 Expanded Editor no longer cause a dead-end state
- Fix - Icon Picker selections in Repeater fields no longer disappear
- Fix - Range field number input now syncs to the slider and correctly updates V3 block previews
- Fix - Message field Name and Instructions settings are no longer shown in the field group editor
- Fix - Image field no longer crashes in WordPress 7.0 release candidates
- Fix - Auto Inline Editing blocks now receive block context variables in render templates
- Fix - V3 blocks registered via PHP now correctly show the "Open in Expanded Editor" button
- Fix - Flexible Content disabled layouts now work correctly in Blocks V3
- Fix - Auto Inline Editing now works with blocks using
renderCallback - i18n - Added Danish translation
- Security - Users'
unfiltered_htmlcapability is now correctly applied to REST API calls - Security - Block Preview rendering now correctly checks the user has permission to edit that post
- Security - Repeater fields using pagination now correctly checks the user has permissions to edit that post
- Security - Flexible content fields layout title AJAX requests now correctly verify security nonces
- Security - Clone field AJAX admin endpoints now correctly check ACF admin permissions for field group listings
- Security - User field AJAX queries now enforce field-configured role restrictions and validate search permissions
- Security - Post Object, Relationship, and Page Link field AJAX queries now enforce field-configured restrictions for post status, post type, and taxonomy
- Fix - Posts with V3 blocks can now be saved without clicking the block
- Fix - Fields in V3 Blocks used as an InnerBlock are now clickable
- Fix - V3 Blocks with a script tag in the render template no longer crash in the editor
- Fix - V3 Blocks with Inline Editing enabled no longer crash the browser tab in some scenarios
- Fix - V3 Blocks with Inline Editing enabled used as an InnerBlock no longer update the field values of the parent block
- Fix - Quickly closing the expanded editor for V3 blocks will no longer prevent field values from being updated
- View Release Post
- New - ACF Blocks V3 now supports Inline Editing - edit your block content directly in place, right inside the editor. Just opt in to enable it.
- Enhancement - Accordion field accessibility improvements
- Enhancement - Google Maps field accessibility improvements
- Enhancement - Styling improvements to the V3 Blocks expanded editor
- Fix - V3 ACF Blocks validation now clears properly when more than one block is in the editor.
- Fix - Relationship, Post Object, and Page Link fields now sort posts correctly on WordPress 6.8+
- Fix - List tables now respect the convert_field_name_to_lowercase javascript filter
- Fix - WYSIWYG field on attachment pages no longer sends ajax on every keystroke
- Enhancement - Added a new
convert_field_name_to_lowercaseJS filter to allow uppercase letters in ACF field names - Enhancement - The form for V3 Blocks can now be optionally hidden from the sidebar via a new
hideFieldsInSidebarsetting in block.json - Enhancement - V3 Blocks now display an "Open Expanded Editor" button in the sidebar for easier access to the full edit form
- Fix - The buttons to reorder ACF metaboxes are no longer hidden for metaboxes in the block editor sidebar
- Fix - V3 Blocks now display a fallback message when the block preview can't be rendered due to invalid HTML being used in field values
- Fix - V3 Blocks no longer show a loading spinner when preloaded
- Fix - V3 Blocks now save default field values even if the block wasn't interacted with before saving
- Fix - Pressing CMD/CTRL + Z no longer causes the fields to disappear in V3 Blocks
- Fix - The form for V3 Blocks now opens on the left side in RTL languages
- Fix - The Color Picker palette now displays correctly with a larger number of custom palette colors
- Fix - The WYSIWYG field no longer displays an extra textarea in ACF Blocks
- Fix - The type signature of the ACF Blocks render function now matches prior to 6.6, resolving potential type hinting errors
- Fix - V3 Blocks now correctly update the block preview when changing text controls
- Fix - V3 Blocks now work correctly in the Widget block editor
- Fix - V3 Blocks no longer render an extra hidden div into the block editor
- Fix - Fields on V3 blocks now consistently render properly when switching between “Post” and “Block” view in the sidebar
- View Release Post
- New - ACF Blocks Version 3 supports WordPress Block API Version 3
- New - ACF now requires WordPress version 6.2 or newer
- Enhancement - Field Groups can now have a separate Display Title
- Enhancement - Accessibility improvements for button groups, checkbox, radio, and image field types
- Enhancement - Color Picker field can now use a custom palette or use theme.json colors as the palette
- Enhancement - ACF admin notices now use WordPress core styles again
- Enhancement - The Flexible Content “Delete Layout” and “Rename Layout” modals now display correctly on mobile
- Fix - Blocks V3: You can now edit ACF blocks in Edit mode inside WP Core's pattern editor
- Fix - Blocks V3: Validation errors now first appear after you click "Save/publish", as opposed to immediately, while you are typing into a field for the first time
- Fix - Blocks V3: After fixing a field validation error it shows as fixed immediately as opposed to needing to click out of the block and back into it
- Fix - Blocks V3: Blocks with radio buttons no longer affect each other's field values
- Fix - Blocks V3: Blocks with required radio buttons now validate correctly
- Fix - Blocks V3: ACF field validation now works in the Site Editor
- Fix - Blocks V3: WYSIWYG fields are no longer affected by typing into other blocks
- Fix - New field names are lowercase only
- Fix - Icon Picker now enforces required validation
- Fix - Calls to jQuery’s deprecated focus function have been updated to use the trigger function
- Fix - Layouts inside cloned Flexible Content fields can now be disabled and renamed
- i18n - Updated PRO Japanese translations (props danielkun)
- Enhancement - The Flexible Content “Expand All” and “Collapse All” button now appear correctly on mobile
- Enhancement - The Flexible Content delete layout button is now back in the main layout header, making it easier to delete layouts
- Enhancement - The JSON import tool now limits the selectable files to JSON files
- Fix - Disabled Flexible Content layouts are no longer counted towards min/max layout validation
- Fix - The top “Add Row” button for layouts is now disabled when layouts have reached the max layouts validation
- Fix - The per-layout “Add Row” and “Duplicate Layout” buttons are now disabled when layouts have reached the max layouts validation
- Fix - Disabling Flexible Content layouts no longer disables layouts in cloned Flexible Content fields using a different post ID on the same page
- Fix - Flexible Content “Add Layout” menu is no longer hidden by some field types
- Fix - Flexible Content layout names can now allow some safe HTML
- Fix - When creating a temporary post type during import, ACF now correctly sets the ACF post type, rather than defaulting to post
- Fix - ACF PRO updates are now shown even when no other plugins have an update available
- Fix - Flexible Content layouts configured with a "Layout" setting of "Table" are now rendered correctly in the post editor
- Fix - Flexible Content "Add Layout" buttons now insert the new layout in the correct position
- Fix - Long Flexible Content layout names no longer extend outside of the "Add Layout" dropdown
- New - Flexible Content layouts can now be renamed in the post editor, giving content editors better clarity when managing layouts
- New - Flexible Content layouts can now be disabled, preventing them from rendering on the frontend without needing to delete their data
- New - Flexible Content layouts can now be collapsed and expanded in bulk for faster content editing
- New - Editing a Flexible Content layout now highlights the layout being edited, making it easier to identify
- New - The Date and Date Time Picker fields can now be configured to default to the current date
- Fix - Custom Icon Picker tabs now work correctly when used inside an ACF Block
- Fix - Duplicating a Field Group no longer causes a fatal error when using Russian translations
- Fix - ACF classes no longer use dynamic class properties, improving compatibility with PHP 8.2+
- Fix - ACF PRO no longer shows an update available immediately after updating to the latest version
- Fix - Field group metabox collapse and expand buttons are no longer misaligned in the post editor
- Fix - The ACF Site Health section no longer causes a PHP warning when field group location rules are incomplete
- Security - HTML is now escaped from field validation errors and tooltips
- Security - Unsafe HTML in field group labels is now correctly escaped for conditionally loaded field groups, resolving a JS execution vulnerability in the classic editor
- Security - HTML is now escaped from field group labels when output in the ACF admin
- Security - Bidirectional and Conditional Logic Select2 elements no longer render HTML in field labels or post titles
- Security - The
acf.escHtmlfunction now uses the third party DOMPurify library to ensure all unsafe HTML is removed. A newesc_html_dompurify_configJS filter can be used to modify the default behaviour - Security - Post titles are now correctly escaped whenever they are output by ACF code. Thanks to Shogo Kumamaru of LAC Co., Ltd. for the responsible disclosure
- Security - An admin notice is now displayed when version 3 of the Select2 library is used, as it has now been deprecated in favor of version 4
- New - In ACF PRO, fields can now be added to WooCommerce Subscriptions when using HPOS
- Security - Changing a field type no longer enables the "Allow Access to Value in Editor UI" setting
- Fix - Paginated Repeater fields no longer save duplicate values when saving to a WooCommerce Order with HPOS disabled
- Fix - Blocks registered via acf_register_block_type() with a
parentvalue ofnullno longer fail to register
- New - Select fields can now be configured to allow creating new options when editing the field's value (requires the "Stylized UI" and "Multiple" field settings to be enabled)
- Enhancement - The "Escaped HTML" warning notice introduced in ACF 6.2.5 is now disabled by default
- Enhancement - The Icon Picker field now supports supplying an array of icons to a custom tab via a new
acf/fields/icon_picker/{tab_name}/iconsfilter - Fix - ACF Blocks are now forced into preview mode when editing a synced pattern
- Fix - The free ACF plugin once again works with the Classic Widgets plugin and the legacy ACF Options Page addon
- Fix - ACF no longer causes an infinite loop in bbPress when editing replies
- Fix - Calling
acf_get_reference()with an invalid field name no longer causes a fatal error
- New - In ACF PRO, fields can now be added to WooCommerce orders when using HPOS
- Enhancement - ACF now uses Composer to autoload some classes
- Fix - Repeater pagination now works when the Repeater is inside a Group field
- Fix - Various translations are no longer called before the WordPress
initaction hook - Security - Link field no longer has a minor local XSS vulnerability
- i18n - Various British English translation strings no longer have a quoting issue breaking links
- i18n - Added Dutch (formal) translations (props @toineenzo)
- 增强 - 当现场验证失败时发生的错误消息现在不足的安全性 nonce 现在有其他上下文
- 修复 - 重复的 ACF 块在启用块预加载后初始保存后不再丢失其现场值
- 修复 - 启用 React Strictmode 时,包含复杂字段类型的 ACF 块现在正确行为
- 增强功能 - 点击后可复制字段组键值
- 修复 - 通过条件逻辑隐藏字段的中继表现在可正确呈现
- 修复 - ACF 块现在可在 React StrictMode 中正确运行
- 修复:WordPress 块应用程序接口版本为 3 的 ACF 块不再提供编辑模式,因为 iframe 中不支持字段编辑。
- 修复 - 当任何不支持的传统 ACF 附加组件处于活动状态时,ACF Free 不再导致致命错误
- 修复 - 当 WPML 处于活动状态时,ACF Free 不再导致致命错误
- 安全性 - 现在,为自定义文章类型和分类法设置元宝回调需要管理员身份,多站点安装则需要超级管理员身份
- 安全性 - 字段特定的 ACF nonces 现在有了前缀,解决了第三方 nonces 在 AJAX 调用中可能被视为有效的问题
- 增强功能 - 在编辑字段组时,新增了「关闭并添加字段」选项,可在编辑字段后插入一个新字段
- 增强功能 - ACF 和 ACF PRO 现在共享相同的插件更新程序,以提高可靠性和性能
- 修复 - 导出包含元框回调的文章类型和分类法现在可正确导出用户定义的回调
- 安全性 - 在字段组编辑器中编辑 ACF 字段不再执行存储的 XSS 漏洞。感谢来自 Viettel Cyber Security 的 Duc Luong Tran (janlele91) 负责披露
- 安全性--文章类型和分类元方框回调不再能够访问任何超全局值,从而进一步加强了 6.3.8 中的原始修复。
- 修复--在块编辑器中使用并附加到侧边栏的 ACF 字段现在可正确验证。
- Security - ACF defined Post Type and Taxonomy metabox callbacks no longer have access to $_POST data. (Thanks to the Automattic Security Team for the disclosure)
- Security - ACF Free now uses its own update mechanism from WP Engine servers
- Security - Newly added fields now have to be explicitly set to allow access in the content editor (when using the ACF shortcode or Block Bindings) to increase the security around field permissions. See the release notes for more details
- Security Fix - Field labels are now correctly escaped when rendered in the Field Group editor, to prevent a potential XSS issue. Thanks to Ryo Sotoyama of Mitsui Bussan Secure Directions, Inc. for the responsible disclosure
- Fix - Validation and Block AJAX requests nonces will no longer be overridden by third party plugins
- Fix - Detection of third party select2 libraries will now default to v4 rather than v3
- Fix - Block previews will now display an error if the render template PHP file is not found
- Fix - The ACF Shortcode now correctly outputs a comma separated list of values for arrays
- Fix - ACF Blocks rendered in auto mode now correctly re-render their previews after editing fields
- Fix - ACF Block validation no longer raises required validation messages if HTML will automatically select the first value when rendered
- Fix - ACF Block validation no longer raises required validation messages if a default value will be rendered as the field value
- Fix - ACF Block validation no longer raises required validation messages for fields hidden by conditional logic when adding a new block
- Security Fix - The ACF shortcode now prevents access to fields from different private posts by default. View the release notes for more information
- Fix - Users without the
edit_postscapability but with custom capabilities for a editing a custom post type, can now correctly load field groups loaded via conditional location rules - Fix - Block validation no longer validates a field’s sub fields on page load, only on edit. This resolves inconsistent validation errors on page load or when first adding a block
- Fix - Deactivating an ACF PRO license will now remove the license key even if the server call fails
- Fix - Field types returning objects no longer cause PHP warnings and errors when output via
the_field,the_sub_fieldor the ACF shortcode, or when retrieved by aget_function with the escape html parameter set - Fix - Server side errors during block rendering now gracefully displays an error to the editor
- Enhancement - All dashicons are now available to the icon picker field type
- Fix - The True/False field now correctly shows it’s description message beside the switch when using the Stylized UI setting
- Fix - Conditional logic values now correctly load options when loaded over AJAX
- Fix - ACF PRO will no longer trigger license validation calls when loading a front-end page
- i18n - Fixed an untranslatable string on Option Page previews
- Fix - ACF Blocks no longer trigger a JavaScript error when fetched via AJAX
- Security Fix - ACF now generates different nonces for each AJAX-enabled field, preventing subscribers or front-end form users from querying other field results
- Security Fix - ACF now correctly verifies permissions for certain editor only actions, preventing subscribers performing those actions
- Security Fix - Deprecated a legacy private internal field type (output) to prevent it being able to output unsafe HTML
- Security Fix - Improved handling of some SQL filters and other internal functions to ensure output is always correctly escaped
- Security Fix - ACF now includes blank index.php files in all folders to prevent directory listing of ACF plugin folders for incorrectly configured web servers
- Fix - ACF Blocks in widget areas no longer cause a fatal error when no context is available
- Fix - ACF Blocks with no fields assigned no longer show a gap in the sidebar where the form would render
- Fix - Repeater and Flexible Content fields no longer error when duplicating or removing rows containing Icon Picker subfields
- Fix - ACF Blocks containing Flexible Content fields now correctly load their edit form
- Fix - ACF Blocks no longer have a race condition where the data store is not initialized when read
- Fix - ACF Blocks no longer trigger a JS error for blocks without fields and with an empty no-fields message
- Fix - ACF Block preloading now works correctly for fields consuming custom block context
- Fix - ACF Block JavaScript debug messages now correctly appear when SCRIPT_DEBUG is true
- Enhancement - Options Pages registered in the UI can now be duplicated
- Fix - ACF Block validation now correctly validates Repeater, Group, and Flexible Content fields
- Fix - ACF Block validation now correctly validates when a field is using a non-default return type
- Fix - Fields moved between field groups now correctly updates both JSON files
- Fix - Icon Picker fields now render correctly when using left-aligned labels
- Fix - Icon Picker fields no longer renders tabs if only one tab is selected for display
- Fix - Icon Picker fields no longer crash the post editor if no icon picker tabs are selected for displayed
- Fix - True/False field now better handles longer On/Off labels
- Fix - Select2 results loaded by AJAX for multi-select Taxonomy fields no longer double encode HTML entities
- Fix - A possible fatal error no longer occurs in the new site health functionality for ACF PRO users
- Fix - A possible undefined index error no longer occurs in ACF Blocks for ACF PRO users
- New - ACF now requires WordPress version 6.0 or newer, and PHP 7.4 or newer.
- New - ACF Blocks now support validation rules for fields. View the release notes for more information
- New - ACF Blocks now supports storing field data in the postmeta table rather than in the post content
- New - Conditional logic rules for fields now support selecting specific values for post objects, page links, taxonomies, relationships and users rather than having to enter the ID
- New - New Icon Picker field type for ACF and ACF PRO
- New - Icon selection for a custom post type menu icon
- New - Icon selection for an options page menu icon
- New - ACF now surfaces debug and status information in the WordPress Site Health area
- New - The escaped html notice can now be permanently dismissed
- Enhancement - Tab field now supports a
selectedattribute to specify which should be selected by default, and support class attributes - Fix - Block Preloading now works reliably in WordPress 6.5 or newer
- Fix - Select2 results loaded by AJAX for post object fields no longer double encode HTML entities
- Fix - Custom post types registered with ACF will now have custom field support enabled by default to better support revisions
- Fix - The first preview after publishing a post in the classic editor now displays ACF fields correctly
- Fix - ACF fields and Flexible Content layouts are now correctly positioned while dragging
- Fix - Copying the title of a field inside a Flexible Content layout no longer adds whitespace to the copied value
- Fix - Flexible Content layout names are no longer converted to lowercase when edited
- Fix - ACF Blocks with attributes without a default now correctly register
- Fix - User fields no longer trigger a 404 when loading results if the nonce generated only contains numbers
- Fix - Description fields for ACF items now support being solely numeric characters
- Fix - The field group header no longer appears above the WordPress admin menu on small screens
- Fix - The
acf/json/save_file_namefilter now correctly applies when deleting JSON files - i18n - All errors raised during ACF PRO license or update checks are now translatable
- Other - The ACF Shortcode is now disabled by default for new installations of ACF as discussed in the ACF 6.2.7 release notes
- Security Fix - ACF Blocks no longer allow render templates, or render or asset callbacks to be overridden in the block's attributes. For full information, please read the release blog post
- Enhancement - The Select2 escapeMarkup function can now be overridden when initializing a custom Select2
- Fix - “Hide on Screen” settings are now correctly applied when using conditionally loaded field groups
- Fix - Field names are no longer converted to lowercase when editing the name
- Fix - Field group titles will no longer convert HTML entities into their encoded form
- New - Support for the Block Bindings API in WordPress 6.5 with a new
acf/fieldsource. For more information on how to use this, please read the release blog post - New - Support for performance improvements for translations in WordPress 6.5
- Enhancement - A new JS filter,
select2_escape_markupnow allows fields to customize select2's HTML escaping behavior - Fix - Options pages can no longer set to have a parent of themselves
- Fix - ACF PRO license activations on multisite subsite installs will now use the correct site URL
- Fix - ACF PRO installed on multisite installs will no longer try to check for updates resulting in 404 errors when the updates page is not visible
- Fix - ACF JSON no longer produces warnings on Windows servers when no ACF JSON folder is found
- Fix - Field and layout names can now contain valid non-ASCII characters
- Other - ACF PRO now requires a valid license to be activated in order to use PRO features. Learn more
- Security Fix -
the_fieldnow escapes potentially unsafe HTML as notified since ACF 6.2.5. For full information, please read the release blog post - Security Fix - Field and Layout names are now enforced to alphanumeric characters, resolving a potential XSS issue
- Security Fix - The default render template for select2 fields no longer allows HTML to be rendered resolving a potential XSS issue
- Security Enhancement - A
acf/shortcode/prevent_accessfilter is now available to limit what data the ACF shortcode is allowed to access - Security Enhancement - i18n translated strings are now escaped on output
- Enhancement - ACF now universally uses WordPress file system functions rather than native PHP functions
- Fix - Fatal JS error no longer occurs when editing fields in the classic editor when Yoast or other plugins which load block editor components are installed
- Fix - Using
$escape_htmlon get functions for array returning field types no longer produces an Array to string conversion error
- Enhancement - The
get_field()and otherget_functions now support anescape_htmlparameter which return an HTML safe field value - Enhancement - The URL field will be now escaped with
esc_urlrather thanwp_kses_postwhen returning an HTML safe value - Fix - ACF fields will now correctly save into the WordPress created revision resolving issues with previews of drafts on WordPress 6.4 or newer
- Fix - Multisite subsites will now correctly be activated by the main site where the ACF PRO license allows, hiding the updates page on those subsites
- Fix - Field types in which the
requiredproperty would have no effect (such as the tab, or accordion) will no longer show the option - Fix - Duplicating a field group now maintains the current page of field groups being displayed
- Fix - Fields in ACF Blocks in edit mode in hybrid themes will now use ACF's styling, rather than some attributes being overridden by the theme
- Fix - Text in some admin notices will no longer overlap the dismiss button
- Fix - The word
linkis now prohibited from being used as a CPT name to avoid a WordPress core conflict - Fix - Flexible content layouts can no longer be duplicated over their maximum count limit
- Fix - All ACF notifications shown outside of ACF's admin screens are now prefixed with the plugin name
- Fix - ACF no longer checks if a polyfill is needed for <PHP7 and the polyfill has been removed
- Security Fix - The ACF shortcode will now run all output through
wp_kses, escaping unsafe HTML. This may be a breaking change to your site but is required for security, a message will be shown in WordPress admin if you are affected. Please see the blog post for this release for more information. Thanks to Francesco Carlucci via Wordfence for the responsible disclosure - Security - ACF now warns via an admin message, when upcoming changes to
the_fieldandthe_sub_fieldmay require theme changes to your site to avoid stripping unsafe HTML. Please see the blog post for this release for more information - Security - Users may opt in to automatically escaping unsafe HTML via a new filter
acf/the_field/escape_html_optinwhen usingthe_fieldandthe_sub_fieldbefore this becomes default in an upcoming ACF release.
- Fix - Custom Post Types labels now match the WordPress 6.4 behavior for "Add New" labels
- Fix - When exporting both post types and taxonomies as PHP, taxonomies will now appear before post types, matching the order ACF registers them. This resolves issues where taxonomy slugs will not work in post type permalinks
- Fix - Advanced Settings for Taxonomies, Post Types or Options Pages now display with the correct top padding when toggled on
- Fix - When a parent option page is set to "Redirect to Child Page", the child page will now correctly show it's parent setting
- Fix - When activated as a must-use plugin, the ACF PRO "Updates" page is now visible. Use the existing
show_updatessetting to hide - Fix - When activated as a must-use plugin, ACF PRO licenses defined in code will now correctly activate sites
- Fix - When
show_updatesis set or filtered to false, ACF PRO will now automatically still activate defined licenses - i18n - Maintenance and internal upstream messages from the ACF PRO activation server are now translatable
- View Release Post
- New - An ACF Blocks specific JSON schema for block.json is now available on GitHub
- New - Flexible Content fields now show the layout name in the layout's header bar and supports click-to-copy
- New - Duplicating Flexible Content layouts now appends "Copy" to their name and label, matching the behavior of field group duplication
- Enhancement - ACF PRO will now automatically attempt license reactivation when the site URL changes, e.g. after a site migration. This resolves issues where updates may fail
- Enhancement - Presentation setting for "High" placement of the Field Group made clear that it's not supported in the block editor
- Fix -
acf_format_datenow ensures the date parameter is valid to prevent fatal errors if other data types are passed in - Fix - CPTs with a custom icon URL now display the posts icon in the location column of the field groups screen
- Fix - The ACF JSON import form will now disable on first submit resolving an issue where you could submit the form twice
- Fix - The "Add Row" button in the Flexible Content field now displays correctly when using nested layouts
- Fix - Warning and Error notices no longer flicker on ACF admin pages load
- i18n - ACF PRO license activation success and error messages are now translatable
- Enhancement - ACF Blocks which have not been initialized by the editor will now render correctly
- Enhancement - Added a new
acf/filesizefilter to allow third party media plugins to bypass ACF callingfilesize()on attachments with uncached file sizes, which may result in a remote download if offloaded - Enhancement - ACF PRO license status and subscription expiry dates are now displayed on the “Updates” page
- Fix - Product pages for WooCommerce version 8.2 or newer now correctly support field group location rules
- Fix - Relationship field items can now be removed on mobile devices
- Fix - Color picker fields no longer autocomplete immediately after typing 3 valid hex characters
- Fix - Field settings no longer appear misaligned when the viewport is something other than 100%
- Fix - Select fields without an aria-label no longer throw a warning
- Fix - CPTs and Taxonomies with a custom text domain now export correctly when using PHP export
- Fix - Editing a field group no longer generates an error when UI options pages are disabled
- New - Options Pages created in the admin UI can now be assigned as child pages for any top-level menu item
- New - Added a "Title Placeholder" setting to ACF Post Types which filters the "Add title" text when editing posts
- Enhancement - ACF PRO will now warn when it can't update due to PHP version incompatibilities
- Enhancement - ACF PRO will now work correctly with WordPress automatic updates
- Enhancement - The internal ACF Blocks template attribute parser function
parseNodeAttrcan now be shortcut with the newacf_blocks_parse_node_attrfilter. - Enhancement - Removed legacy code for supporting WordPress versions under 5.8
- Fix - The "Menu Position" setting is no longer hidden for child options pages
- Fix - The tabs for the "Advanced" settings in Post Types and Taxonomies are now rendered inside a wrapper div
- Fix - Options pages will no longer display as a child page in the list view when set to a top level page after previously being a child
- Fix - Conflict with Elementor CSS breaking the ACF PRO banner
- Fix - Errors generated during the block editor's
savePostfunction will no longer be caught and ignored by ACF
- View Release Post
- New - ACF now requires WordPress version 5.8 or newer, and PHP 7.0 or newer. View the release post for more information
- New - Bidirectional Relationships now supported for Relationship, Post Object, User and Taxonomy fields. View the release post for more information
- New - Options Pages can now be registered and managed by the admin UI in ACF PRO
- New - Link to the product feedback board added to the plugin footer
- Enhancement - ACF JSON now supports multiple save locations (props Freddy Leitner)
- Enhancement - ACF Post Types and Taxonomies can now be duplicated
- Enhancement - The filename for JSON files can now be customized with the
acf/json/save_file_namefilter - Fix - REST updates of fields with choices containing integer or mixed keys now behave correctly
- Fix - Using the
block_type_metadata_settingsPHP filter to add usesContext values no longer breaks ACF blocks - Fix - Notice to import post types/taxonomies from CPTUI no longer flashes on page load
- Fix - Various buttons for fields in blocks now display correctly
- Fix - The settings for the DateTime field are no longer cut off when nested in several fields in the field group editor
- Fix - The newline added to the end of JSON files will now use
PHP_EOLto detect the correct newline character with a filteracf/json/eof_newlineto alter it. - i18n - Updated French and Portuguese translations (Thanks to pedro-mendonca and maximebj)