Kitgenix CAPTCHA for Cloudflare Turnstile
| 开发者 |
kitgenix
carlbensy16 |
|---|---|
| 更新时间 | 2026年9月3日 04:29 |
| 捐献地址: | 去捐款 |
| PHP版本: | 8.1 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv3 or later |
| 版权网址: | 版权信息 |
详情介绍:
- WordPress login.
- WordPress registration.
- Lost-password and password-reset flows.
- WordPress comments.
- Custom login forms produced with
wp_login_form(). - WooCommerce login, registration, lost password, checkout and related account flows supported by the integration.
- Easy Digital Downloads.
- Elementor forms.
- Contact Form 7.
- WPForms.
- Gravity Forms.
- Fluent Forms.
- Formidable Forms.
- Forminator.
- Ninja Forms.
- Jetpack Forms.
- JetFormBuilder.
- Kadence Forms.
- MailPoet.
- bbPress.
- BuddyPress.
- wpDiscuz.
- Ultimate Member.
- MemberPress.
- Paid Memberships Pro.
- Kitgenix Plugin Score integration points included in the codebase.
[kitgenix_turnstile]
The shortcode is useful when the site owner needs to render the widget in a supported custom workflow. Rendering a widget alone does not automatically secure arbitrary custom PHP processing; custom form handlers must still validate the submitted token server-side.
Diagnostics, Metrics and Site Health
The plugin includes diagnostics for configuration and verification health, local counters for passed/failed checks, latency information, recent verification events and integration-level metrics. Site Health integration can surface configuration or connectivity issues to administrators.
Developer Mode adds additional troubleshooting detail without changing the fundamental requirement that live submissions be verified correctly when protection is active.
Settings Portability
Settings can be exported and imported for controlled migration between WordPress installations. The transfer system is designed for plugin configuration rather than for exporting visitor submissions or unrelated site data.
Performance and Script Loading
The public Cloudflare Turnstile script is loaded only for pages/contexts where the plugin determines that a Turnstile widget may be needed. The loader includes duplicate-script detection so multiple integrations do not intentionally enqueue several copies of the same Turnstile API script.
Public assets are kept separate from the admin interface, and admin-only diagnostics/settings code does not need to run as part of every anonymous form request.
Privacy and Data Flow
Turnstile is an external service provided by Cloudflare, so challenge rendering and server-side verification necessarily communicate with Cloudflare. The plugin itself stores configuration and limited diagnostic/aggregate verification data locally. It does not require a Kitgenix account and does not send form contents to Kitgenix for verification.
The exact Cloudflare data flow, WordPress.org Hub request and Google Fonts admin request are documented in the External Services section below.
Common Uses
- Protect a WordPress login page from automated credential attacks.
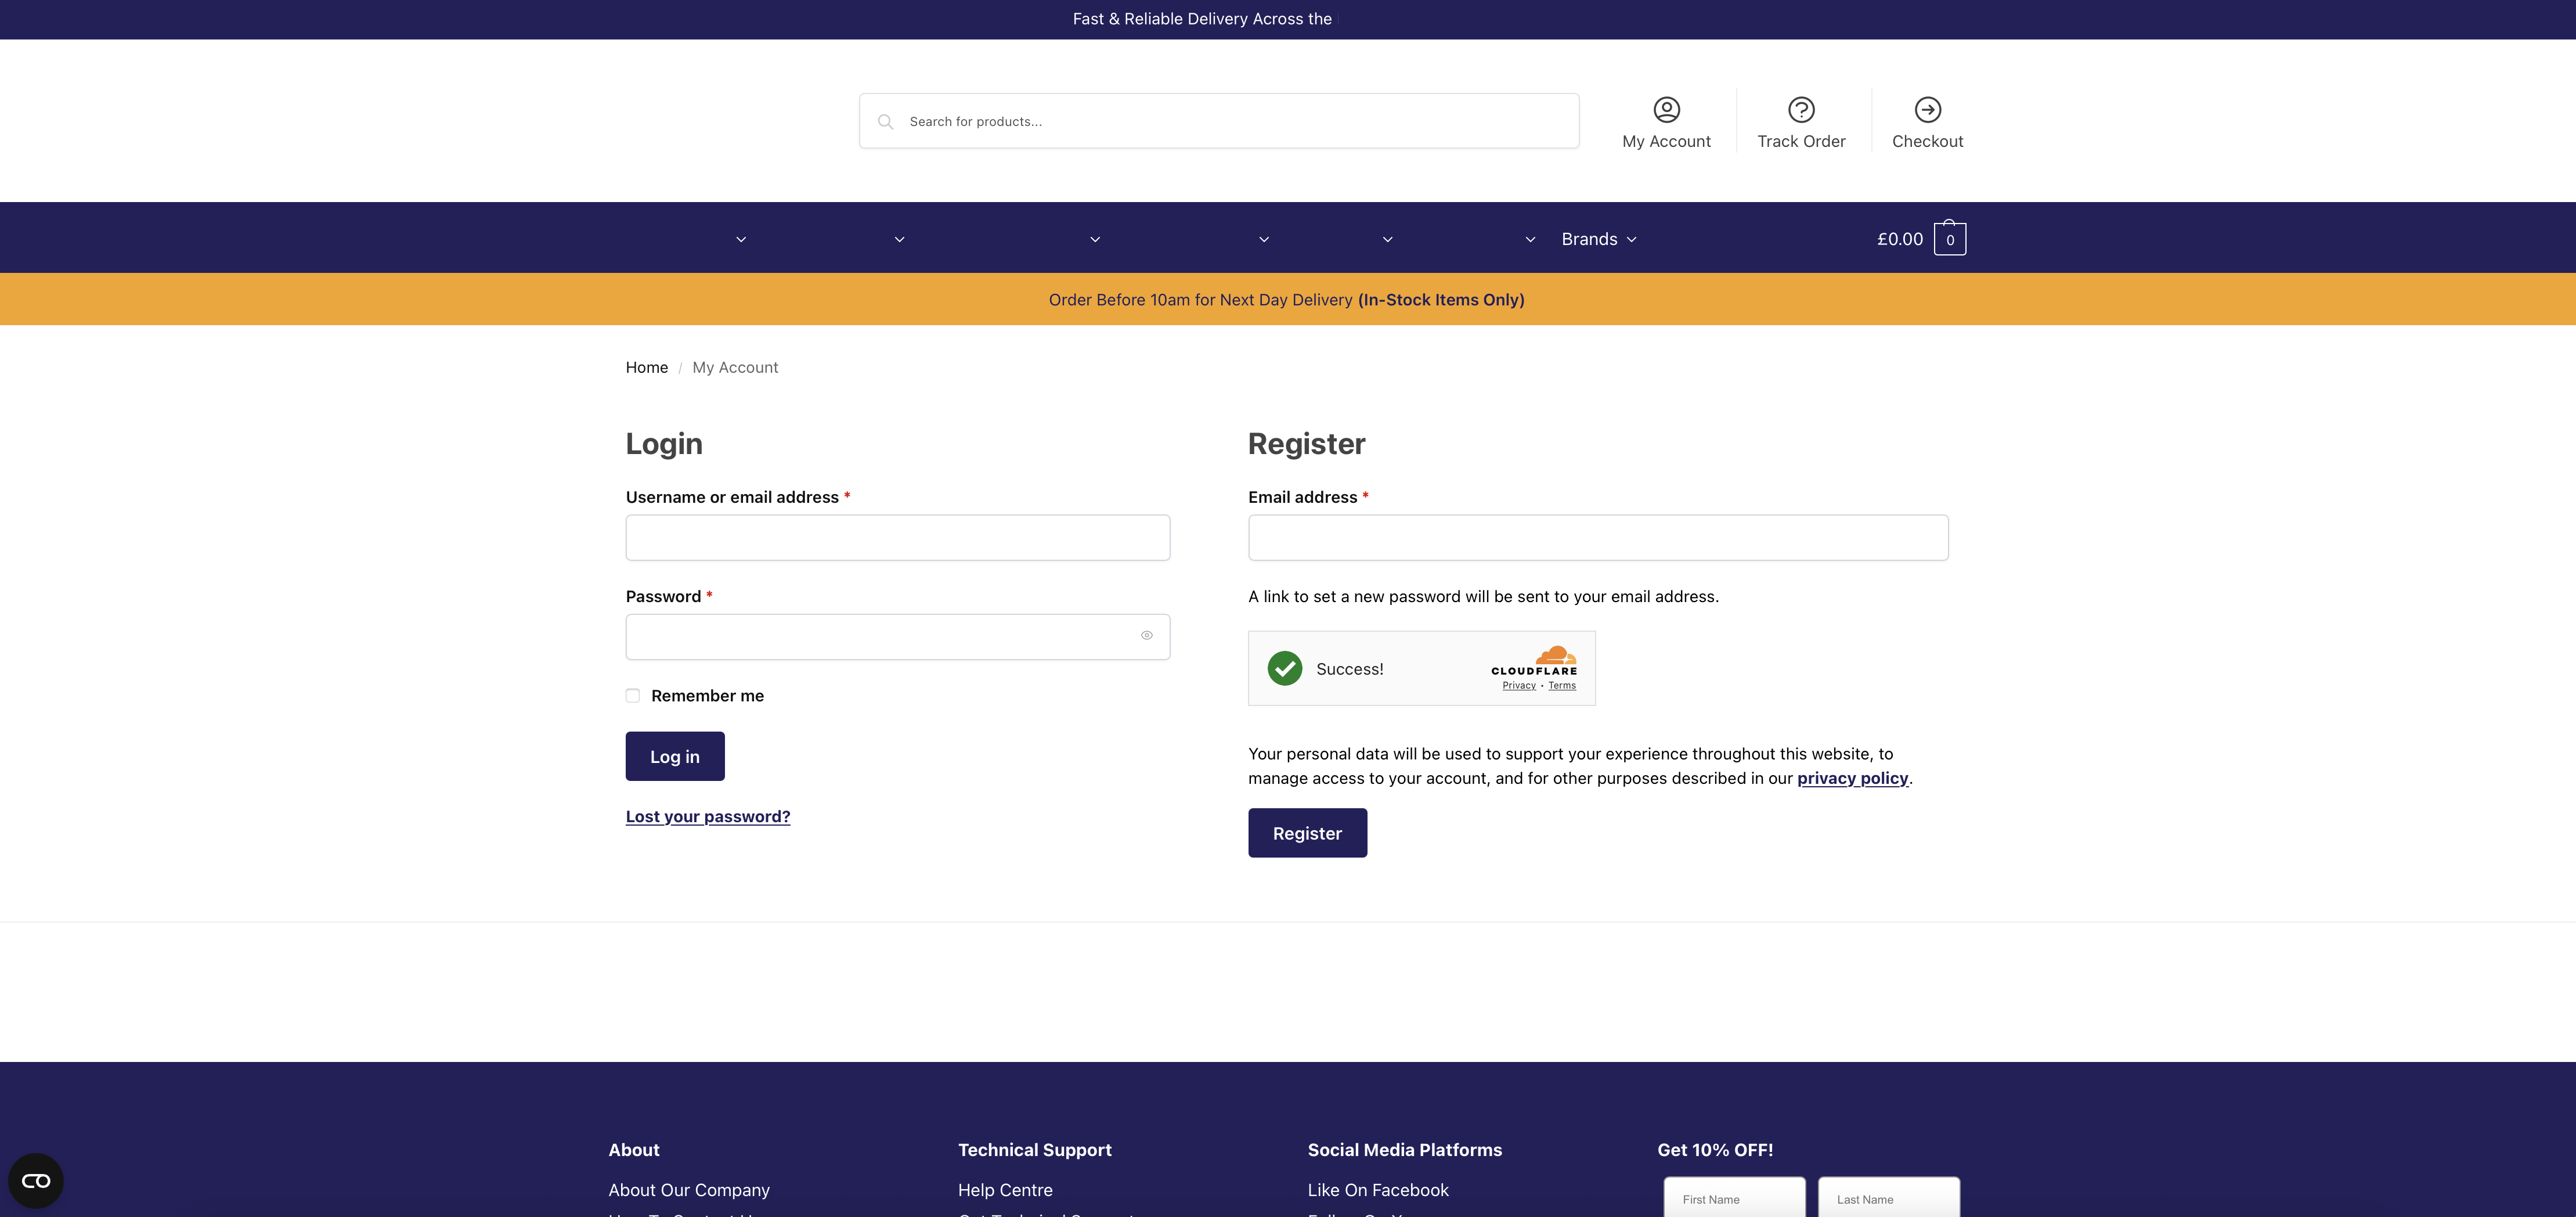
- Reduce spam registrations on WordPress or WooCommerce.
- Add anti-bot verification to WooCommerce checkout and account forms.
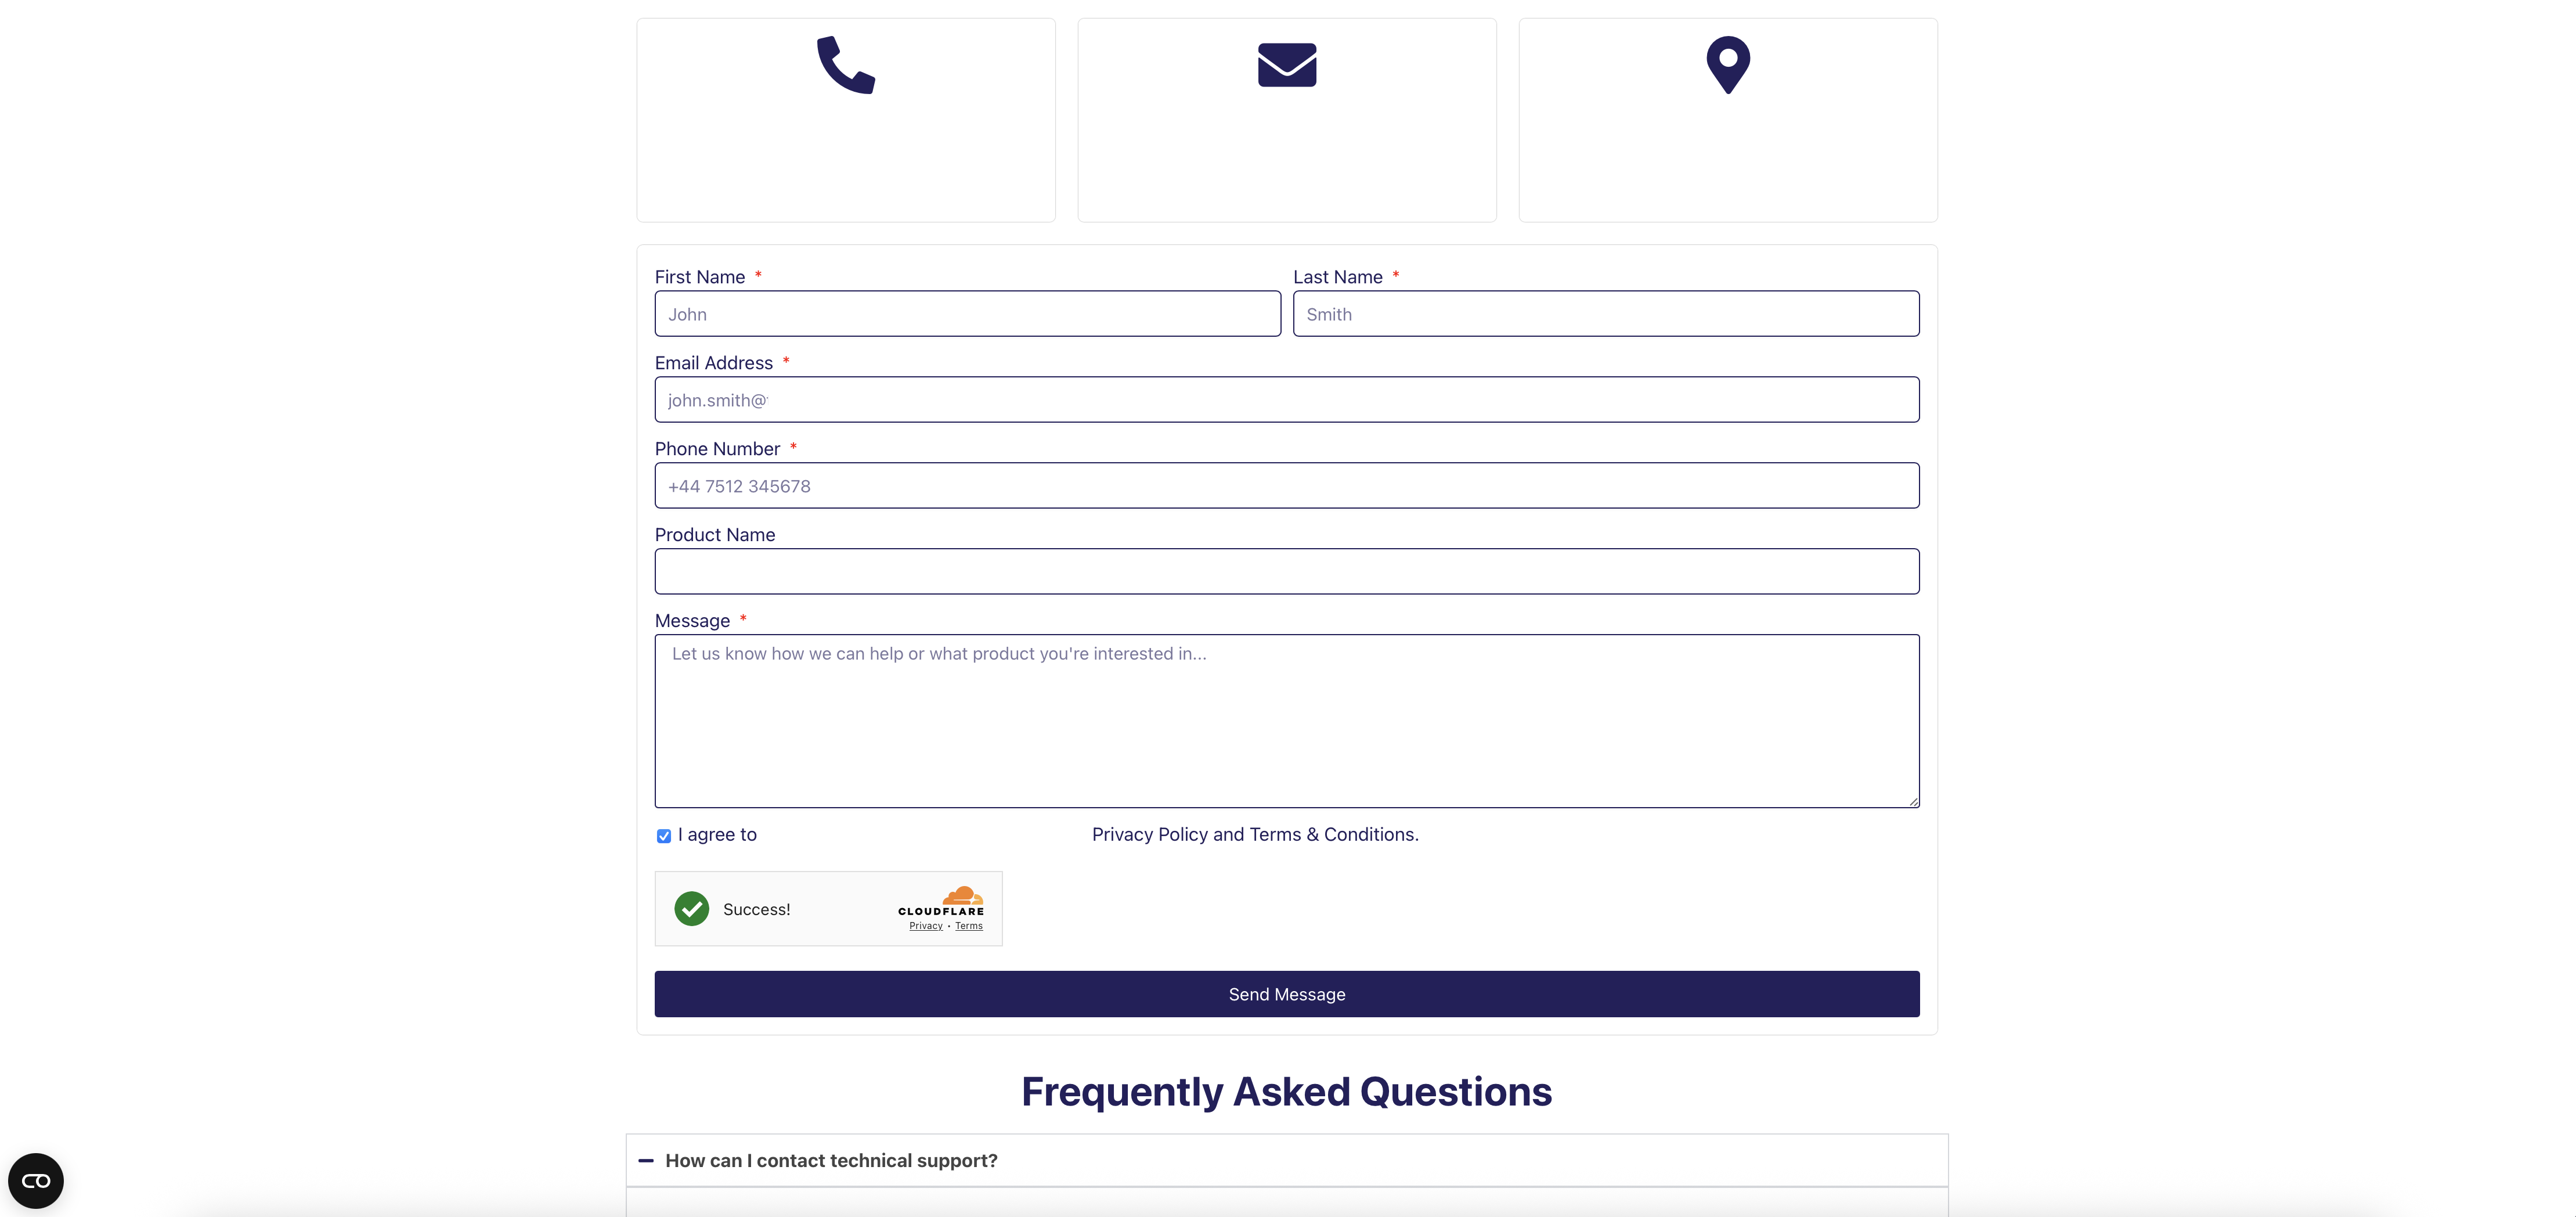
- Protect Elementor and popular WordPress form plugins with one central Turnstile configuration.
- Add a challenge to membership, forum and community registration/login flows.
- Replace more intrusive CAPTCHA experiences with Cloudflare Turnstile while keeping server-side validation.
安装:
- Upload the plugin through Plugins → Add New → Upload Plugin, or install it from the WordPress.org Plugin Directory.
- Activate Kitgenix CAPTCHA for Cloudflare Turnstile.
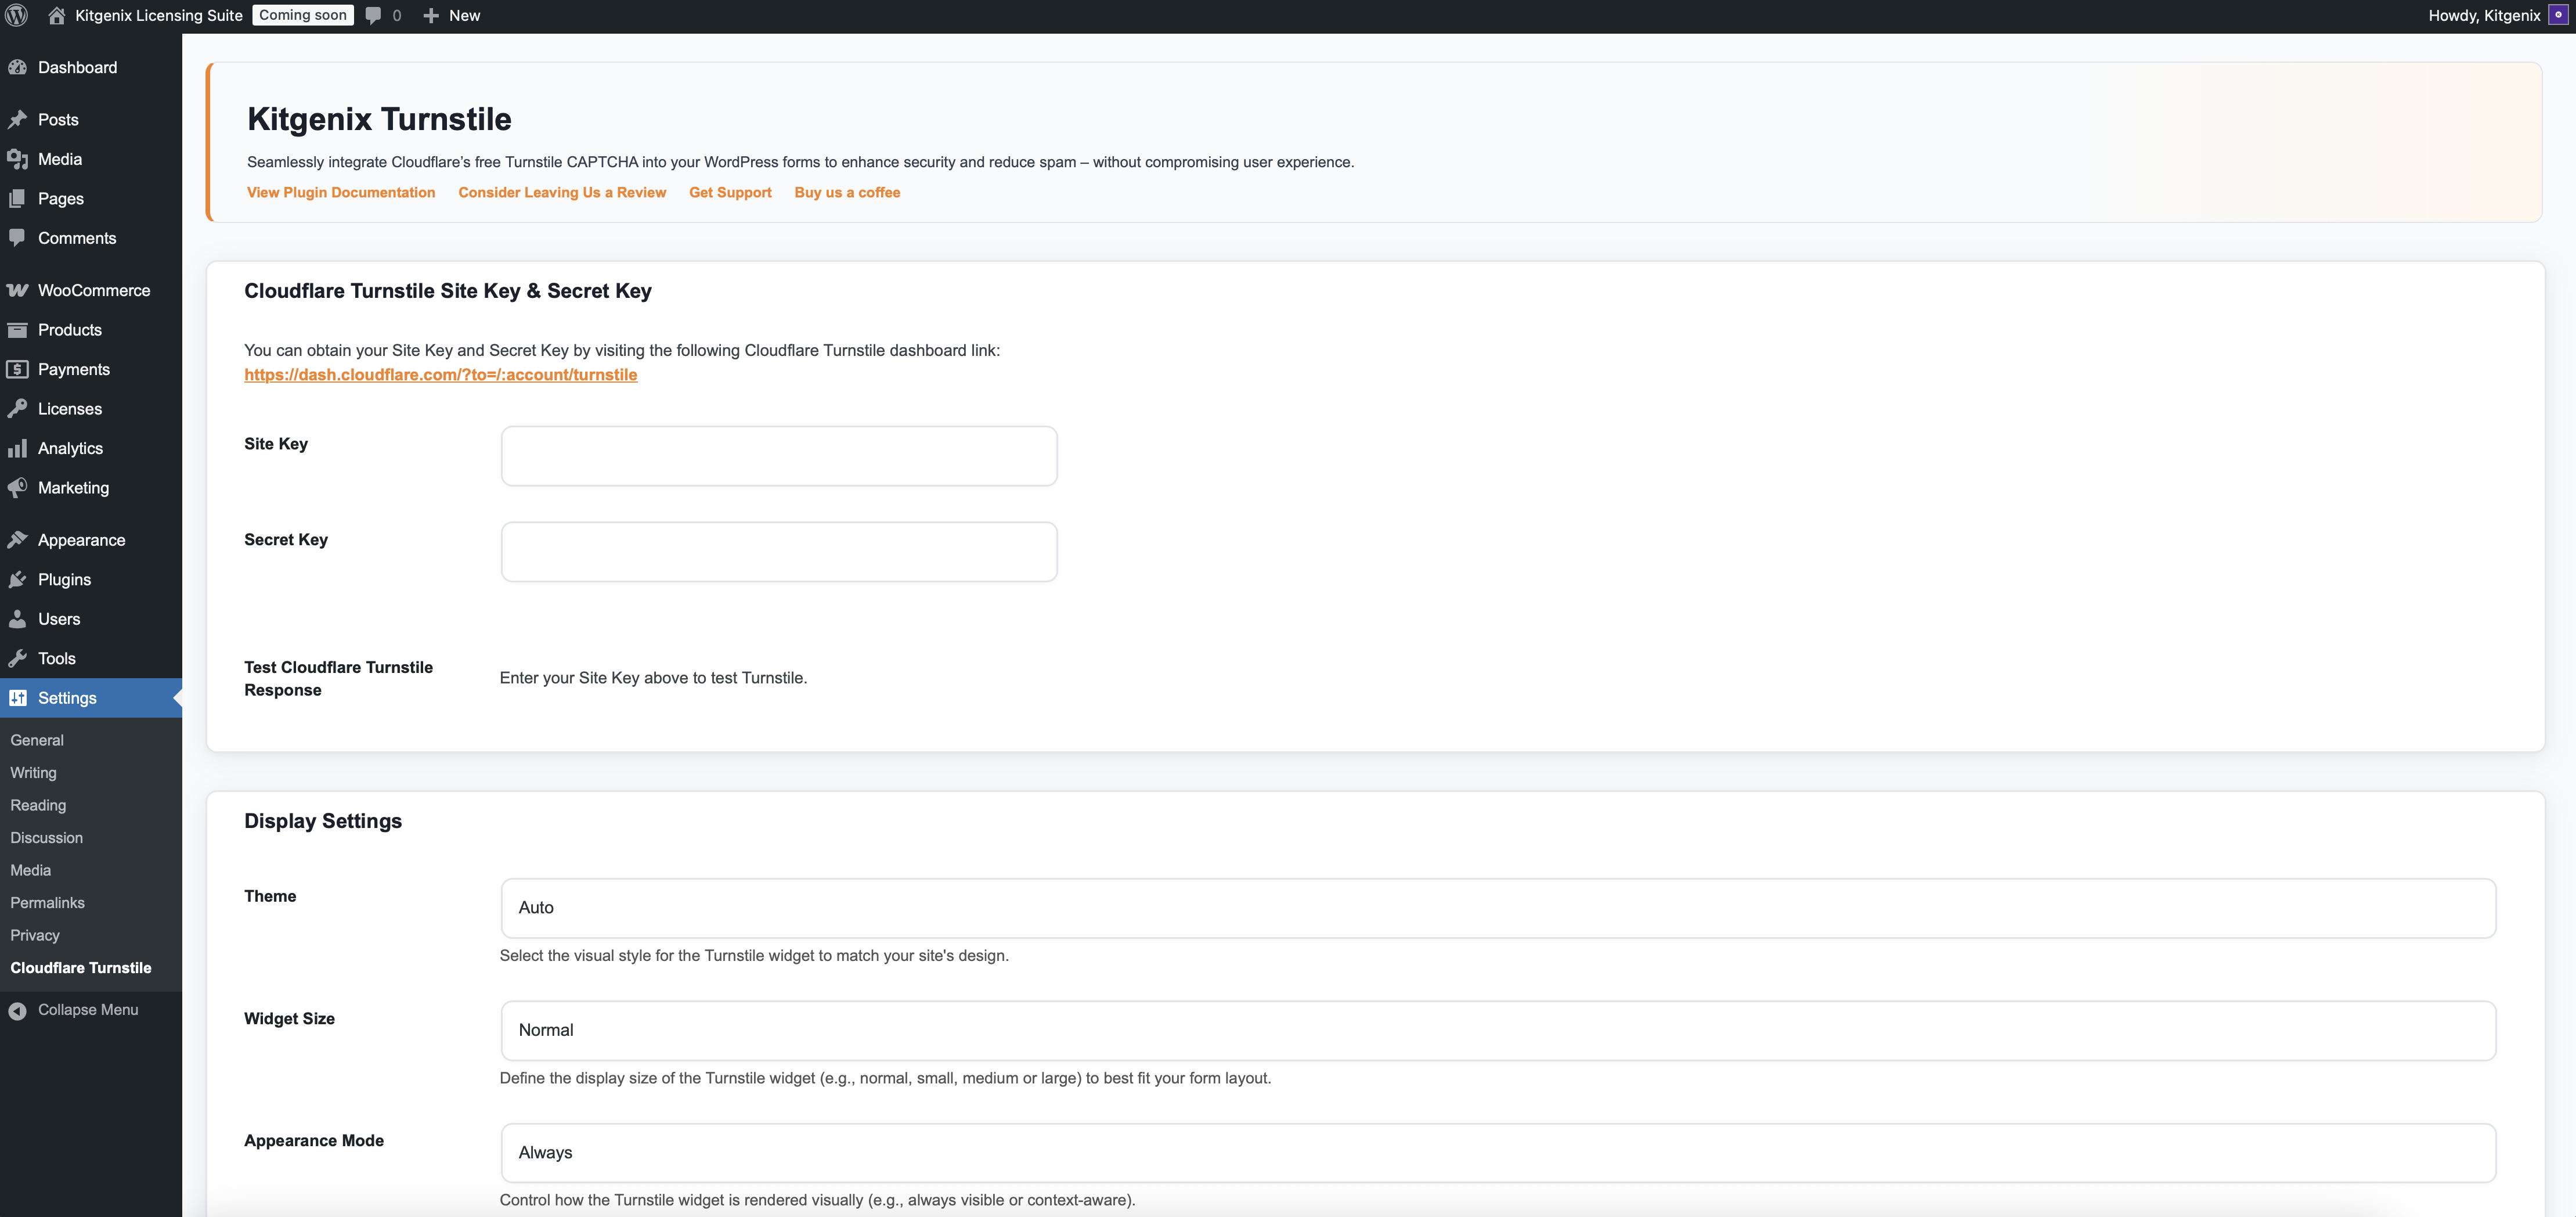
- Create a Turnstile widget in your Cloudflare account and copy its Site Key and Secret Key.
- Open the plugin settings from the Kitgenix menu in wp-admin.
- Enter the Site Key and Secret Key and run the setup verification test.
- Enable only the integrations and forms you want to protect.
- Test the protected forms while logged out and, where relevant, through checkout/account flows.
屏幕截图:


常见问题:
What is Cloudflare Turnstile?
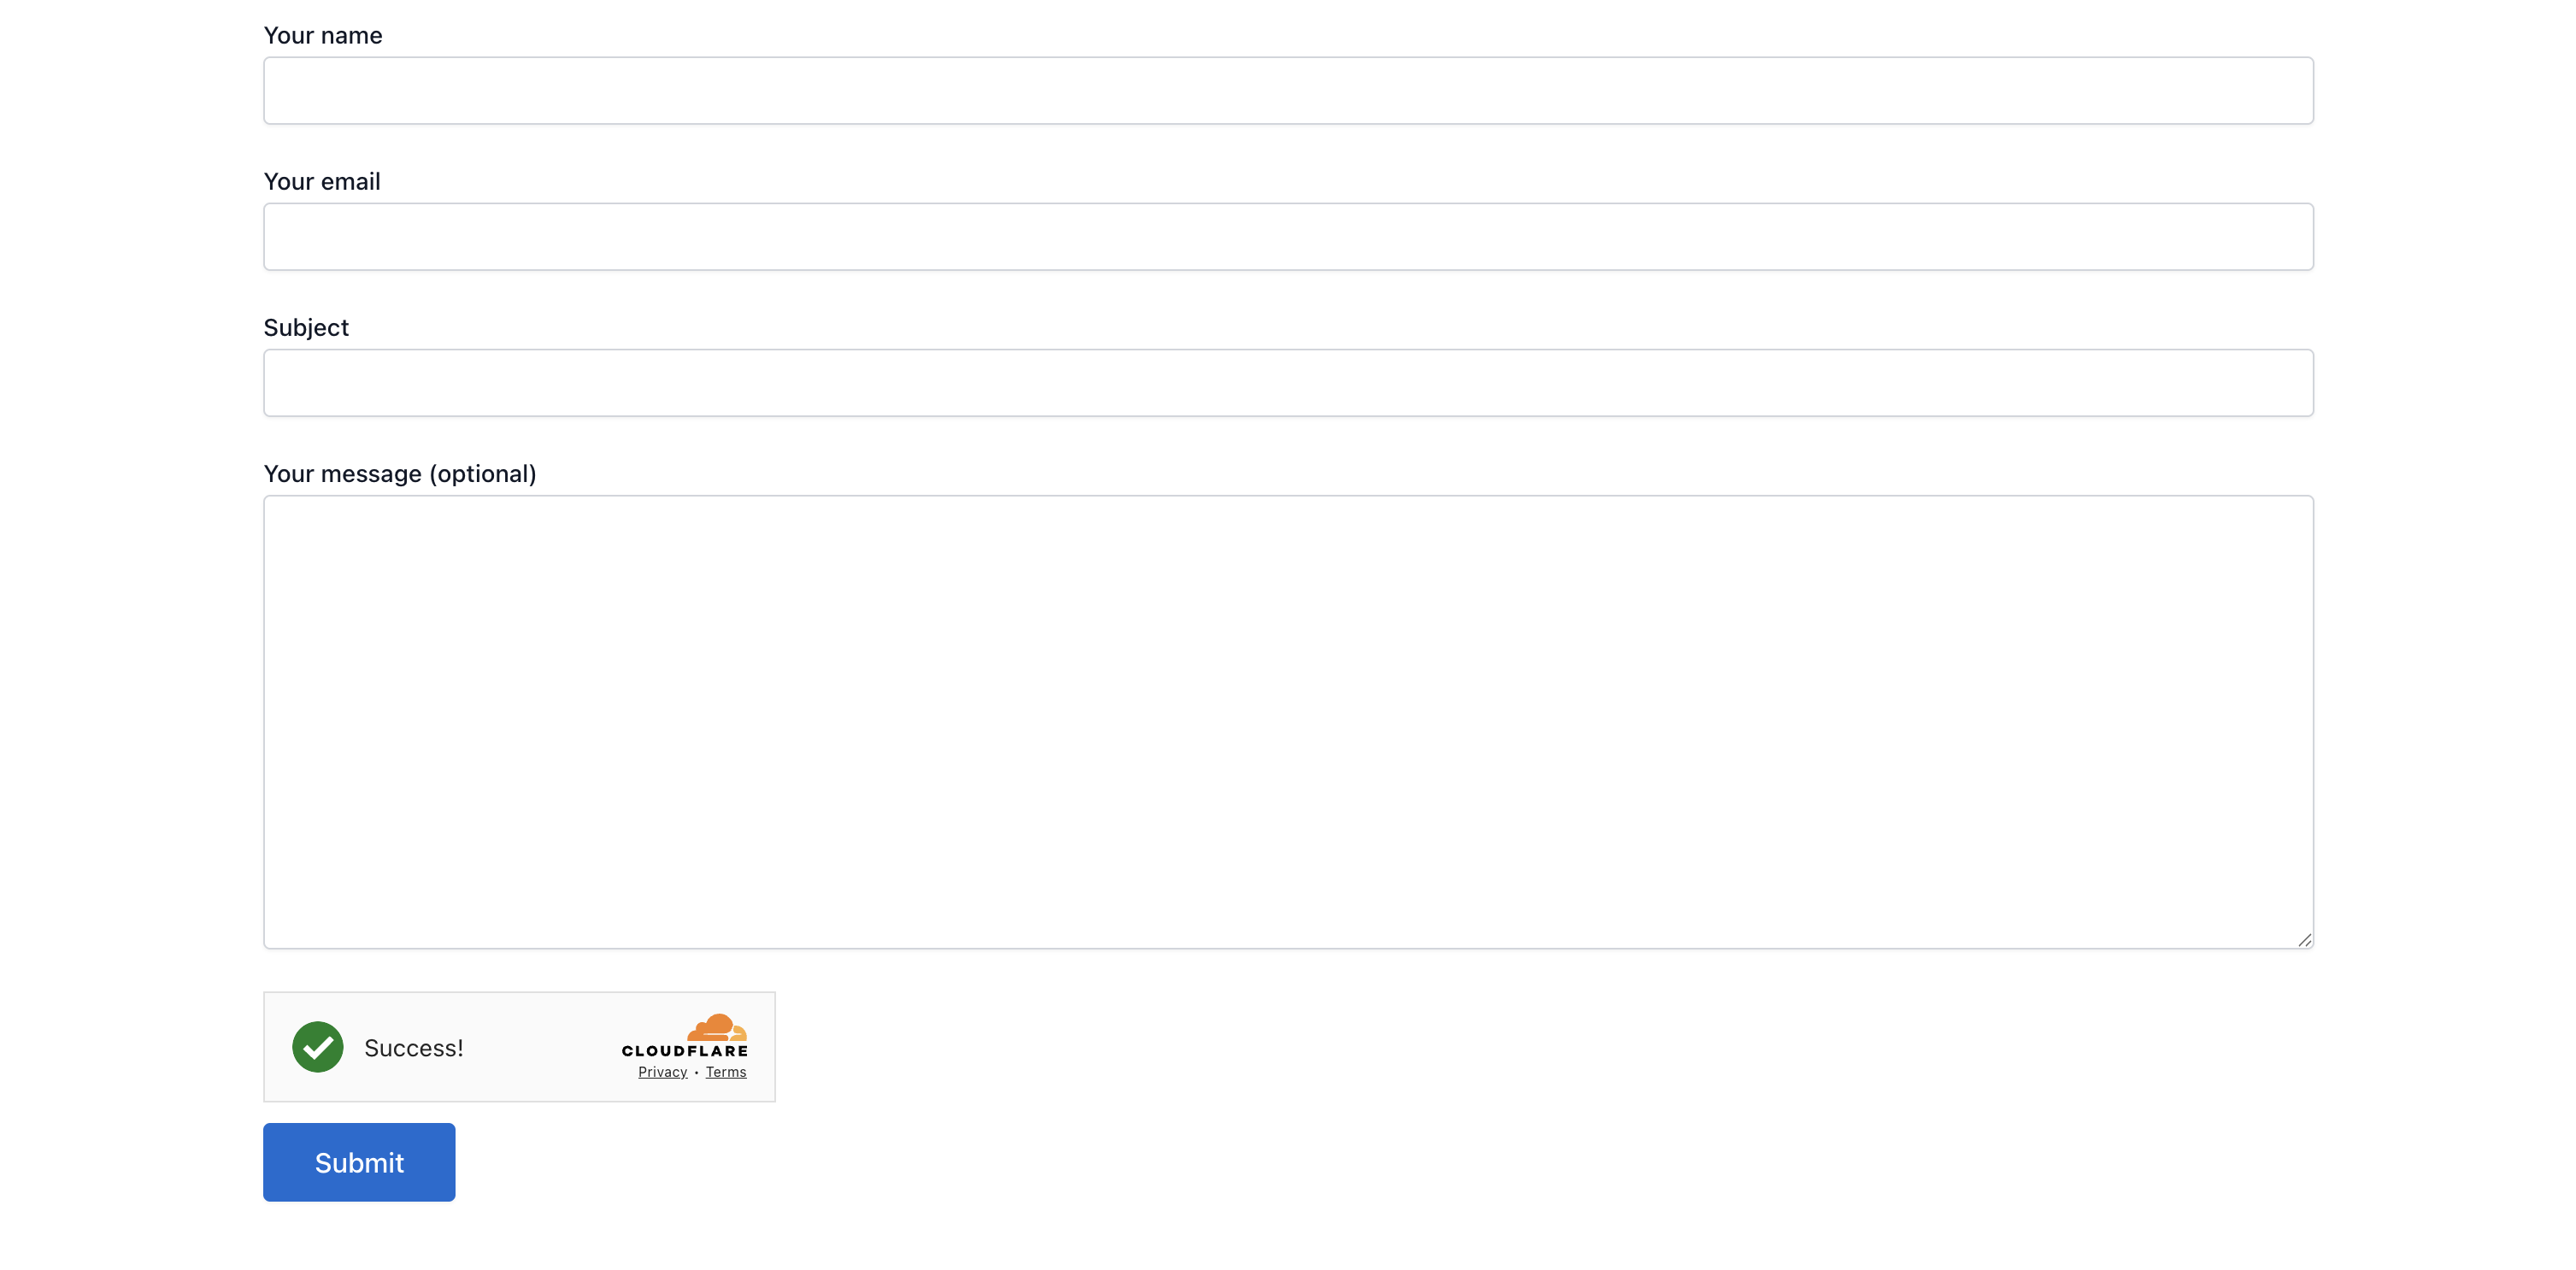
Cloudflare Turnstile is a CAPTCHA alternative that runs a challenge in the visitor's browser and produces a token. The token must then be validated server-side before the protected action is accepted.
Do I need to use Cloudflare DNS or the Cloudflare CDN?
No. Turnstile can be used on a WordPress site even when the site's traffic is not proxied through Cloudflare.
Do I need a Cloudflare account?
Yes. You need a Cloudflare account and a Turnstile Site Key / Secret Key pair.
Does the plugin verify Turnstile on the server?
Yes. Supported integrations validate the token with Cloudflare's Siteverify endpoint before accepting the protected submission, unless Developer Mode or the relevant per-integration Test Mode is intentionally configured to warn rather than block.
Which WordPress forms can it protect?
Native WordPress login, registration, lost/reset password and comment forms are supported. The plugin also supports WooCommerce, Easy Digital Downloads, Elementor Pro Forms, Contact Form 7, WPForms, Fluent Forms, Formidable Forms, Forminator, Gravity Forms, JetFormBuilder, Jetpack Forms, Kadence Forms, Ninja Forms and several membership/community plugins.
Does it support WooCommerce Checkout Blocks?
Yes. The plugin can render Turnstile in block-based checkout and validates the token server-side during the WooCommerce Store API checkout request.
Does it support WooCommerce HPOS?
Yes. The plugin declares HPOS compatibility and uses WooCommerce order CRUD methods for its Checkout Blocks verification metadata.
Can I choose where the Turnstile widget appears?
Yes. Automatic placement is available for supported integrations, and many integrations include a shortcode-only placement option. The [kitgenix_turnstile] shortcode can also render a widget manually.
Can I use the shortcode on any custom form?
The shortcode can render the widget, but an unsupported custom form still needs a server-side validation integration. Rendering a widget alone is not sufficient security.
Can different forms use different Turnstile themes or sizes?
Yes. Global theme, size and language settings can be overridden per integration.
What does Developer Mode do?
Developer Mode is warn-only. Failed verification is recorded but does not block the submission. Individual integrations can also be placed in Test Mode without putting the entire site into warn-only mode.
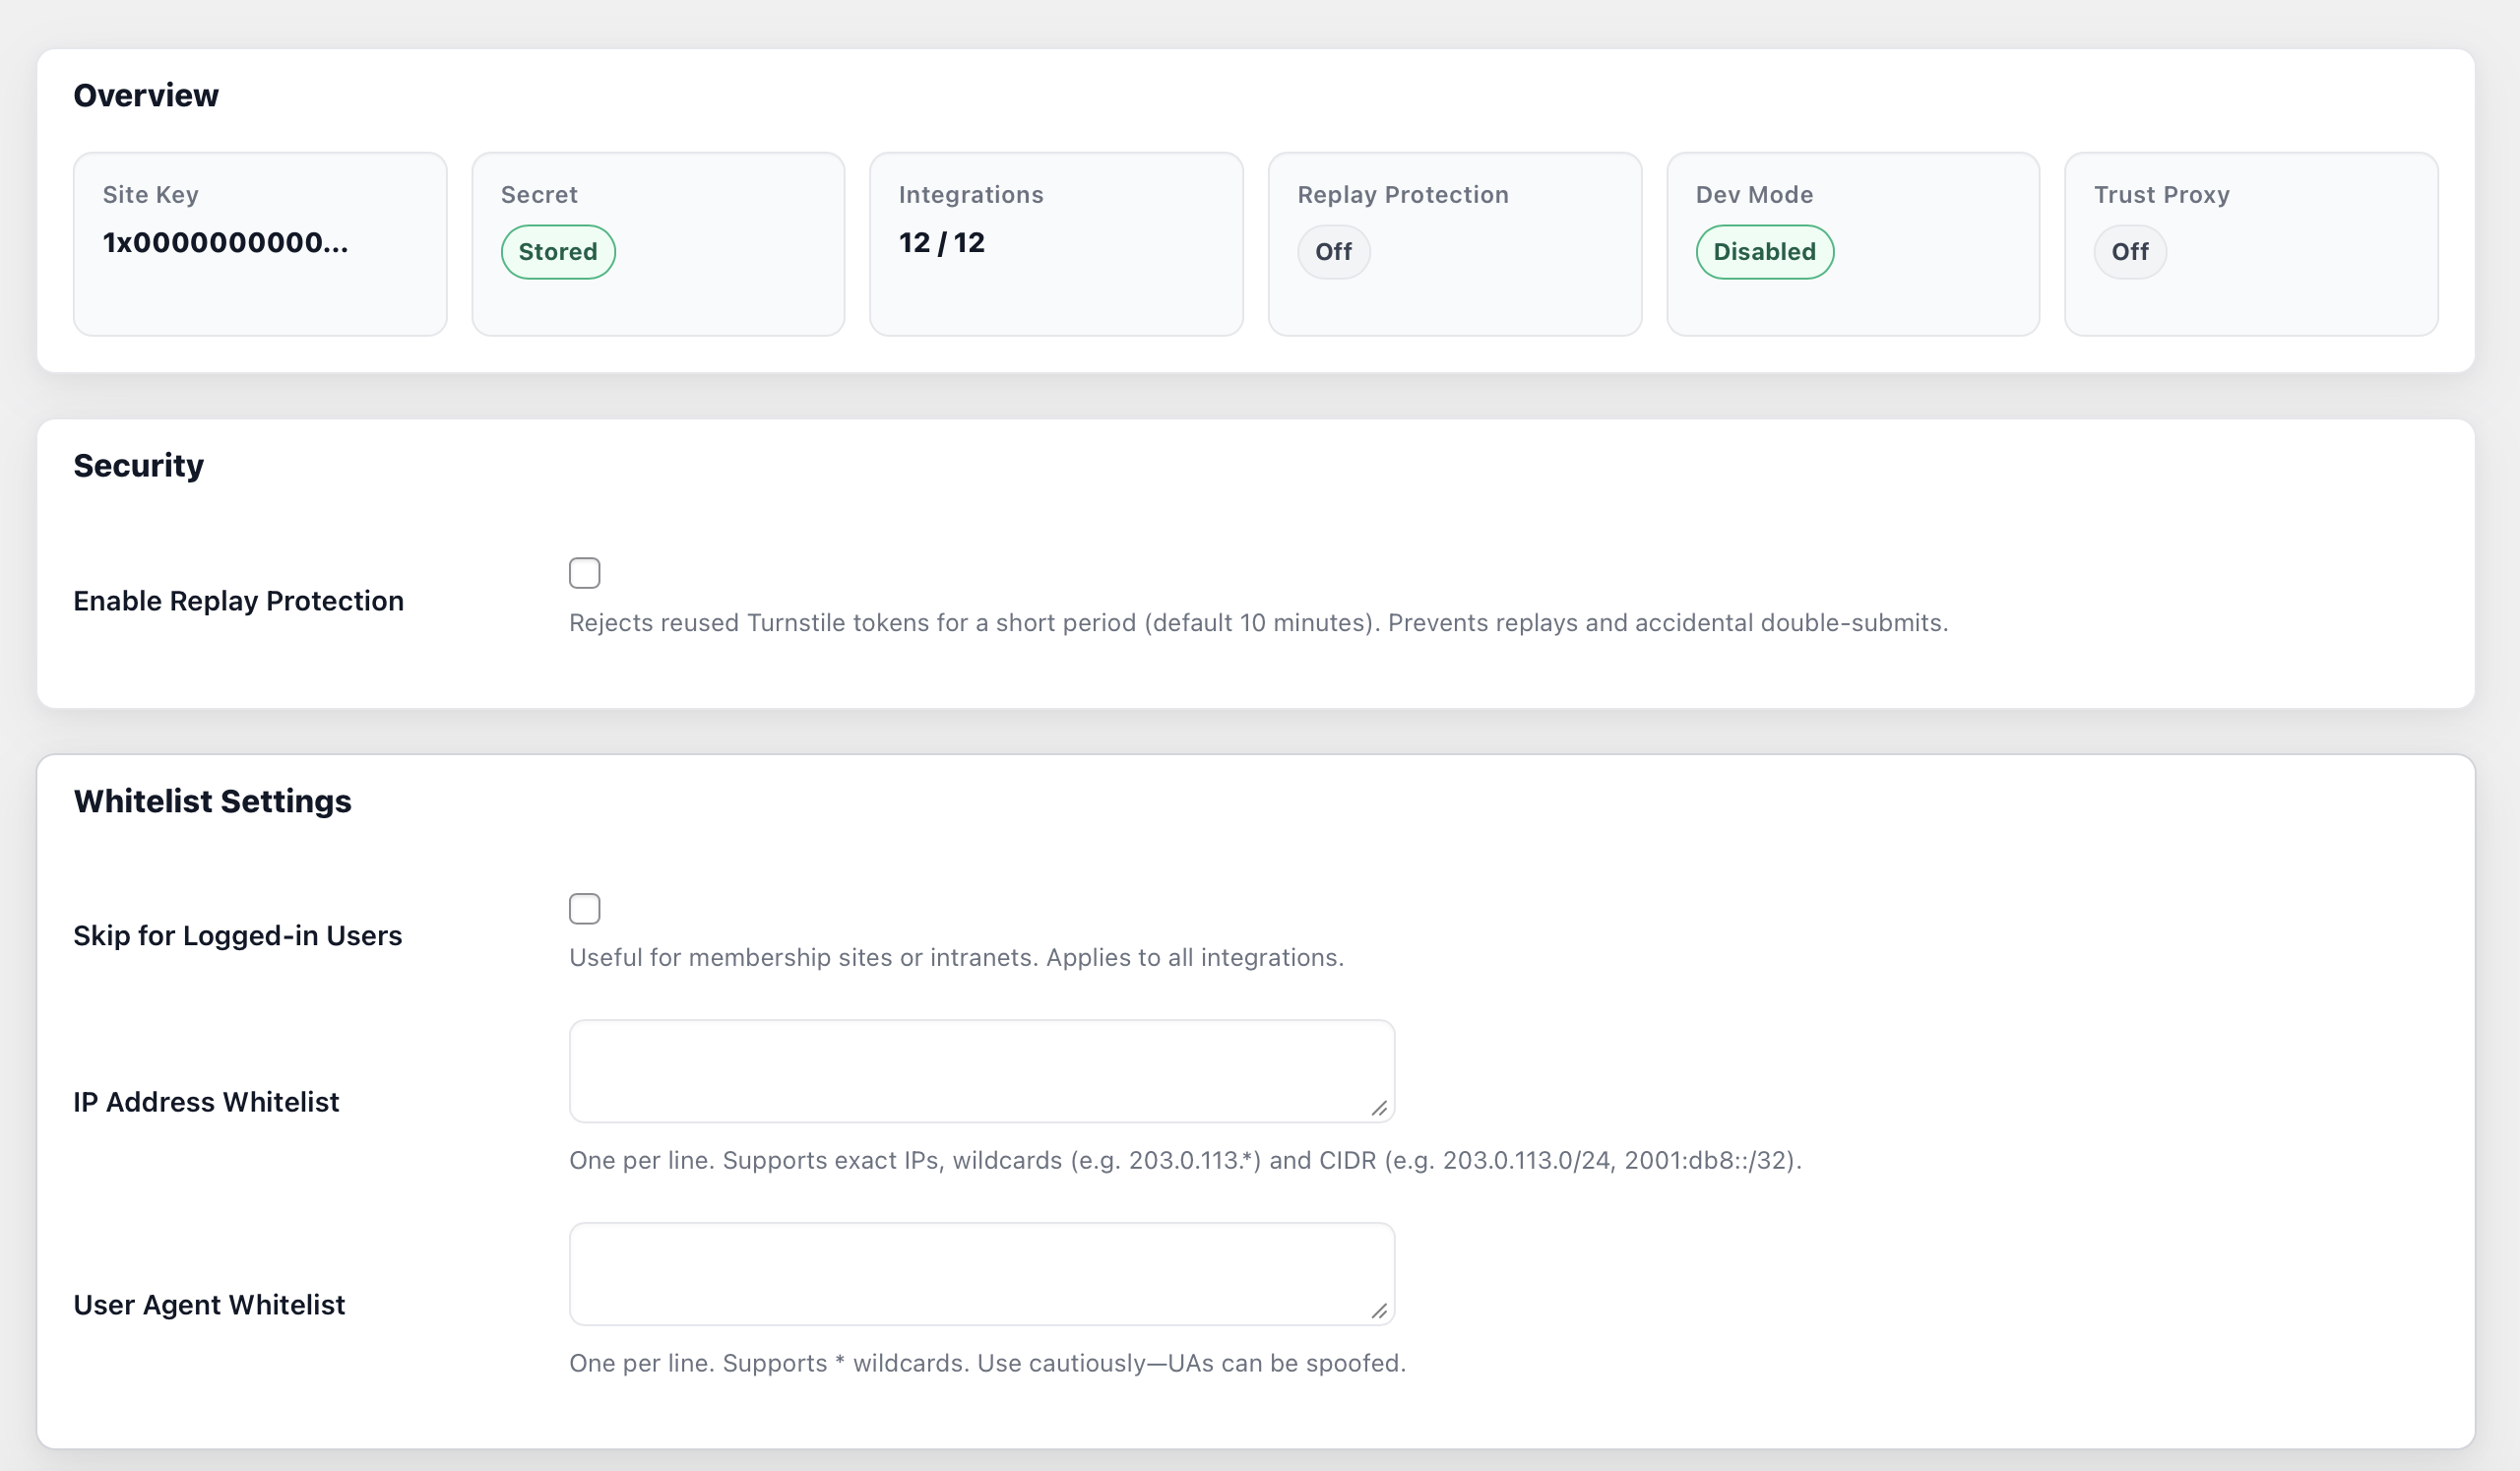
What is replay protection?
Replay protection helps reject a Turnstile token that has already been accepted or processed. This reduces the usefulness of captured or repeatedly submitted tokens.
Does the plugin include a honeypot?
Yes. The optional honeypot can reject simple automated submissions before Cloudflare Siteverify is contacted.
Can I whitelist administrators or trusted visitors?
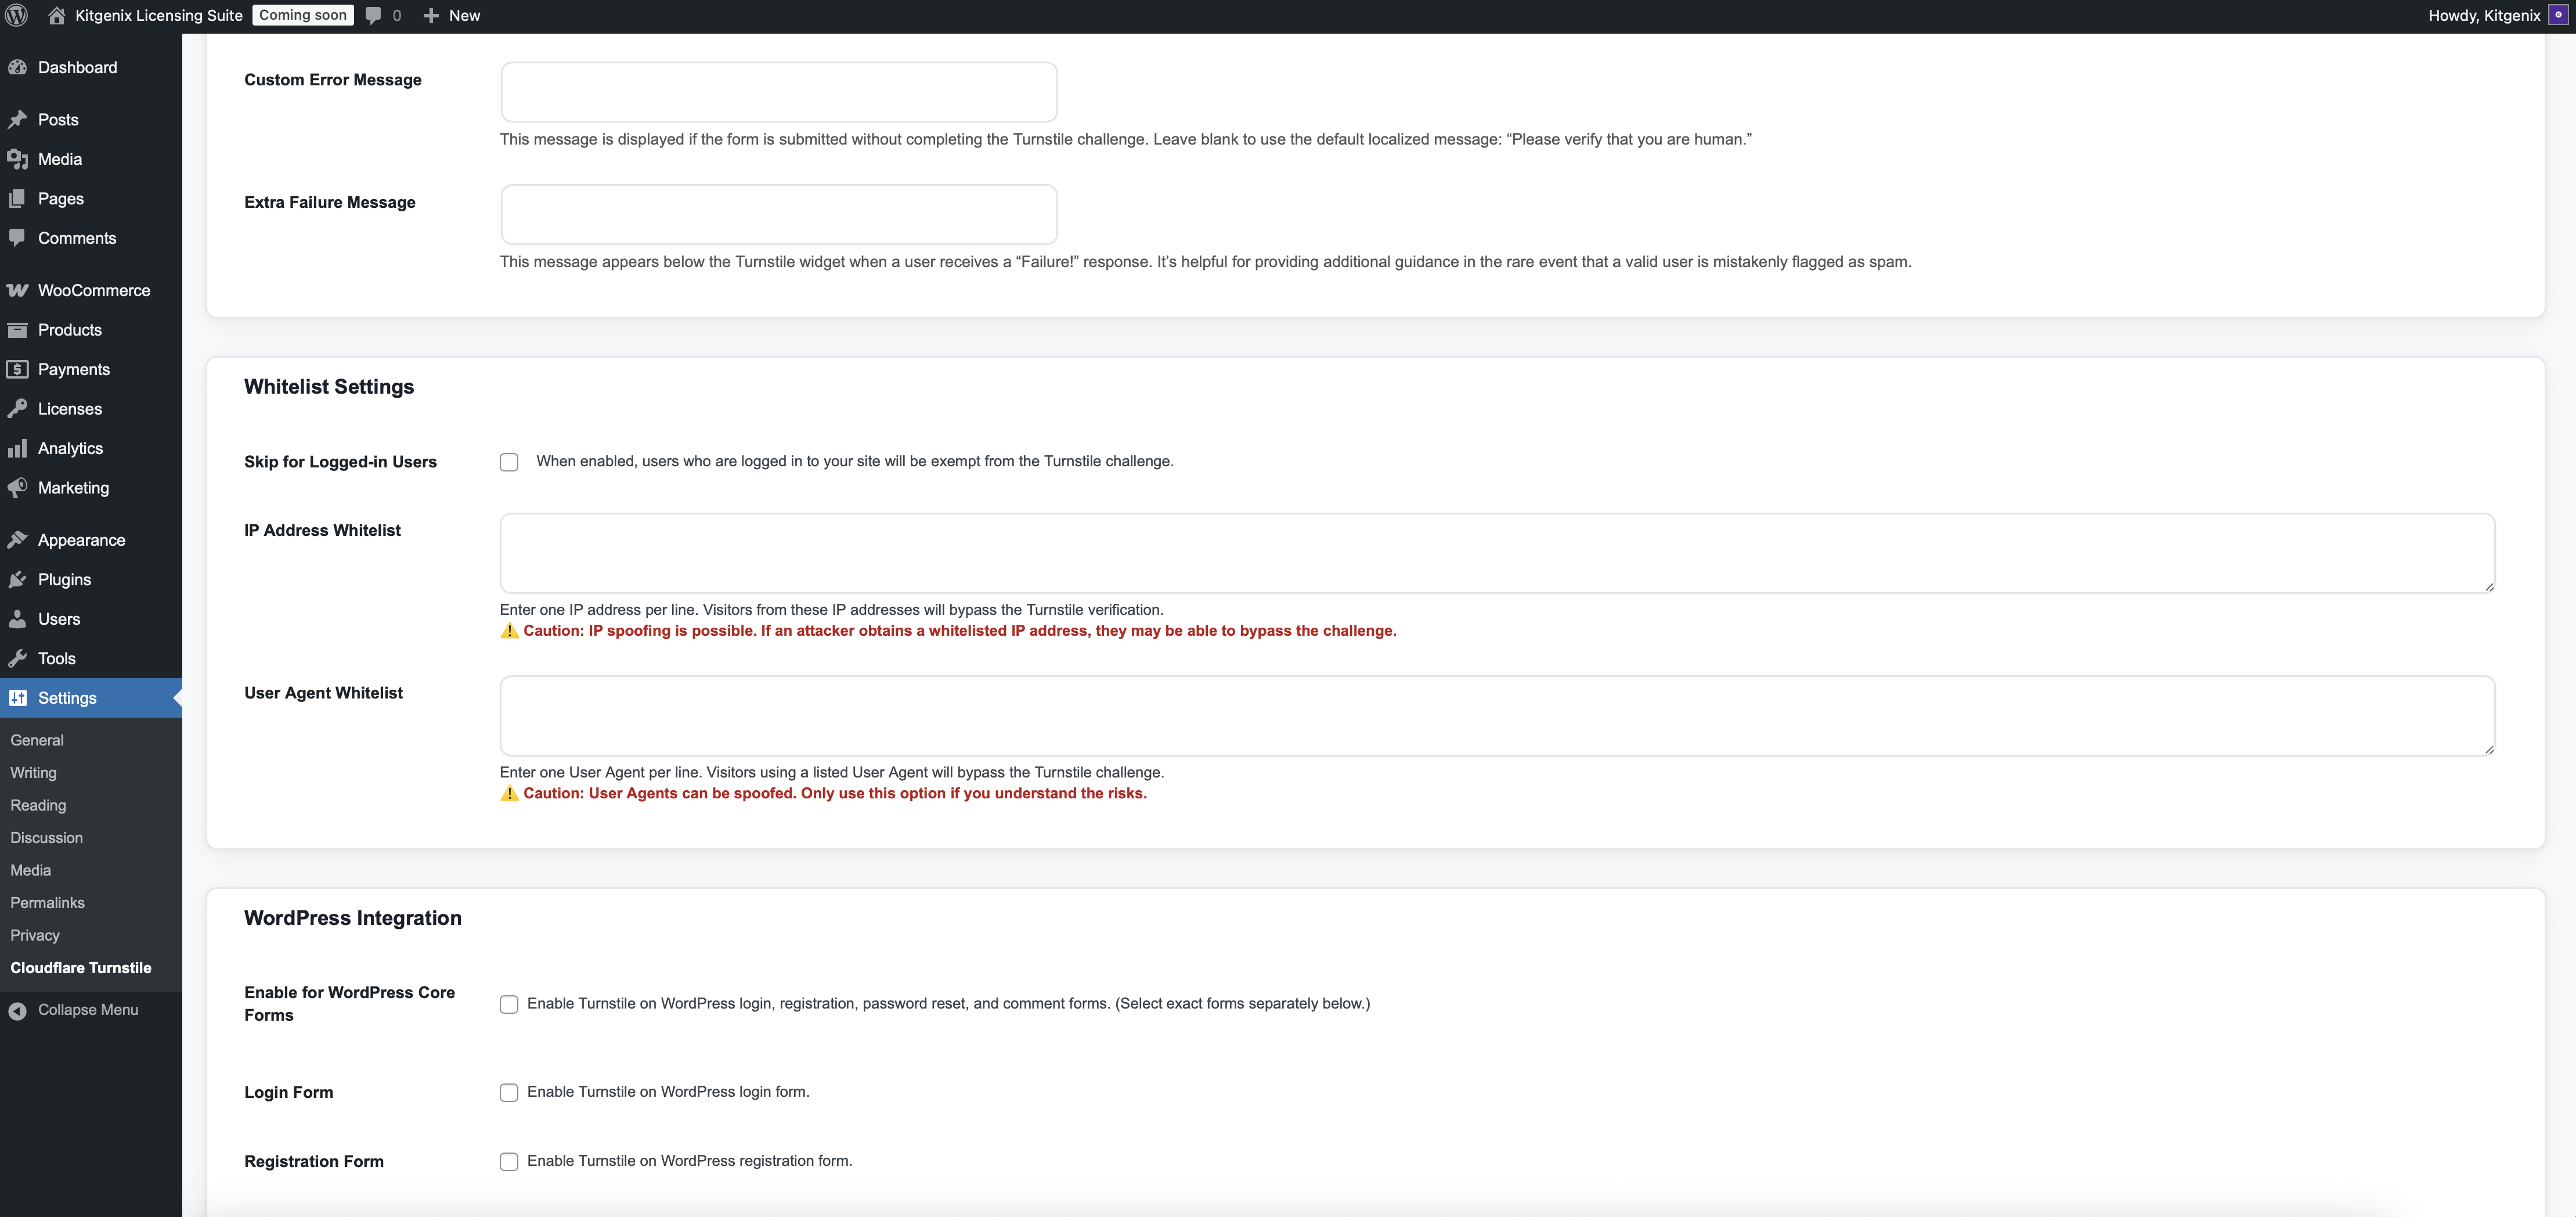
The plugin can whitelist logged-in users, configured IP addresses/ranges and User-Agent strings. Whitelisted visitors do not need to complete Turnstile, and the frontend Turnstile script is skipped for them.
Does it work behind Cloudflare or another reverse proxy?
Yes. Proxy-aware IP detection is included. For security, forwarded headers are trusted only when proxy trust is enabled and the connecting proxy matches your configured trusted proxy list.
Can I stop the visitor IP address being sent to Cloudflare Siteverify?
Developers can return false from the kitgenix_turnstile_send_remoteip filter. See the External Services section for the default data flow.
Can I store the Site Key and Secret Key outside the WordPress database?
Yes. The plugin supports the KITGENIX_CAPTCHA_FOR_CLOUDFLARE_TURNSTILE_SITE_KEY and KITGENIX_CAPTCHA_FOR_CLOUDFLARE_TURNSTILE_SECRET_KEY constants and matching environment variables.
Can I move settings between sites?
Yes. Export settings to JSON and import them using Replace or Merge mode. Credentials are excluded by default unless you explicitly include them.
Why is the widget not appearing?
Check that the Site Key exists, the integration and relevant form toggle are enabled, the visitor is not whitelisted, and another plugin or optimisation rule is not blocking https://challenges.cloudflare.com. Also check the plugin's duplicate-loader warning and Site Health test.
Why do I see expired, missing or replayed-token errors?
Turnstile tokens are short-lived and single-use. Cached forms, back-button resubmissions, double-clicks, delayed JavaScript or submitting after a token has expired can all require a fresh Turnstile challenge.
更新日志:
- New: Added an optional Cloudflare outage failsafe (Settings → Advanced → Reliability, off by default) that independently checks Cloudflare Turnstile's reachability server-side and, once enabled, lets protected forms submit instead of blocking every visitor during a confirmed Cloudflare outage. A visitor cannot trigger this bypass themselves; it only activates when the plugin's own probe confirms Cloudflare is unreachable.
- New: Added a live "Cloudflare outage failsafe is active" alert on the Log tab and in Site Health for as long as the failsafe is bypassing verification, and failsafe bypasses are logged distinctly from genuine Cloudflare-verified passes in the recent events log and per-integration metrics.
- Fix: Resolved an issue where the WooCommerce Blocks Checkout widget could stop rendering after the checkout block re-renders during a normal page load (cart totals, shipping rates and payment methods resolving in sequence). A container that was emptied out by one of these re-renders could be left behind still marked as already rendered, so it silently stayed blank instead of showing the widget. The self-healing recovery logic now recognises a genuinely emptied container and re-renders into it, gated by a grace period so it never interrupts a widget that is still loading or has already been solved.
- Fix: The plugin now properly calls Cloudflare's
turnstile.remove()before clearing and re-rendering any widget container, across every integration (WooCommerce, Elementor, Gravity Forms, Formidable Forms, Forminator, Jetpack Forms, Fluent Forms, Kadence Forms). Previously the container was cleared directly without unregistering the widget first, which could leave a stale widget reference behind and produce "Cannot find Widget" warnings after repeated re-renders. - Fix: The WooCommerce Blocks Checkout container-recovery observer now unregisters a widget from Cloudflare's script when the block's own re-render removes its container from the DOM, instead of leaving an orphaned widget reference behind for the replacement container to collide with.
- Fix: Removed an unnecessary plugin-version query parameter that WordPress's automatic asset versioning was appending to Cloudflare's third-party
api.jsscript URL. Turnstile's own script logged this as an unrecognised parameter; the URL now matches what Cloudflare's CDN expects.
- Fix: Resolved an issue where the WooCommerce Block Checkout widget would not render consistently.
- New: Redesigned the admin settings interface around the shared Kitgenix design system with a sticky topbar, cross-plugin branding, grouped navigation, an Advanced dropdown for Security, Advanced, and Portability, and a light/dark theme toggle that remembers the selected preference.
- New: Added in-page settings search with "/" and Cmd/Ctrl+K keyboard shortcuts, filtering the active tab's cards and rows as you type and displaying a dedicated no-results state when nothing matches.
- New: Added a central Kitgenix Hub page for discovering, installing, activating, and reviewing Kitgenix plugins from one screen, integrated into the same topbar and navigation shell as the plugin settings.
- New: Added a shared Kitgenix component library providing reusable modals, collapsible sections, copy-to-clipboard controls, sortable/searchable tables, and toast notifications.
- New: Added a dedicated Log tab containing active alerts, site-impact statistics, per-integration analytics, and the recent diagnostic log, moving diagnostics out of the Support tab.
- New: Added Ninja Forms integration with Turnstile tokens delivered through a request header rather than a hidden field, matching Ninja Forms' JSON-based submission architecture.
- New: Documented and re-verified the existing Kitgenix Plugin Score integration for login, registration, and forgotten-password protection.
- New: Added per-integration widget overrides for Theme, Widget Size, and Language, allowing individual integrations to override the global display settings or inherit them unchanged.
- New: Added an optional honeypot fallback under Settings → Security that rejects bots which blindly populate hidden fields before any request is sent to Cloudflare's
siteverifyendpoint. - New: Added Test Mode per Integration under Settings → Developer Mode, allowing individual integrations to operate in warn-only mode while the rest of the site remains fully enforced.
- New: Diagnostic log entries now record Cloudflare
siteverifyround-trip latency so slow successful responses can be distinguished from failures and timeouts. - New: Added a Protection Health card to the Log tab with actionable states including Healthy, No recent traffic, High failure rate, Cloudflare unavailable, Duplicate Turnstile loader, and Configuration problem.
- New: Added Integration, Result, Category, and Time Period filters to the recent diagnostic log alongside the existing free-text search.
- New: Renamed the per-integration analytics table to "Integration health matrix" and added each integration's Enabled/Disabled state and Auto/Shortcode injection mode.
- New: Settings imports now provide a client-side preview showing setting-key count, export date, whether Site/Secret keys are included, included settings groups, and plugin-identifier mismatch warnings before Replace or Merge is committed.
- New: On WordPress 7.1 and later, the Kitgenix brand icon is registered with the WordPress Icon Registration API as
kitgenix/markfor discovery throughwp_get_icon()and the icons REST endpoint. - Improved: All settings areas – Site Keys, Display, Integrations, Security, Advanced, and Portability – now use consistent cards, labelled rows, toggle switches, and unified alert components.
- Improved: Refreshed the admin and public-facing Turnstile widget colours from the previous purple palette to the updated Kitgenix blue palette, including light and dark mode variants.
- Improved: The plugin-specific admin stylesheet now builds on the shared Kitgenix admin UI stylesheet for consistent spacing, typography, and component styling.
- Improved: The recent diagnostic log is now displayed as a searchable, paginated table with time, integration, outcome, and a plain-English note instead of a read-only text block.
- Improved: Retained the "Copy recent log" action for quickly copying the raw diagnostic log for troubleshooting or support.
- Improved: Per-integration analytics now supports live search and pagination.
- Improved: The Support tab is now three focused cards – a donate card with a collapsible monthly-amount picker, a "what your support funds" summary, and a "get involved" panel for reviews and plugin links.
- Improved: Stale WordPress security tokens are no longer counted as blocked attempts or included in the failure-spike alert threshold because they represent recoverable session or caching friction rather than genuine security rejections.
- Improved: The replayed-token diagnostic message now explains that the event can result from legitimate actions such as double-clicks or back-button resubmissions as well as malicious replay attempts.
- Improved: Both Turnstile validation entry points now consistently respect site-wide Developer Mode and the new per-integration Test Mode.
- Fix: WooCommerce lost/reset-password protection is now self-contained. Enabling only the WooCommerce lost-password integration now validates its own My Account reset-request form without depending on the separate WordPress Core integration.
- Fix: WooCommerce lost-password validation is scoped to WooCommerce's own form and does not interfere with the native
wp-login.phplost-password flow. - Fix: WooCommerce login verification now runs only once per request when both modern and legacy WooCommerce login-error filters fire, preventing legitimate submissions from being incorrectly rejected as replayed or expired.
- Fix: bbPress forum creation now validates Turnstile exactly once on the correct pre-insert action instead of running a second redundant validation through
bbp_new_forum_pre_insert. - Fix: Removed incorrect handling that could replace bbPress forum post data with an unexpected validation return value.
- Fix: WPForms Turnstile errors now render the actual error message instead of the literal text "Array".
- Fix: The admin language allow-list is now sourced from
Script_Handler::get_allowed_languages()so global and per-integration language settings cannot drift apart. - Fix: Elementor AJAX handling is now scoped to the form that actually submitted a solved Turnstile token instead of affecting every Elementor form on the page.
- Fix: Elementor widgets are now hidden or cleared only after a confirmed successful form submission, preserving the widget after validation failures so visitors can retry.
- Security: Completed a full hook-by-hook enforcement audit of every supported integration to verify that a failed Turnstile check in enforcement mode actually blocks the protected action rather than merely being logged.
- Security: Fixed Contact Form 7 shortcode-only mode so the
wpcf7_validatevalidation filter is always registered. Previously shortcode-only placement could render the widget while allowing submissions to bypass validation completely. - Security: Contact Form 7 shortcode mode now correctly respects the integration's enable/disable setting.
- Security: Removed request-method fail-open checks from Contact Form 7 and Elementor validation. Validation now runs whenever the host plugin invokes the relevant validation hook rather than trusting
$_SERVER['REQUEST_METHOD']as a security boundary. - Security: Fixed Easy Digital Downloads login protection by replacing the nonexistent
edd_process_login_formhook with WordPress's realauthenticatefilter, scoped to EDD login submissions through EDD's own nonce field. - Security: Fixed Fluent Forms enforcement by replacing the nonexistent
fluentform_submit_validationhook with Fluent Forms' actualfluentform/validation_errorsvalidation filter. - Security: Rebuilt Kadence Forms protection against the current Kadence Blocks "Form (Adv)" implementation using
kadence_blocks_advanced_form_submission_reject, replacing dead hooks and an invalid class check that meant validation previously never ran. - Security: Kadence Advanced Form widget injection now uses an appropriate frontend script bridge because the block does not expose a suitable PHP render filter.
- Security: Fixed Ninja Forms token delivery by attaching the token to the relevant AJAX request header rather than inserting a hidden DOM field that Ninja Forms never included in its JSON submission payload.
- Security: Ninja Forms failed Turnstile checks now terminate the submission request directly instead of writing to an error-array structure that Ninja Forms does not consult.
- Security:
Turnstile_Validator::validate_token()now respects site-wide Developer Mode and per-integration Test Mode consistently withis_valid_submission(). - Security: Confirmed diagnostic and analytics CSV exports do not introduce spreadsheet formula/DDE injection because they contain plugin-generated labels and counters rather than raw user-submitted form values.
- Security: Confirmed settings exports continue to exclude the Site Key and Secret Key unless an administrator explicitly opts to include them.
- Security: Re-verified trusted-proxy client IP resolution against spoofed proxy headers and out-of-range CIDRs.
- Security: Proxy headers including
CF-Connecting-IP,True-Client-IP,X-Forwarded-For, andX-Real-IPare only trusted whenREMOTE_ADDRmatches an administrator-configured trusted proxy address or CIDR. - Security: Client IP values extracted from trusted proxy headers must be valid public addresses; private and reserved addresses are rejected.
- Performance: Frontend Turnstile script loading remains unchanged. Cloudflare
api.jscontinues to load once and only when a widget will actually render for the current visitor. - Performance: Whitelisted requests continue to skip Turnstile frontend script loading entirely.
- Performance: The existing duplicate Turnstile loader detector remains unchanged.
- Compatibility: Confirmed compatibility with WordPress 7.1.
- Compatibility: Declared WooCommerce High-Performance Order Storage (HPOS /
custom_order_tables) compatibility. - Compatibility: Re-verified that Checkout Blocks order verification metadata uses WooCommerce's
WC_OrderCRUD API throughupdate_meta_data()andsave()rather than direct database access. - Compatibility: Verified WooCommerce 11.x compatibility across Classic Checkout, Checkout Blocks/Store API, and WooCommerce My Account login, registration, and lost-password flows against current WooCommerce source.
- Dev: Added
Turnstile_Validator::get_all_integration_keys()as the canonical list of integrations eligible for Test Mode and per-integration settings, sourced consistently withget_integration_label(). - Dev: Updated Kitgenix logo and favicon filenames and references throughout the plugin and Kitgenix Hub to use the shared brand asset set.
- Dev: Refreshed the Kitgenix Hub plugin directory listing, including the renamed MultiStore for WooCommerce entry and the new Image Optimizer listing.
- Dev: Added automated tests covering enforcement regressions discovered during the integration audit.
- Dev: Added automated tests covering spoofed trusted-proxy headers and out-of-range CIDR scenarios.
- Documentation: Documented the Kitgenix Plugin Score integration in the readme for the first time.
- Documentation: Expanded the changelog to distinguish security-sensitive enforcement fixes from general bug fixes.
- Documentation: Documented the previously undocumented
kitgenix_turnstile_skip_wp_login_validationfilter under Developers → Filters.