
Nexora Engine
| 开发者 | auralogics |
|---|---|
| 更新时间 | 2026年9月18日 20:35 |
| PHP版本: | 8.0 及以上 |
| WordPress版本: | 7.1 |
| 版权: | GPLv2 or later |
| 版权网址: | 版权信息 |
详情介绍:
advanced-cache.php before WordPress boots, achieving 22ms TTFB on any shared host (Apache, Nginx, LiteSpeed, IIS). Zero PHP execution on cache hits.
Ghost Protocol
Strips every WordPress fingerprint from HTML, headers, and JavaScript. Generator meta tags, REST API discovery links, window.wp, and X-Powered-By: PHP are all removed or rewritten. Wappalyzer reports Nginx, not WordPress.
Intelligent Automation
Content changes trigger selective snapshot regeneration, so only affected pages rebuild, with a 30-second debounce to coalesce bulk edits. Asset references are validated before serving.
Free Features
- Static HTML delivery with universal drop-in cache
- SPA client-side navigation between static pages
- Elementor & Gutenberg compatibility
- Delivery diagnostics (SSG status, serve-rule checker)
- Cache hit tracking and basic analytics
- Security hardening: REST user-enumeration block, author-enumeration block, XML-RPC disable, WordPress version removal, masked login errors
- Ghost Protocol WP masking: removes generator tags, REST discovery links and other WordPress signals from every response
- XML sitemap and the SEO & Metadata report There is no page limit, no time limit, and no feature that stops working. Every page on your site can be served statically on the free version, for as long as you use it.
- Advanced Ghost Protocol: Stealth Proxy asset-path rewriting and JS namespace cloaking
- Smart automation: auto-rebuild on publish/update, debounced regeneration, conflict detection
- Scheduled regeneration cron
- Core Web Vitals tracking (LCP, INP, CLS) from real-user field data
- SEO intelligence and on-page scoring
- PDF infrastructure reports
- Edge CDN purge for Cloudflare and Bunny
- White-label admin branding
- Portal connectivity for auralogicslabs.com/portal
- Multisite fleet orchestration: network-wide SSG enable/disable and fleet dashboard
- Analytics are opt-in: disabled by default on new installs (see Settings → Neural Pulse)
- IP addresses are hashed before storage (SHA-256 with a per-site salt, non-reversible) and the raw address is never written to disk
- No data is sent to external servers without explicit user action
- No obfuscated code. Full GPL source.
- Cleanup on deletion: removes the plugin's options, database tables, post and user meta, scheduled events, and the cache drop-in. The generated static files in /wp-content/uploads/nexora-static/ are kept, since they are your rendered content; delete them from Tools before removing the plugin if you want them gone.
安装:
- Upload the plugin folder to
/wp-content/plugins/nexora-engine/. - Activate Nexora Engine through the Plugins menu in WordPress.
- The Setup Wizard will launch automatically on first activation.
- Follow the wizard: enable Static Delivery, install the drop-in cache, and verify the setup.
屏幕截图:
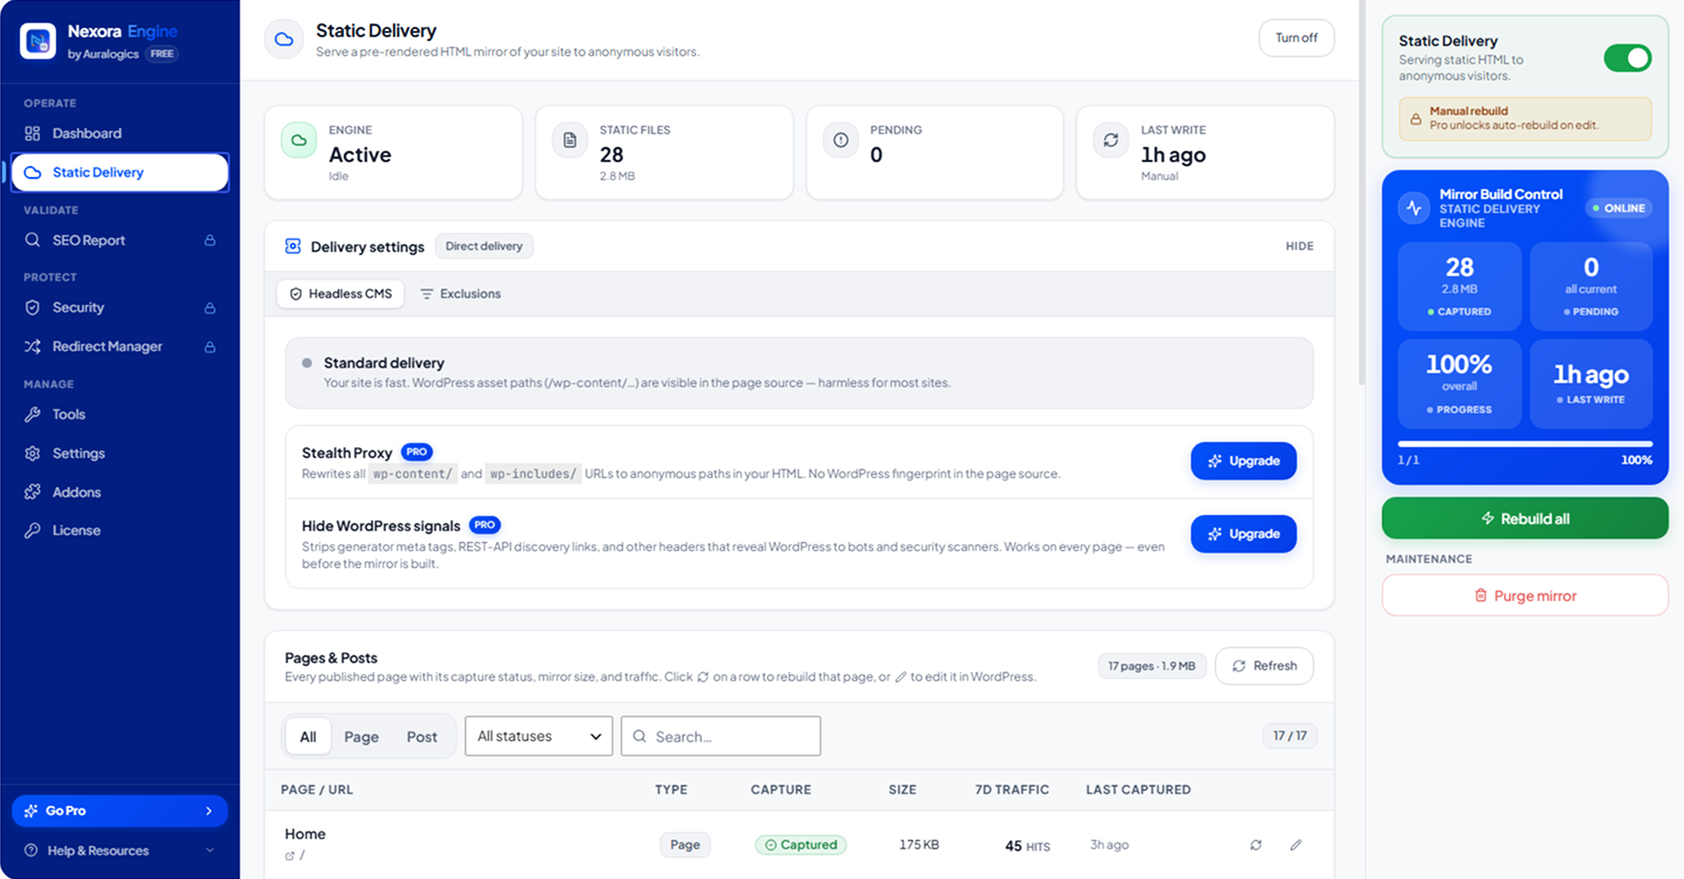
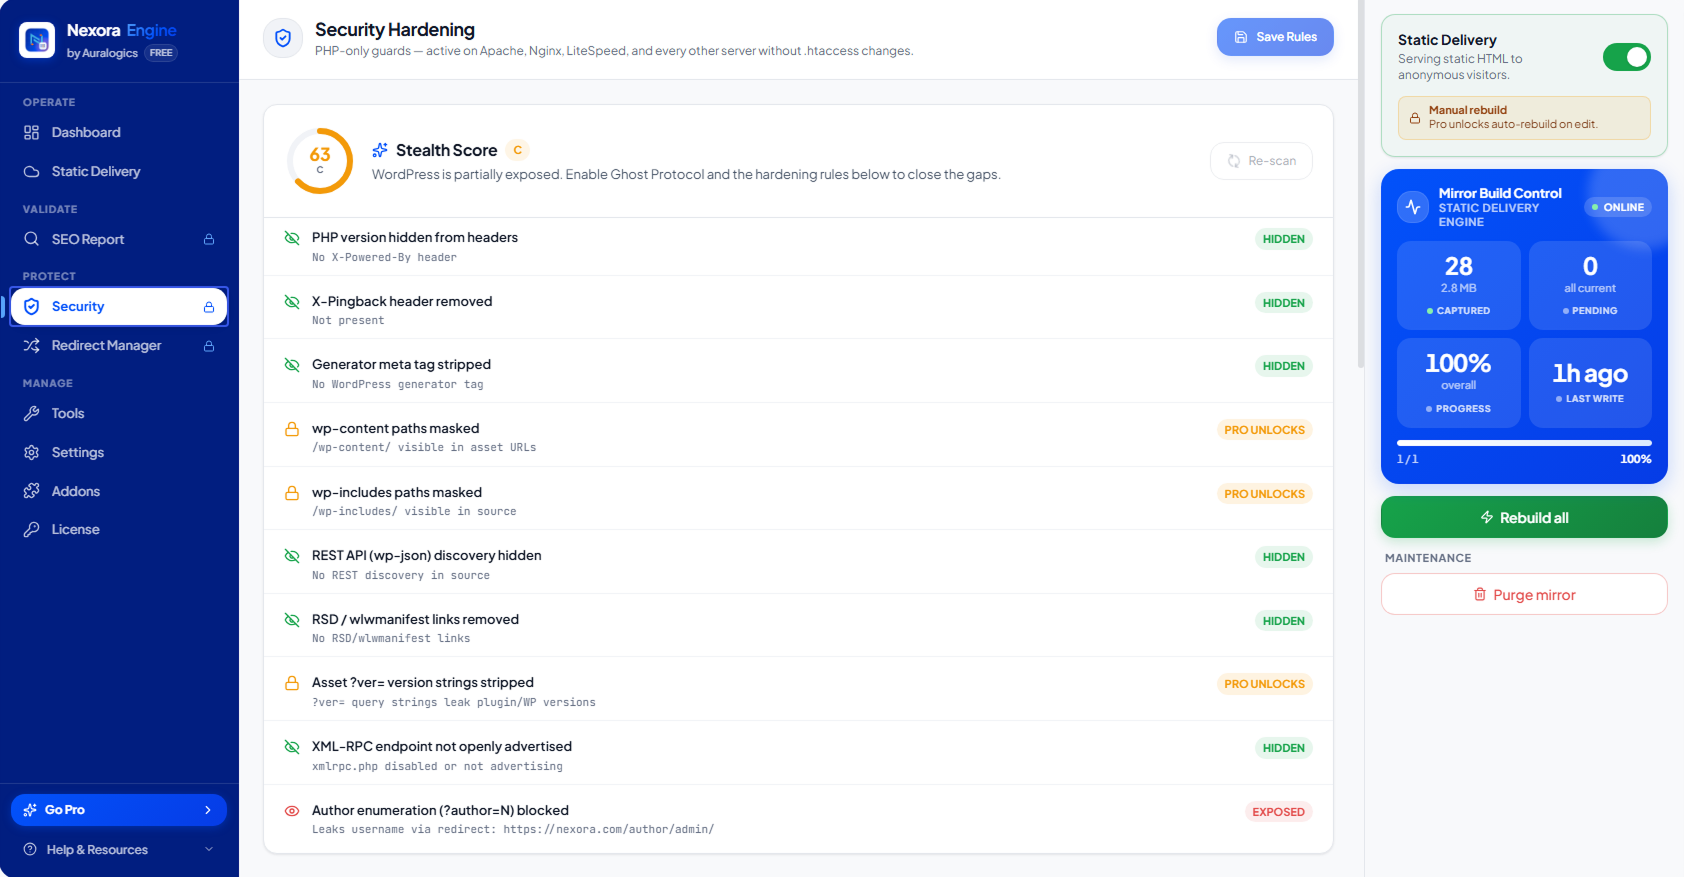
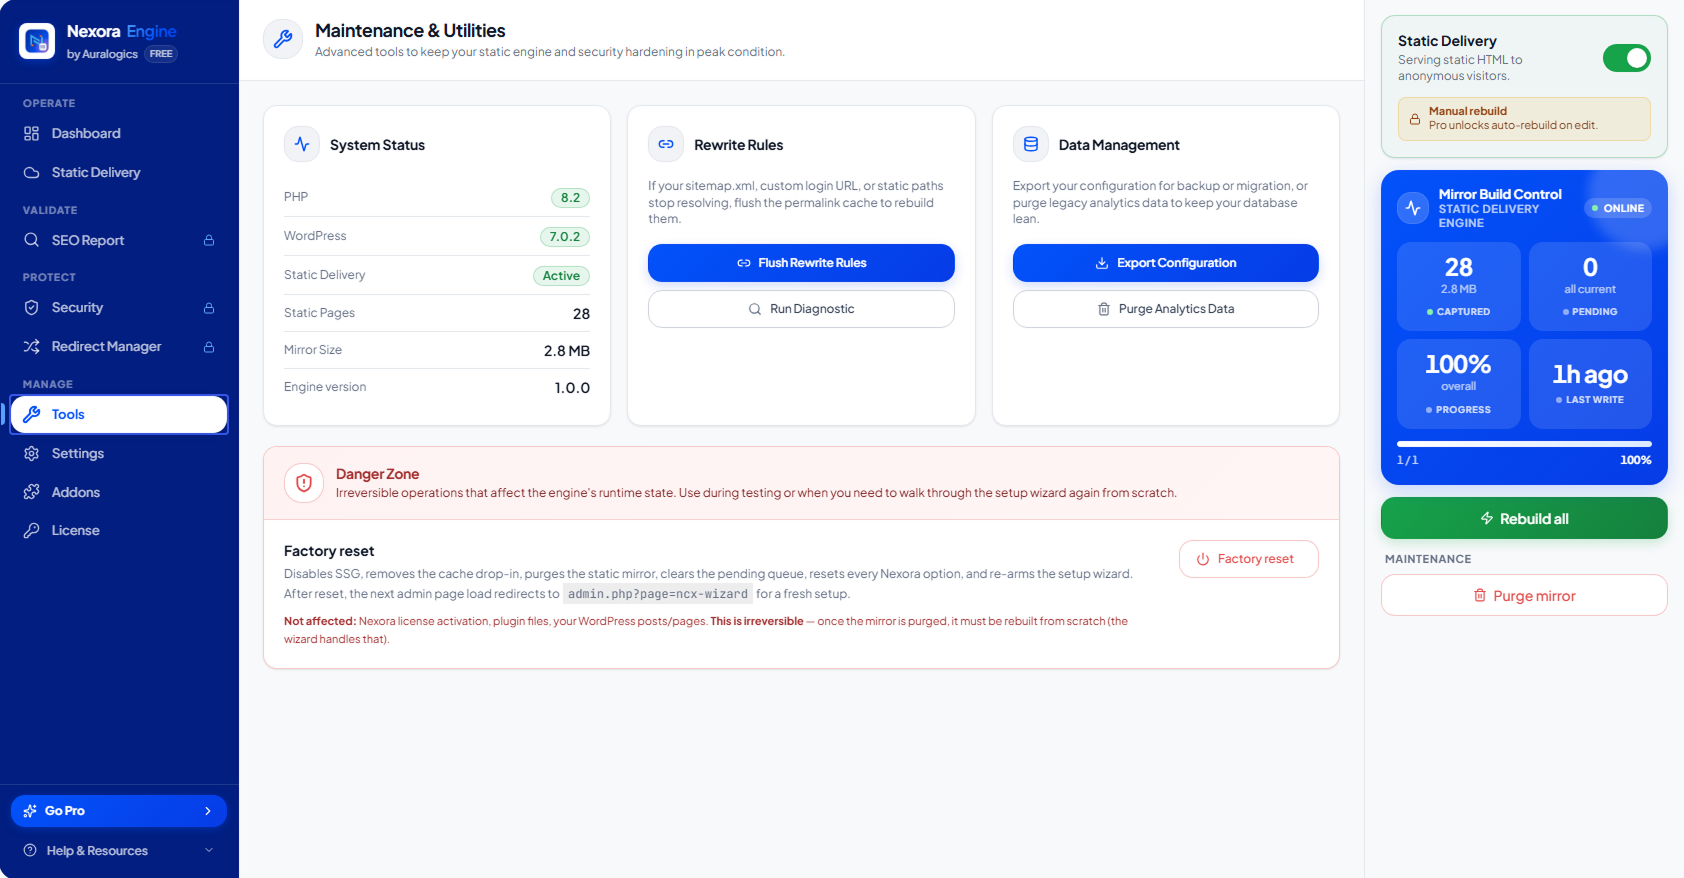
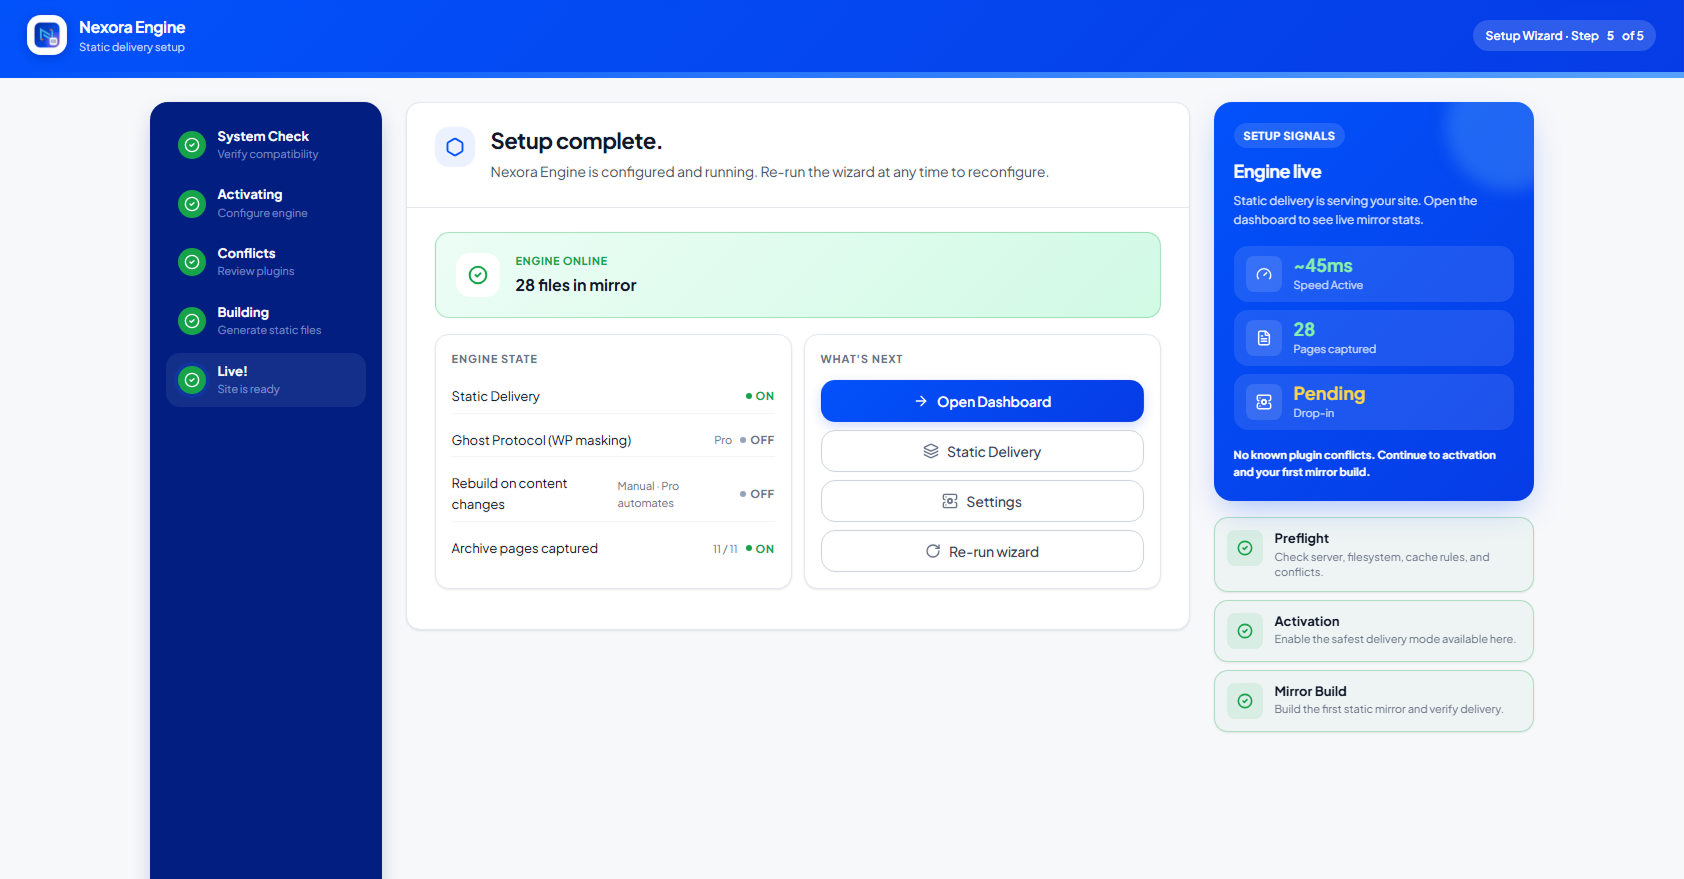
常见问题:
Does this replace my theme?
No. Nexora Engine sits on top of WordPress. Your theme, Elementor layouts, Gutenberg blocks, and page builders are unchanged; the plugin just captures their output as static HTML.
Do I need a separate Node.js server?
No. Static files are served directly from wp-content/uploads/nexora-static/ via advanced-cache.php or Apache/Nginx rewrites. No external server required.
Is it compatible with Elementor, Divi, and WPBakery?
Yes. Nexora Engine captures the rendered HTML output after page builders run. Editor experience is completely unchanged.
When I edit a page, post, category, or tag, does the static mirror update automatically?
On the free version, any change to a page, post, or public category/tag is tracked and the affected pages are added to a Pending list. You rebuild the mirror with one click from the Static Delivery screen (or the "Build pending" button), keeping you fully in control of when the static site refreshes. The Pro version adds automatic rebuild on publish/update, so every change is mirrored in the background with no manual step.
Is the free version limited in how many pages it can serve?
No. The free version has no page cap, no time limit, and no trial period. Every page on your site can be served statically, indefinitely. What Pro adds is automation and scale: rebuilds happen by themselves on publish, asset paths are cloaked, metadata is editable per page, and multisite networks are managed centrally. A small site is well served by the free version for as long as it stays small; a site that publishes daily is where the automation starts paying for itself. If a limit is ever introduced on the free tier, it will be stated in this readme before it ships, never discovered by running into it.
What happens if I deactivate the plugin?
On deactivation, the advanced-cache.php drop-in is removed and all WordPress rewrite rules are flushed. Your site returns to normal PHP rendering instantly.
更新日志:
- Fixed: upgrading to the Pro build could fail with a PHP fatal error and leave the upgrade unapplied. The free build now loads safely alongside the Pro build during the changeover, so the switch completes cleanly. The site itself was never affected, the upgrade simply did not apply.
- Fixed: two internal redeclaration guards checked for the wrong function name and never took effect.
- Fixed: the plugin constants are now defined only once, removing PHP warnings when two builds are briefly loaded together.
- Fixed: upgrade links in the dashboard, headless, redirects and security screens pointed at a page that no longer exists. They now open the correct pricing page.
- Fixed: the Setup Wizard upgrade button bypassed the plugin pricing resolver and could open a page that is intentionally disabled.
- Static HTML delivery: pre-rendered page snapshots served from a universal
advanced-cache.phpdrop-in before WordPress boots, for fast time-to-first-byte on any host (Apache, Nginx, LiteSpeed, IIS). - SPA-style client navigation between static pages, with full Elementor and Gutenberg compatibility. Your theme and page builders are captured exactly as rendered.
- Setup Wizard: one-click guided setup that enables static delivery, installs the drop-in, builds the first mirror, and verifies serving.
- Mirror Build Control: build, pause, resume, and refresh changed pages, with live progress and clear per-page error reporting.
- Delivery diagnostics: SSG status, serve-rule checker, and a self-test so you can confirm static delivery is active.
- Ghost Protocol WP masking: removes WordPress fingerprints (generator meta tags, version strings, and REST API discovery links) from every response, not just the static output.
- Security hardening (free): block REST and URL user enumeration, disable XML-RPC, remove the WordPress version string, and basic login protection.
- Cache hit tracking and basic delivery analytics (opt-in). Visitor IP addresses are hashed with SHA-256 and a per-site salt at the moment of capture; the raw address is never written to disk.
- WooCommerce-aware: cart, checkout, and account pages are automatically excluded from static capture.
- Optional revalidation webhook to notify an external host/front end when a page changes.
- Deleting the plugin removes the drop-in, flushes rewrite rules, and cleans up all plugin data: options, transients, database tables, scheduled events, and the plugin's own post and user meta. Meta belonging to other plugins is never touched.
- Admin interface fonts are bundled with the plugin and served from your own site. No request is made to any font CDN. The Pro version adds Stealth Proxy asset cloaking, smart auto-rebuild on publish, per-page SEO metadata editing, advanced security guards, Core Web Vitals tracking, infrastructure reports, the Redirect Manager, scheduled regeneration, portal connectivity, and multisite fleet orchestration. See the Description above.